Swaprum - Audit 1
CertiK reviewed swaprum.finance (Swaprum - Audit 1) on 5 May 2023: 23 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings23
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 4 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 19 | 0 | 0 |
HighCentralization Risks in MasterChef.solOpen
In the contract `MasterChef` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and perform, including but not limited to, the following: - set the `BONUS_MULTIPLIER` to 0 and remove any kind of rewards from all the pools. - set the `allocPoint` of a pool to 0 and exclude it from the rewards. - set the `migrator` contract address to a malicious one, which can execute any code with the call `migrator.migrate(lpToken)` (e.g., stealing all lpTokens of a pool). 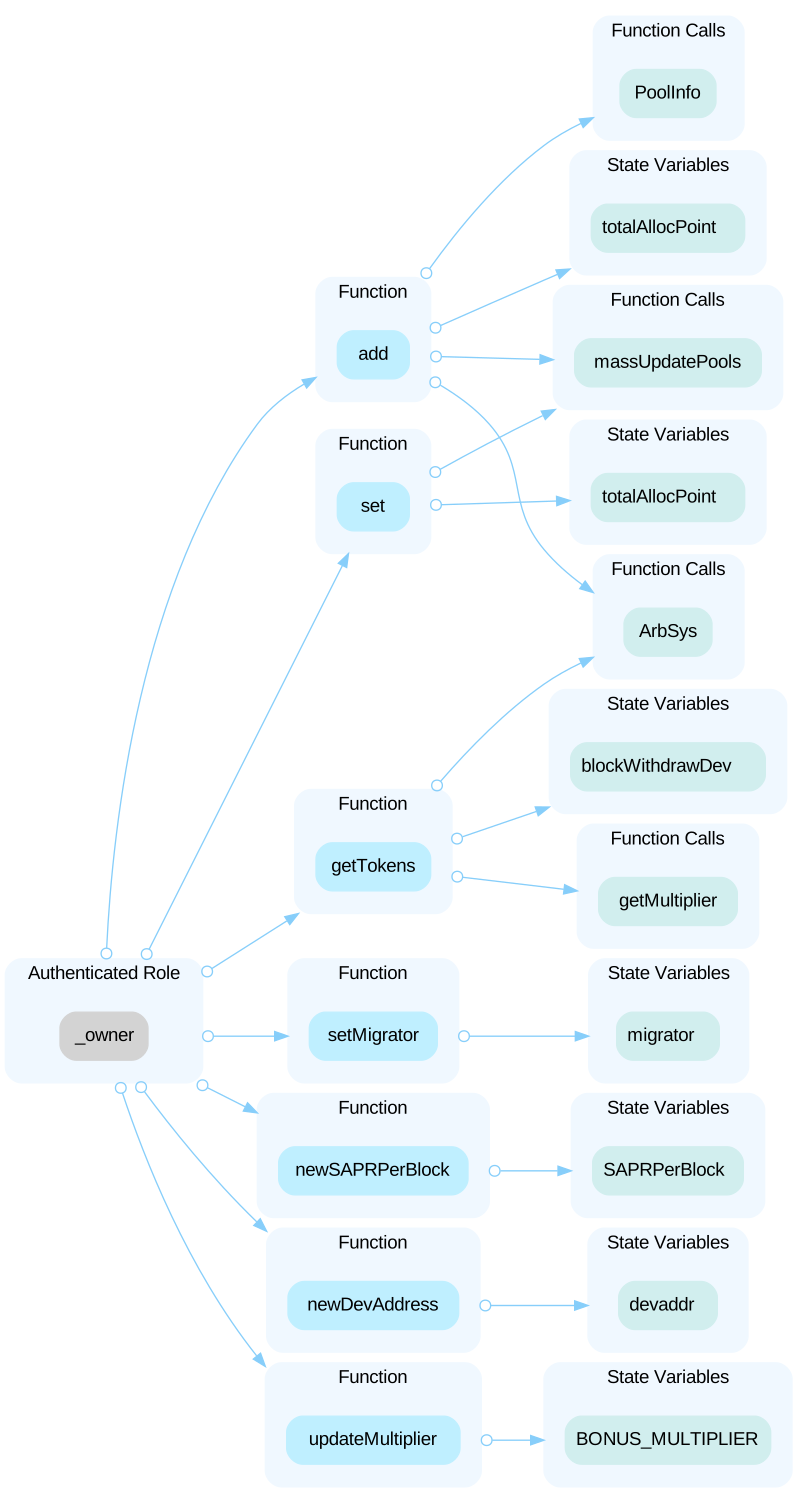
HighCentralization Risks in SwaprumV2Factory.solOpen
In the contract `SwaprumV2Factory` the role `feeToSetter` has authority over the functions shown in the diagram below. 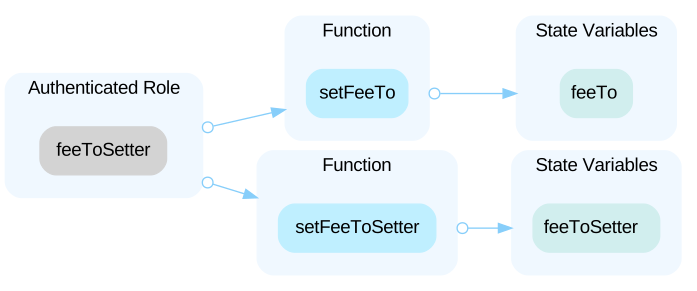 Any compromise to the `feeToSetter` account may allow the hacker to take advantage of this authority and change the recipient address of the fees.
HighCentralized Control of Contract UpgradeOpen
The `MasterChef` is an upgradeable contract, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
HighUnknown Implementation of `migrator.migrate()`Open
The `setMigrator()` function can set the migrator contract to any contract that is implemented from the `IMigratorChef` interface by the owner. As a result, invoking `migrator.migrate()` in the `migrate()` function may have dangerous effects that are unknown to the user. However, removing `setMigrator()` and `migrate()` could result in losing the ability to upgrade and migrate the project.
Low`add()` Function Not RestrictedOpen
When the same LP token is added into a pool more than once in function `add()`, the total amount of reward in function `updatePool()` is incorrectly calculated. The current implementation is relying on the operational correctness to avoid repeatedly adding the same LP token to the pool, as the function can only be called by the owner.
LowCheck Effect Interaction Pattern ViolatedOpen
The order of external call/transfer and storage manipulation must follow the check-effect-interaction pattern in functions: - `enterStaking()` - `leaveStaking()` - `deposit()` - `withdraw()` - `emergencyWithdraw()` - `getTokens()`
LowImproper Usage of `public` and `external` TypeOpen
`public` functions that are never called by the contract could be declared as `external`. `external` functions can be more efficient than `public` functions.
LowIncompatibility With Deflationary TokensOpen
The MasterChef contract operates as the main entry for interaction with staking users. The staking users deposit LP tokens into the Swaprum pool and in return get a proportionate share of the pool’s rewards. Later on, the staking users can withdraw their own assets from the pool. In this procedure, `deposit()` and `withdraw()` are involved in transferring users’ assets into (or out of) the Swaprum protocol. When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged (and burned) transaction fee. As a result, this may not meet the assumption behind these low-level asset-transferring routines and will bring unexpected balance inconsistencies.
LowIncorrect Event EmitOpen
The functions `enterStaking()` and `leaveStaking()` emit an event when they are called. Such events are `Deposit` and `Withdraw`, respectively. These errors can confuse as users can not deposit nor withdraw the `SAPR` token but they can either `Stake` or `Unstake` them.
LowLack of Input ValidationOpen
At the pointed locations the input parameters are not checked to be valid: - The function `initialize()` does not check that the parameters `_SAPR`, `_devaddr`, `_SAPRPerBlock`, and `_startBlock` are not the zero address or the value zero, as they correspond. - The function `updateMultiplier()` does not check whether the new value of `BONUS_MULTIPLIER` is zero. - The function `newDevAddress()` does not check whether the new parameter `_devaddr` is the zero address. - The function `setMigrator()` does not check whether the new parameter `_migrator` is the zero address. - The functions `deposit()`, `withdraw()`, `enterStaking()` and `leaveStaking()` do not check whether the parameter `_amount` is zero.
Show 10 more
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowMissing Explicit Pool Validity ChecksOpen
The functions at the pointed location, do not have a sanity check to validate if a pool is existing.
LowMissing License IdentifiersOpen
While the SPDX license identifiers where not introduced until Solidity 0.6.8 it is still good practice to include them when using earlier compiler versions as well.
LowRedundant Calls To `arbBlockNumber()`Open
The function `getTokens()` calls three times the function `ArbSys(100).arbBlockNumber()` to get the current block number. Two of those calls can be avoided if the value was stored in a local variable. This could save gas and make the code more efficient. A similar issue happens on the functions `pendingSAPR()` and `updatePool()`.
LowRedundant FunctionsOpen
In the codebase, the functions `enterStaking()` and `leaveStaking()` are implemented almost identically to `deposit()` and `withdraw()`. The main difference is that they update the `depositedSapr` value, which represents the total supply of the `SAPR` pool. This creates unnecessary code duplication and could lead to confusion for developers maintaining the codebase.
LowRedundant MultiplicationOpen
The linked code is a multiplication of one, which will return the same value. This multiplication can be removed to optimize the code.
LowSafeMath Not UsedOpen
OpenZeppelin's `SafeMath` library is not used in the linked operations, making it possible for overflow/underflow to occur and lead to inaccurate calculations.
LowTyposOpen
There are typos in the highlighted lines of the codebase. "R" can be deleted. "1/2th" should be "1/2".
LowUnclear Error MessageOpen
The linked error message reads "withdraw: not good". This message does not state what is the condition that didn't meet.
LowUnder-minted TokensOpen
The function `updatePool()` mints less than the expected `SAPRReward`. In fact, the total value is multiplied by `855` and divided by `1000` reducing the token minting by a 14.5%.
Show 3 more
LowUnused VariableOpen
The linked variable is unused and can be removed.
LowUsage of Magic NumbersOpen
Different magic numbers are used as-is in code.
LowVariables That Could Be Declared as ImmutableOpen
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of swaprum.finance’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us