Peezy - Audit
CertiK reviewed Peezy Coin (Peezy - Audit) on 5 Feb 2025: 9 findings, 0 critical; 2 marked fixed, 6 acknowledged, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings9
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 2 |
| Medium | 0 | 1 | 0 |
| Low | 0 | 5 | 0 |
HighCentralization Risks in PEEZY.solFixed
In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and renounce current ownership. 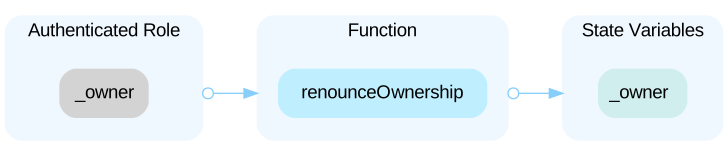 In the contract `PEEZY`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and open trading and enable swap functionality, remove transaction and wallet size limits, add bots to the list, remove bots from the list, and remove the transfer tax. 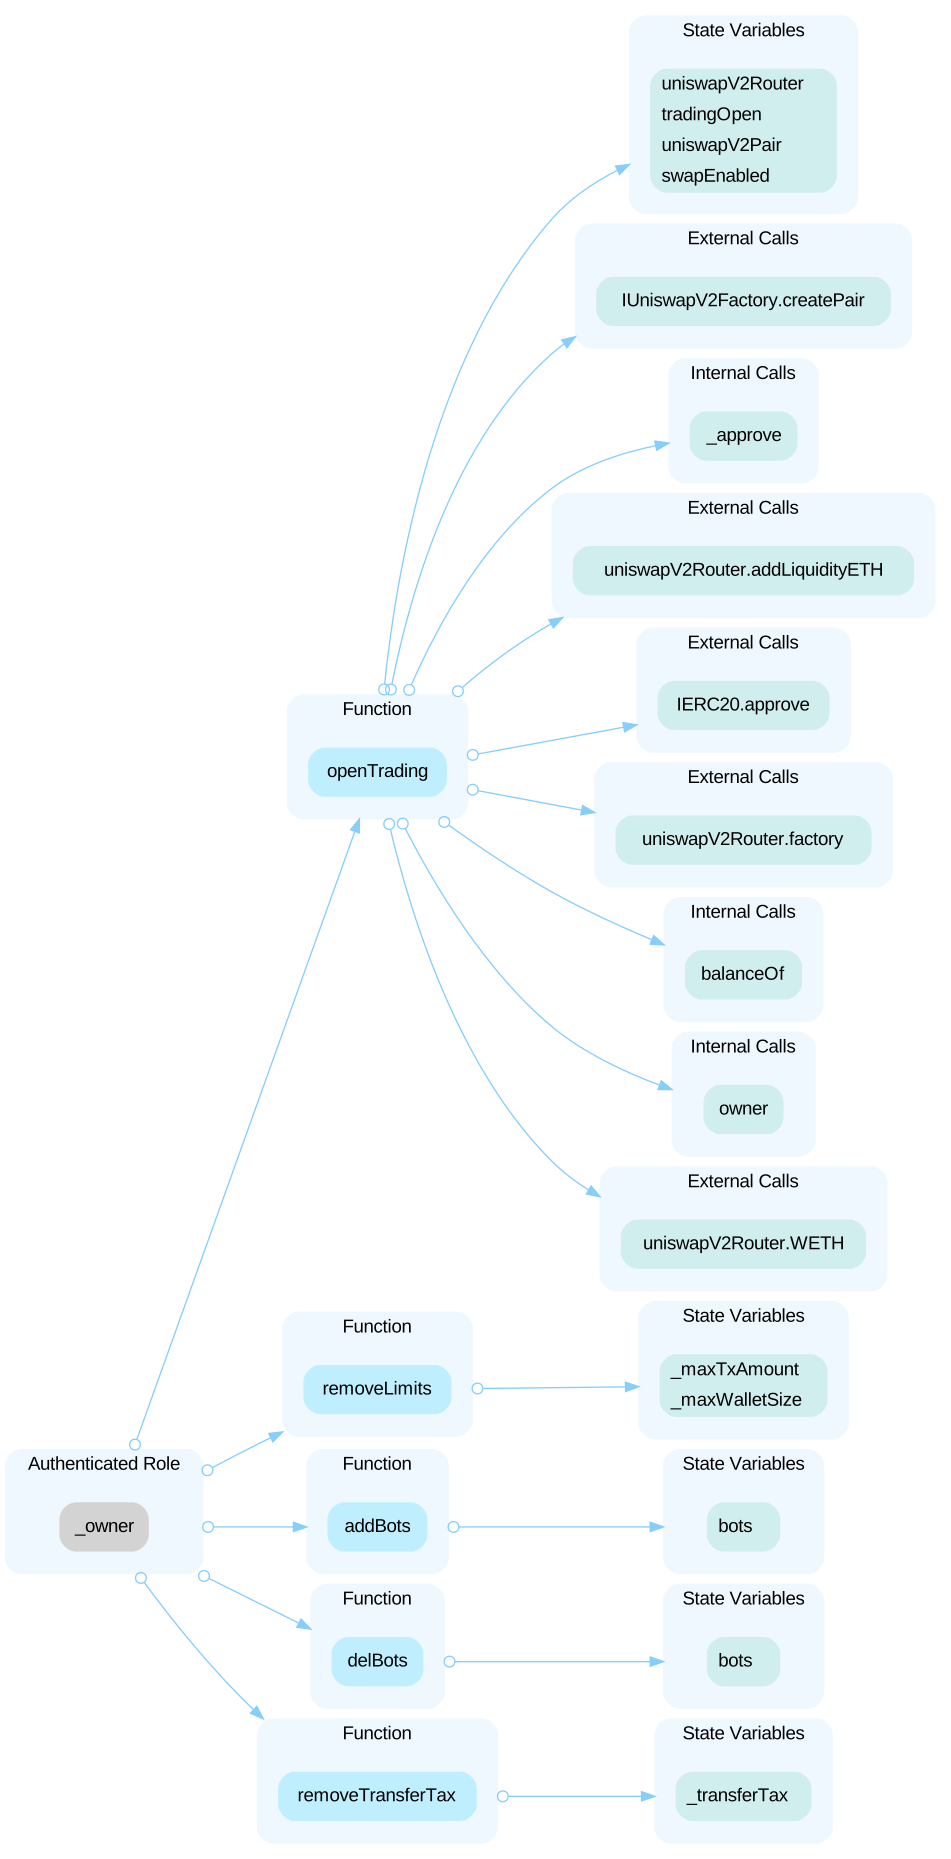 In the contract `PEEZY`, the role `_taxWallet` has authority over the functions shown in the diagram below. Any compromise to the `_taxWallet` account may allow the hacker to take advantage of this authority and send ETH to the fee wallet manually, perform manual token swap and fee distribution, and reduce the transaction fee. 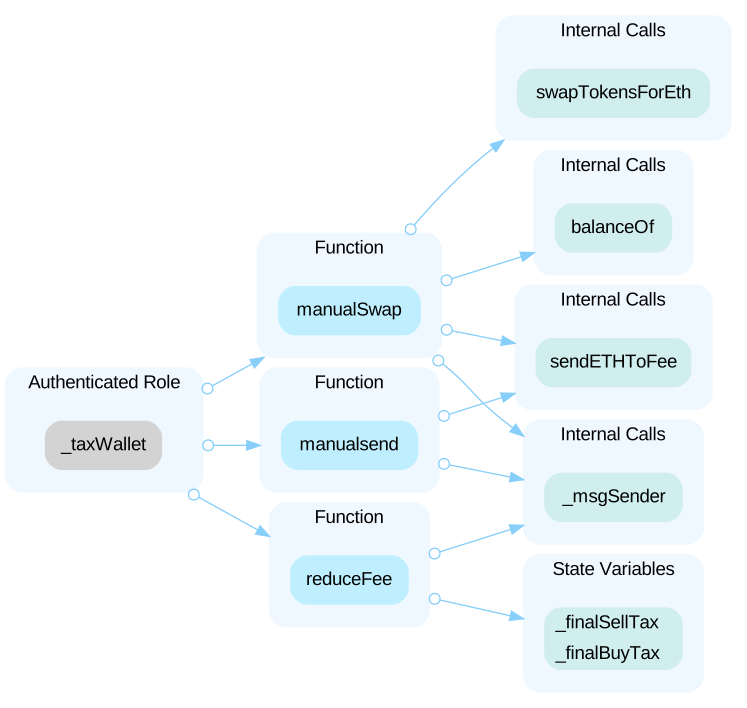
HighCentralized Token Holding Position RiskFixed
In the contract `PEEZY`, the owner has all the tokens minted at the time of the contract deployment. This creates a severe centralization risk and can lead to manipulation of the tokenomic of the project. Any compromise to the private keys of the owner may allow a hacker to take advantage of the owner authority and sell tokens on the market and/or remove the pool liquidity, causing a severe price drop. ```solidity=322 function openTrading() external onlyOwner() { require(!tradingOpen,"trading is already open"); uniswapV2Router = IUniswapV2Router02(0x7a250d5630B4cF539739dF2C5dAcb4c659F2488D); _approve(address(this), address(uniswapV2Router), _tTotal); uniswapV2Pair = IUniswapV2Factory(uniswapV2Router.factory()).createPair(address(this), uniswapV2Router.WETH()); uniswapV2Router.addLiquidityETH{value: address(this).balance}(address(this),balanceOf(address(this)),0,0,owner(),block.timestamp); IERC20(uniswapV2Pair).approve(address(uniswapV2Router), type(uint).max); swapEnabled = true; tradingOpen = true; } ```
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x698b1d54e936b9f772b8f58447194bbc82ec1933 | Chain: Ethereum | Source code: Verified source |
Part of Peezy Coin’s security record
 Peezy Coin
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us