Floppa
CertiK reviewed Floppa on 22 May 2023: 4 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 1 | 0 |
| Low | 0 | 2 | 0 |
HighInitial Token DistributionAcknowledged
All **FLOP** tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute **FLOP** tokens without the consensus of the community.
MediumCentralization Risks in BigFloppaToken.solAcknowledged
In the contract `BigFloppaToken` the role `_owner` has authority over the functions shown in the diagram and list below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and control the token transfers. 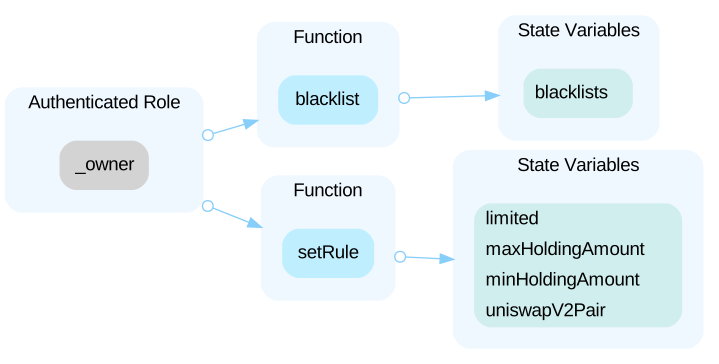 - `blacklist()`: Owner can blacklist addresses from transferring tokens. - `setRules()`: Owner can set configurations of the contract. In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram and list below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership to other addresses. 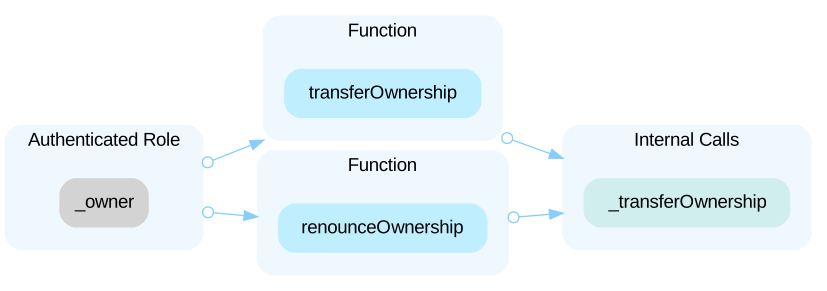 - `transferOwnership()`: Owner can transfer contract ownership. - `renounceOwnership()`: Owner can give up contract ownership.
LowMinimum Holding Rules for BigFloppaToken.solAcknowledged
The condition `super.balanceOf(to) + amount >= minHoldingAmount` in the `_beforeTokenTransfer` function enforces a minimum holding requirement for any address receiving tokens from the Uniswap pair. From the way this condition is written, it would require that the balance of tokens in the recipient's (`to`) address after the transfer is at least the `minHoldingAmount`. This means that a recipient must either already have enough tokens to meet the `minHoldingAmount` or the amount they are receiving should be enough to take their balance to the `minHoldingAmount` or above.
LowMissing checks for input parametersAcknowledged
The following areas are missing checks on input parameters to ensure that the inputs are appropriate. ### blacklist() * `_isBlacklisting` - No checks that the value contained in `blacklists[_address]` is not equal to the value of `_isBlacklisting` before setting a new value to `blacklists[_address]` ### setRule() * `_minHoldingAmount` - No checks to ensure that `_minHoldingAmount` is less than `_maxHoldingAmount`
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of Floppa’s security record
 Floppa
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us