Zkswap Finance - Audit
CertiK reviewed zkSwap Finance (Zkswap Finance - Audit) on 27 Dec 2023: 6 findings, 0 critical; 1 marked fixed, 5 open.
The original report was removed from its address (seen 17 Oct 2026).
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 4 | 0 | 1 |
HighCentralization Related RisksOpen
In the contract `ZFFactory` the role `feeToSetter` has authority over the functions shown in the diagram below. Any compromise to the `feeToSetter` account may allow the hacker to take advantage of this authority. - set the address of `feeTo` - set `swapFee` - set protocol fee factor - set the address of `pendingFeeToSetter`, who can accept the `feeToSetter` role - set swap fee point override for a pair 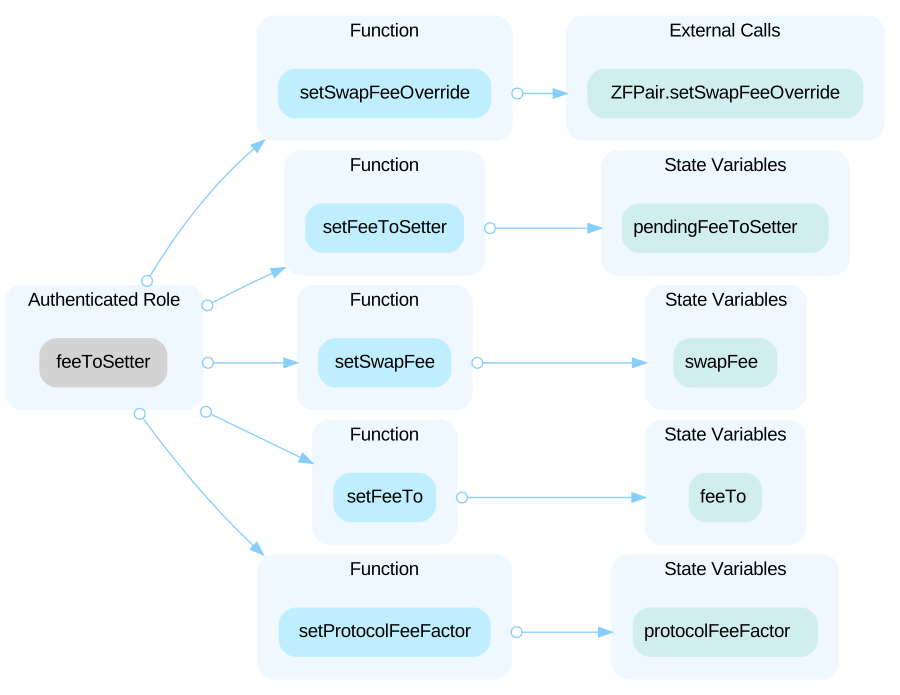 In the contract `ZFFactory` the role `pendingFeeToSetter` has authority over the functions shown in the diagram below. Any compromise to the `pendingFeeToSetter` account may allow the hacker to take advantage of this authority. - accept the `feeToSetter` role 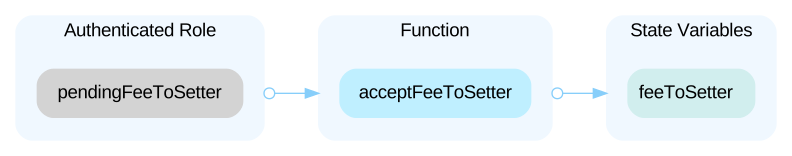 In the contract `ZFPair` the role `factory` has authority over the functions shown in the diagram below. Any compromise to the `factory` account may allow the hacker to take advantage of this authority. - set the `swapFeeOverride` 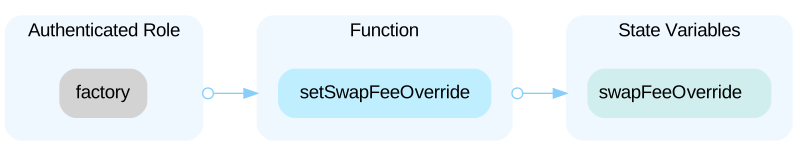
Low`indexedPairs` Not Update When Users Remove LiquiOpen
We note that the variable `indexedPairs` is used to keep track of users who add liquidity, but does not remove the user from the variable `indexedPairs` after the user removes liquidity completely.
LowLack of reasonable limitOpen
The `setProtocolFeeFactor()` function allows the `feeToSetter` to set the minimum `protocolFeeFactor` as 2, which means half of the fee will be charged and sent to the `_feeTo`. The popular DEXs Uniswap V2 charges 1/6 and Pancake charges 1/4. ```solidity function _getFeeLiquidity(uint _totalSupply, uint _rootK2, uint _rootK1, uint8 _feeFactor) private pure returns (uint) { uint numerator = _totalSupply * (_rootK2 - _rootK1); uint denominator = (_feeFactor - 1) * _rootK2 + _rootK1; return numerator / denominator; } ```
LowMissing Zero Address ValidationOpen
Addresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior or vulnerabilities. For example, transferring tokens to a zero address can result in a permanent loss of those tokens. ```solidity=34 feeToSetter = _feeToSetter; ``` - `_feeToSetter` is not zero-checked before being used. --- ```solidity=69 feeTo = _feeTo; ``` - `_feeTo` is not zero-checked before being used. --- ```solidity=86 pendingFeeToSetter = _feeToSetter; ``` - `_feeToSetter` is not zero-checked before being used. --- ```solidity=53 token0 = _token0; ``` - `_token0` is not zero-checked before being used. --- ```solidity=54 token1 = _token1; ``` - `_token1` is not zero-checked before being used. --- ```solidity=19 factory = _factory; ``` - `_factory` is not zero-checked before being used. --- ```solidity=20 WETH = _WETH; ``` - `_WETH` is not zero-checked before being used.
LowUnsafe Integer CastOpen
Type casting refers to changing an variable of one data type into another. The code contains an unsafe cast between integer types, which may result in unexpected truncation or sign flipping of the value. ```solidity=109 principal0: uint112(liquidity * _reserve0 / _totalSupply), ``` Casted expression `liquidity * _reserve0 / _totalSupply` has estimated range [0, 115792089237316195423570985008687907853269984665640564039457584007913129639935] but target type `uint112` has range [0, 5192296858534827628530496329220095]. --- ```solidity=110 principal1: uint112(liquidity * _reserve1 / _totalSupply), ``` Casted expression `liquidity * _reserve1 / _totalSupply` has estimated range [0, 115792089237316195423570985008687907853269984665640564039457584007913129639935] but target type `uint112` has range [0, 5192296858534827628530496329220095]. --- ```solidity=118 principal0: uint112(liquidity * _reserve0 / _totalSupply), ``` Casted expression `liquidity_scope_0 * _reserve0 / _totalSupply` has estimated range [0, 115792089237316195423570985008687907853269984665640564039457584007913129639935] but target type `uint112` has range [0, 5192296858534827628530496329220095]. --- ```solidity=119 principal1: uint112(liquidity * _reserve1 / _totalSupply), ``` Casted expression `liquidity_scope_0 * _reserve1 / _totalSupply` has estimated range [0, 115792089237316195423570985008687907853269984665640564039457584007913129639935] but target type `uint112` has range [0, 5192296858534827628530496329220095].
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (6)
- contracts/core/ZFFactory.sol
- contracts/core/ZFPair.sol
- contracts/core/ZFRouterInternal.sol
- contracts/core/MetadataHelper.sol
- contracts/core/ZFRouter.sol
- contracts/core/ZFLibrary.sol
Part of zkSwap Finance’s security record
 zkSwap Finance
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us