ACENT Mainnet
CertiK reviewed ACENT (ACENT Mainnet) on 15 Nov 2022: 47 findings, 1 critical; 9 marked fixed, 38 open.
The original report was removed from its address (seen 17 Oct 2026).
Trustblock does not review code.
Findings47
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 12 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 26 | 0 | 7 |
HighCentralization Risks In `treasury` AddressOpen
File: ADEVault.sol The linked statement transfers the withdrawal/performance fee valued in the `ADE` token to the `treasury`. As a result, over time the `treasury` will accumulate a significant portion of `ADE` tokens. If the `treasury` is an EOA (Externally Owned Account), mishandling its private key can have devastating consequences for the project as a whole.
HighCentralization Risks in AcentFactory.solOpen
In the contract `AcentFactory` the role `feeToSetter` has authority over the functions shown in the diagram below. Any compromise to the `feeToSetter` account may allow the hacker to take advantage of this authority. 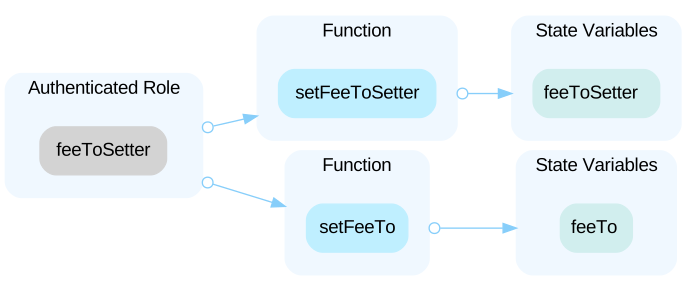
HighCentralization Risks in AcentPair.solOpen
In the contract `AcentPair` the role `factory` has authority over the functions shown in the diagram below. Any compromise to the `factory` account may allow the hacker to take advantage of this authority. 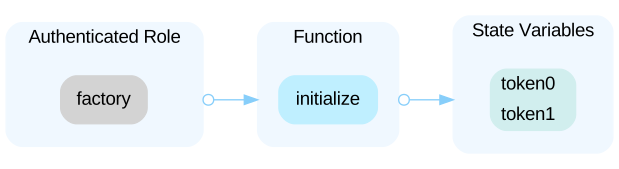
HighCentralization Risks in ADEInitMintable.solOpen
In the contract `ADEInitMintable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 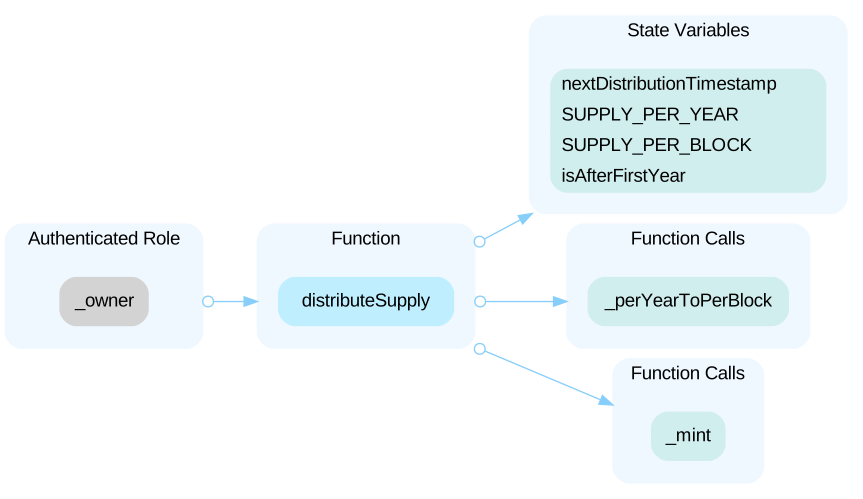
HighCentralization Risks in ADEToken.solOpen
In the contract `ADEToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 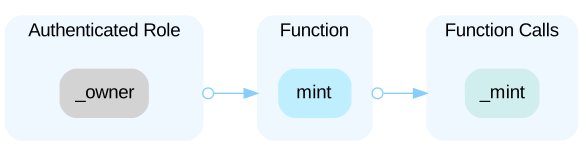
HighCentralization Risks in ADEVault.solOpen
In the contract `ADEVault` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 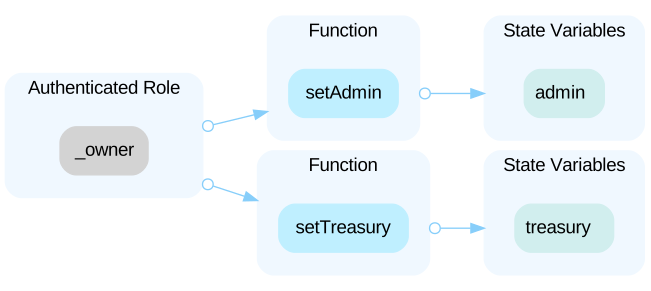 In the contract `ADEVault` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority. 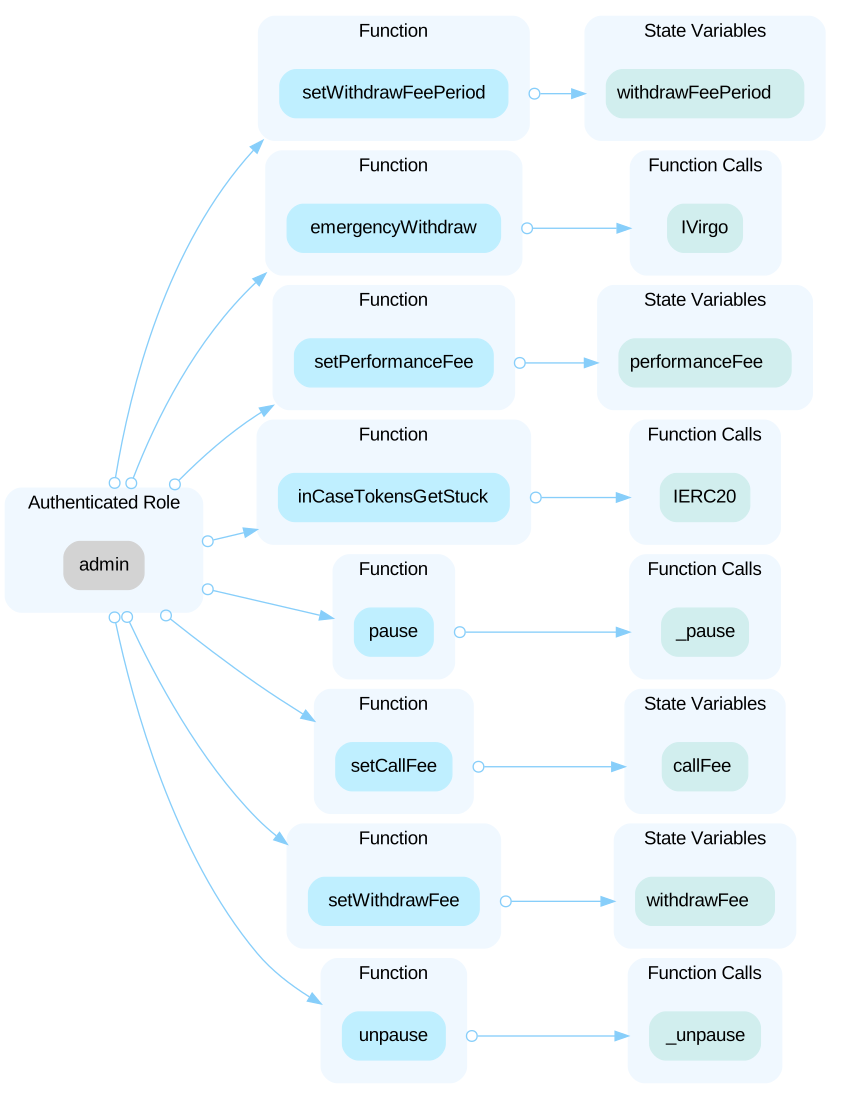
HighCentralization Risks in FundDistributor.solOpen
In the contract `FundDistributor` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority. 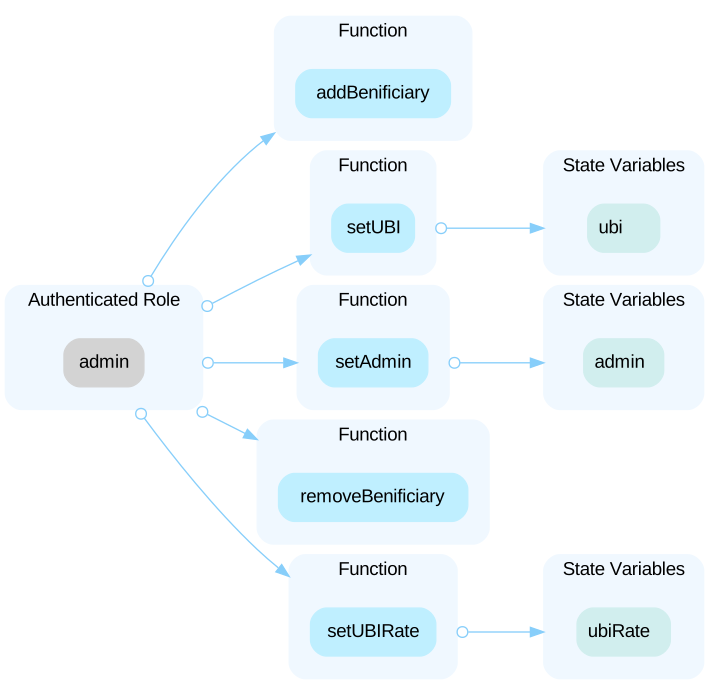
HighCentralization Risks in Spica.solOpen
In the contract `Spica` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 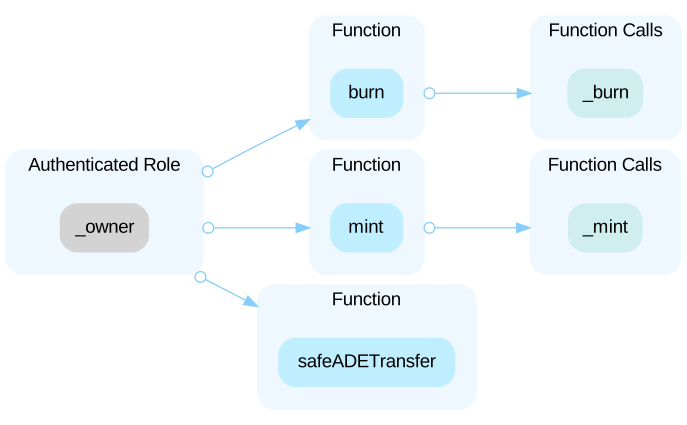
HighCentralization Risks in Supercluster.solOpen
In the contract `Supercluster` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 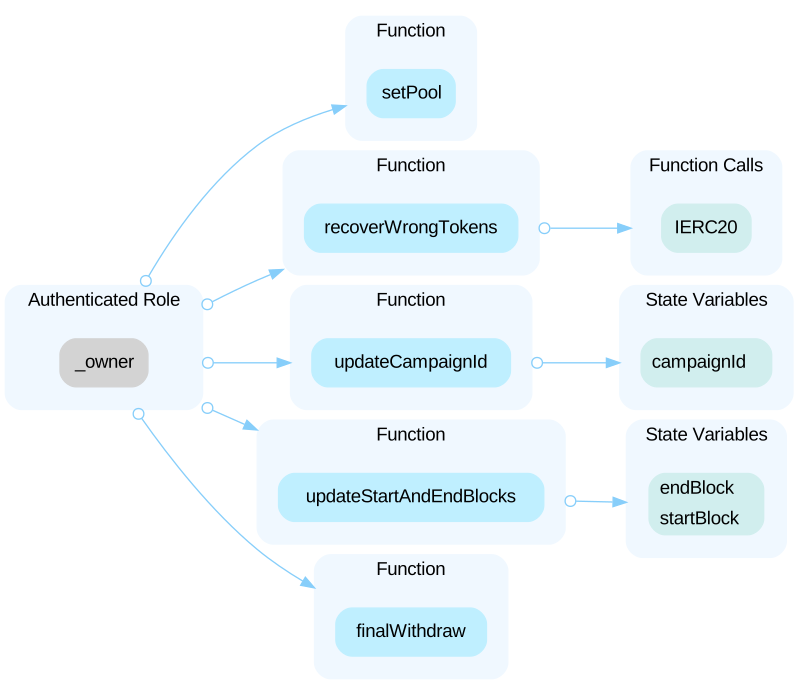
HighCentralization Risks in Timelock.solOpen
In the contract `Timelock` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority. 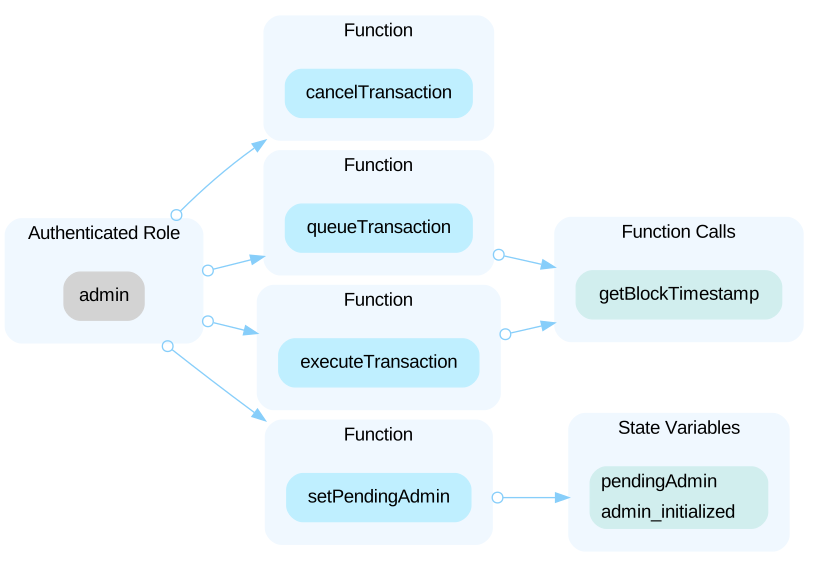 In the contract `Timelock` the role `pendingAdmin` has authority over the functions shown in the diagram below. Any compromise to the `pendingAdmin` account may allow the hacker to take advantage of this authority. 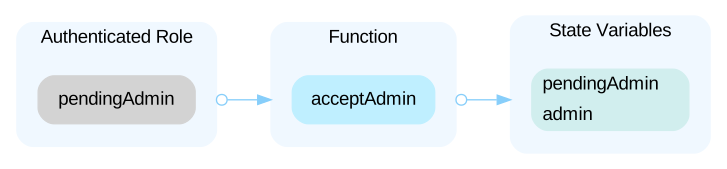
Show 10 more
HighCentralization Risks in Virgo.solOpen
In the contract `Virgo` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 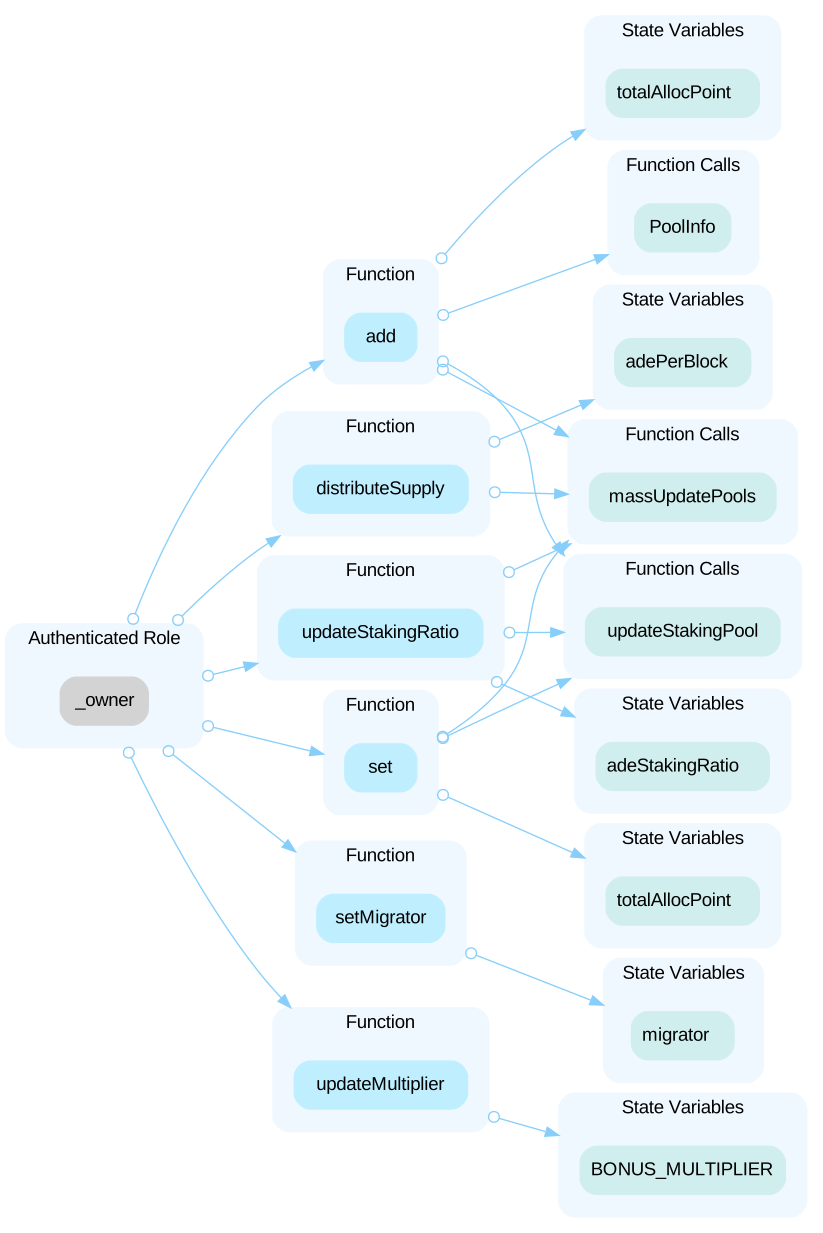 In the contract `Virgo` the role `devaddr` has authority over the functions shown in the diagram below. Any compromise to the `devaddr` account may allow the hacker to take advantage of this authority. 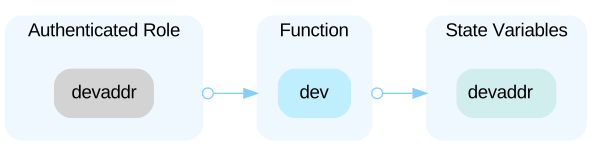
HighCentralization Risks in VirgoAdmin.solOpen
In the contract `VirgoAdmin` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 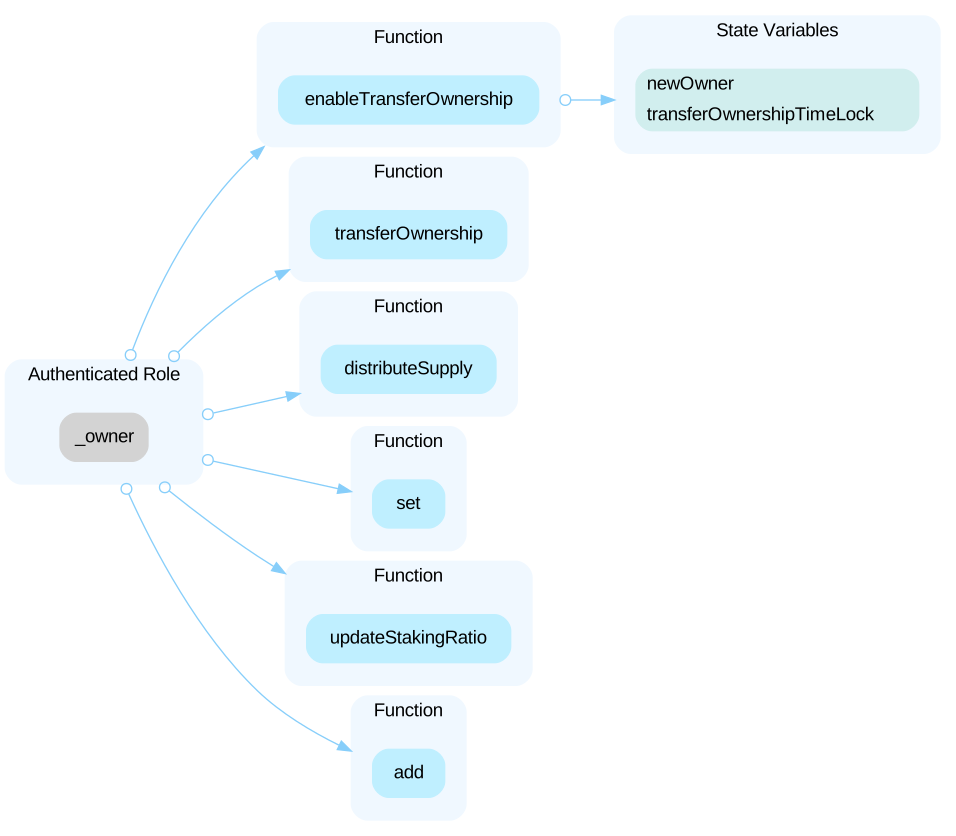
Low`add()` Function Not RestrictedOpen
File: Virgo.sol When the same LP token is added into a pool more than once in the function `add()`, the total amount of reward in the function `updatePool()` will be incorrectly calculated. The current implementation is relying on the operation correctness to avoid repeatedly adding the same LP token to the pool, as the function will only be called by the owner.
LowCheck Effect Interaction Pattern ViolatedOpen
File: ADEVault.sol The order of external call/transfer and storage manipulation must follow the check-effect-interaction pattern in the following functions: - `withdraw()`
LowCheck Effect Interaction Pattern ViolatedOpen
File: Virgo.sol The order of external call/transfer and storage manipulation must follow the check-effect-interaction pattern in the following functions: - `deposit()` - `withdraw()` - `enterStaking()` - `leaveStaking()` - `emergencyWithdraw()`
LowFunction `transfer` Prevents Overflows in the RecOpen
File: WACE.sol Any invocation of `transfer(recipient, amount)` must fail if it causes the balance of the `recipient` address to overflow.
LowFunction `transfer` Prevents Overflows in the RecOpen
File: WACE.sol Any invocation of `transfer(recipient, amount)` must fail if it causes the balance of the `recipient` address to overflow.
LowFunction `transfer` Prevents Transfers to the ZerOpen
File: WACE.sol Any call of the form `transfer(recipient, amount)` must fail if the recipient address is the zero address.
LowFunction `transfer` Prevents Transfers to the ZerOpen
File: WACE.sol Any call of the form `transfer(recipient, amount)` must fail if the recipient address is the zero address.
LowFunction `transferFrom` Fails for Transfers FromOpen
File: WACE.sol All calls of the form `transferFrom(from, dest, amount)` where the `from` address is zero, must fail.
Show 10 more
LowFunction `transferFrom` Fails for Transfers FromOpen
File: WACE.sol All calls of the form `transferFrom(from, dest, amount)` where the `from` address is zero, must fail.
LowFunction `transferFrom` Fails for Transfers To thOpen
File: WACE.sol All calls of the form `transferFrom(from, dest, amount)` where the `dest` address is zero, must fail.
LowFunction `transferFrom` Fails for Transfers To thOpen
File: WACE.sol All calls of the form `transferFrom(from, dest, amount)` where the `dest` address is zero, must fail.
LowFunction `transferFrom` Prevents Overflows in theOpen
File: WACE.sol Any call of `transferFrom(from, dest, amount)` with a value in `amount` whose transfer would cause an overflow of the balance of address `dest` must fail.
LowFunction `transferFrom` Prevents Overflows in theOpen
File: WACE.sol Any call of `transferFrom(from, dest, amount)` with a value in `amount` whose transfer would cause an overflow of the balance of address `dest` must fail.
LowImproper Usage of `public` and `external` TypeOpen
`public` functions that are never called by the contract could be declared as `external`. `external` functions are more efficient than `public` functions.
LowIncompatibility With Deflationary TokensOpen
File: ADERouter.sol When users add or remove LP tokens into the router, and the `mint` and `burn` operations are performed. When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. As a result, the amount inconsistency will occur and the transaction may fail due to the validation checks.
LowIncompatibility With Deflationary TokensOpen
File: Virgo.sol The contract `MasterChef` operates as the main entry for interaction with staking users. The staking users deposit LP tokens into the `AcentSwap` pool and in return get a proportionate share of the pool’s rewards. Later on, the staking users can withdraw their own assets from the pool. In this procedure, the functions `deposit()` and `withdraw()` are involved in transferring users’ assets into (or out of) the `AcentSwap` protocol. When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged (and burned) transaction fee. As a result, this may not meet the assumption behind these low-level asset-transferring routines and will bring unexpected balance inconsistencies.
LowInefficient Code Execution PathOpen
The linked statement at L135 will cause data copy operation from `memory` to `storage` space and need more gas fee to execute, however, it is unnecessarily executed if the values of `preAllocPoint` and `_allocPoint` are the same.
LowLack of Pool Validity ChecksOpen
File: Virgo.sol There's no sanity check to validate if a pool exists.
Show 8 more
LowMissing Input ValidationOpen
File: Supercluster.sol The given input is missing the check for the array size.
LowMissing Zero Address ValidationOpen
Addresses should be checked before assignment or external call to make sure they are not zero addresses. ```solidity=18 (bool success, bytes memory returnData) = router.delegatecall(abi.encodeWithSelector( IADERouter01(router).swapExactTokensForTokens.selector, amountIn, amountOutMin, path, to, deadline )); ``` - `router` is not zero-checked before being used. --- ```solidity=28 feeToSetter = _feeToSetter; ``` - `_feeToSetter` is not zero-checked before being used. --- ```solidity=33 (bool success, bytes memory returnData) = router.delegatecall(abi.encodeWithSelector( IADERouter01(router).swapTokensForExactTokens.selector, amountOut, amountInMax, path, to, deadline )); ``` - `router` is not zero-checked before being used. --- ```solidity=47 (bool success, bytes memory returnData) = router.delegatecall(abi.encodeWithSelector( IADERouter01(router).swapExactETHForTokens.selector, amountOutMin, path, to, deadline )); ``` - `router` is not zero-checked before being used. --- ```solidity=48 disliked = _validator; ``` - `_validator` is not zero-checked before being used. --- ```solidity=54 feeTo = _feeTo; ``` - `_feeTo` is not zero-checked before being used. --- ```solidity=59 feeToSetter = _feeToSetter; ``` - `_feeToSetter` is not zero-checked before being used. --- ```solidity=62 (bool success, bytes memory returnData) = router.delegatecall(abi.encodeWithSelector( IADERouter01(router).swapTokensForExactETH.selector, amountOut, amountInMax, path, to, deadline )); ``` - `router` is not zero-checked before being used. --- ```solidity=77 (bool success, bytes memory returnData) = router.delegatecall(abi.encodeWithSelector( IADERouter01(router).swapExactTokensForETH.selector, amountIn, amountOutMin, path, to, deadline )); ``` - `router` is not zero-checked before being used. --- ```solidity=78 token0 = _token0; ``` - `_token0` is not zero-checked before being used. --- ```solidity=79 token1 = _token1; ``` - `_token1` is not zero-checked before being used. --- ```solidity=91 (bool success, bytes memory returnData) = router.delegatecall(abi.encodeWithSelector( IADERouter01(router).swapETHForExactTokens.selector, amountOut, path, to, deadline )); ``` - `router` is not zero-checked before being used.
LowMutability Specifiers MissingOpen
The linked variables are assigned only once, either during their contract-level declaration or during the `constructor`'s execution.
LowMutability Specifiers MissingOpen
The linked variables are assigned only once, either during their contract-level declaration or during the `constructor`'s execution.
LowPotential Risk Of Low-level CallOpen
File: Multicall2.sol Anyone can call the two functions `aggregate()` and `tryAggregate()` because they don't have access limitations. The attackers may successfully access such the `onlyOwner/onlyAdmin` functions of the target contract with the malicious `callData` if the `Muticall2` contract is set to be the `owner/admin` of the `target` contract. In this case, the contract is attacked.
LowUnknown Implementation of `migrator.migrate()`Open
File: Virgo.sol The `owner` can set the `migrator` to any contract that implements the `IMigratorChef` interface via the function `setMigrator()`. Therefore, calling `migrator.migrate()` in the function `migrate()` may have dangerous implications, since it is unknown to the user. However, if `setMigrator()` and `migrate()` are removed, the project may lose the ability to upgrade and migrate.
LowUnlocked Compiler VersionOpen
The contract has unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to an ambiguity when debugging as compiler specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one.
LowUnused State VariableOpen
File: Virgo.sol The linked state variable is never used within the `Virgo` contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (40)
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/interfaces/IAcentERC20.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/IERC20.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/ADEInitMintable.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/IADEFactory.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/ADERouter.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/AcentPair.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/ADEVault.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/AcentERC20.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/Supercluster.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/Virgo.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/libraries/SafeMath.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/libraries/ADEOracleLibrary.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/Spica.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/RealAdeRouter.sol
- Core/POSA Smart Contract/contracts/FundDistributor.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/WACE.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/interfaces/IAcentCallee.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/ADEToken.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/IADEMigrator.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/IADERouter01.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/Timelock.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/libs/WACE.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/libraries/ADELibrary.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/interfaces/IAcentFactory.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/IADEPair.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/ISupercluster.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/interfaces/IERC20.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/IWETH.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/V1/IADEV1Exchange.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/ADERouter01.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/libraries/UQ112x112.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/libraries/SafeMath.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/VirgoAdmin.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/IADERouter02.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/libraries/Math.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/ADEMigrator.sol
- Core/Acent Swap Smart Contract/Ade-Farm/contracts/libs/Multicall2.sol
- Core/Acent Swap Smart Contract/deploy_periphery2/contracts/interfaces/V1/IADEV1Factory.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/AcentFactory.sol
- Core/Acent Swap Smart Contract/ace-swap-core-sh/contracts/interfaces/IAcentPair.sol
Part of ACENT’s security record
 ACENT
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us