AIRTNT - Audit
CertiK reviewed AIRTNT (AIRTNT - Audit) on 25 Nov 2022: 3 findings, 0 critical; 2 acknowledged, 1 open.
Report hosted on skynet.certik.com.
Statuses are the security firm’s own, from this report. Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 0 |
HighCentralization Risks in TNT.solAcknowledged
In the contract `TNT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause the contract. 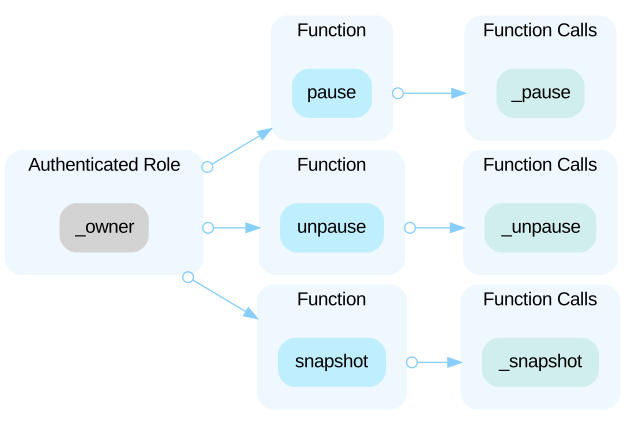
HighInitial Token DistributionAcknowledged
All of the `TNT` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute `TNT` tokens without obtaining the consensus of the community.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/TNT.sol
Part of AIRTNT’s security record
 AIRTNT
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us