Decimalchain - audit
CertiK reviewed Decimal (Decimalchain - audit) on 24 May 2023: 3 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 0 |
HighCentralization Risks in DERC20.solAcknowledged
In the contract `AccessControl` the role `ADMIN_ROLE` has authority over the functions: - revokeRole() - grantRole() Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority. In the contract `DERC20` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 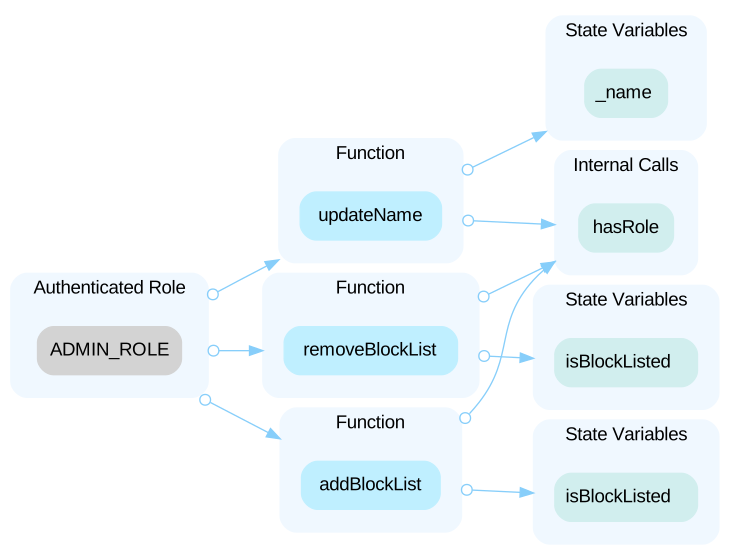 In the contract `DERC20` the role `BURNER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BURNER_ROLE` account may allow the hacker to take advantage of this authority. 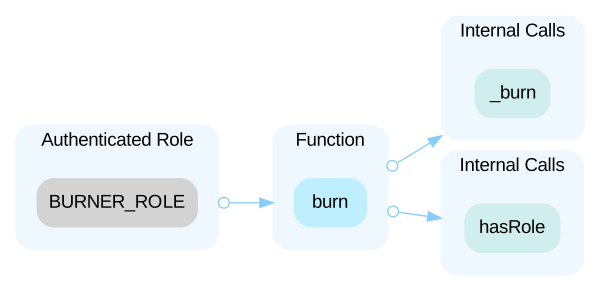 In the contract `DERC20` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority. 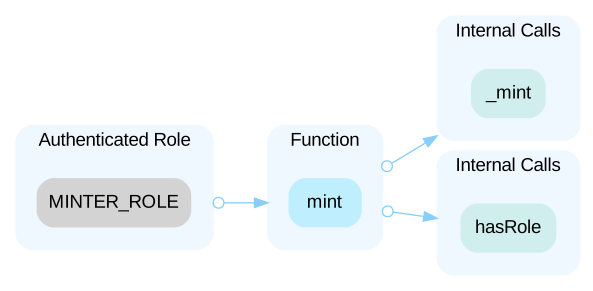 In the contract `DERC20` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority. 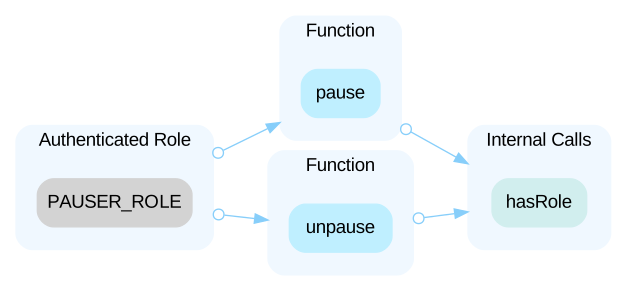
HighCentralized Balance ManipulationAcknowledged
In the contract DERC20, the role `MINTER_ROLE` has the authority to update the token balance of an arbitrary account without sanity restriction. Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and manipulate users' balances. The hacker could also update his/her balance to a large number, sell these tokens, and cause the token price to drop.
LowInconsistent Solidity VersionsAcknowledged
The codebase contains multiple Solidity versions, which can lead to unexpected behavior, potential vulnerabilities, difficulties in maintaining the code, and inconsistencies in the execution of the smart contract. Using different versions may also result in increased complexity during code auditing, as different security features and bug fixes are present in different versions of the compiler. Versions used: `^0.8.0` `^0.8.0` is used in DERC20.sol file. ```solidity=702 pragma solidity ^0.8.0; ```
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x9cec03362d759ceca736e5918e8ba7636e2bd64e | Chain: BNB Chain | Source code: Verified source |
Part of Decimal’s security record
 Decimal
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us