IOST
CertiK reviewed IOST on 10 Mar 2025: 4 findings, 0 critical; 2 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 2 |
HighCentralization Related RisksOpen
### IOSToken In the contract `IOSToken`, the role `_owner` has authority over the functions shown in the diagram below. 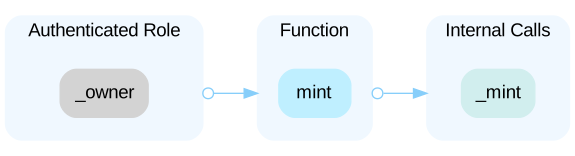 **Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint arbitrage tokens to a specific account, provided that the total supply remains within the configured cap (90,000,000,000).** ### Vesting In the contract `Vesting`, the role `_owner` has authority over the functions shown in the diagram below. 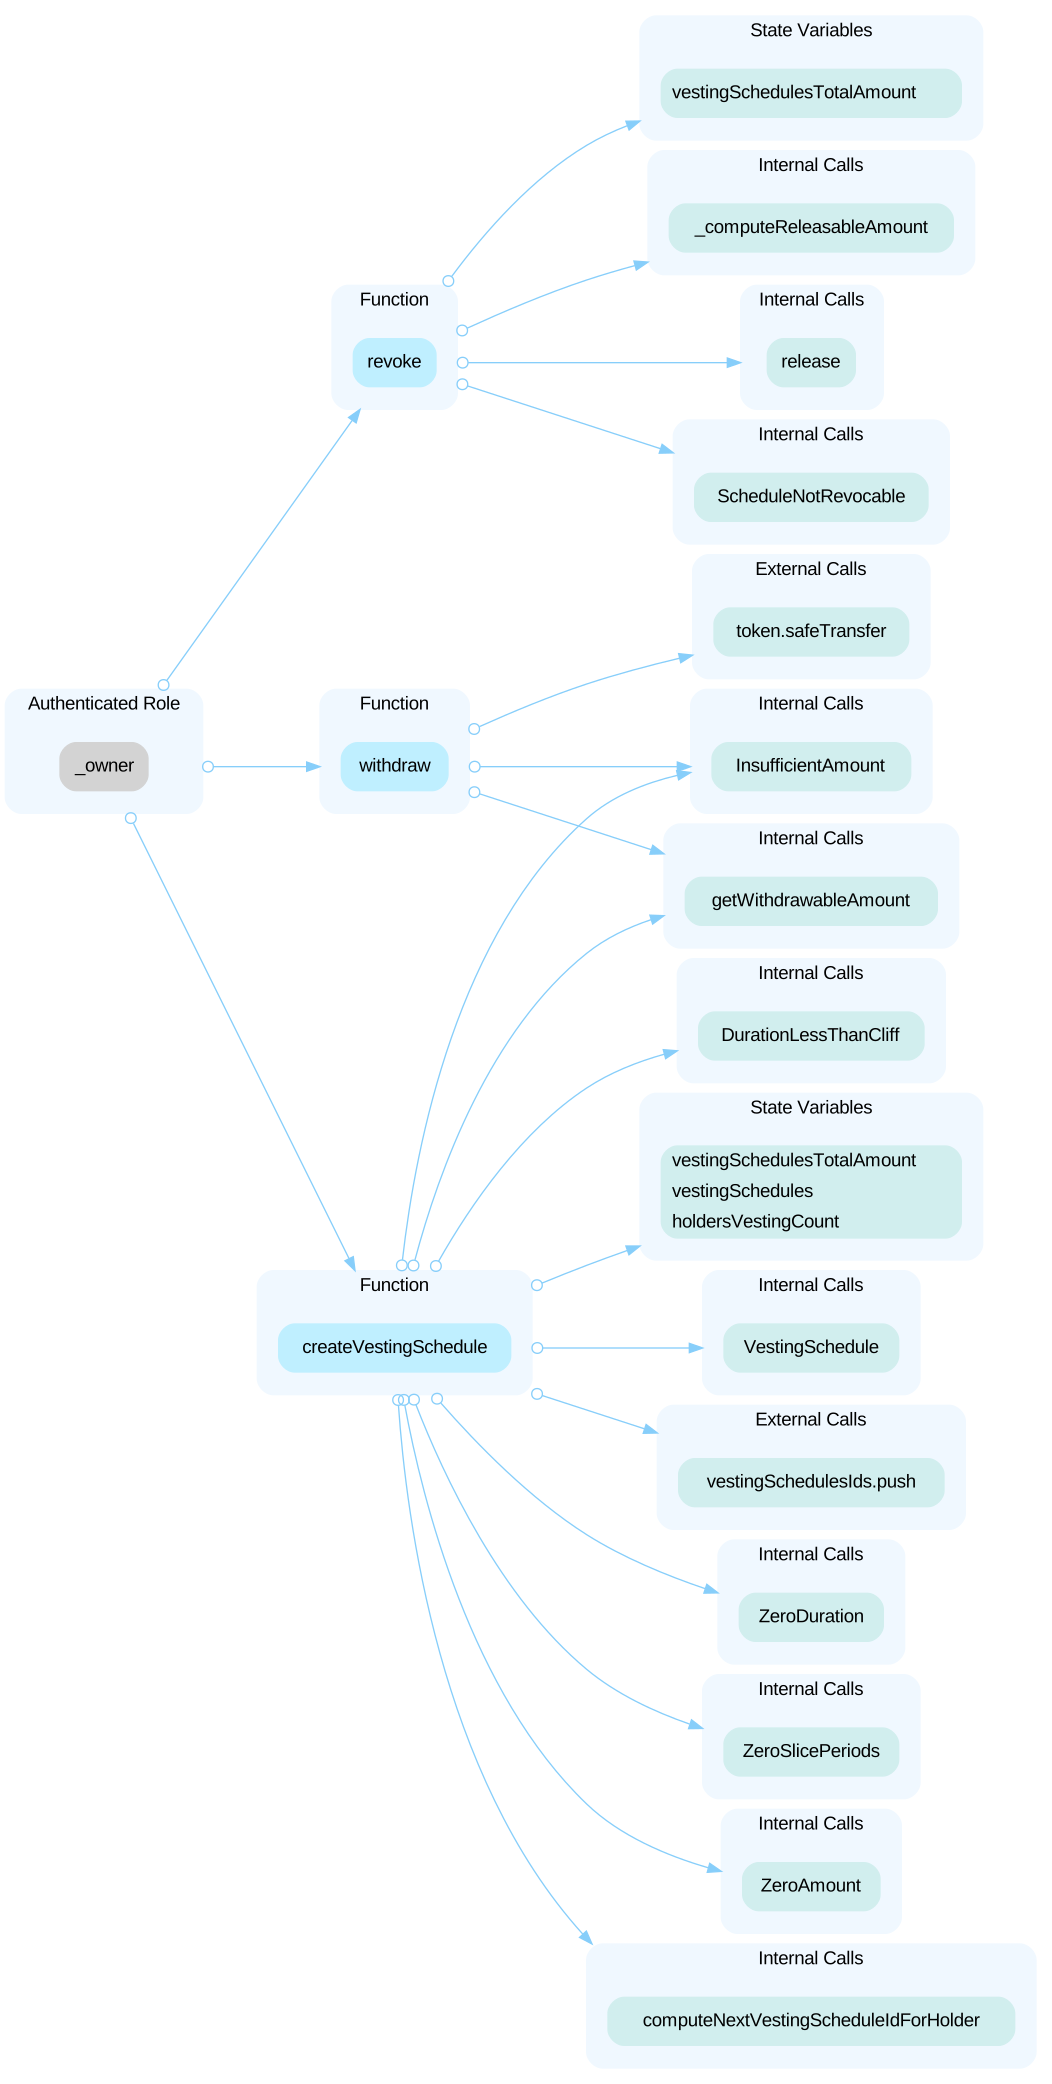 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and revoke a vesting schedule, create a vesting schedule for a beneficiary, and withdraw a specified amount safely.
HighInitial Token DistributionOpen
All initial IOSToken tokens (21,320,000,000) are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (4)
- https://github.com/gavin11599/iost-bsc-contract/contracts/IOSToken.sol at commit 3d5c25541db25314df32d5ea75a618d6a7b7a5b8
- https://github.com/gavin11599/iost-bsc-contract/contracts/Vesting.sol at commit 3d5c25541db25314df32d5ea75a618d6a7b7a5b8
- https://github.com/gavin11599/iost-bsc-contract/contracts/IOSToken.sol at commit e846518c3deae99c74a3c3c74a9d204827821e2a
- https://github.com/gavin11599/iost-bsc-contract/contracts/Vesting.sol at commit e846518c3deae99c74a3c3c74a9d204827821e2a
Part of IOST’s security record
 IOST
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us