Coinzix
CertiK reviewed Coinzix Token (Coinzix) on 28 Sep 2022: 15 findings, 2 critical; 7 marked fixed, 8 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings15
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 2 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 3 | 0 | 5 |
CriticalCentralization Risks in ICO.solOpen
In the contract `ICO` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, manage ICO & ICO status, set vesting and wallet, and transfer the token out of the contract. 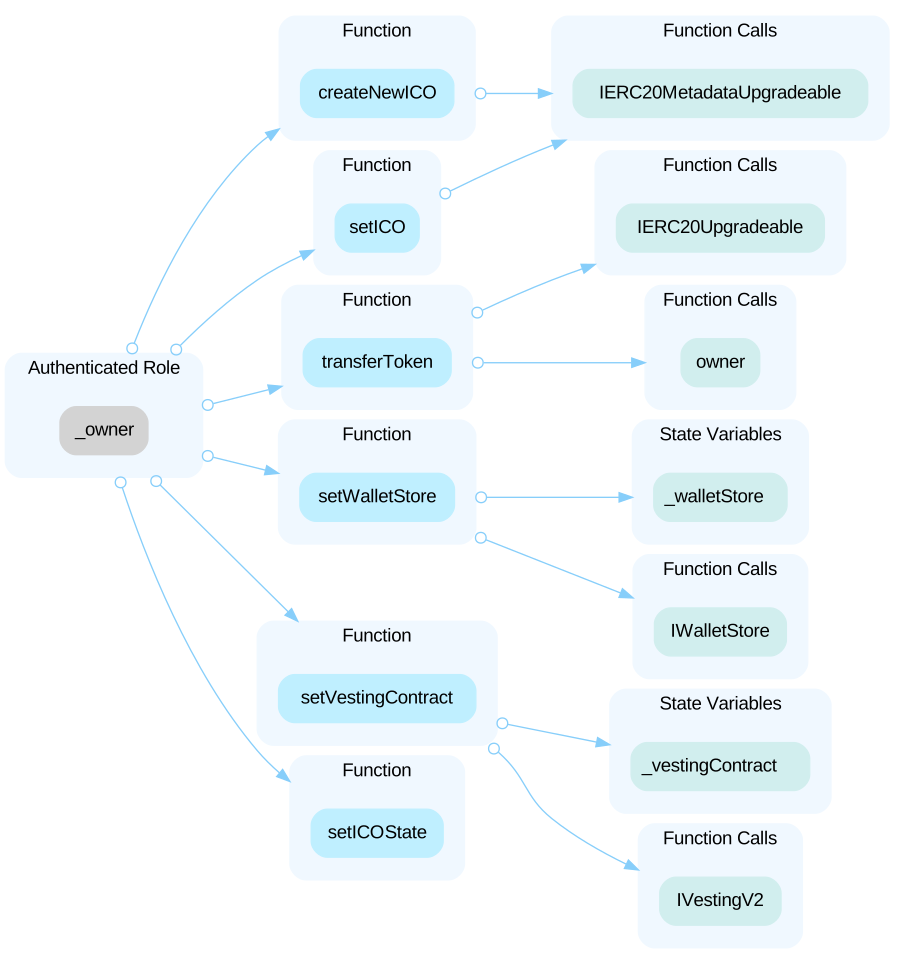
CriticalCentralization Risks in VestingV2.solOpen
In the contract `VestingV2` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, manage the vesting strategy, white list & token, revoke the user's vesting, and transfer the token to the owner. 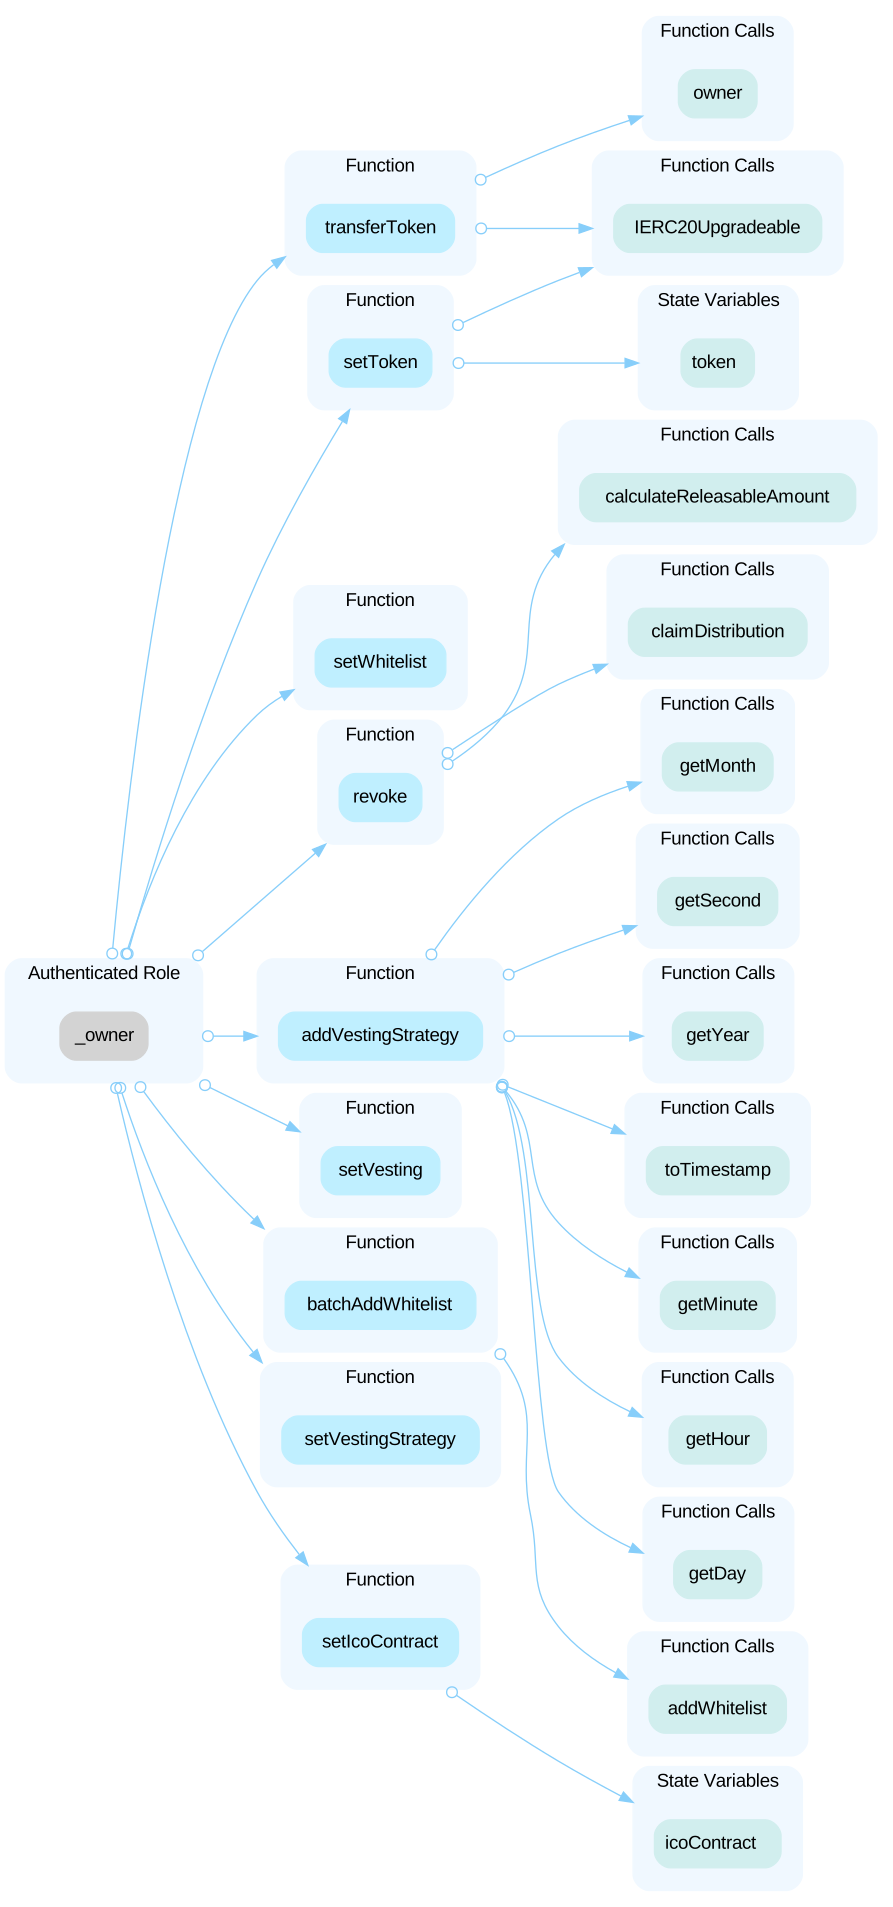
HighCentralization Risks in Walletstore.solOpen
In the contract `WalletStore` the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - `function setManager()` Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and change the manager. In the contract `WalletStore` the role `MANAGER_ROLE` has authority over the following functions: - `functoin batchAddUser()` - `function replaceUser()` - `function removeUser()` - `function addUser()` Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and manage the vesting users.
HighCentralized Control of Contract UpgradeOpen
Linked contracts are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
HighInitial Token DistributionOpen
All of the ZIX tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute ZIX tokens without obtaining the consensus of the community.
LowLack of Storage GapOpen
For upgradeable contracts, there must be storage gap to "allow developers to freely add new state variables in the future without compromising the storage compatibility with existing deployments". Otherwise it may be very difficult to write new implementation code. Without storage gap, the variable in child contract might be overwritten by the upgraded base contract if new variables are added to the base contract.
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowUnnecessary Use of SafeMathOpen
The `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow. ```solidity=12 using SafeMathUpgradeable for uint256; ``` - `SafeMath` library is used for `uint256` type in `ICO` contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (5)
- Token.sol
- IWalletStore.sol
- IVestingV2.sol
- DateTime.sol
- IICO.sol
Part of Coinzix Token’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us