PS.
CertiK reviewed Project SEED (PS.) on 4 Apr 2023: 24 findings, 4 critical; 6 marked fixed, 18 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings24
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 3 | 0 | 1 |
| High | 4 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 11 | 0 | 4 |
CriticalAll the staked funds can be stolen via `unstake()Open
`unstake(_amount)` decrements `stakeholder.staked` by `_amount`, however, `_withdrawStaked(stakeholder.staked)` is performed. So, all the `totalStaked` can be extracted by calls `unstake(1)`.
CriticalReward earning mechanism is flawedOpen
`stakeholder.timestamp` is used for both `_getTimeSinceStaked()` (as a first deposit time) and as last `claimReward()` call time. Consider the scenario: 1. The `duration` is 10 seconds. 1. User calls `stake(1)` at `startTime`. The user gets `stakedRatio = 10` and `timestamp = startTime`. 2. After 5 seconds user calls `stake(1000)`. The user gets `stakedRatio = 5010`. `timestamp` left intact. 3. Let's assume `rewardAmount == totalStakedRatio == 5010`. 4. `earned()` becomes `5010 * 5 / 10 = 2505`. 5. User can **immediately** `claimReward()` and get 2505 `rewardToken`. This is not expected by the contract logic. 6. `timestamp` becomes `startTime + 5`, and `stakedRatio` is still 5010. 7. After 5 seconds more user calls `claimReward()` and gets 5010 `rewardToken` **again**. `earned()` returns `5010 * 5 / 5`. This is not expected by the contract logic.
CriticalUnlimited reward can be extracted via `unstake()`Open
In `claimReward()` after the call `_withdrawReward()` the `stakeholder.timestamp` is updated to `block.timestamp`. That means that the reward was claimed until the current moment. However, in `unstake()` after the call `_withdrawReward()` the `stakeholder.timestamp` is not updated. That means, that by calling `unstake(1)` full `earned()` reward can be claimed multiple times.
HighCalling `claimReward()` after `stopTime` breaks uOpen
`claimReward()` sets `stakeholder.timestamp = block.timestamp`. Since `earned()` uses `stopTime - stakeholder.timestamp`, claiming the reward and unstaking becomes impossible if `claimReward()` was executed after `stopTime`.
HighCentralization Related RisksOpen
In the contract `ShillLock` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and drain all tokens by calling function `releaseTokens()`. 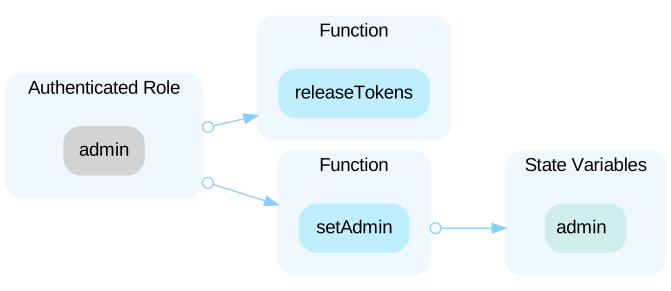 In the contract `NFTEngine` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and mint NFTs to attacker-controlled addresses by calling function `issueToken()` or `issueBatch()`. 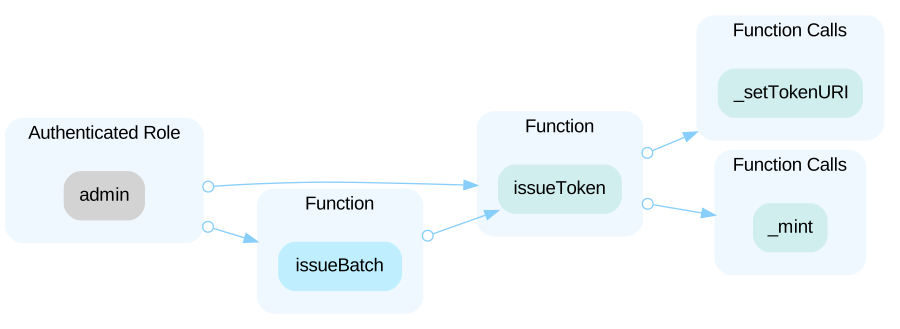 In the contract `Staking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and drain all tokens from the contract, as well as pause the main utility of the contract, keeping users from claiming rewards or unstaking their tokens. 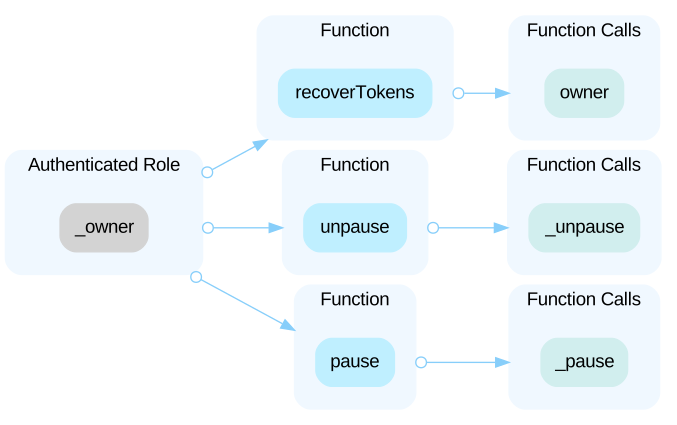 In the contract `CappableStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the cap amount, making it difficult for users to call `stake()`. 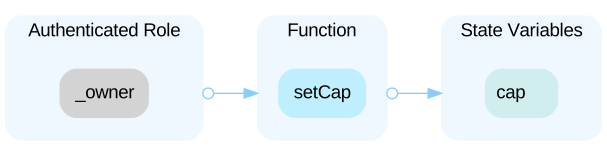 In the contract `AccessProtected` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set an attacker-controlled address as an admin or revoke original admins by calling function `setAdmin()`. 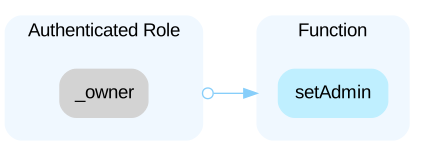
HighInitial Token DistributionOpen
Tokens are minted to the contract owner when deploying the contract. This is a centralization risk as the contract owner can distribute tokens without obtaining the consensus of the community.
HighOwner can extract all stakes via `recoverTokens()Open
`recoverTokens()` allows the contract owner to extract all funds including `rewardToken` and `stakingToken`. This will break the contract logic.
Low`if` condition will never be metOpen
The condition, ```solidity if (stakeholder.timestamp == 0) ``` will never be met, because in the previous line `stakeholder.timestamp` is set to `block.timestamp`. Therefore, the `if` block logic will never be executed.
Low`Withdraw` event uses `msg.sender` argumentOpen
```solidity=177 emit Withdraw(msg.sender, reward); ``` Event uses `msg.sender`, however, using of `_to` argument would be more accurate.
LowConditional operators can be simplifiedOpen
`getTimeRemaining()` and `getTimeElapsed()` are hard to read. Brackets or `if` statements can simplify the code logic.
Show 8 more
LowIncompatibility with Deflationary TokensOpen
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. ```solidity=96 IERC20(stakingToken).transferFrom(msg.sender, address(this), _amount); ``` - Transferring tokens by `_amount`. ```solidity=85 stakeholder.staked += _amount; ``` - The `_amount` appears to be used for bookkeeping purposes without compensating the potential transfer fees.
LowLack of Zero Address ValidationOpen
The cited functions lack important checks that the input addresses are never `address(0)`.
LowPotential Reentrancy in `stake()`Open
A reentrancy attack can occur when the contract creates a function that makes an external call to another untrusted contract before resolving any effects. If the attacker can control the untrusted contract, they can make a recursive call back to the original function, repeating interactions that would have otherwise not run after the external call resolved the effects. The `stake()` function calls `stakingToken` functions that potentially can lead to the execution of the attacker's code and re-entering other functions in `Staking` contract. This can lead to events reordering.
LowRedundant code in `unstake()`Open
```solidity=120 if(stakeholder.stakedRatio == 0){ stakeholder.timestamp = 0; } ``` `stakeholder.stakedRatio` will never be zero if something was staked for at least 1 second. The code is redundant and ambiguous.
LowStaking exactly at `stopTime` disallows to `unstaOpen
User is allowed to `stake()` at exactly `block.timestamp == stopTime`. If that is the first staking, `stakeholder.timestamp` is set to `block.timestamp`. This prevents the call to `_withdrawReward()` and to `unstake()` since `earned()` can't be calculated due to division by zero.
LowThe reward can't be claimed if not staking at theOpen
The user can't `claimReward()` and `earned()` returns 0, if `stakeholder.staked == 0`. Consider the scenario: 1. User stakes 100 tokens for 10 seconds, gets `stakeholder.stakedRatio += 1000` 2. After 5 seconds user withdraws 100 tokens, gets half of the reward - `earned()` returns 500, gets `stakeholder.stakedRatio -= 500` 3. After that 500 `stakeholder.stakedRatio` can't be claimed because `stakeholder.staked == 0`. 4. `stakedRatio` can still be claimed if `staked == 1`
LowThird Party DependencyOpen
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=11 IERC20 public immutable token; ``` - The contract `ShillLock` interacts with third party contract with `IERC20` interface via `token`. --- ```solidity=13 address public override stakingToken; ``` - The contract `Staking` interacts with third party contract with `IERC20` interface via `stakingToken`. --- ```solidity=14 address public override rewardToken; ``` - The contract `Staking` interacts with third party contract with `IERC20` interface via `rewardToken`. --- ```solidity=26 string memory hash ``` - The contract `NFTEngine` has functions `issueToken()` and `issueBatch()` which rely on a third party to provide input `hash` that is unique for the purposes of minting ERC721 tokens.
LowUnchecked ERC-20 `transfer()`/`transferFrom()` CaOpen
The return value of the transfer()/transferFrom() call is not checked. ```solidity=60 IERC20(rewardToken).transferFrom(msg.sender, address(this), rewardAmount); ``` --- ```solidity=66 _token.transfer(owner(), balance); ``` --- ```solidity=96 IERC20(stakingToken).transferFrom(msg.sender, address(this), _amount); ``` --- ```solidity=165 IERC20(stakingToken).transfer(_to, _amount); ``` --- ```solidity=170 IERC20(rewardToken).transfer(_to, reward); ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (7)
- solidity-contract/contracts/bridge-created by nonceblox/ShillLock.sol
- solidity-contract/contracts/utils/AccessProtected.sol
- solidity-contract/contracts/nftengine-created by nonceblox/NFTEngine.sol
- solidity-contract/contracts/staking-modified by ps/interfaces/IStaking.sol
- solidity-contract/contracts/shill erc20 -created by nonceblox/Shill.sol
- solidity-contract/contracts/staking-modified by ps/Staking.sol
- solidity-contract/contracts/staking-modified by ps/extensions/CappableStaking.sol
Part of Project SEED’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us