Metacraft.
CertiK reviewed MUMUBIT TOKEN (Metacraft.) on 5 Sep 2022: 36 findings, 5 critical; 19 marked fixed, 3 acknowledged, 14 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings36
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 5 |
| High | 8 | 0 | 1 |
| Medium | 0 | 3 | 1 |
| Low | 6 | 0 | 12 |
HighCentralization RiskOpen
In the contract, `MetaCraftAuction`, the role, `owner`, has the authority over the functions shown in the diagram below. Any compromise to the privileged account which has access to `owner` may allow the hacker to take advantage of this. 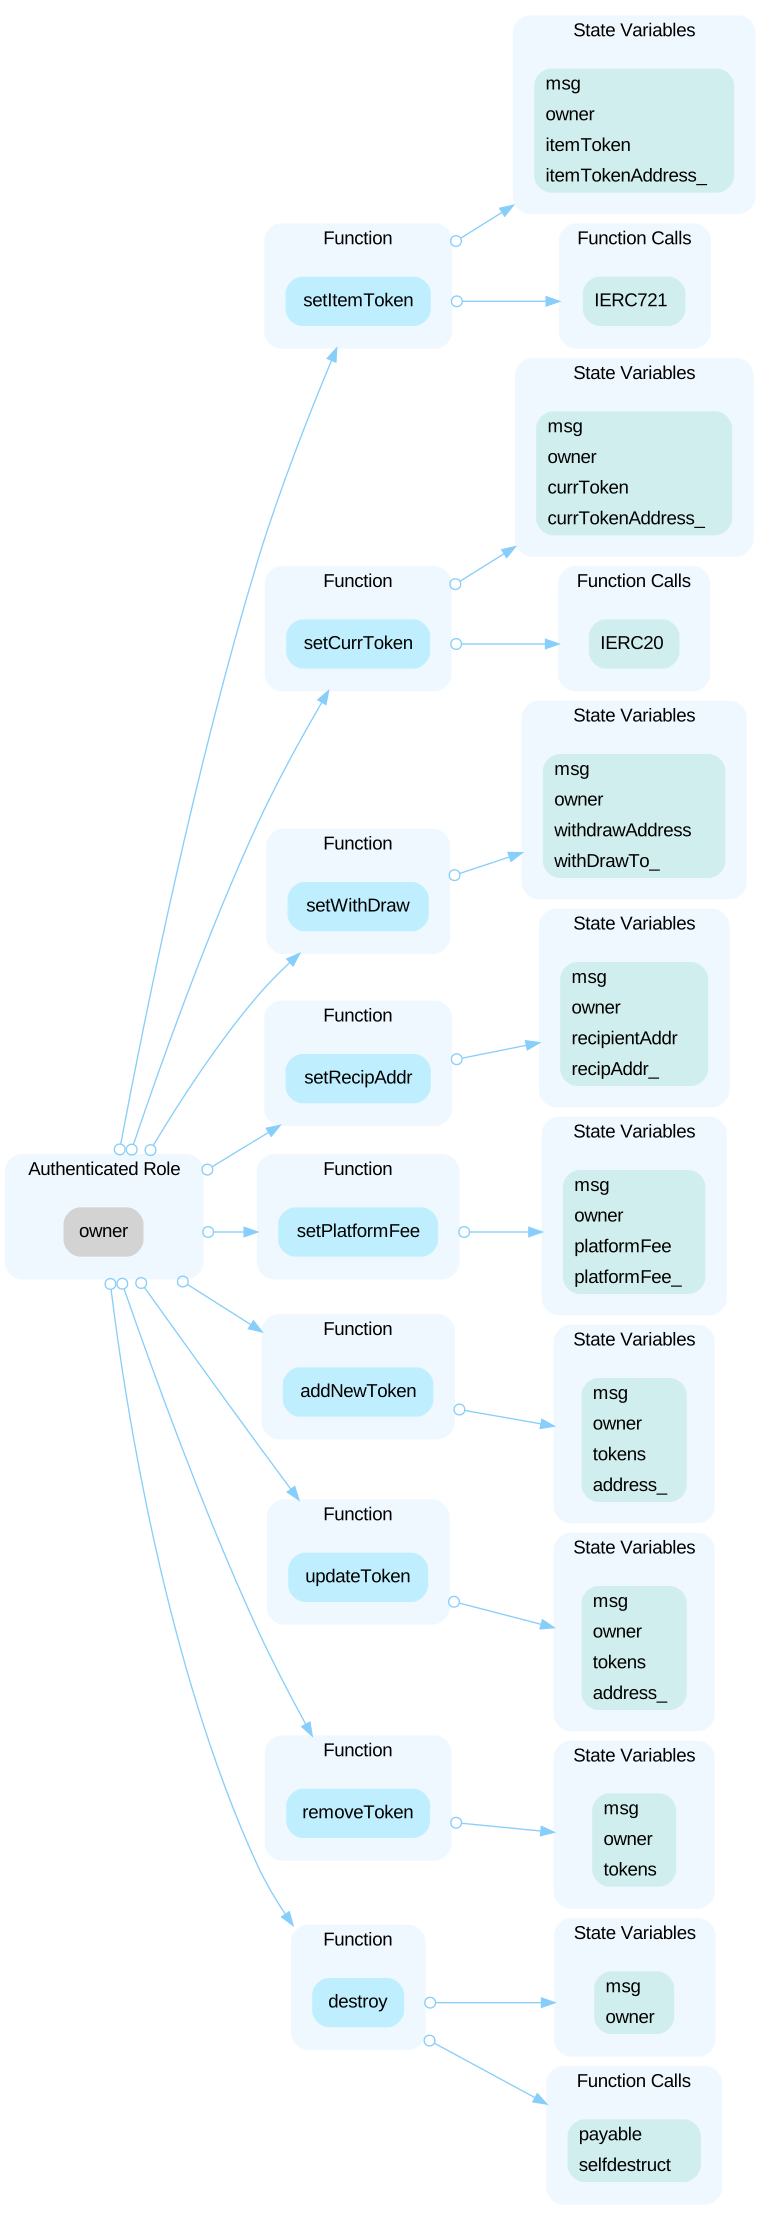 In the contract, `MetaCraftAuction`, the role, `withdrawAddress`, has the authority over the functions shown in the diagram below. Any compromise to the privileged account which has access to `withdrawAddress` may allow the hacker to take advantage of this. 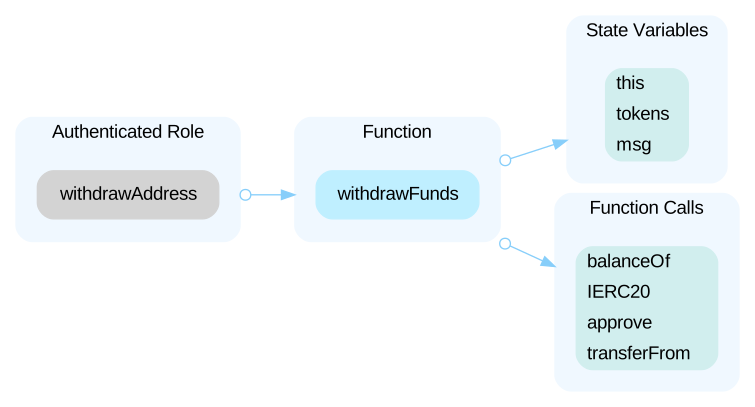
HighCentralization RiskOpen
In the contract, `MetaCraftItem`, the role, `owner`, has the authority over the functions shown in the diagram below. Any compromise to the privileged account which has access to `owner` may allow the hacker to take advantage of this. 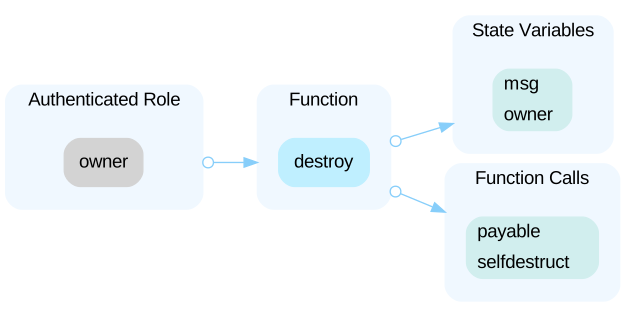
HighCentralization RiskOpen
In the contract, `MetaCraftTrade`, the role, `owner`, has the authority over the functions shown in the diagram below. Any compromise to the privileged account which has access to `owner` may allow the hacker to take advantage of this. 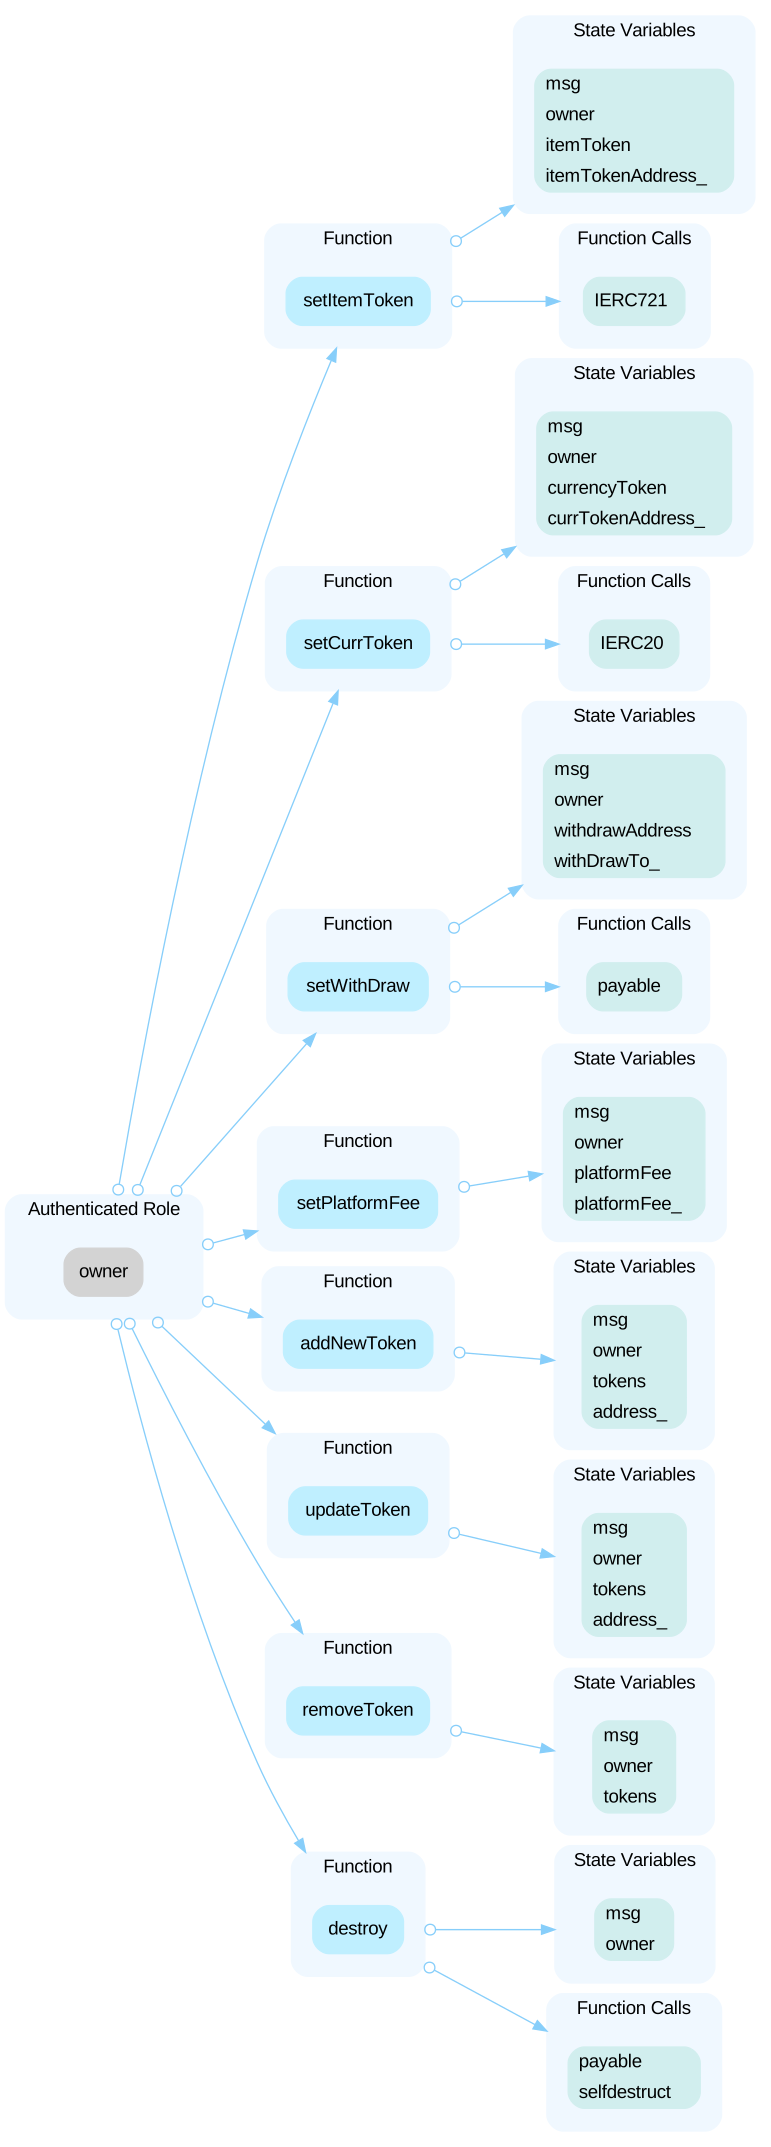 In the contract, `MetaCraftTrade`, the role, `withdrawAddress`, has the authority over the functions shown in the diagram below. Any compromise to the privileged account which has access to `withdrawAddress` may allow the hacker to take advantage of this. 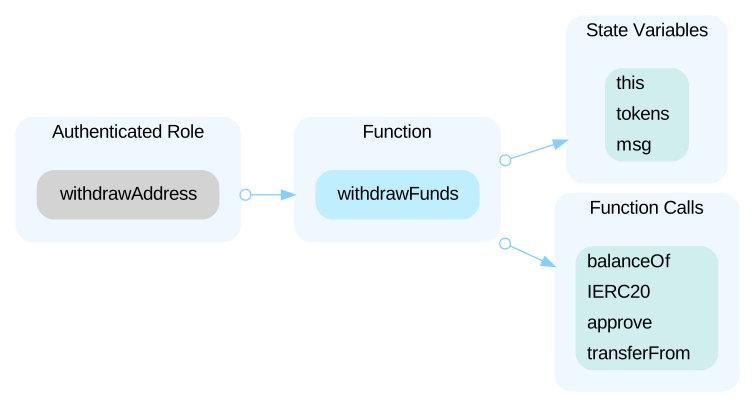
HighCentralization Risks in NFTS.solOpen
In the contract `Ownable` the role `owner_` has authority over the functions listed below: - `transferOwnership()`: transfer ownership to another account. Any compromise to the `owner_` account may allow the hacker to take advantage of this authority and change the configuration of the contract. In the contract `MyDelegated` the role `owner_` and `delegates` have authority over the functions listed below: - `setDelegate()`: set the delegates of an account. Any compromise to the `owner_` and `delegates` account may allow the hacker to take advantage of this authority and change the configuration of the contract. In the contract `MetaCraftToken` the role `owner_` has authority over the functions listed below: - `setEmergentHalt()`: manage the state variable `halted_`; - `transferAnyERC20Token()`: transfer assets to the `owner_`. Any compromise to the `owner_` account may allow the hacker to take advantage of this authority, change the configuration of the contract, and transfer assets. In the contract `MetaCraftToken` the role `delegates` has authority over the functions listed below: - `mint()`: mint tokens to an account; - `burn()`: burn tokens of an account. Any compromise to the `delegates` account may allow the hacker to take advantage of this authority, and mint/burn tokens of the contract. --- The following content is based on commit [b16c503fd485b16c30439befb11028b9e6739329](https://github.com/metacraftpro/metacontract/commit/b16c503fd485b16c30439befb11028b9e6739329). The team removed the contract `MyDelegated` and refactored the contract `Ownable`. In the contract `Ownable` the role `_owner` has authority over the functions listed below: - `renounceOwnership()`: renounce ownership of the contract; - `transferOwnership()`: transfer ownership to another account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the configuration of the contract. In the contract `MetaCraftToken` the role `_owner` has authority over the functions listed below: - `setEmergentHalt()`: manage the state variable `halted_`; - `mint()`: mint tokens to an account; - `burn()`: burn tokens of an account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, change the configuration of the contract, and mint/burn tokens of the contract. --- The following content is based on commit [e783b1a66bbe9a17bbc6e3ec747cfc2a4d4b32f3](https://github.com/metacraftpro/metacontract/tree/e783b1a66bbe9a17bbc6e3ec747cfc2a4d4b32f3). The team removed the `mint()` and `burn()` functions, and will distribute the initial tokens to `msg.sender`, which is a centralized risk on Initial Token Distribution.
HighInitial Token DistributionOpen
The following content is based on commit [e783b1a66bbe9a17bbc6e3ec747cfc2a4d4b32f3](https://github.com/metacraftpro/metacontract/tree/e783b1a66bbe9a17bbc6e3ec747cfc2a4d4b32f3). All of the MCTP tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute MCTP tokens without obtaining the consensus of the community.
HighLack of returning the NFTs to userOpen
It is needed to transfer all the NFTs back to the owners before calling the `destroy` function. Also for the ERC20 tokens in the contract.
HighMissing Check Existing TradeOpen
It is possible to add the same trade because the owner can change the NFT contract and different NFT contracts can generate the same NFT id. There is no check on the existing trade to avoid adding the same trade in the function `openTrade`. The staked nft in trade will be lost when the trade is overridden.
HighSide effect of updating the value of `itemToken`Open
Update the value of `itemToken` will cause the old trades in the `trades` array fail to be processed due to the failure of transferring the NFTs.
LowData overwritingOpen
The same NFT could be traded or canceled multiple times and its old data in the `trades` array will be overwrote by the new trading. Is that designed as expected?
LowEveryone Can Mint NFTOpen
Function `mintNFT` is public to anyone, without access limit, so anyone can call it to mint NFT. Is that designed as expected?
Show 4 more
LowMissing emit eventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowUnchecked Value of ERC-20 `transferFrom()` CallOpen
The linked `transferFrom()` invocations do not check the return value of the function call which should yield a `true` result in case of a proper ERC-20 implementation.
LowUnsafe ERC-721 `transferFrom()` CallOpen
The implementation of `transferFrom()` in openzeppelin does not check the return value of `IERC721Receiver-onERC721Received`. If the `to` address is a smart contract, the transferred nft token may be locked forever.
LowUser Can Buy Any Trade With `bnb`Open
In the function `executeTrade(uint256 _item)`, the symbol of the trade will not be checked and it means that user can buy any type of trade with `bnb`. Is that designed as expected?
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- MetaCraftItem.sol
- MetaCraftAuction.sol
- MetaCraftTrade.sol
Part of MUMUBIT TOKEN’s security record
 MUMUBIT TOKEN
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us