LandRocker - Audit
CertiK reviewed LandRocker (LandRocker - Audit) on 18 Jun 2024: 2 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings2
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 0 |
HighCentralization Risks in LRT.solAcknowledged
In the contract `LRT` the role `_distributor` has authority over the functions shown in the diagram below. Any compromise to the `_distributor` account may allow the hacker to take advantage of this authority and distribute tokens from the contract to any address. 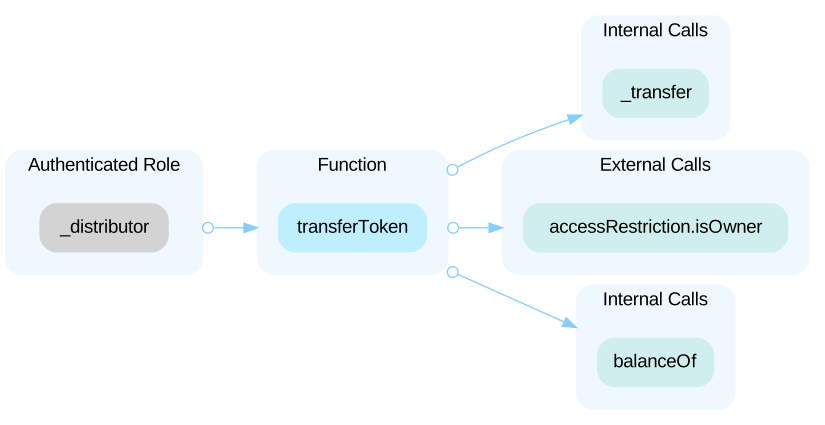
LowThird-Party Dependency UsageAcknowledged
The contract is serving as the underlying entity to interact with one or more out of scope protocols. The scope of the audit treats these entities as black boxes and assumes their functional correctness. However, in the real world, those contracts can be compromised and this may lead to lost or stolen assets. I ```solidity=26 IAccessRestriction public immutable accessRestriction; ``` - The contract `LRT` interacts with out of scope contract with `IAccessRestriction` interface via `accessRestriction`.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0xfb7f8a2c0526d01bfb00192781b7a7761841b16c | Chain: Polygon (POS) | Source code: Verified source |
Part of LandRocker’s security record
 LandRocker
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us