Pixer
CertiK reviewed PIXER on 12 Apr 2024: 5 findings, 0 critical; 1 acknowledged, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 1 | 0 |
| Low | 2 | 0 | 0 |
HighCentralization Risks in PIXER.solOpen
In the contract `BEP20Burnable` the role `_owner` has authority over the functions shown in the diagram below. 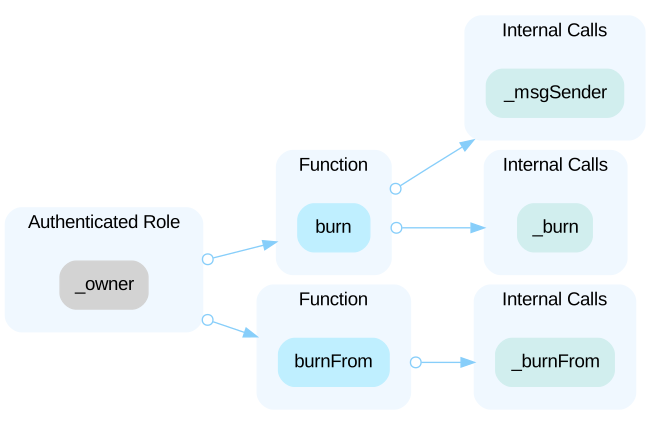 - `burn(uint256 amount)`: This function allows the owner to burn a specified amount of tokens from his/her own account, reducing the total supply. This action is only accessible by the contract owner. - `burnFrom(address account, uint256 amount)`: This function allows the owner to burn a specified amount of tokens from a specified account. Only the contract owner can call this function. --- In the contract `BEP20Lockable` the role `_owner` has authority over the functions shown in the diagram below. 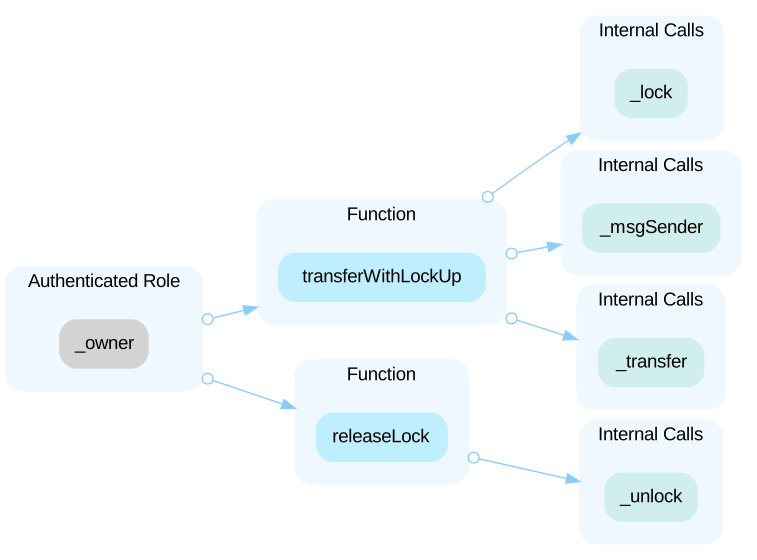 - `releaseLock(address from)`: This function allows the owner to release all locks on a specified address. It's accessible only to the contract owner. - `transferWithLockUp(address recipient, uint256 amount, uint256 due)`: This function allows the owner to transfer a specific amount of tokens to a recipient with a lockup period. Only the contract owner can call this function. --- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 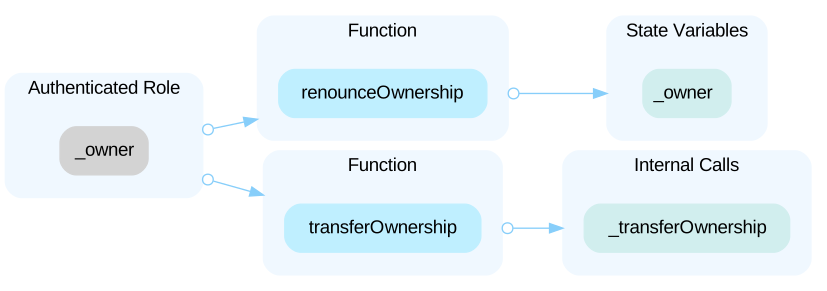 - `renounceOwnership()`: This function allows the current owner to relinquish the ownership of the contract. Only the current owner can call this function. - `transferOwnership(address newOwner)`: This function allows the current owner to transfer the ownership of the contract to a new owner. Only the current owner can call this function. --- Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project.
HighInitial Token DistributionOpen
All `PXT` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute `PXT` tokens without the consensus of the community.
LowBurn Tokens Without Checking Lock InfoOpen
The functions `transfer()` and `transferFrom()` are wrapped by the modifier `checkLock`, which ensures that locked tokens can not be used. However, the functions `burn()` and `burnFrom()` do not check whether the burnt tokens are locked or not.
LowUnnecessary Use of SafeMathOpen
The `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow. ```solidity=104 library SafeMath { ``` - An implementation of `SafeMath` library is found. --- ```solidity=245 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `BEP20` contract. *Note: Only a sample of 1 `SafeMath` library usage in this contract (out of 3) are shown above.* --- ```solidity=245 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `BEP20` contract. ```solidity=254 _totalSupply = _totalSupply.add(amount); ``` - `SafeMath.add` is called in `_mint` function of `BEP20` contract. *Note: Only a sample of 2 `SafeMath` library usage in this contract (out of 10) are shown above.* --- ```solidity=245 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `BEP20` contract. ```solidity=513 _approve(from, _msgSender(), _allowances[from][msg.sender].sub(amount)); ``` - `SafeMath.sub` is called in `transferFrom` function of `PIXER` contract. *Note: Only a sample of 2 `SafeMath` library usage in this contract (out of 6) are shown above.*
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0xeb79c85c6d633ae81c97be71e1691ee7dc6e132d | Chain: BNB Chain | Source code: Verified source |
Part of PIXER’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us