Welthee
CertiK reviewed Welthee on 6 Sep 2022: 6 findings, 1 critical; all marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 0 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 4 |
CriticalCentralization Risks in InsuredTokenSale.solFixed
In the contract `InsuredTokenSale` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and withdraw all the tokens owned by the contract from any `ERC20` contract, then transfer these funds from the `_owner` account to their own account. 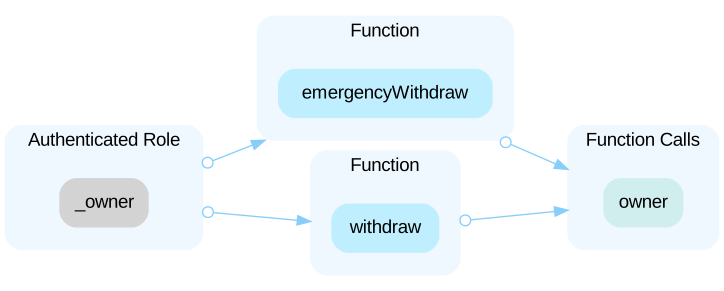
MediumNo Tokens Transferred To The ContractFixed
The linked functions attempt to transfer `ERC20` tokens out of this contract to EOA's and vesting contracts. This contract never explicitly receives tokens and as a result, it will most likely revert during balance checks and token transfers.
LowMissing Emit EventsFixed
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowPotential Cross-chain Replay AttackFixed
Within the current contract, there is no distinction between the different blockchains supported by the `Welthee` project. If the signer signed a message on one chain (e.g. Ethereum), and accidentally leaks the message, the message would be valid for a similar transaction of a chain with the same encryption method (e.g. BSC). For example, if the signer signed a message using `encodeClaimHash(ClaimParam memory claimInfo)` on Ethereum and the same `claimInfo.investor` and `claimInfo.id` exists on BSC, the attacker can reuse this signed message to maliciously claim tokens with `claim()` on BSC.
LowUnhandled Expiry Time CaseFixed
Neither of the `if` statements in the function `isAvailableToClaim()` check whether `orders[investor][id].insuranceExpiryTime` is equal to `block.timestamp`. The order will have neither a claim type of `INSURANCE` nor `TOKEN` in this case even if the order has not been claimed before.
LowUnused ContractFixed
```solidity=4 library AddressesArray { ``` - The library `AddressesArray` is included in the audit scope but is never used by the other contracts.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- token-sale/contracts/Libraries.sol
- token-sale/contracts/Interfaces.sol
- token-sale/contracts/InsuredTokenSale.sol
Part of Welthee’s security record
 Welthee
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us