Geodnet
CertiK reviewed Geodnet on 12 Apr 2024: 4 findings, 0 critical; all marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 0 | 2 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 1 |
HighCentralization Related RisksFixed
In the contract `XToken` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set the token supply cap and pause/unpause token transfers. 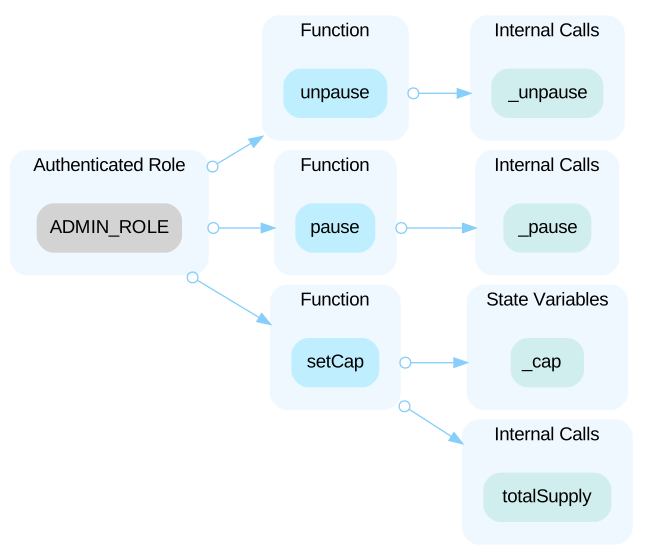 In the contract `XToken` the role `BLACKLISTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BLACKLISTER_ROLE` account may allow the hacker to take advantage of this authority and add/remove addresses from the blacklist. 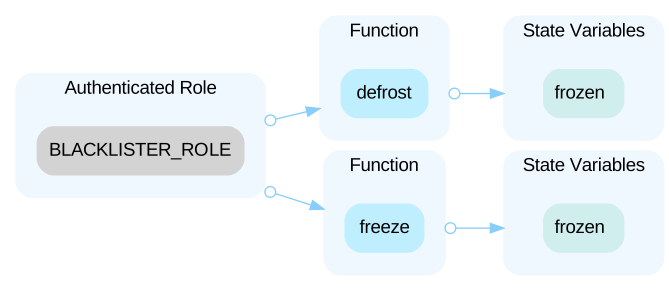 In the contract `XToken` the role `BURNER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BURNER_ROLE` account may allow the hacker to take advantage of this authority and burn tokens. 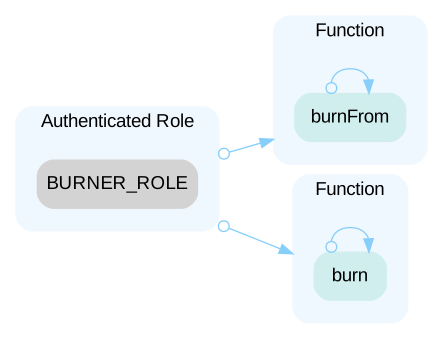 In the contract `XToken` the role `MINTER_ROLE` has authority over the function shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens. 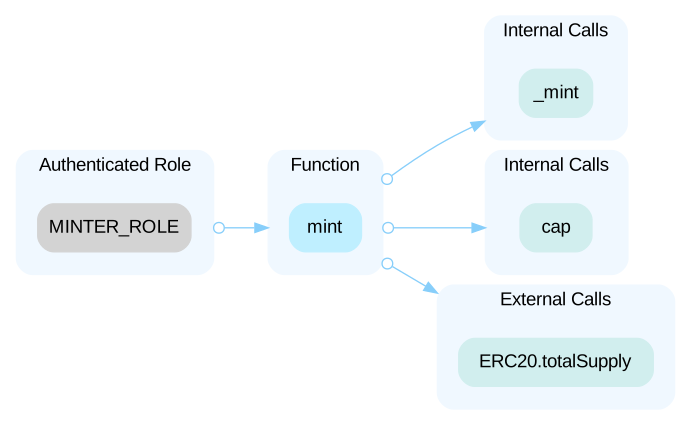 ---- In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts.
HighCentralized Balance ManipulationFixed
In the `XToken` contract, the `MINTER_ROLE` is authorized to mint tokens to any account, with the minting amount limited only by the `totalSupply` reaching the `_cap`. It's crucial to note that the `_cap` can be adjusted by the `ADMIN_ROLE`. Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and manipulate users' balances. For example, The hacker could also update his/her balance to a large number, sell these tokens, and cause the token price to drop.
MediumIncorrect Role ManagementFixed
The `RoleAccess` contract is meant to handle role and permission management in a system but shows a mismatch in how roles are administered. For example, while functions like `grantMinter()` are supposed to be controlled by accounts with the `ADMIN_ROLE`, they require the corresponding role's admin due to the underlying `AccessControl` contract's implementation. This issue arises because the `grantRole()` function, used within `grantMinter()`, requires the caller to be the admin of the role being granted. This is determined by `getRoleAdmin(role)`. Yet, in this contract, `DEFAULT_ADMIN_ROLE` serves as the admin for all roles, meaning it alone has the authority to grant or revoke roles. As a result, the following functions with `onlyAdmin` modifier in the `RoleAccess` contract do not work as intended: - addRoleMember() - removeRoleMember() - grantMinter() - revokeMinter() - grantBurner() - revokeBurner() - grantGranter() - revokeGranter() - grantBlacklister() - revokeBlacklister() ```solidity=95 function grantMinter(address minter) external onlyAdmin returns (bool) { grantRole(MINTER_ROLE, minter); return true; } ``` ```solidity function grantRole(bytes32 role, address account) public virtual override onlyRole(getRoleAdmin(role)) { _grantRole(role, account); } ```
LowIncorrect CommentsFixed
The comments for the following functions are incorrect. The functions are used to set "granters" instead of "burners". ```solidity=118 // assign burner role to another EOA or smart contract function grantGranter(address granter) external onlyAdmin returns (bool) { grantRole(GRANTER_ROLE, granter); return true; } // revoke burner role to another EOA or smart contract function revokeGranter(address granter) external onlyAdmin returns (bool) { revokeRole(GRANTER_ROLE, granter); return true; } ```
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0xac0f66379a6d7801d7726d5a943356a172549adb | Chain: Polygon (POS) | Source code: Verified source |
Part of Geodnet’s security record
 Geodnet
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us