Wemix Retainer 65 DEX V2
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 65 DEX V2) on 31 Oct 2023: 16 findings, 0 critical; 10 marked fixed, 6 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings16
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 4 | 0 | 9 |
HighCentralization Related RisksOpen
In the contract `DEXConfig` the role `GOVERNOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `GOVERNOR_ROLE` account may allow the hacker to take advantage of this authority and set the minimum order amount of tokens. 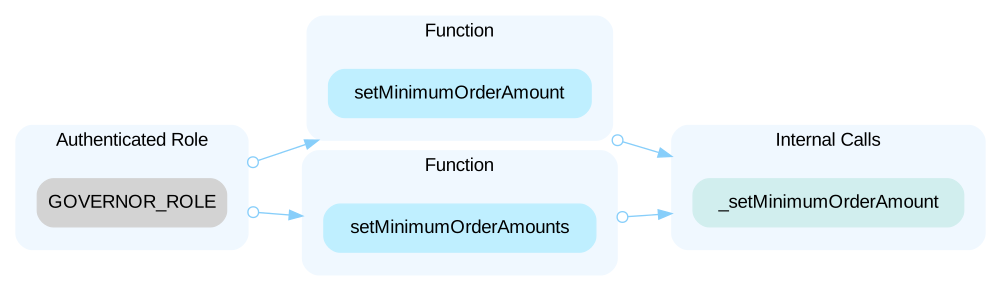 In the contract `DEXConfig` the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and set whitelist workers. 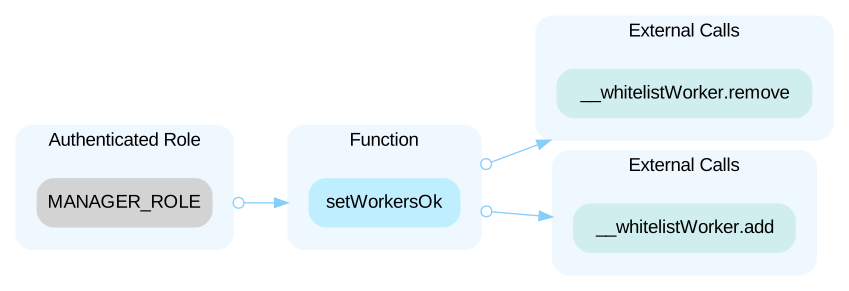 In the contract `DEXConfig` the role `MASTER_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set the dev address, set `maxExchangeLoop`, `maxFindPrice`, `maxNearPrices`, and `escrow` and upgrade the contract 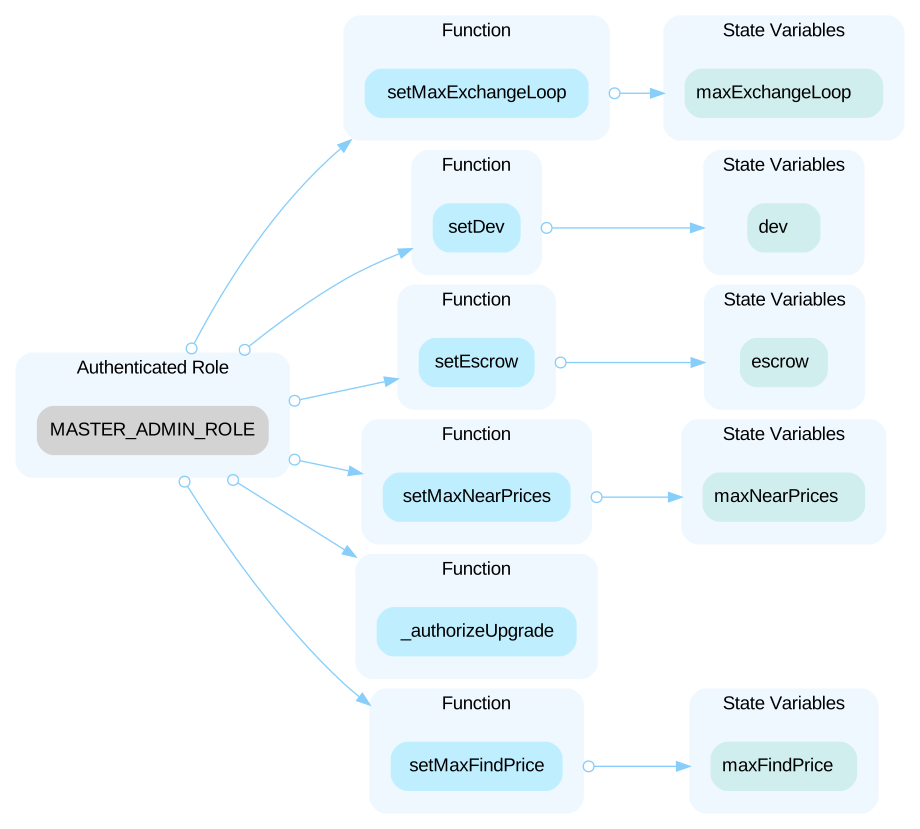 ----- In the contract `Factory` the role `GOVERNOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `GOVERNOR_ROLE` account may allow the hacker to take advantage of this authority and pause/unpause the pair and set base/quote unit. 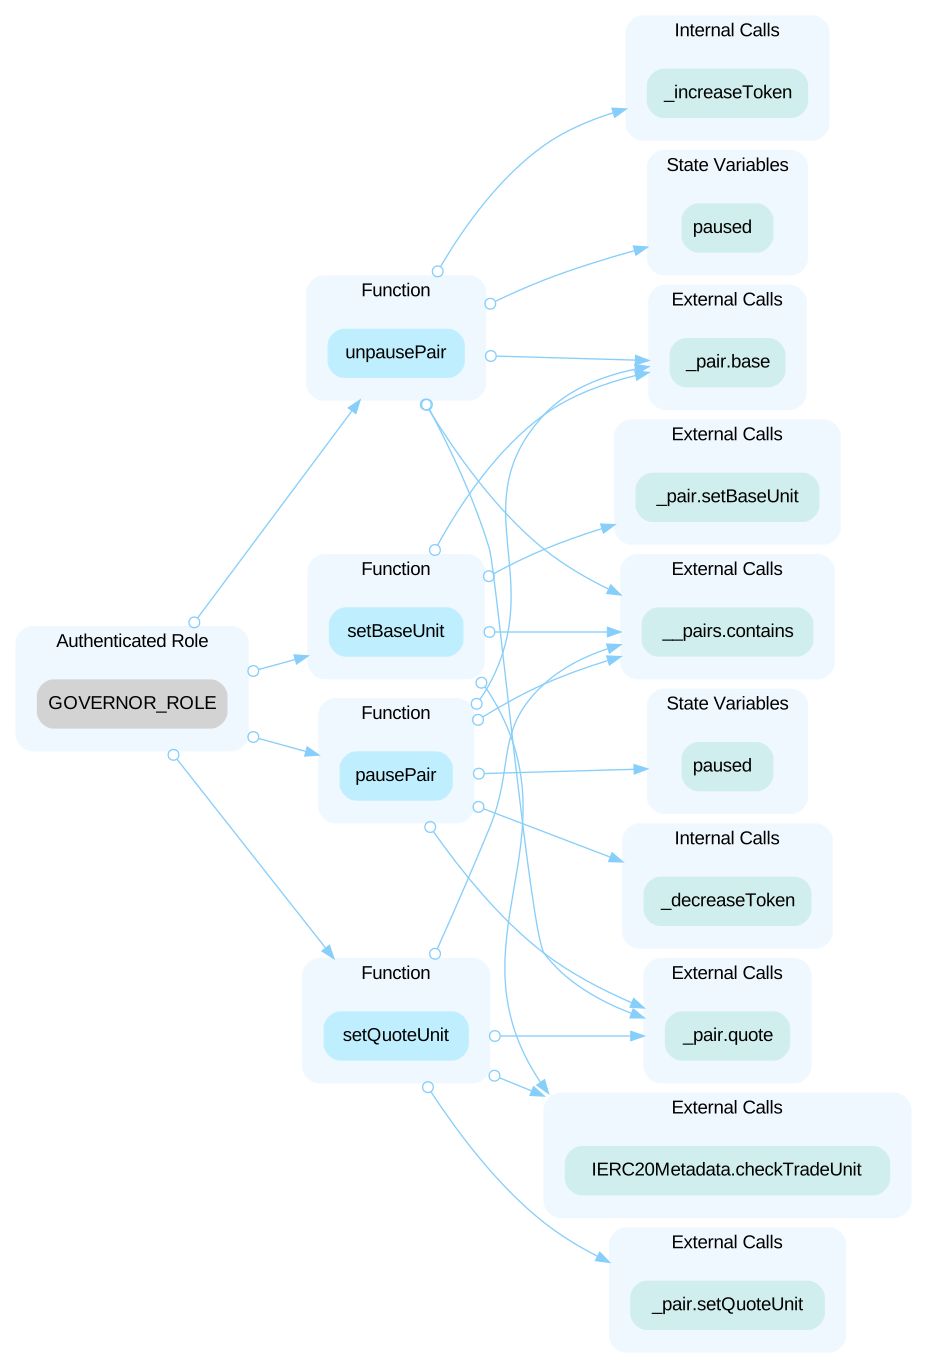 In the contract `Factory` the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and create a new pair. 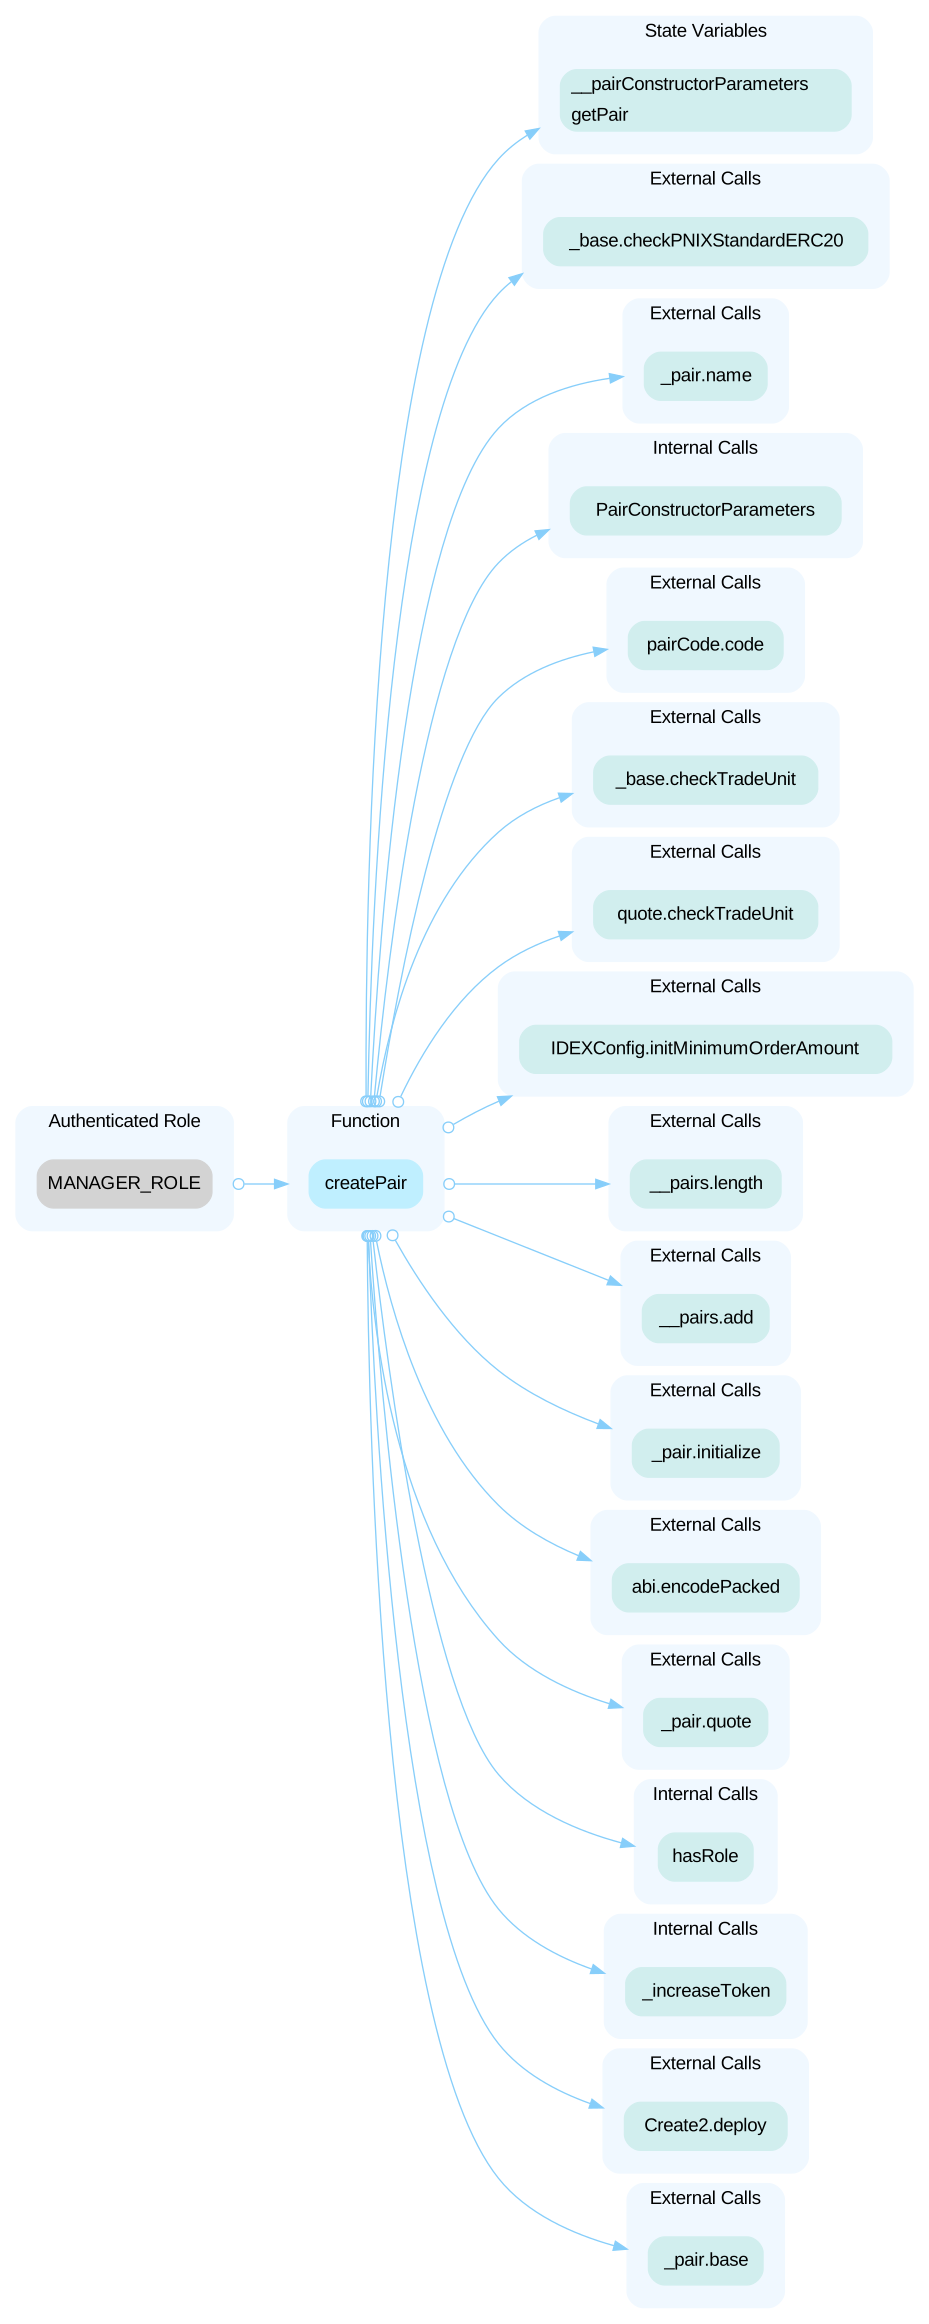 In the contract `Factory` the role `MASTER_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set components and routers. 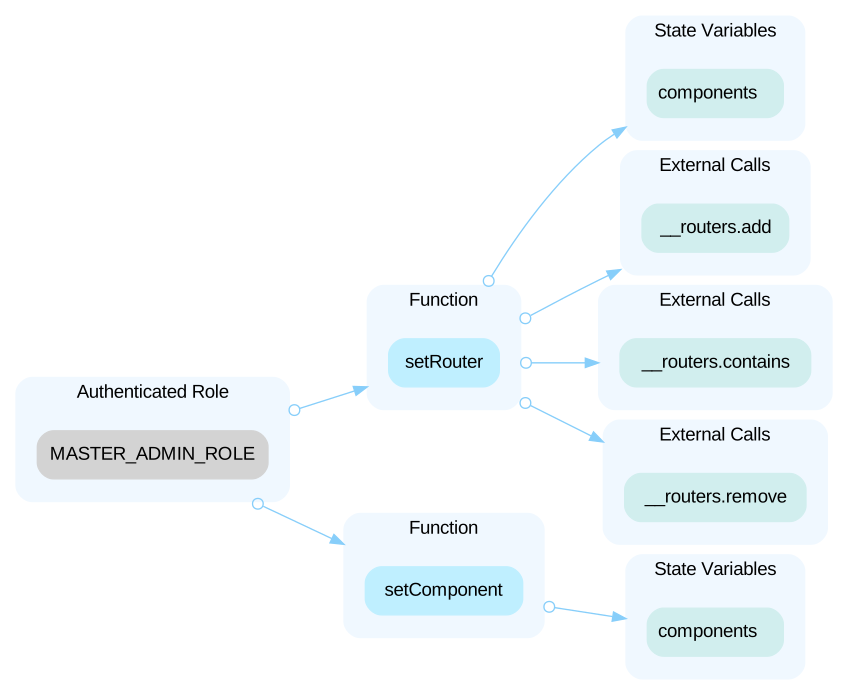 In the contract `Factory` the role `PAIR_CREATOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAIR_CREATOR_ROLE` account may allow the hacker to take advantage of this authority and create a new pair. 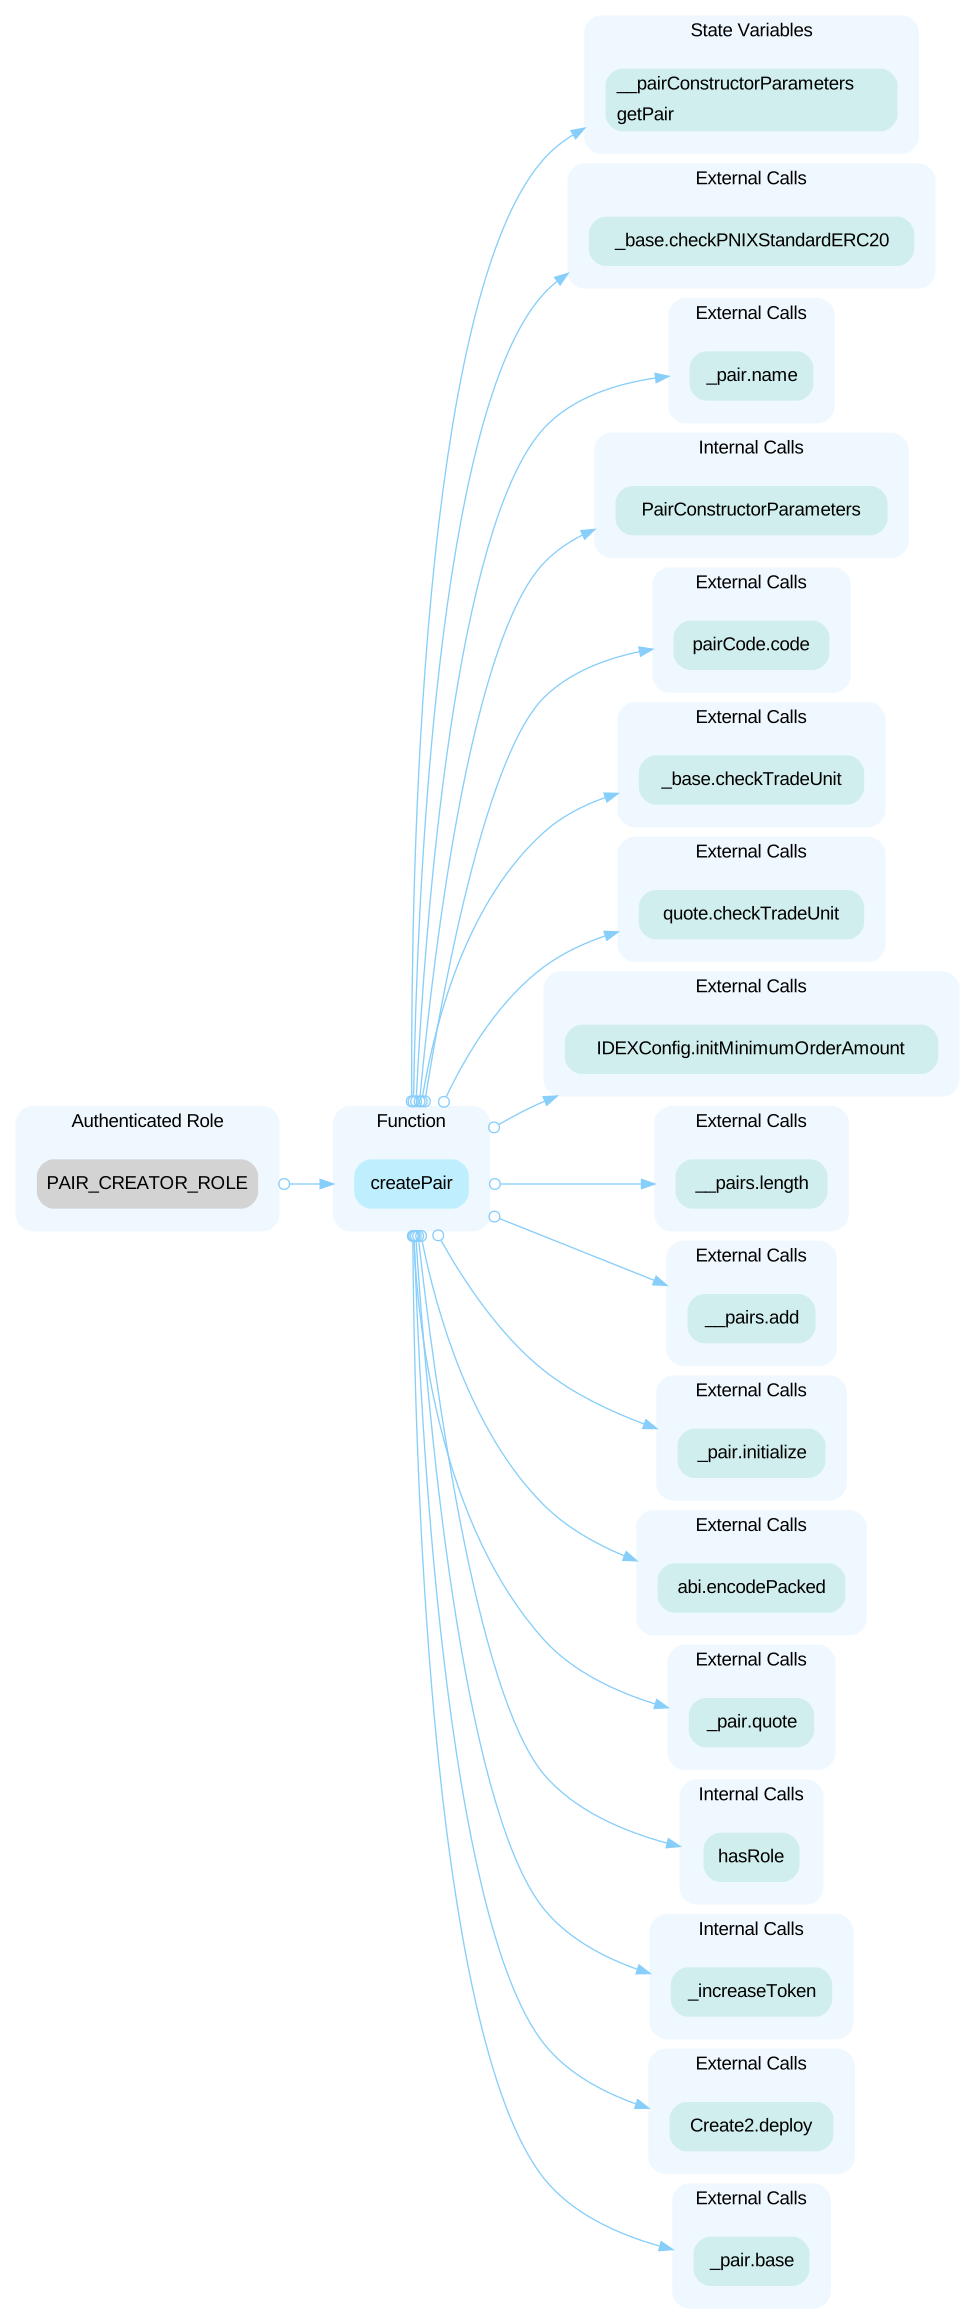 In the contract `Factory` the role `_role` has authority over the functions shown in the diagram below. Any compromise to the `_role` account may allow the hacker to take advantage of this authority and set role admin. 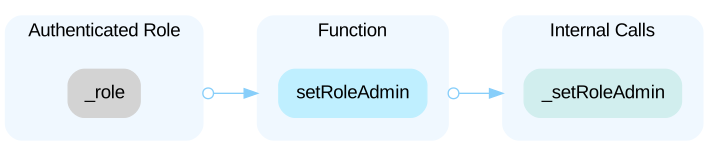 ----- In the contract `FeeStation` the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and update fees. 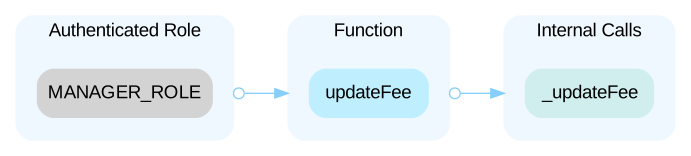 In the contract `FeeStation` the role `MASTER_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and upgrade the contract. 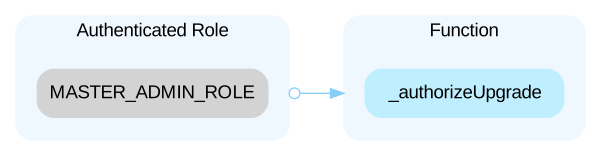 ----- In the contract `Reward` the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and set `mintingRateM` and `mintingRateMByPair`. 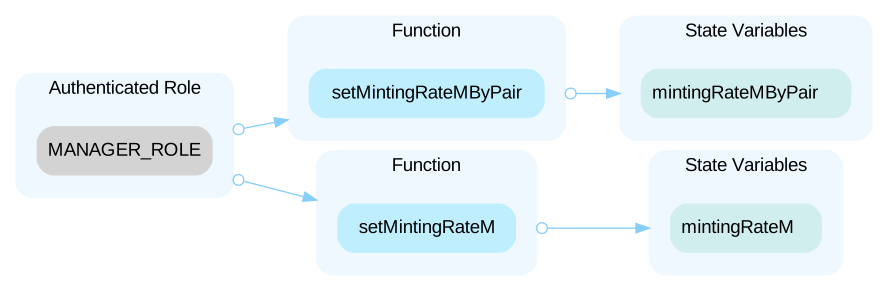 In the contract `Reward` the role `MASTER_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and upgrade the contract. 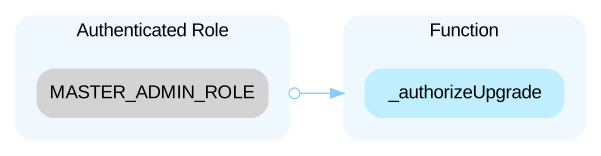 ----- In the contract `Router` the role `MANAGER_ROLE
HighCentralized Control of Contract UpgradeOpen
In the contract `DEXConfig`, `FeeStation`, `Reward`, and `Router`, the role `MASTER_ADMIN_ROLE` has the authority to update the implementation contract behind these contracts. Any compromise to the `MASTER_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
LowIncompatibility with Deflationary TokensOpen
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction.
LowPotential Out-of-Gas ExceptionOpen
When a loop allows an arbitrary number of iterations or accesses state variables in its body, the function may run out of gas and revert the transaction. ```solidity=386 for (uint i = 0; i < _nearPricesLen; ) { ``` Function `Pair.findNextPrice` contains a loop and its loop condition depends on external calls: `Math.min`. --- ```solidity=407 for (; _price < _next; _next = _sideWards[_next].next) require(--_findGas > 0, "failed to find next price forward BUY"); ``` Function `Pair.findNextPrice` contains a loop and its loop condition depends on parameters: `_price`. --- ```solidity=409 for (; _price > _next; _next = _sideWards[_next].next) require(--_findGas > 0, "failed to find next price forward SELL"); ``` Function `Pair.findNextPrice` contains a loop and its loop condition depends on parameters: `_price`. --- ```solidity=414 for (; _price > _next; _next = _sideWards[_next].prev) require(--_findGas > 0, "failed to find next price backward BUY"); ``` Function `Pair.findNextPrice` contains a loop and its loop condition depends on parameters: `_price`. --- ```solidity=416 for (; _price < _next; _next = _sideWards[_next].prev) require(--_findGas > 0, "failed to find next price backward SELL"); ``` Function `Pair.findNextPrice` contains a loop and its loop condition depends on parameters: `_price`. --- ```solidity=59 while (_maker.id != _oppositeTail) { ``` Function `Simulator._simulateAmount` contains a loop and its loop condition depends on external calls: `_pair.orderByID`. --- ```solidity=78 while (_maker.id != _oppositeTail) { ``` Function `Simulator._simulateValue` contains a loop and its loop condition depends on external calls: `_pair.orderByID`. --- ```solidity=45 for (uint i = 0; i < _pairs.length; i++) { ``` Function `TokenViewer.getBalances` contains a loop and its loop condition depends on parameters: `_pairs`. --- ```solidity=67 for (uint i = 0; i < _pairsLength; i++) { ``` Function `TokenViewer.getBalancesAll` contains a loop and its loop condition depends on external calls: `__factory.pairsLength`.
LowThe use of the parameter `_traderType`Open
The function `rewardTrade()` includes a parameter `_traderType`, yet it remains unused within the function.
LowThird-Party Dependency UsageOpen
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=26 IFactory private __factory; ``` - The contract `FeeStation` interacts with the third-party contract with `IFeePass` interface via `__factory`. ```solidity=43 _poet.claim(); ``` - The contract `PoetTreasury` interacts with the third-party contract with `IPoet` interface.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (29)
- contracts/interfaces/IWorker.sol
- contracts/interfaces/IFeePass.sol
- contracts/Router.sol
- contracts/interfaces/IFaucet.sol
- contracts/interfaces/IRouter.sol
- contracts/interfaces/IWETH.sol
- contracts/periphery/TokenViewer.sol
- contracts/DEXConfig.sol
- contracts/interfaces/IFactory.sol
- contracts/libraries/PairConst.sol
- contracts/interfaces/IReward.sol
- contracts/Reward.sol
- contracts/interfaces/ISimulator.sol
- contracts/Pair.sol
- contracts/Rewarder.sol
- contracts/Mileage.sol
- contracts/periphery/PairViewer.sol
- contracts/libraries/DEXLibrary.sol
- contracts/interfaces/IGovToken.sol
- contracts/interfaces/IMileage.sol
- contracts/interfaces/IPair.sol
- contracts/interfaces/IDEXConfig.sol
- contracts/interfaces/IPoet.sol
- contracts/FeeStation.sol
- contracts/interfaces/IFeeStation.sol
- contracts/Factory.sol
- contracts/FeePass.sol
- contracts/periphery/PoetTreasury.sol
- contracts/WETH.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us