Wemix Retainer 53 (Championship TicketNFT)
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 53 (Championship TicketNFT)) on 11 Sep 2023: 8 findings, 0 critical; 4 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 2 | 0 | 3 |
HighCentralization Related RisksOpen
In the contract `BenefitBase` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and modify the configuration of the contract. 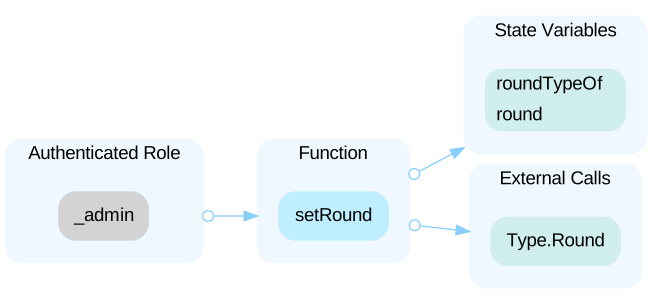 ----- In the contract `BenefitBox` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and modify the important configurations of the contract. 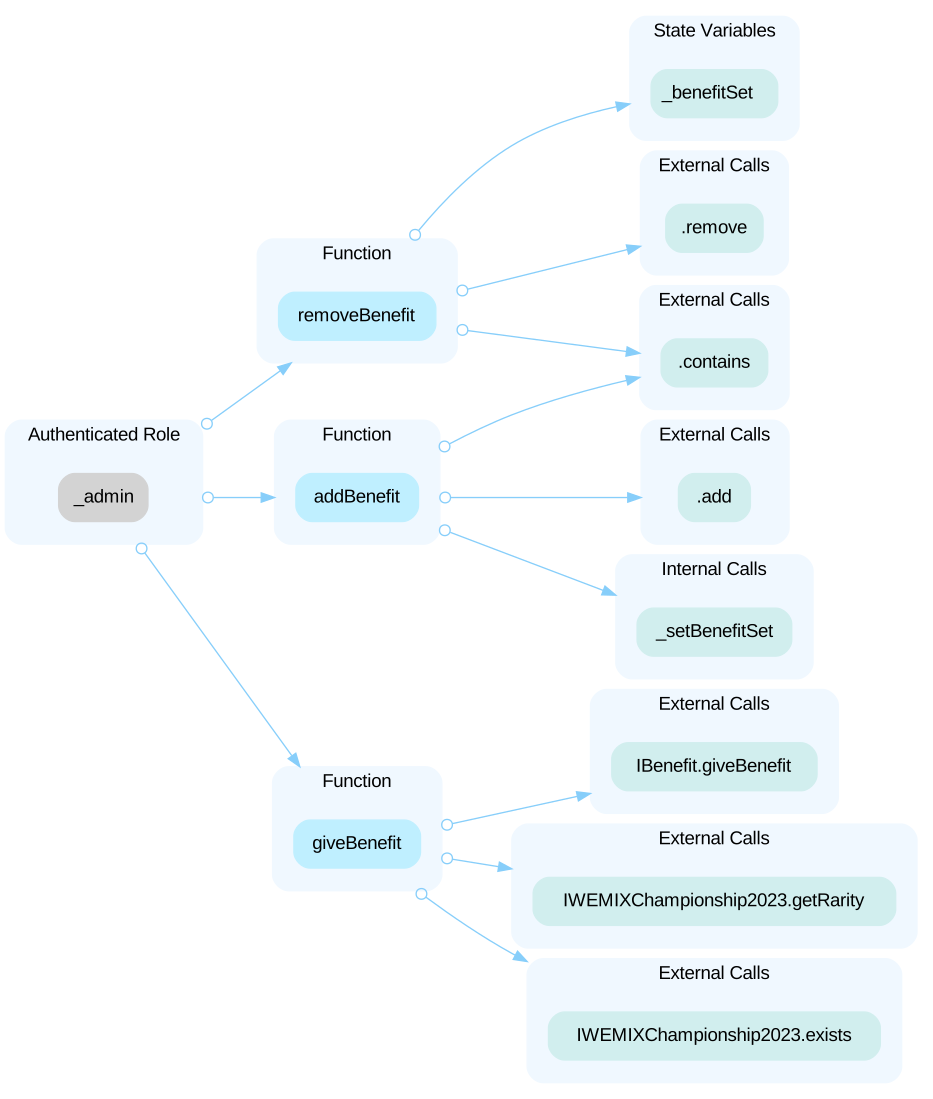 In the contract `BenefitBox` the role `_store` has authority over the functions shown in the diagram below. Any compromise to the `_store` account may allow the hacker to take advantage of this authority and use/unuse and give benefits. 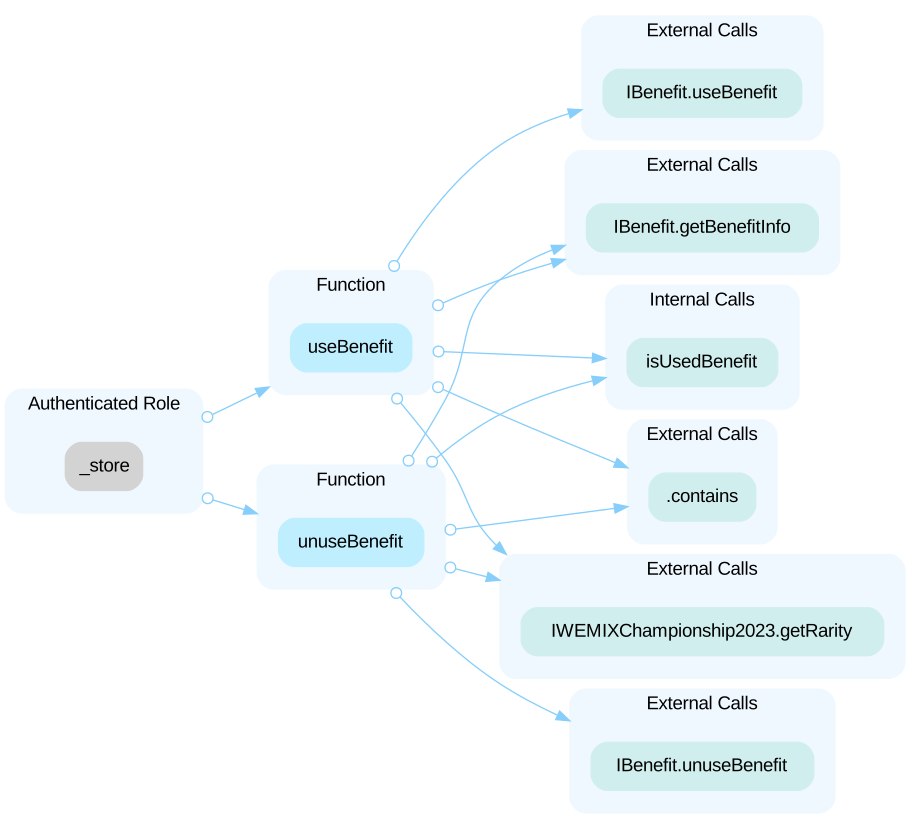 ----- In the contract `FreeDrink` the role `_benefitbox` has authority over the functions shown in the diagram below. Any compromise to the `_benefitbox` account may allow the hacker to take advantage of this authority and use/unuse and give benefits. 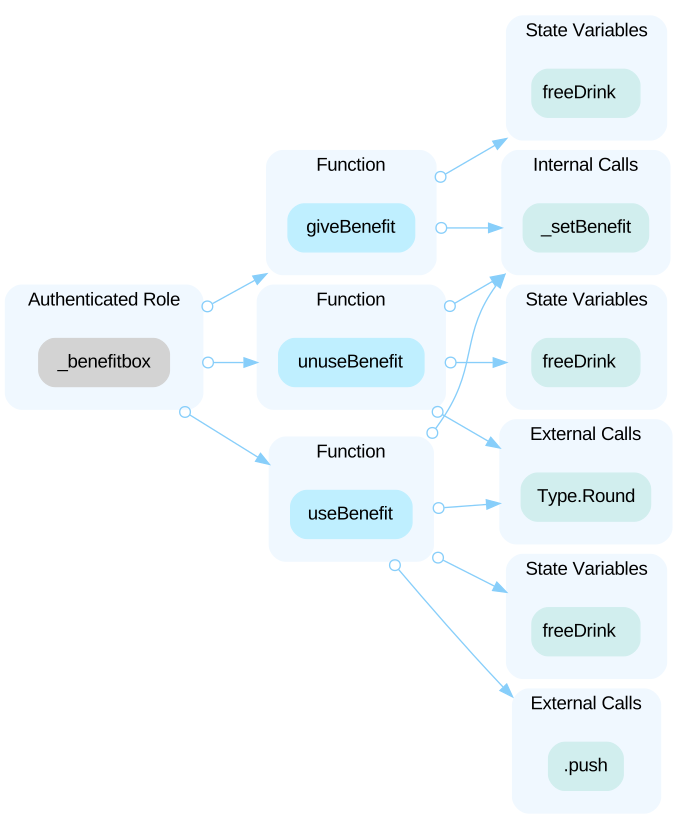 ----- In the contract `FreeFood` the role `_benefitbox` has authority over the functions shown in the diagram below. Any compromise to the `_benefitbox` account may allow the hacker to take advantage of this authority and use/unuse and give benefits. 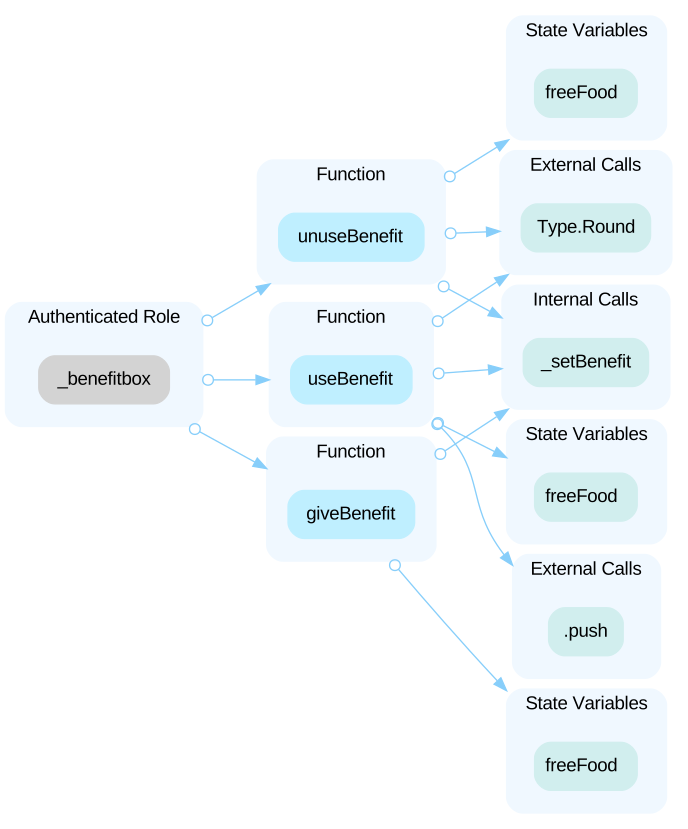 ----- In the contract `Gallery` the role `_benefitbox` has authority over the functions shown in the diagram below. Any compromise to the `_benefitbox` account may allow the hacker to take advantage of this authority and use/unuse and give benefits. 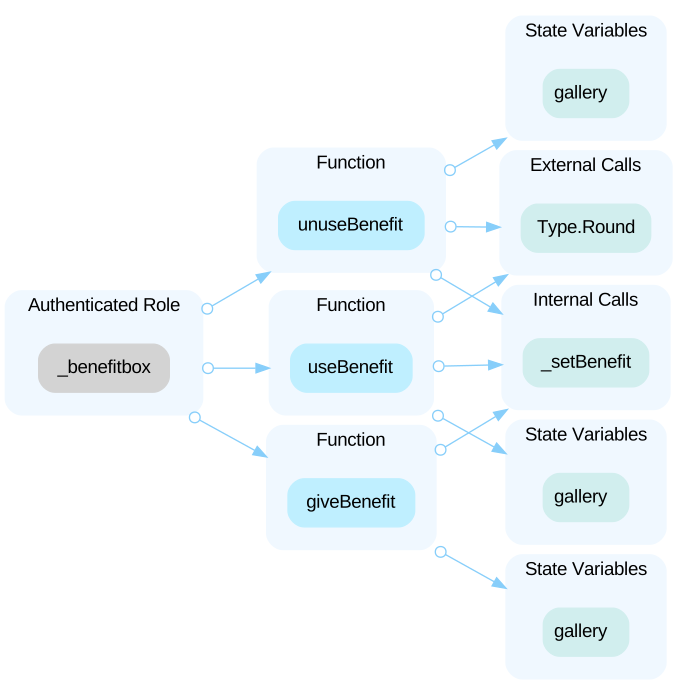 ----- In the contract `Gift` the role `_benefitbox` has authority over the functions shown in the diagram below. Any compromise to the `_benefitbox` account may allow the hacker to take advantage of this authority and use/unuse and give benefits. 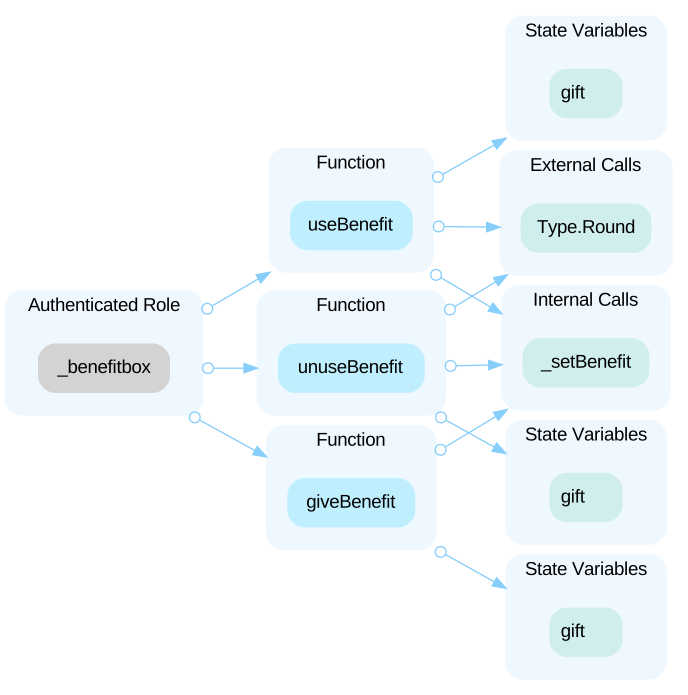 ----- In the contract `ParkingArea` the role `_benefitbox` has authority over the functions shown in the diagram below. Any compromise to the `_benefitbox` account may allow the hacker to take advantage of this authority and use/unuse and give benefits. 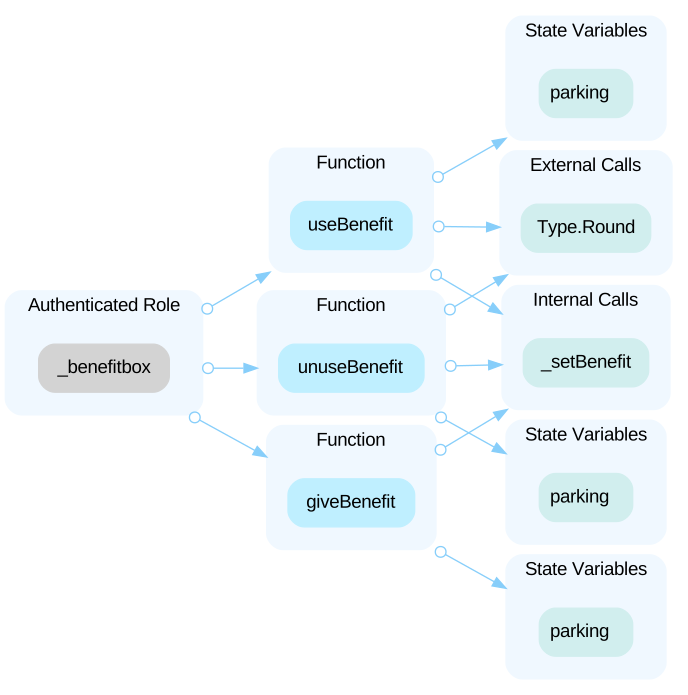 ----- In the contract `WEMIXChampionship2023` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and mint tokens and modify the token configuration. 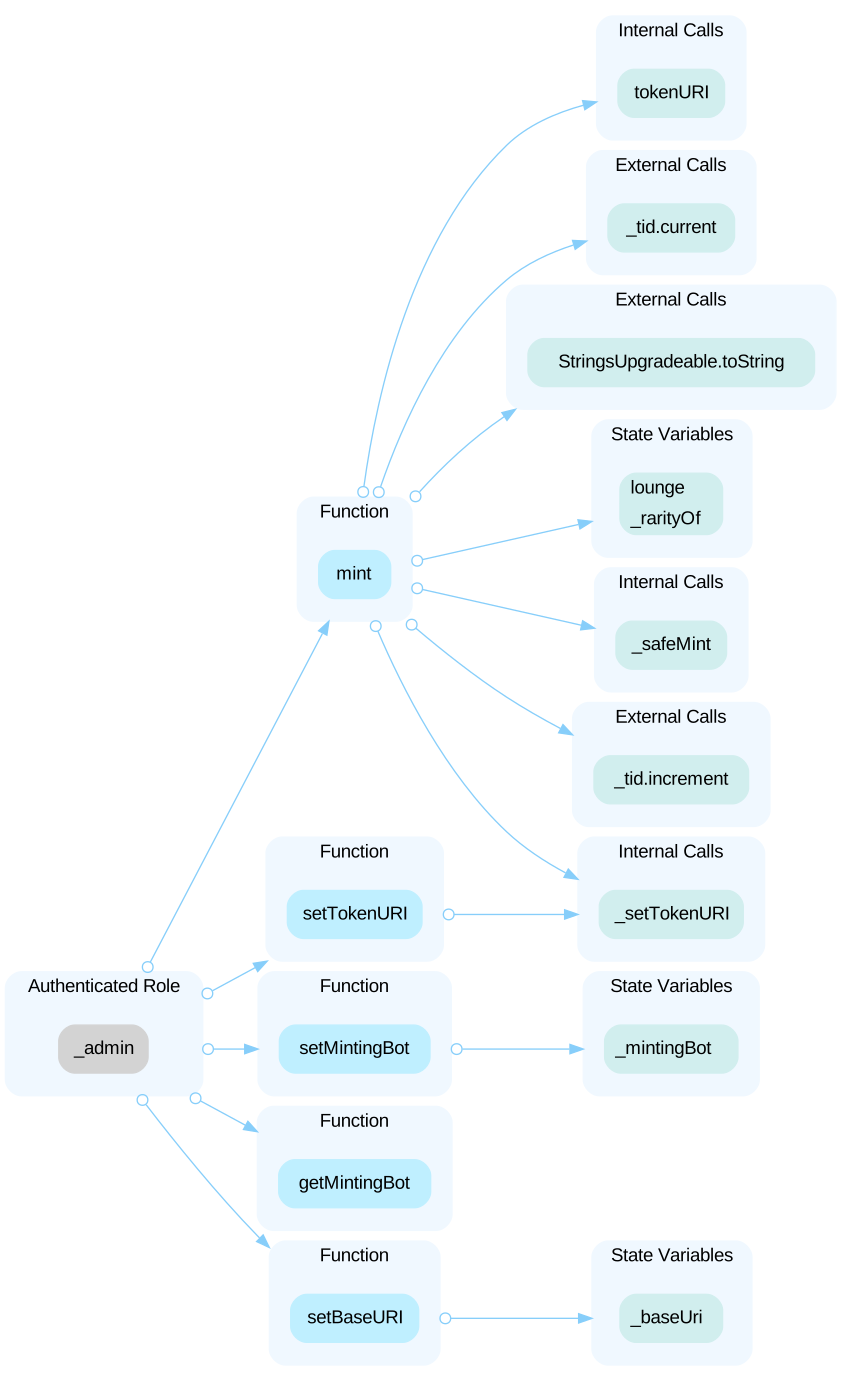 ----- In the contract `AccessController` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify privileged roles within the contract. 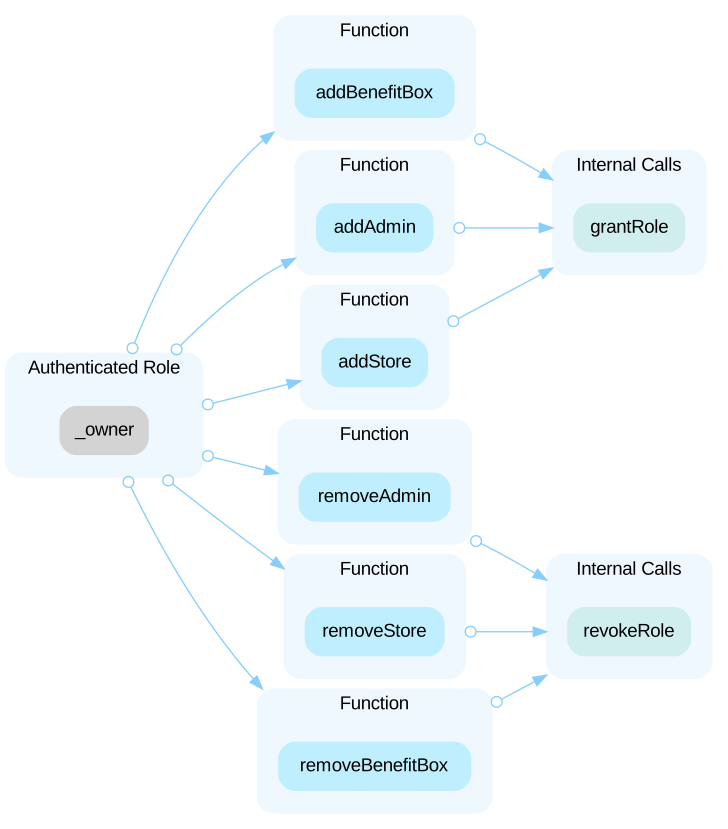
HighCentralized Control of Contract UpgradeOpen
Multiple contracts inherits upgradeable contracts, indicating that it is part of an upgradeable system. Upgradeable contracts often pair with a proxy contract that is responsible for managing contract upgrades. The `privileged roles` of the proxy often have the authority to update the implementation contract. Any compromise of the privileged account could allow a hacker to exploit this authority, potentially altering the implementation contract pointed to by the proxy and thus executing malicious functionality within the implementation contract.
LowMissing `getUseDate` in `FreeDrink.sol`Open
The `FreeFood.sol` contract contains the `getUseDate` function, which is used for querying the "_useDateOf" data. However, it is missing in the `FreeDrink.sol` file.
LowOut of Scope DependenciesOpen
Most of the non-view functions in the project can only be called by privileged roles, such as the Owner, "onlyStore," and "onlyAdmin." The security and operational correctness will heavily rely on the contracts outside the current audit scope or off-chain components. If the out-of-scope component performs incorrect operations, it can cause the contracts in scope to exhibit erroneous behavior.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (10)
- contracts/benefit/Gallery.sol
- contracts/benefit/Gift.sol
- contracts/nft/WEMIXChampionship2023.sol
- contracts/benefit/BenefitBase.sol
- contracts/library/Type.sol
- contracts/benefit/FreeFood.sol
- contracts/benefit/ParkingArea.sol
- contracts/benefit/BenefitBox.sol
- contracts/benefit/FreeDrink.sol
- contracts/role/AccessController.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us