Nut DeFi - Audit
CertiK reviewed Nut DeFi (Nut DeFi - Audit) on 20 Jan 2025: 33 findings, 0 critical; 18 marked fixed, 3 acknowledged, 12 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings33
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 0 |
| Medium | 6 | 0 | 8 |
| Low | 6 | 0 | 10 |
HighCentralization Related RisksAcknowledged
In the contract `AbsToken`, the role `_feeWhiteList` has authority over the functions shown in the diagram below. Any compromise to the `_feeWhiteList` account may allow the hacker to take advantage of this authority and set automatic LP burn settings. 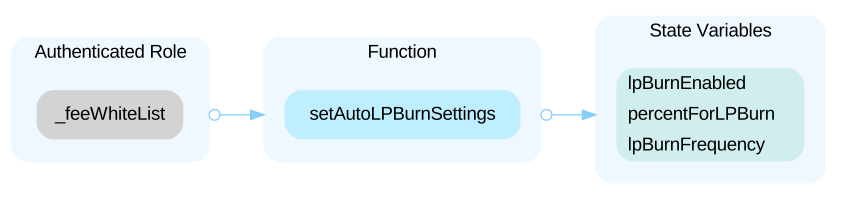 In the contract `AbsToken`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set or unset reward exclusion for accounts, set auto LP burn settings, set batch user information, set LP provider exclusion status, initiate the trading process, set the fund address, set the LP reward time debt, set fee whitelist for multiple addresses, set the buy fee, set the sell fee parameters, set the LP hold condition, set the remove liquidity pool fee, set the slippage value, set fee whitelist status, and update LP amount for specified accounts. 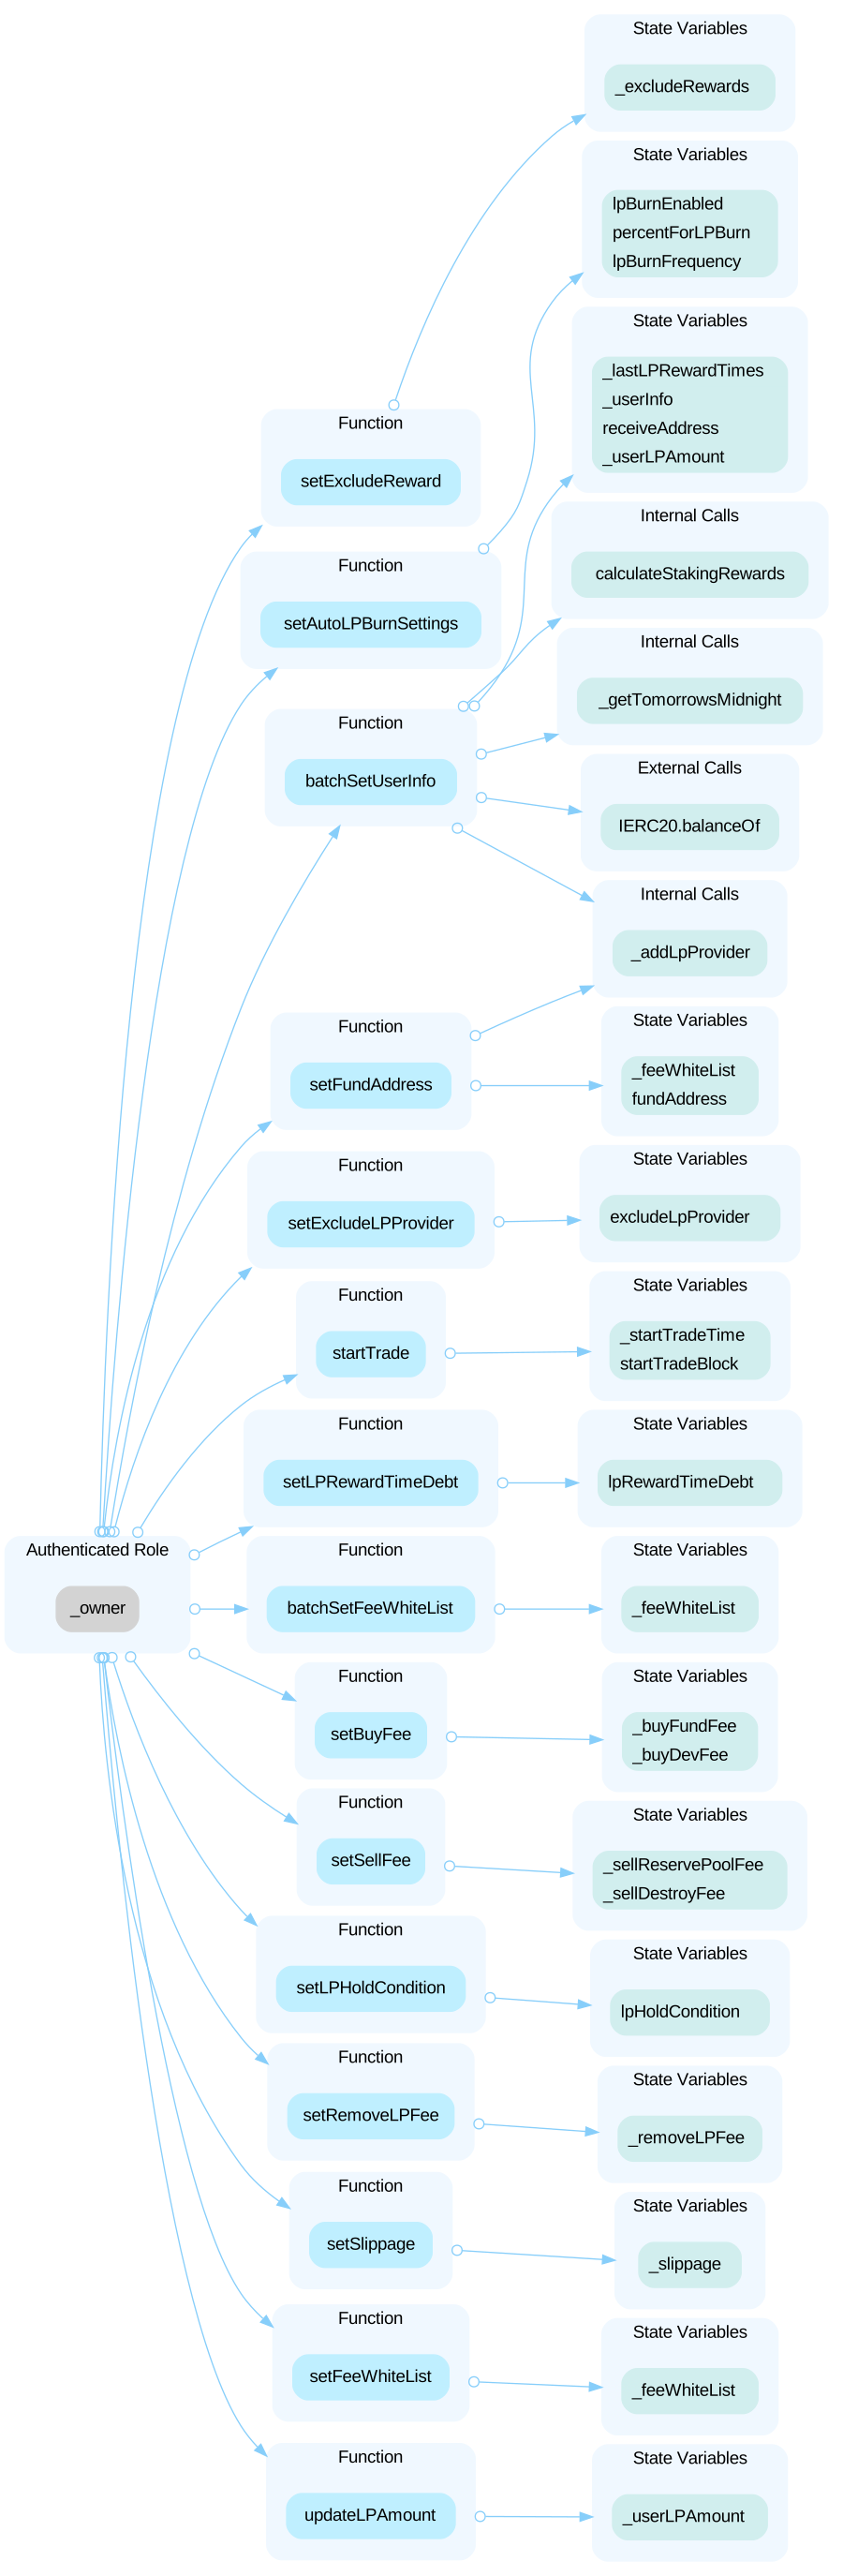 In the contract `AbsToken`, the role `_whitelist` has authority over the functions shown in the diagram below. Any compromise to the `_whitelist` account may allow the hacker to take advantage of this authority and check future LP providers and manage rewards index, set the reward gas value, check LP index for future rewards, claim a specified amount of token, set the per iteration value, claim a balance amount, and set swap pair list entry. 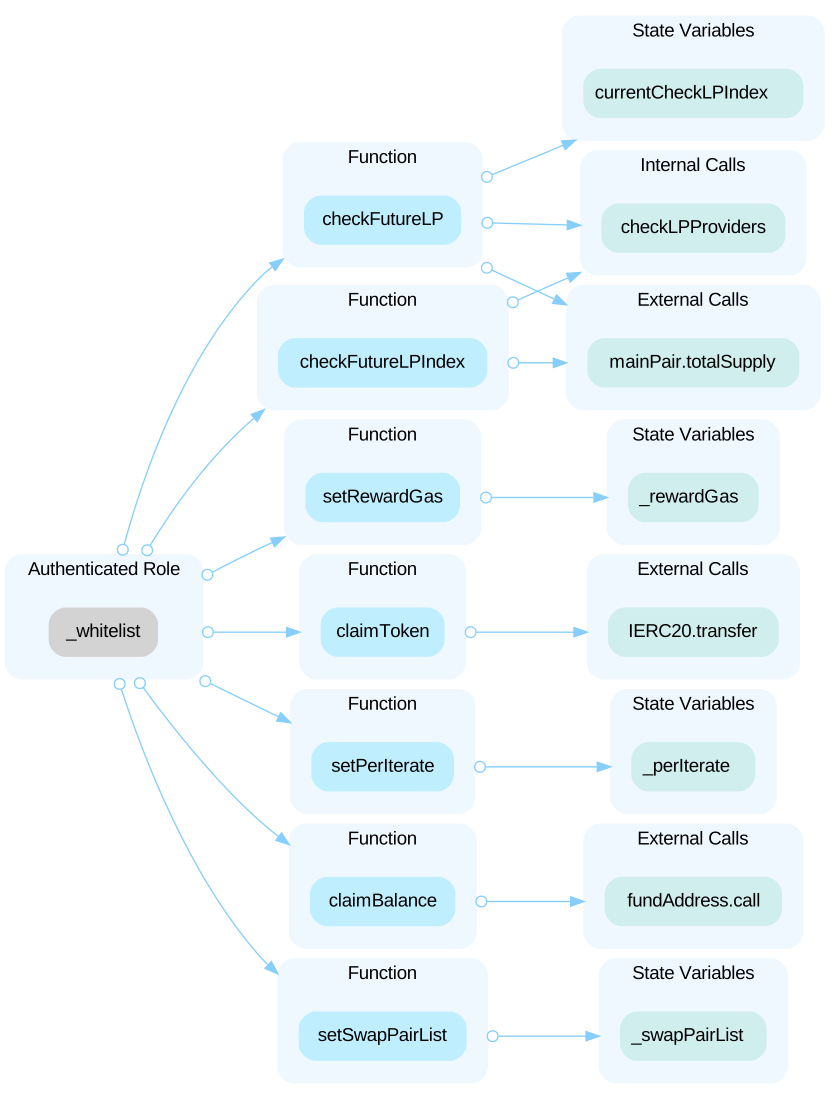 In the contract `AbsToken`, the role `fundAddress` has authority over the functions shown in the diagram below. Any compromise to the `fundAddress` account may allow the hacker to take advantage of this authority and set exclude reward for an account, update the user's LP amount. 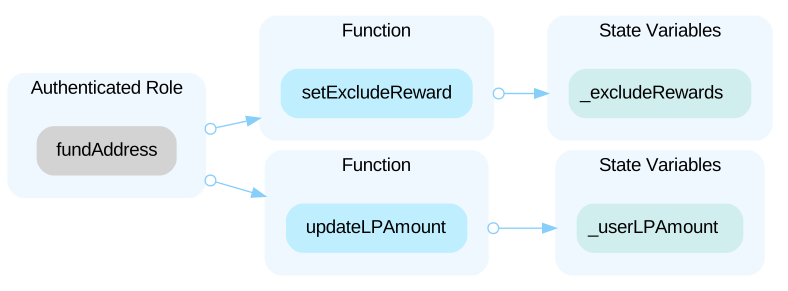 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and renounce contract ownership or transfer ownership to a new address. 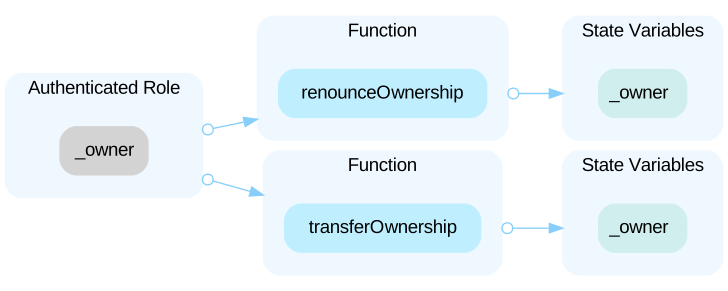 In the contract `TokenDistributor`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and claim tokens to the fund address. 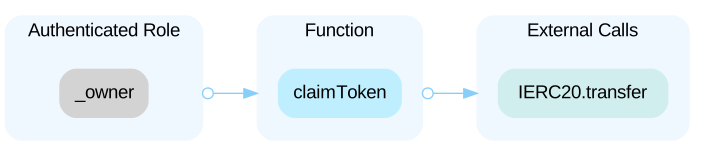
HighInitial Token DistributionAcknowledged
All of the `NUT` tokens in circulation (2 million) are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
HighVulnerability to Reward Manipulation Due to InstaAcknowledged
The `processStakingRewards` function in the contract calculates and distributes rewards based on the **instantaneous balance** of liquidity pool (LP) tokens held by a user at the time of reward calculation. Specifically, the function utilizes the `balanceOf` method to retrieve the current LP token balance of a user: ```solidity=1141 uint256 userLpBalance = IERC20(_mainPair).balanceOf(user); ``` This approach introduces a potential **manipulation vulnerability** in the reward distribution mechanism. LP holders can temporarily increase their LP token balance before the reward calculation occurs, bypassing the `lpHoldCondition` threshold check, and then immediately withdraw these tokens after the reward calculation, deceiving the system. This behavior allows them to claim a disproportionate share of the rewards without maintaining a consistent LP position, thereby unfairly penalizing long-term liquidity providers who keep their LP tokens staked continuously. Additionally, before claiming the reward, price manipulation can be carried out through a `swap` of pair to inflate the LP value, and after receiving the reward, the price can be also restored through swap. If there are no front runner, and the fees paid are much lower than the rewards gained, this also leads to unfair reward distribution.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x29fdf61b4ab5a4af38c745d4e1ef282525d4978d | Chain: BNB Chain | Source code: Verified source |
Part of Nut DeFi’s security record
 Nut DeFi
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us