JOJO - Ⅲ
CertiK reviewed JOJO (JOJO - Ⅲ) on 9 Dec 2022: 18 findings, 0 critical; 11 marked fixed, 3 acknowledged, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings18
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 2 | 0 |
| Low | 4 | 0 | 11 |
HighCentralization Risks in JOJOOperation.solAcknowledged
In the contract `JOJOOperation` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and extract all the funds via setting of bad `RiskParams` (fake Oracle, unexpected `liquidationThreshold` and `insuranceFeeRate`) . 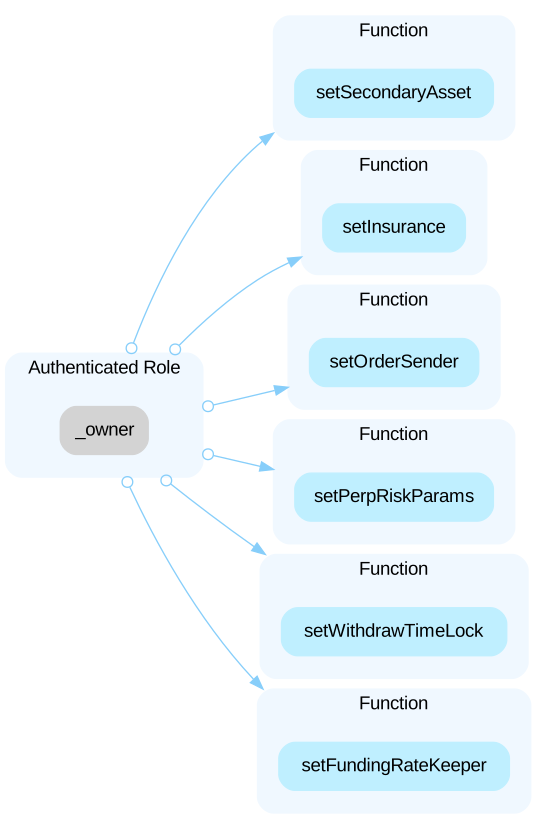
Medium`validOrderSender` can manipulate the marketAcknowledged
`validOrderSender` can "replay" a cancelled off-chain order or fulfill makers' orders in wrong order. `validOrderSender` prepares a set of orders to execute the `Perpetual.trade()`. Each order should be signed by `order.signer` or by her operator. However, the cancelled order can still be used until it expires. `nonce` part of the order is only used to distinguish orders, it is never checked on-chain and not "consumed" after cancellation. `validOrderSender` can use the taker order and fulfill her own maker order with the worst possible price, ignoring all the other maker orders with better prices.
MediumOpen positions are discarded if `Perpetual` is deAcknowledged
Function `setPerpRiskParams()` allows to deregister the Perpetual from the Dealer even if there are open positions. Users with positive `credit` will suffer loss, users with negative will gain profit. It would be more fair to forcefully close all the positions before deregistering.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (26)
- contracts/adaptor/constOracle.sol
- contracts/impl/Perpetual.sol
- contracts/lib/Position.sol
- contracts/lib/Liquidation.sol
- contracts/impl/JOJOOperation.sol
- contracts/intf/IDecimalERC20.sol
- contracts/fundingRateKeeper/FundingRateUpdateLimiter.sol
- contracts/lib/Types.sol
- contracts/lib/Funding.sol
- contracts/utils/SignedDecimalMath.sol
- contracts/intf/IMarkPriceSource.sol
- contracts/utils/Errors.sol
- contracts/intf/IDealer.sol
- contracts/impl/JOJOStorage.sol
- contracts/adaptor/chainlinkAdaptor.sol
- contracts/subaccount/SubaccountFactory.sol
- contracts/intf/IPerpetual.sol
- contracts/lib/Operation.sol
- contracts/impl/JOJODealer.sol
- contracts/impl/JOJOView.sol
- contracts/adaptor/emergencyOracle.sol
- contracts/lib/EIP712.sol
- contracts/lib/Trading.sol
- contracts/subaccount/Subaccount.sol
- contracts/adaptor/witnetAdaptor.sol
- contracts/impl/JOJOExternal.sol
Part of JOJO’s security record
 JOJO
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us