Wemix Retainer 113 Liquid Staking
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 113 Liquid Staking) on 15 Apr 2024: 15 findings, 0 critical; 10 marked fixed, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings15
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 1 | 0 | 6 |
| Low | 2 | 0 | 4 |
HighCentralization Risks in StWEMIXV6.solOpen
In the contract `StWEMIXV6` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - migrate the wonder - update the wonder - migrate the wonder from the exit pid - update fee - transfer Wemix coin to the owner - set treasury address - set breaker address 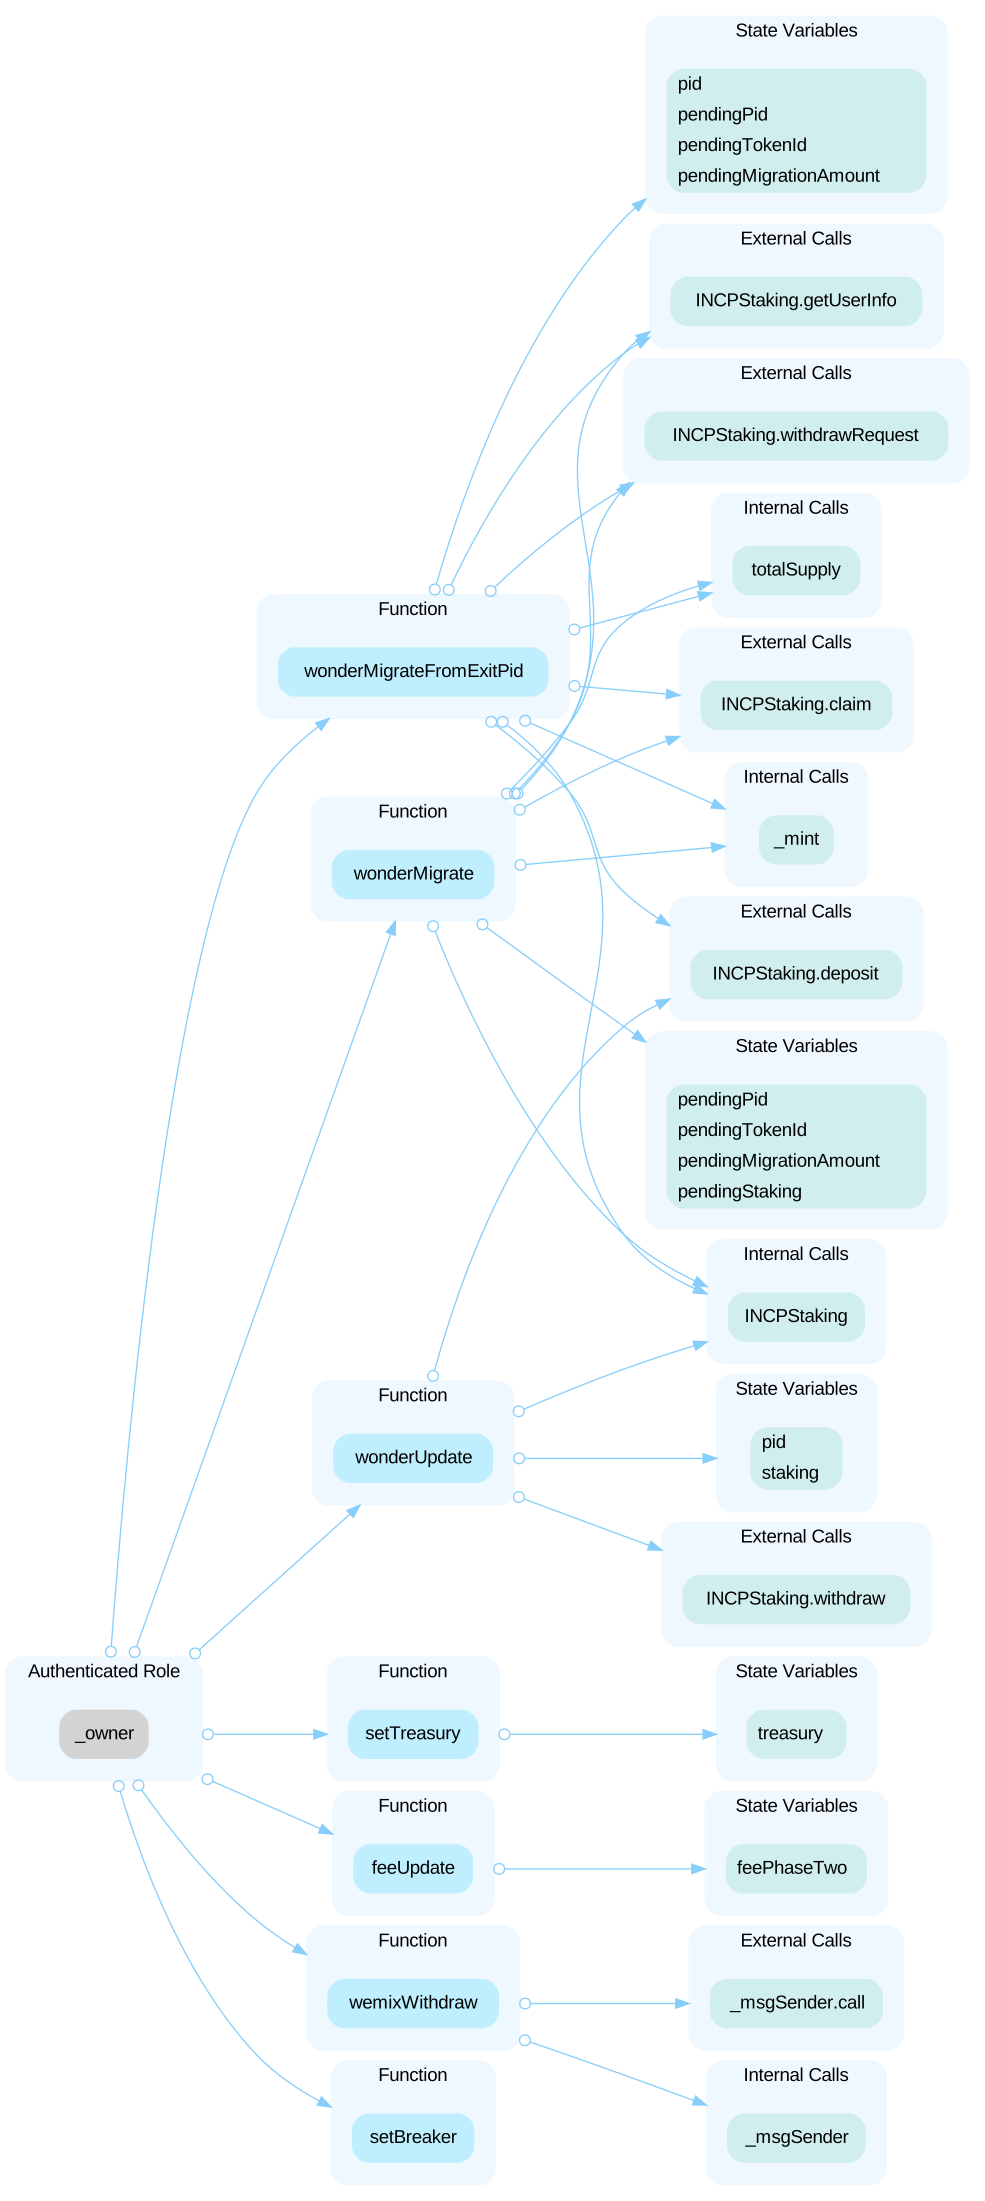 In the contract `StWEMIXV6` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority and pause/unpause this contract. 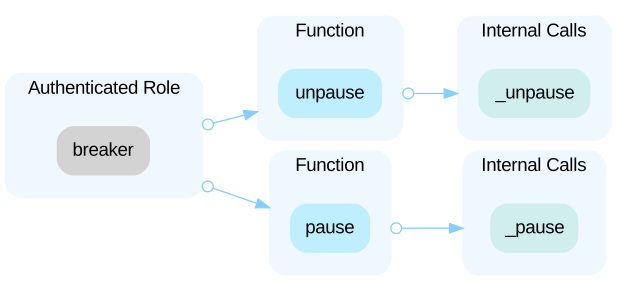
HighCentralized Control of Contract UpgradeOpen
The contract `StWEMIXV6` inherits upgradeable contracts, indicating that it is part of an upgradeable system. Upgradeable contracts often pair with a proxy contract that is responsible for managing contract upgrades. The `admin` of the proxy often has the authority to update the implementation contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
MediumNo Upper Limits for FeesOpen
The function `feeUpdate()` does not limit the percentage of fees applied. The fee of phase two rates could therefore be 100%. If the `feePhaseTwo` is set to `10000`, the reward will be 0 and all fees will be sent to the treasury address.
Low`nonReentrant` Modifier can be Placed and ExecuteOpen
As a best practice, the `nonReentrant` modifier could be placed and executed before other modifiers in functions to prevent reentrancy attacks through other modifiers and make the code more efficient.
LowThird-Party Dependency UsageOpen
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=27 address public staking; // immutable ``` - The contract `StWEMIXV6` interacts with third party contract with `IStaking` interface via `staking`. --- ```solidity=51 address wonder_, ``` - The function `StWEMIXV6.initialize` interacts with third party contract with `INCPStaking` interface via `wonder_`.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/StWEMIXV6.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us