Real Smurf Cat
CertiK reviewed Real Smurf Cat on 29 Jul 2024: 5 findings, 0 critical; 2 marked fixed, 2 acknowledged, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 1 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 2 | 0 |
HighCentralization Risks in SmurfCat.solFixed
**Important Note**: Certain identification and KYC procedures were attempted to be applied to the project team in order to better understand the centralization situation and potential risks of the project. Based on the collected information and further conducted investigation, the project failed to pass the criteria with a certain amount of negative signals. Thus the case analysis concluded that there is potential high risk to the project. We strongly advise end users to conduct further research and exercise due diligence before engaging with the project. It is crucial for end users to independently verify and assess all available information to make informed decisions. In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 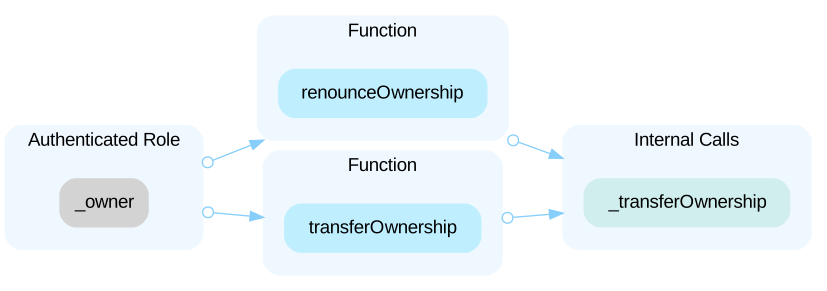 - `renounceOwnership()`: This function is used by the current owner to renounce their ownership of the contract, effectively leaving the contract without an owner and unable to call `onlyOwner` functions. Only the owner can call this function. - `transferOwnership(address newOwner)`: Allows the current owner to transfer ownership of the contract to a new account (`newOwner`). Only the owner can call this function. In the contract `SmurfCat` the role `_owner` has authority over the functions shown in the diagram below. 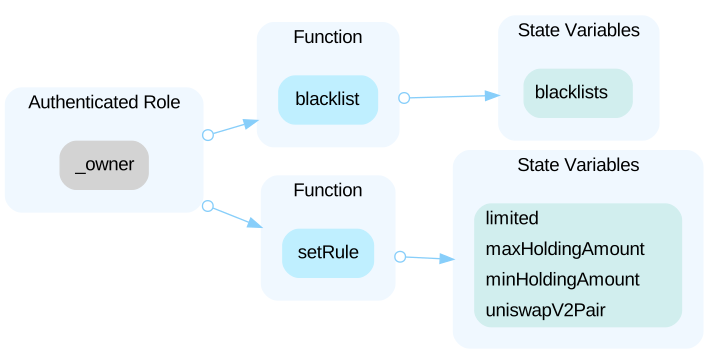 - `blacklist(address _address, bool _isBlacklisting)`: This function allows the owner to add or remove addresses from the blacklist, which prevents them from participating in token transfers. Only the owner of the contract can call this function. - `setRule(bool _limited, address _uniswapV2Pair, uint256 _maxHoldingAmount, uint256 _minHoldingAmount)`: Sets trading rules including enabling/disabling trading limits, setting a Uniswap pair address, and defining maximum and minimum holding amounts. Only the owner can call this function. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functionalities of the project.
MediumBlacklisted users can transfer tokens before settFixed
The protocol has implemented a blacklist feature for security requirements. A blacklisted user will not be able to send or receive tokens. Therefore, before the token is transferred, the protocol checks if the sender or the receiver is blacklisted. However, a malicious user can montior the mempool and if he detects the admin is setting up a blacklist, he can front-run the transaction and transfer the token to another address to avoid being blacklisted.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0xff836a5821e69066c87e268bc51b849fab94240c | Chain: Ethereum | Source code: Verified source |
Part of Real Smurf Cat’s security record
 Real Smurf Cat
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us