Petaverse PPT-Audit
CertiK reviewed Petaverse (Petaverse PPT-Audit) on 26 Jul 2023: 3 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 0 |
HighCentralization Related RisksAcknowledged
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer or renounce the ownership. 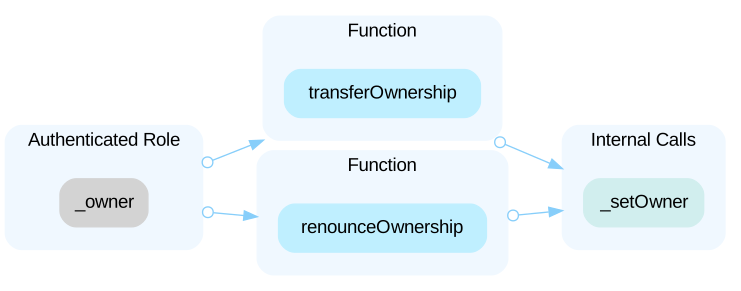 ---- In the contract `ERC1400` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint tokens and add or remove a document from the token. It is important to note that the `issue()` function which is used to mint tokens requires the `_isIssuable` to be true. Since the `_isIssuable` is set to false in the `PPT` contract, the PPT Token is not mintable. 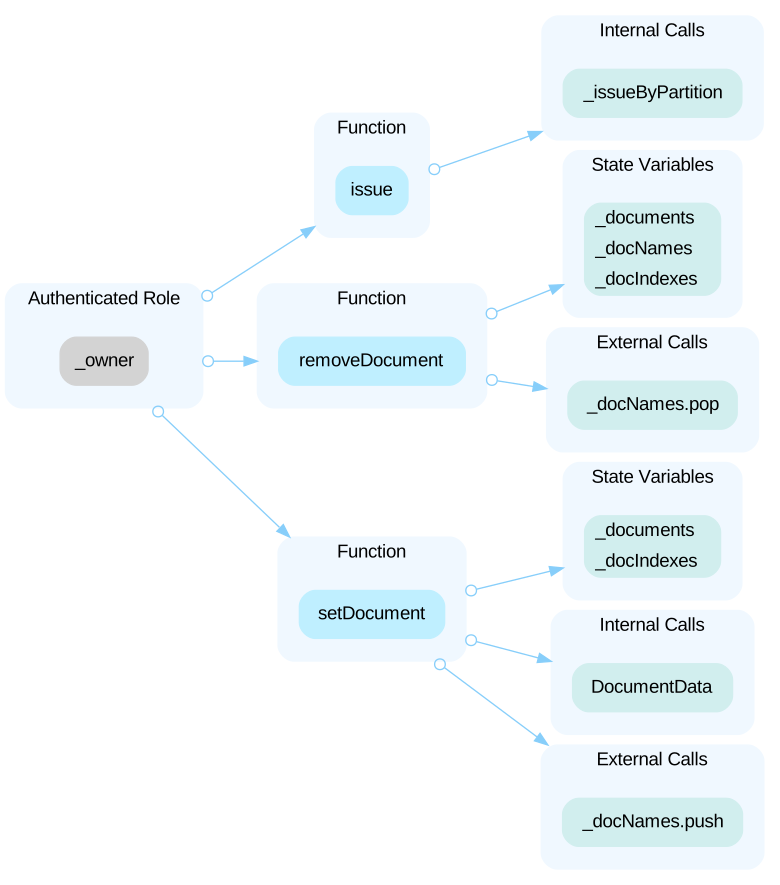 --- In the contract `PPT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update `publicKey`, `feeAddr`, `prosynergyAddr`, and whitelisted accounts. 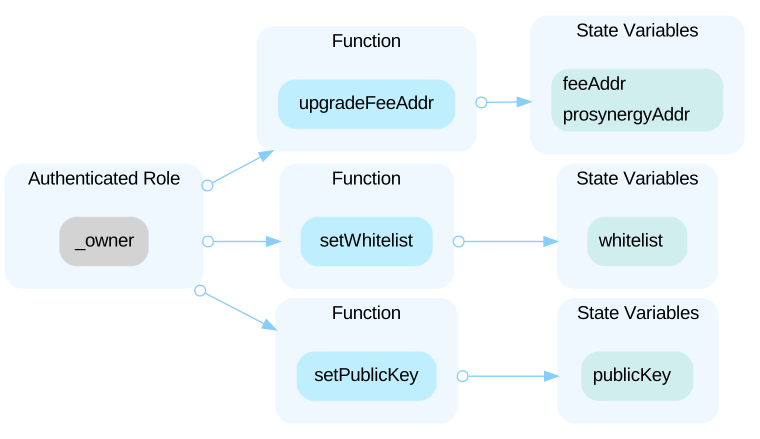 --- In the contract `PPT` the role `publicKey` has authority to provide signatures for the `_transferByPartition()` function. Any compromise to the `publicKey` account may allow the hacker to take advantage of this authority and sign messages to not pay the fees in transactions.
HighInitial Token DistributionAcknowledged
All of the PPT tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the anonymous deployer can distribute tokens without obtaining the consensus of the community. Any compromise to the deployer account that holds undistributed tokens may allow the attacker to steal and sell tokens on the market, resulting in severe damage to the project.
LowMissing Zero Address ValidationAcknowledged
Addresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior or vulnerabilities. ```solidity=33 publicKey = _publicKey; ``` - `_publicKey` is not zero-checked before being used. --- ```solidity=62 publicKey = _publicKey; ``` - `_publicKey` is not zero-checked before being used.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- contracts/ERC1400.sol
- contracts/PPT.sol
Part of Petaverse’s security record
 Petaverse
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us