Yuliverse
CertiK reviewed YULI (Yuliverse) on 5 Jan 2024: 5 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 1 | 0 |
| Low | 0 | 3 | 0 |
HighCentralization Risks in YOG1.solAcknowledged
In the contract `YuliOriginGenOne` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and - Set BaseURI - Set BaseExtension - Set BoxType - Set Platform - Set RoleType 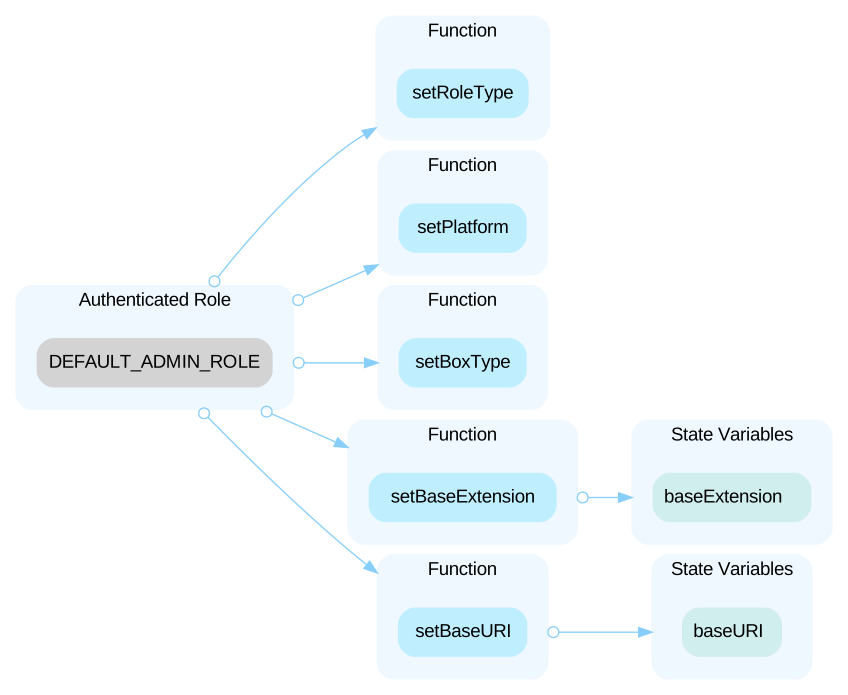 In the contract `YuliOriginGenOne` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and - Mint tokens 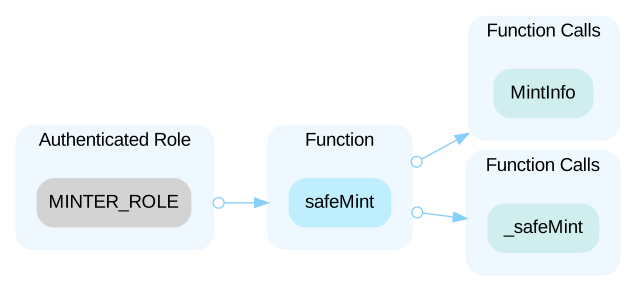 In the contract `YuliOriginGenOne` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and - Control the operation of the contract (through pause and unpause functions) 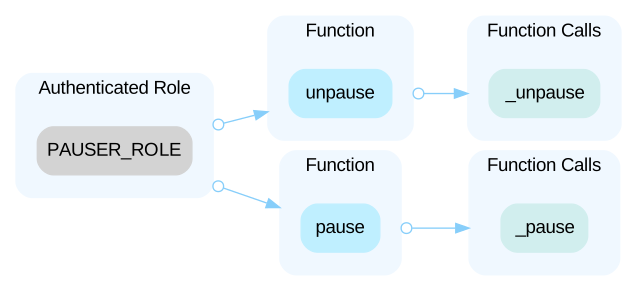
MediumNot Recommended MetadataURI ProtocolAcknowledged
HTTP/HTTPS should not be used for token metadata because the server owner can change token metadata at will, which can dramatically affect the token value.
LowCheck Effect Interaction Pattern ViolatedAcknowledged
The OpenZeppelin implementation of "_safeMint" performs an external call to the receiver address using "_checkOnERC721Received". It is possible to re-enter the "_safeMint" function via this external call. In the YOG1.sol, the "_safeMint" is called before the "tokenMintInfo" mapping is updated, which violates the "Check-Effect-Interaction" pattern. Reference: https://fravoll.github.io/solidity-patterns/checks_effects_interactions.html
LowMissing Emit EventsAcknowledged
Functions that update state variables should emit relevant events as notifications.
LowPotential Mint Logical IssueAcknowledged
According to the code logic, if "newId" is equal to 0, then "tokenId" is assigned the value of "_tokenIdCounter+1". Otherwise, if "newId" is greater than 1000000000, "tokenId" is assigned the value of "newId" input function argument. In this case, if "_tokenIdCounter" reaches 1,000,000,000 and "_tokenIdCounter+1" has been minted, the function cannot be called when "newId" is equal to 0.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- ERC721/YOG1.sol
Part of YULI’s security record
 YULI
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us