Wemix Retainer 147 WEMIX Governance
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 147 WEMIX Governance) on 19 Dec 2024: 4 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 0 |
HighCentralization Risks in GovImp.solOpen
In the contract `GovImp`, the role `_govmem` has authority over the functions shown in the diagram below. Any compromise to the `_govmem` account may allow the hacker to take advantage of this authority and add a proposal for member removal, add a proposal to add a new member, add a proposal to change the governance address, propose a change or exit of a governance member, vote on a ballot index with approval choice, finalize the voting process if ended, add a proposal to change an environment variable, and authorize a contract upgrade for a new implementation address. 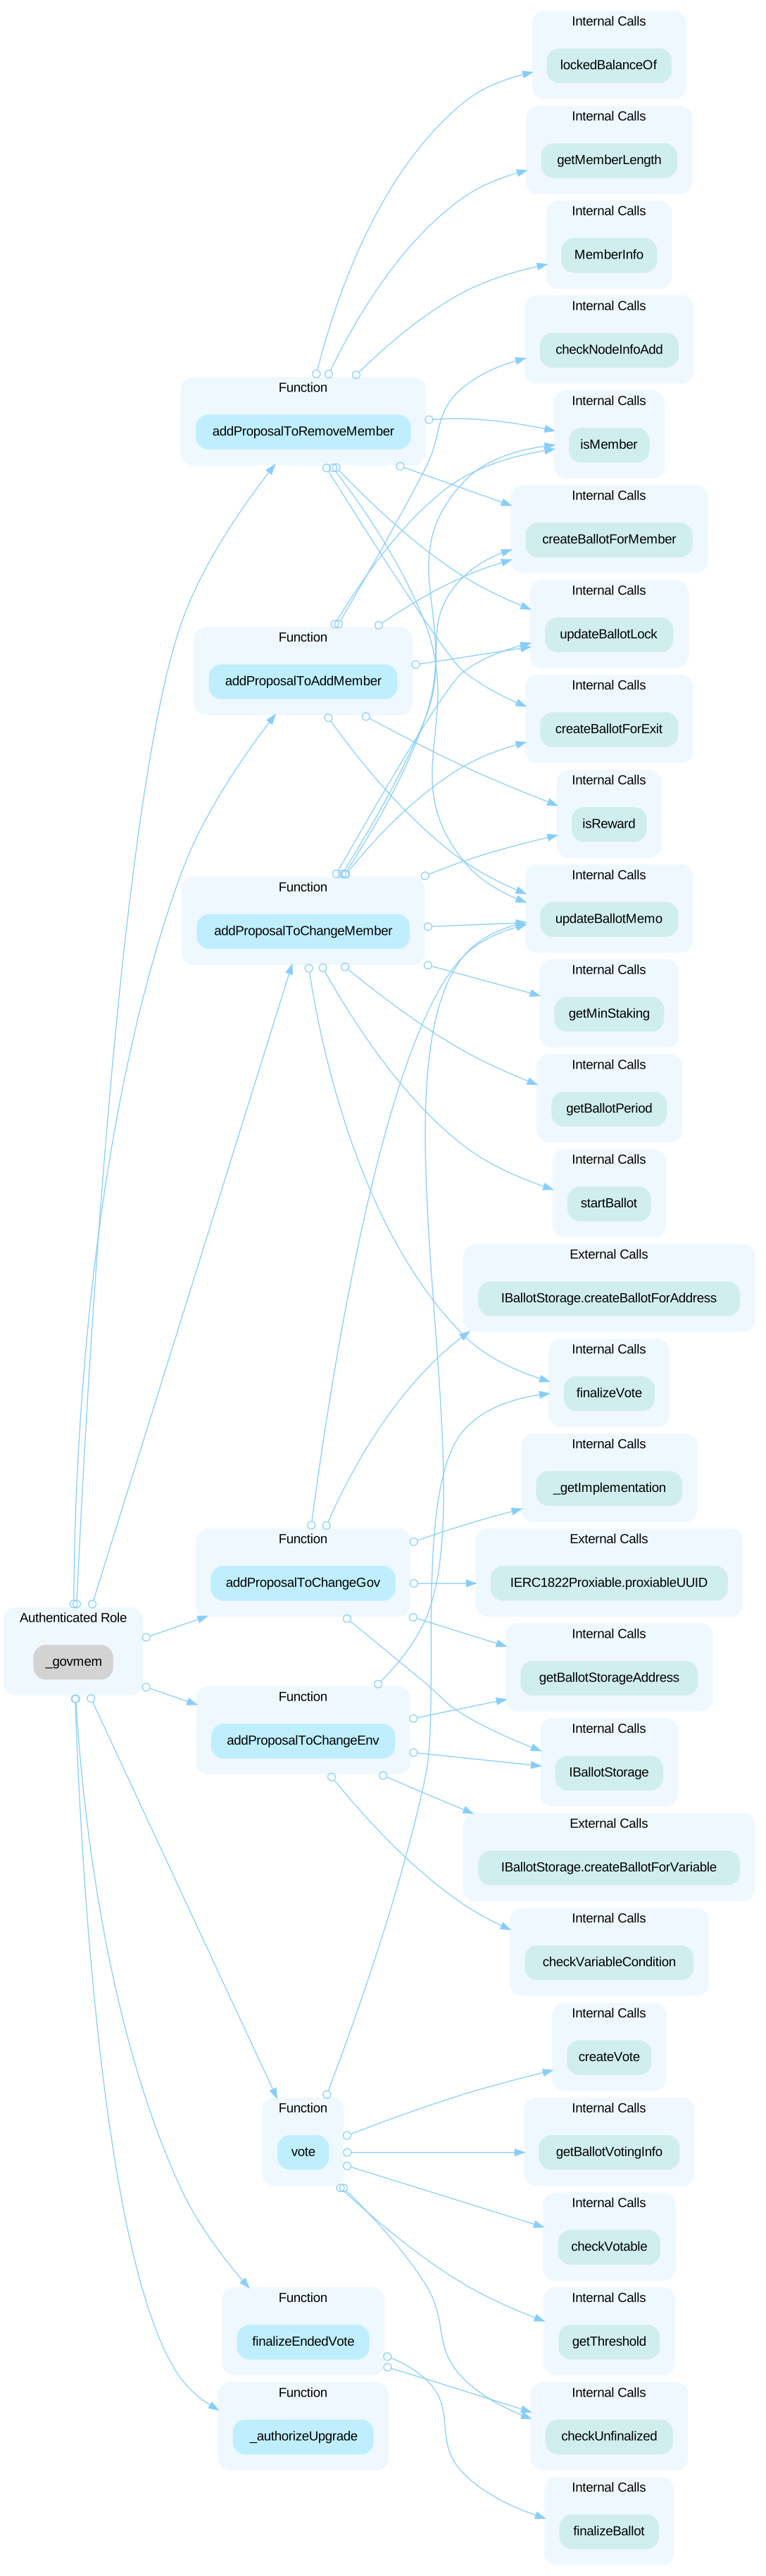 In the contract `GovImp`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and reinitialize node checks and properties, as well as set the proposal time period. 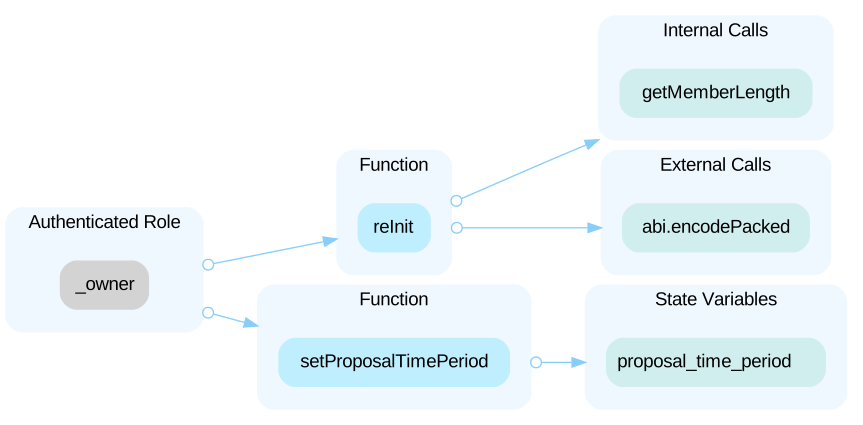
HighCentralized Control of Contract UpgradeOpen
In the contract `GovImp`, the role `GovMem` has the authority to update the implementation contract behind the proxy contract. Any compromise to the `GovMem` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
LowCostly operations inside a loopOpen
Costly operations inside a loop might waste gas, so optimizations are justified. ```solidity=1311 memberLength = i; ``` ```solidity=1331 nodeLength = i; ```
LowMissing Error MessagesOpen
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/GovImp.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us