Huma Finance - Audit
CertiK reviewed Huma Finance (Huma Finance - Audit) on 30 Dec 2022: 14 findings, 0 critical; 12 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings14
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 1 | 0 | 11 |
HighCentralization Related RisksOpen
In the contract `BaseFeeManager` the role `onlyOwner` has authority over the functions shown in the diagram below. 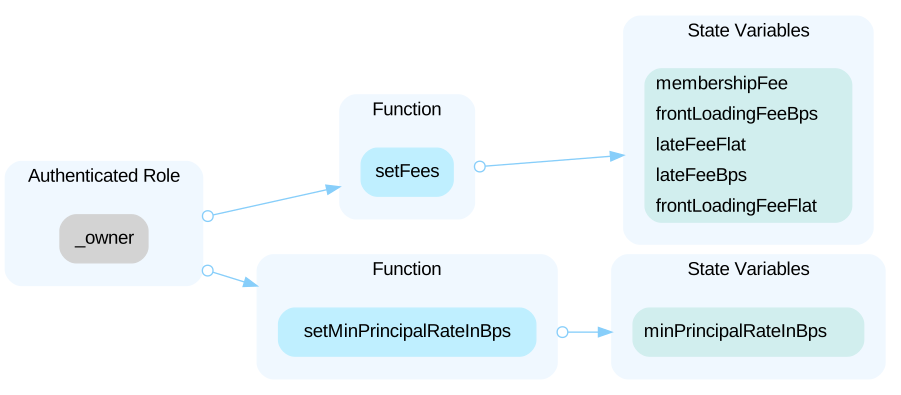 Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this by being able to change the fees to any number they choose. A malicious user could also set `minPrincipalRateInBps` to an arbitrarily high number. ---- In the contract `BasePoolConfig` the role `_onlyOwnerOrHumaMasterAdmin`, `onlyPoolOwnerOrEA`, `onlyPoolOwnerTreasury`, and `humaConfig.owner()` have authority over those functions listed below and the role `onlyOwner` has authority over those functions shown in the diagram: - `setAPR()` - set the default APR for the pool, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setCreditApprovalExpiration()` - set the default for credit approval expiration, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setEARewardsAndLiquidity()` - set the default for rewardsRate and liquidityRate, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setEvaluationAgent()` - add an evaluation agent to be able to approve loans, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setFeeManager()` - set the fee manager for the protocol, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setHumaConfig()` - set the address for the `HumaConfig` file, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setMaxCreditLine()` - set the default max size of each loan and credit line, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setPool()` - set the pool address, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setPoolLiquidityCap()` - set the upper bound that approved depositors can deposit, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setPoolOwnerRewardsAndLiquidity()` - set the default for owner rewards, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setPoolPayPeriod()` - set the pay cycle in amount of periods, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setPoolName()` - set a string for the pool name, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setPoolToken()` - set the address of the pool token, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setReceivableRequiredInBps()` - set the rate in basis points for receivable. This can be over 100% because the pool might want to have over-collateralization, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `setWithdrawalLockoutPeriod()` - set the default amount of time a lender has to make after making a deposit, only callable by `_onlyOwnerOrHumaMasterAdmin`. - `withdrawEAFee()` - withdraw rewards to EA, only callable by `onlyPoolOwnerOrEA`. - `withdrawPoolOwnerFee()` - withdraw rewards to pool owner, only callable by `onlyPoolOwnerTreasury`. - `withdrawProtocolFee()` - withdraw protocol rewards to treasury account, only callable by `humaConfig.owner()`.  Any compromise to the `onlyOwner`, `_onlyOwnerOrHumaMasterAdmin`, `onlyPoolOwnerOrEA`, `onlyPoolOwnerTreasury`, and `humaConfig.owner()` account(s) may allow the hacker to take advantage of these functions. ---- In the contract `EvaluationAgentNFT` the role `onlyOwner` has authority over the functions shown in the diagram below.  Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this and change the `TokenURI`. ---- In the contract `HDT` the role `onlyOwner` has authority over the functions shown in the diagram below. 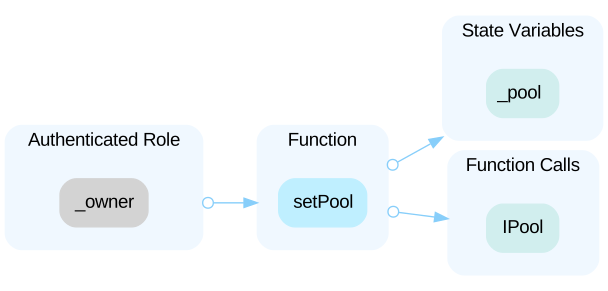 Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this and change the address of the pool. --- In the contract `HumaConfig` the role `onlyOwner` has authority over the functions shown in the diagram below. 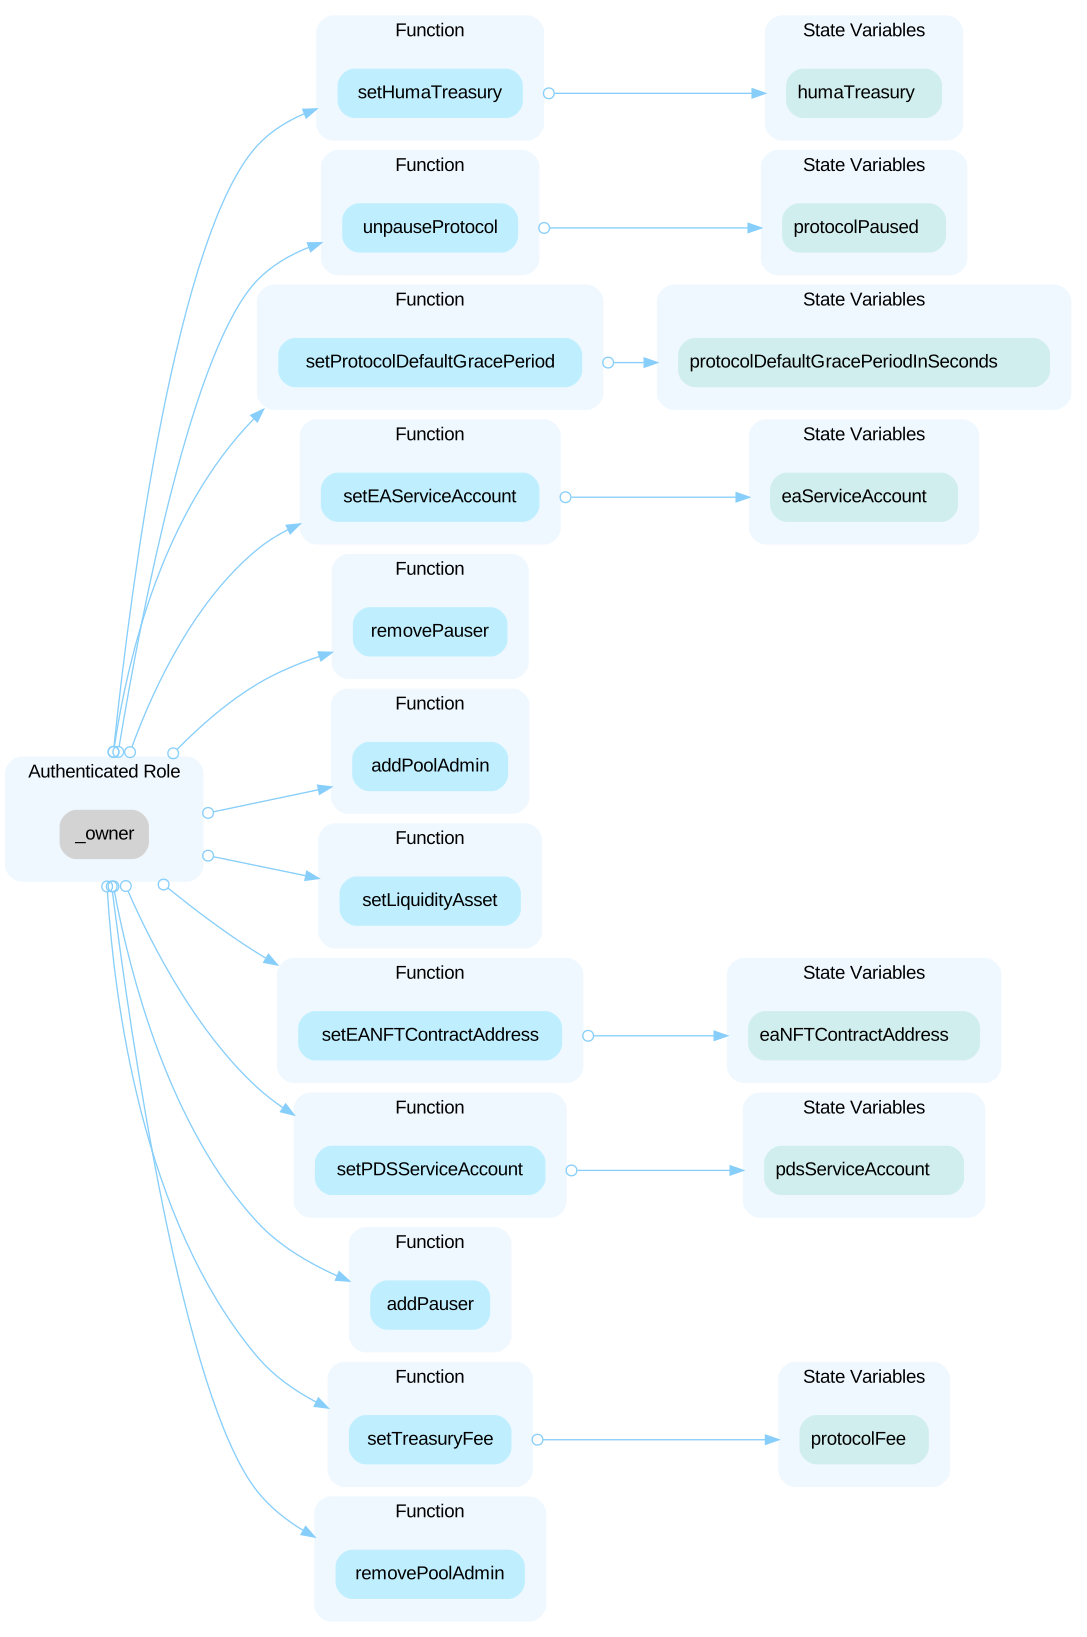 Any compromise to the `onlyOwner` account may allow the hacker to take advantage of these and set the treasury fee to 50%. A malicious user could also pause and unpause the protocol for favorable transactions. They can set the treasury and default grace period. However, the default grace period has a minimum value it cannot be set below. ---- In the contract `BaseCreditPool` the role `onlyEAServiceAccount` has authority over the functions listed below: - `approveCredit()` - approves a user's credit line. - `changeCreditLine()` - if a user wants to change their credit line to lower, they may do that at their own will. If the c
LowThird Party DependenciesOpen
The contract is serving as the underlying entity to interact with third party verification and payment processors. The scope of the audit treats 3rd party entities as black boxes and assume their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts, such as increasing fees of 3rd parties, migrating to new LP pools, etc.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (22)
- https://github.com/00labs/huma-contracts/contracts/BasePool.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/interfaces/ICredit.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/HDT/interfaces/IHDT.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/libraries/BaseStructs.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/BaseCreditPool.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/HDT/HDTStorage.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/BasePoolConfig.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/Errors.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/ReceivableFactoringPool.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/BaseFeeManager.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/interfaces/ILiquidityProvider.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/interfaces/IReceivable.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/interfaces/IFeeManager.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/BasePoolStorage.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/HumaConfig.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/interfaces/IPool.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/openzeppelin/TransparentUpgradeableProxy.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/openzeppelin/TimelockController.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/EvaluationAgentNFT.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/HDT/HDT.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/ReceivableFactoringPoolStorage.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
- https://github.com/00labs/huma-contracts/contracts/BaseCreditPoolStorage.sol at commit 1075003788f343a1a30606834fd9ac073b23c23a
Part of Huma Finance’s security record
 Huma Finance
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us