Ton Bridge Web Application
CertiK reviewed TON (Ton Bridge Web Application) on 29 Nov 2022: 3 findings, 0 critical; all marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 2 |
MediumUsing components with known vulnerabilitiesFixed
The result of the "npm audit" command shows the application is using outdated libraries with know vulnerabilities. 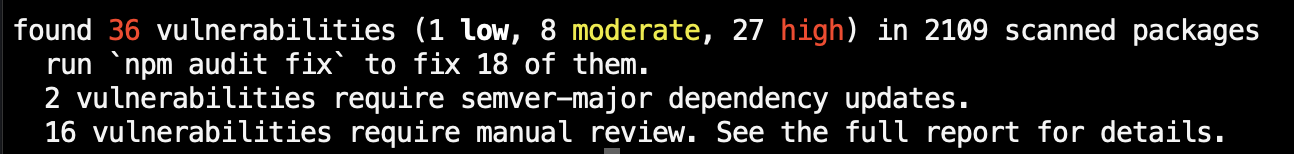
LowClickjackingFixed
The HTTP response of the GET request to https://ton.org/bridge/ doesn't contain any security headers to prevent the website from loading in an iframe.
LowPotential insecure application hostingFixed
The bridge application "https://ton.org/bridge/" is hosted on a third-party platform, "Github". If the application is hosted on a third-party platform, then the team is trusting the platform's own security to prevent an attacker from modifying the site to perform malicious actions within the application. The host "ton.org" points to the Cloudflare CDN. One of the benefits of using Cloudflare is that it offers security features such as "WAF" and DDOS protection. However, the application can be accessed with the alternative URL "https://newton-blockchain.github.io/bridge/". This exposed the application from Cloudflare's protection.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of TON’s security record
 TON
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us