MAZE - audit
CertiK reviewed MAZE (MAZE - audit) on 4 Jul 2022: 8 findings, 0 critical; 3 marked fixed, 5 acknowledged.
Report hosted on skynet.certik.com.
Statuses are the security firm’s own, from this report. Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 1 |
| Medium | 0 | 1 | 0 |
| Low | 0 | 3 | 2 |
HighCentralization Risks in RoyalMasterChef.solAcknowledged
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the ownership. 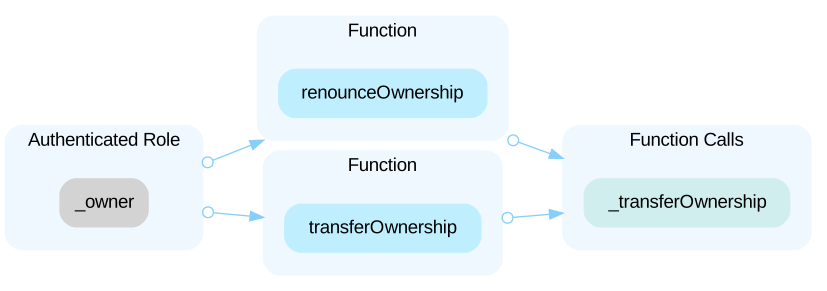 In the contract `RoyalMasterChef` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the basic configuration of the project. 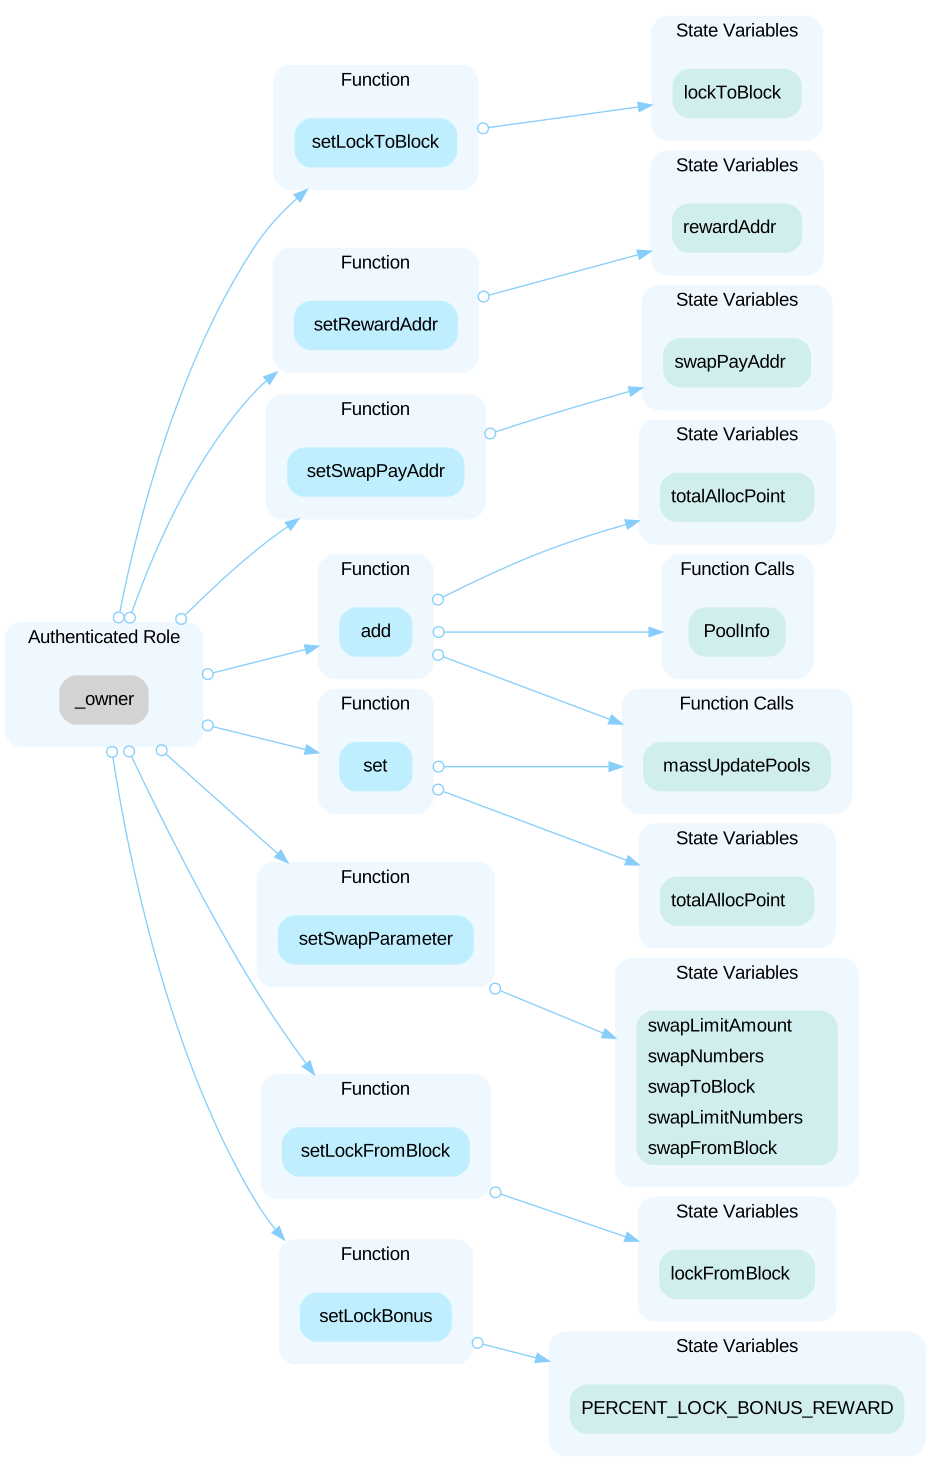 The function `safeMazeTransfer()` use `rewardAddr` to send the reward. But when the balances of the `rewardAddr` are not enough, the `rewardAddr` will transfer all the balance. In extreme cases, the balance of the `rewardAddr` is zero and users can never get the rewards.
MediumFees May Be StuckAcknowledged
The function `deposit()` takes 1% of the amount as the fees. However, there is no way to get those fees out.
Low`add()` Function Not RestrictedAcknowledged
When the same LP token is added into a pool more than once in function `add()`, the total amount of reward in function `updatePool()` will be incorrectly calculated. The current implementation is relying on the operation correctness to avoid repeatedly adding the same LP token to the pool, as the function will only be called by the owner.
LowIncompatibility With Deflationary TokensAcknowledged
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user stakes 100 deflationary tokens (with a 10% transaction fee) in a MasterChef, only 90 tokens actually arrived in the contract. However, the user can still withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. The MasterChef takes the pool token balance(the `lpSupply`) into account when calculating the users' reward. An attacker can repeat the process of deposit and withdraw to lower the token balance(`lpSupply`) in a deflationary token pool and cause the contract to increase the reward amount. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
LowMissing Emit EventsAcknowledged
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of MAZE’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us