CATCEO - Audit
CertiK reviewed CATCEO (CATCEO - Audit) on 30 Mar 2023: 5 findings, 0 critical; 2 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 1 |
| Medium | 0 | 0 | 1 |
| Low | 2 | 0 | 0 |
HighCentralization Risks in CATCEO.solFixed
In the contract `CATCEO` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and include/exclude account from fee/reward. 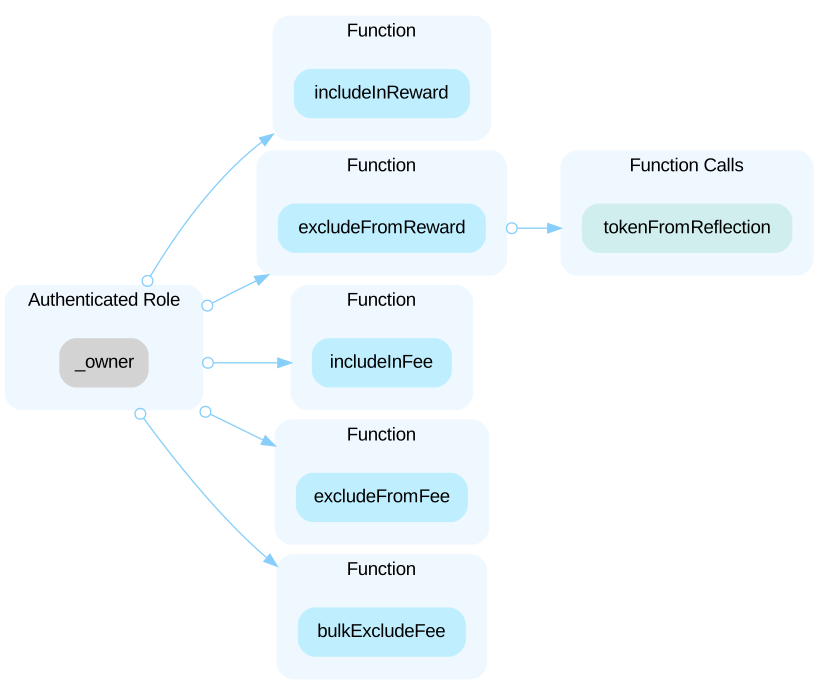 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 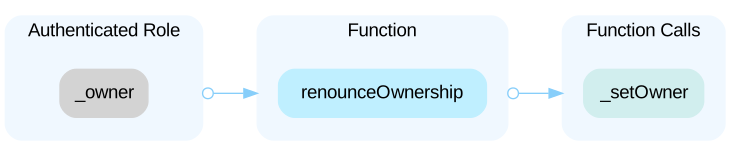
MediumVariable `_rOwned[account]` Not Updated in FunctiFixed
Variable `_rOwned[account]` is not updated in the function `includeInReward()`, which will make the accounts included siphon off the tokens out of the balances of all token holders. The Rate was higher at the moment of the `excludeFromReward(account)` call, so at the time of `includeInRewards(account)` the `_rOwned[account] / _tOwned[account]` ratio will be bigger than expected for the accounts to be included in the reward. ``` solidity=290 function includeInReward(address account) external onlyOwner { require(_isExcluded[account], "Account is not excluded"); for (uint256 i = 0; i < _excluded.length; i++) { if (_excluded[i] == account) { _excluded[i] = _excluded[_excluded.length - 1]; _tOwned[account] = 0; _isExcluded[account] = false; _excluded.pop(); break; } } } ```
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x4937e7d93dd8d8e76eb83659f109cdc633ffdee9 | Chain: BNB Chain | Source code: Verified source |
Part of CATCEO’s security record
 CATCEO
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us