Salad Ventures - Audit
CertiK reviewed Salad Ventures (Salad Ventures - Audit) on 20 Jun 2023: 8 findings, 1 critical; 7 marked fixed, 1 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 0 | 1 | 2 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 0 | 2 |
CriticalUnsafe Invariant CheckFixed
The `_invariantCheck` function assumes that the total balance of the `_asset` held by the contract should always match the contract's `_totalSupply` variable. However, this check does not consider the scenario where someone sends `_asset` tokens directly to the contract's address. If that happens, the balance of `_asset` in the contract will be more than the `_totalSupply`, making the invariant check fail and effectively locking the deposit, withdraw and emergency withdraw operations, even for legitimate users.
HighCentralization Risks in SaladBowl.solFixed
In the contract `SaladBowl` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the rewards and pause/unpause the contract. 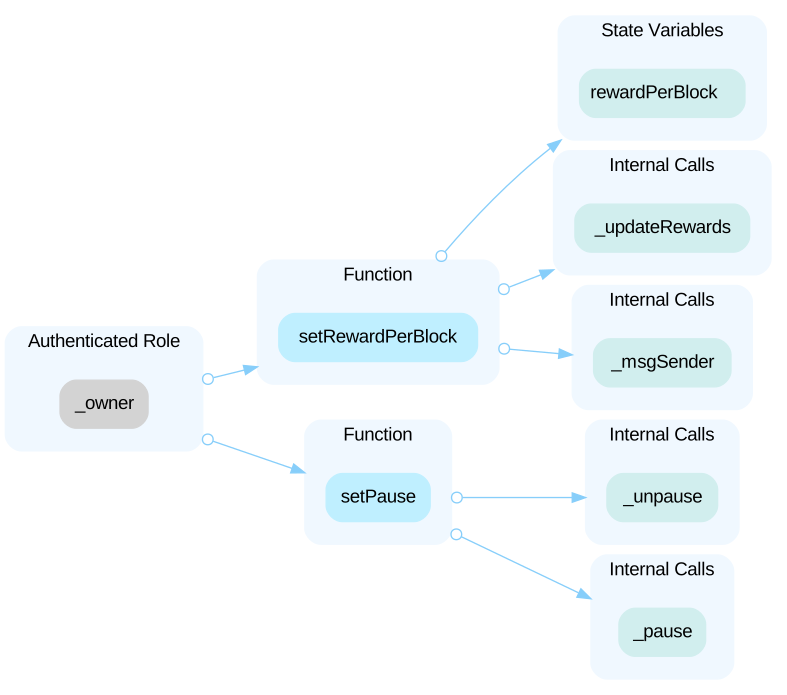
HighPausing Centralization RisksFixed
In the contract `SaladBowl`, the role `_owner` has the authority to update the status of the `whenNotPaused` and further pause/resume the functionality of the following functions: - `deposit` - `withdraw` - `harvest` Any compromise to the private key of the `owner` may allow hackers to take advantage of this authority and allow/prevent external user access to the sensitive functionalities controlled by the whenNotPaused modifier.
MediumHighly gas inefficient reward calculation processFixed
The function `_updateRewards` updates the rewards for all `_stakers` during each `deposit`, `withdraw` and `harvest` action. When the `_stakers` is large, this can result in high gas consumption for users performing these operations In addition, this could lead to a gas limit issue if the number of `_stakers` grows large, preventing the execution of previously highlighted functions.
MediumLack of Input ValidationFixed
The `deposit` function in this contract does not perform any check to ensure that the amount parameter is greater than zero. If a user calls the `deposit` function with an amount of zero, it will add the user to the `_balances` map, `_stakerIndex` map and `_stakers` array.
LowMissing Emit EventsFixed
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowState Variable Should Be Declared ConstantFixed
State variables that never change should be declared as `constant` to save gas. ```solidity=13 uint public TOTAL_SUPPLY = 1_680_000_000e18; // 1.68b SALD ``` - `TOTAL_SUPPLY` should be declared `constant`.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- contracts/SaladToken.sol
- contracts/SaladBowl.sol
Part of Salad Ventures’s security record
 Salad Ventures
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us