Wemix Retainer 78 NewFanToken
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 78 NewFanToken) on 4 Jan 2024: 30 findings, 0 critical; 26 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings30
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 6 |
| Low | 3 | 0 | 20 |
HighCentralization Related RisksOpen
In the contract `FanNFTMinter` the role `_editor` has authority over the functions shown in the diagram below. Any compromise to the `_editor` account may allow the hacker to take advantage of this authority and mint NFT. 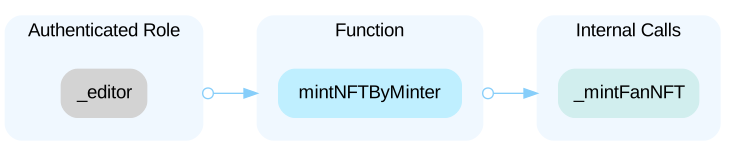 In the contract `FanNFTMinter` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 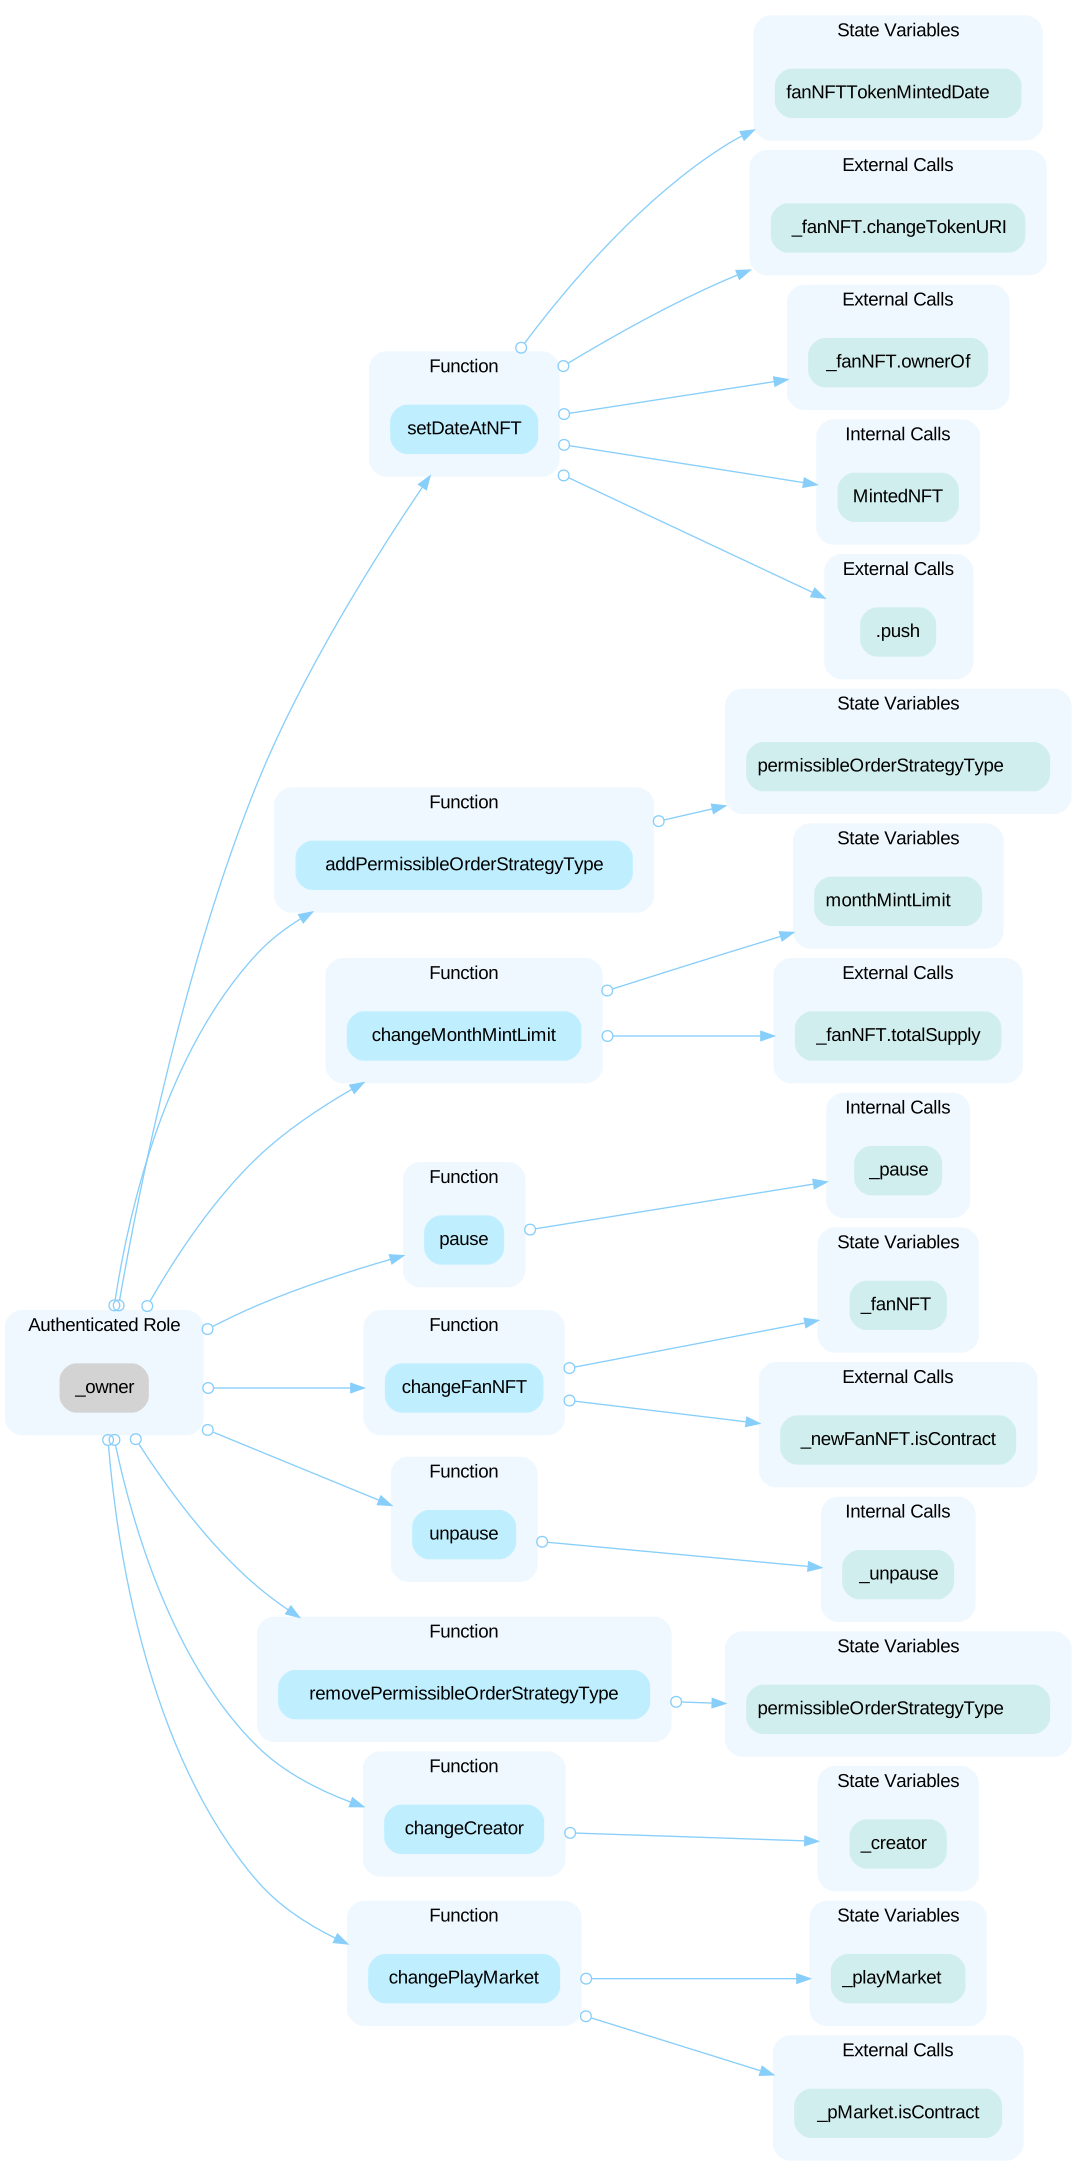 ----- In the contract `FanTokenFactory` the role `_editor` has authority over the functions shown in the diagram below. Any compromise to the `_editor` account may allow the hacker to take advantage of this authority. 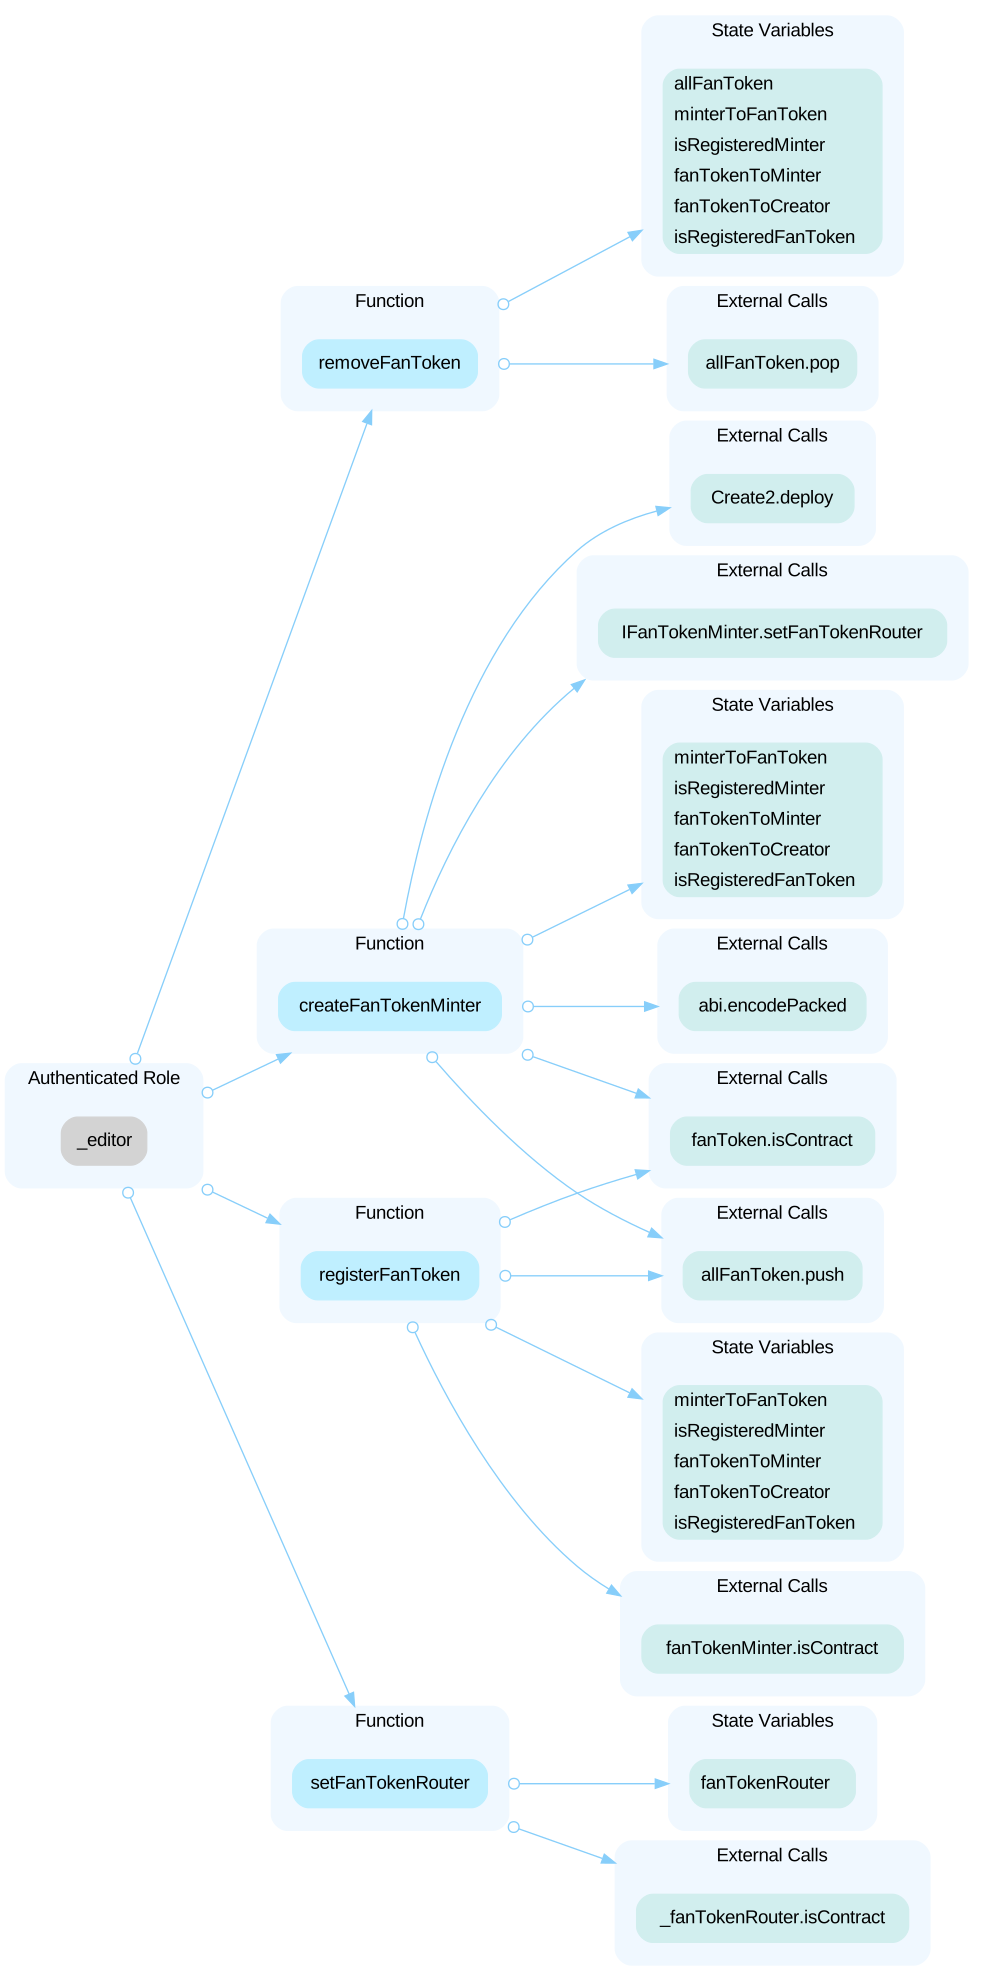 ----- In the contract `FanTokenMarket` the role `_editor` has authority over the functions shown in the diagram below. Any compromise to the `_editor` account may allow the hacker to take advantage of this authority and drain funds. 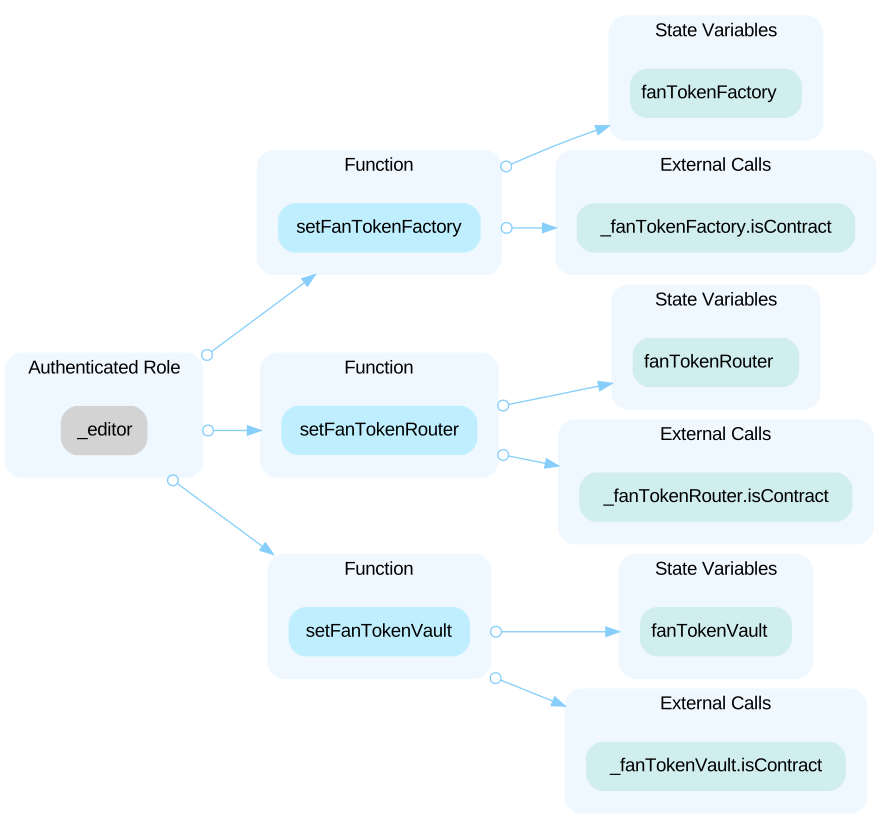 ----- In the contract `FanTokenMinter` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 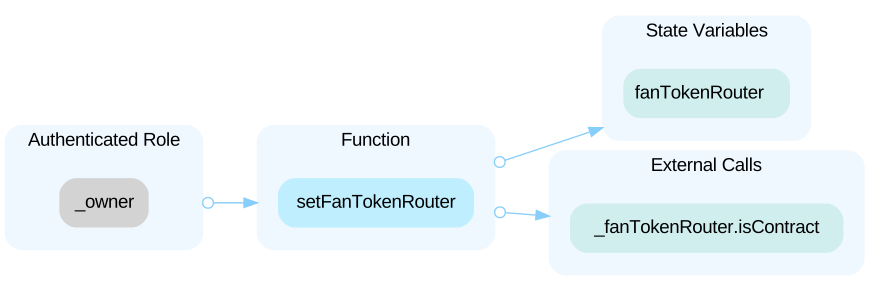 In the contract `FanTokenMinter` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority. 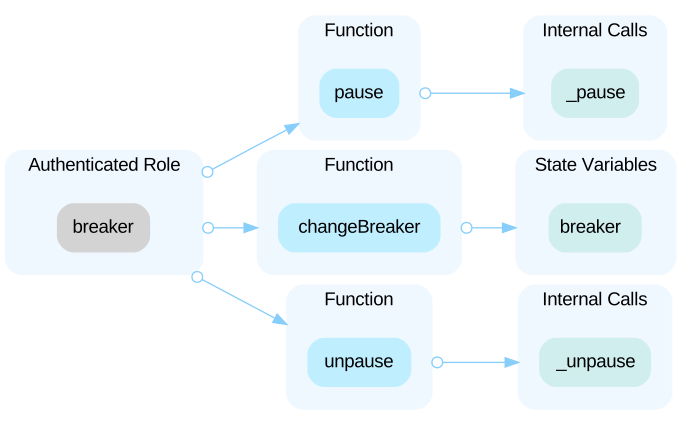 In the contract `FanTokenMinter` the role `parameterSetter` has authority over the functions shown in the diagram below. Any compromise to the `parameterSetter` account may allow the hacker to take advantage of this authority. 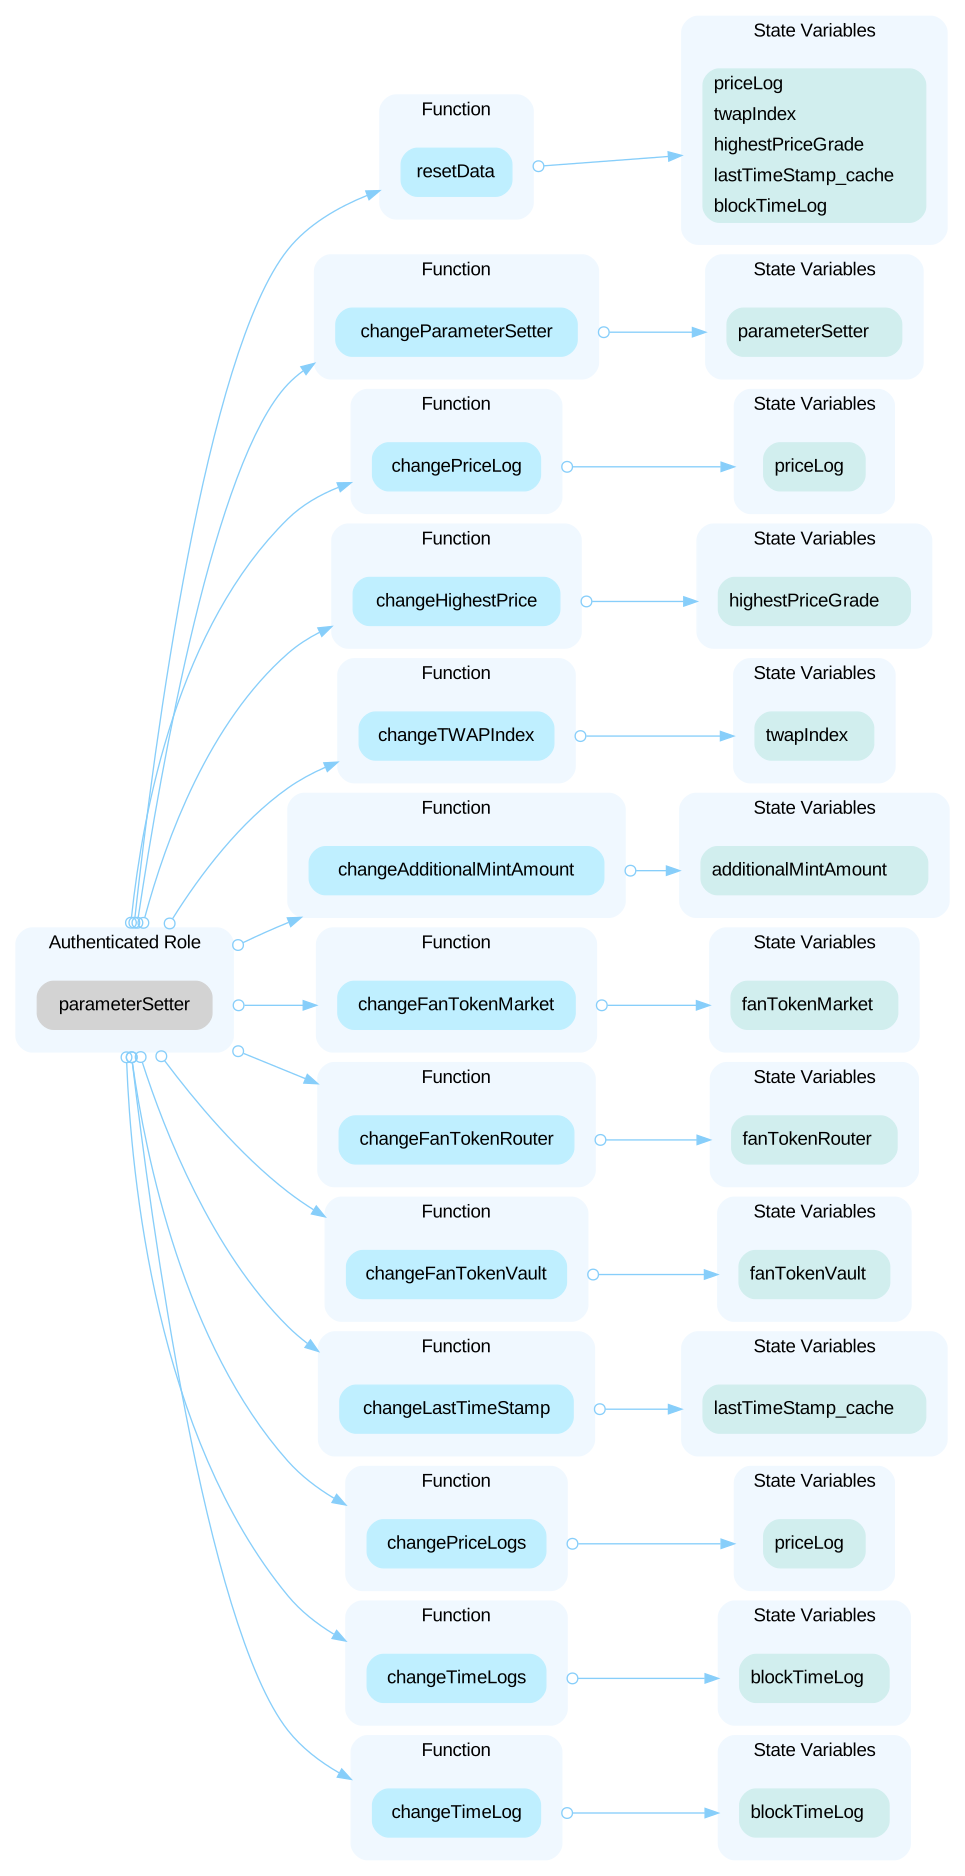 ----- In the contract `FanTokenRouter` the role `_editor` has authority over the functions shown in the diagram below. Any compromise to the `_editor` account may allow the hacker to take advantage of this authority. 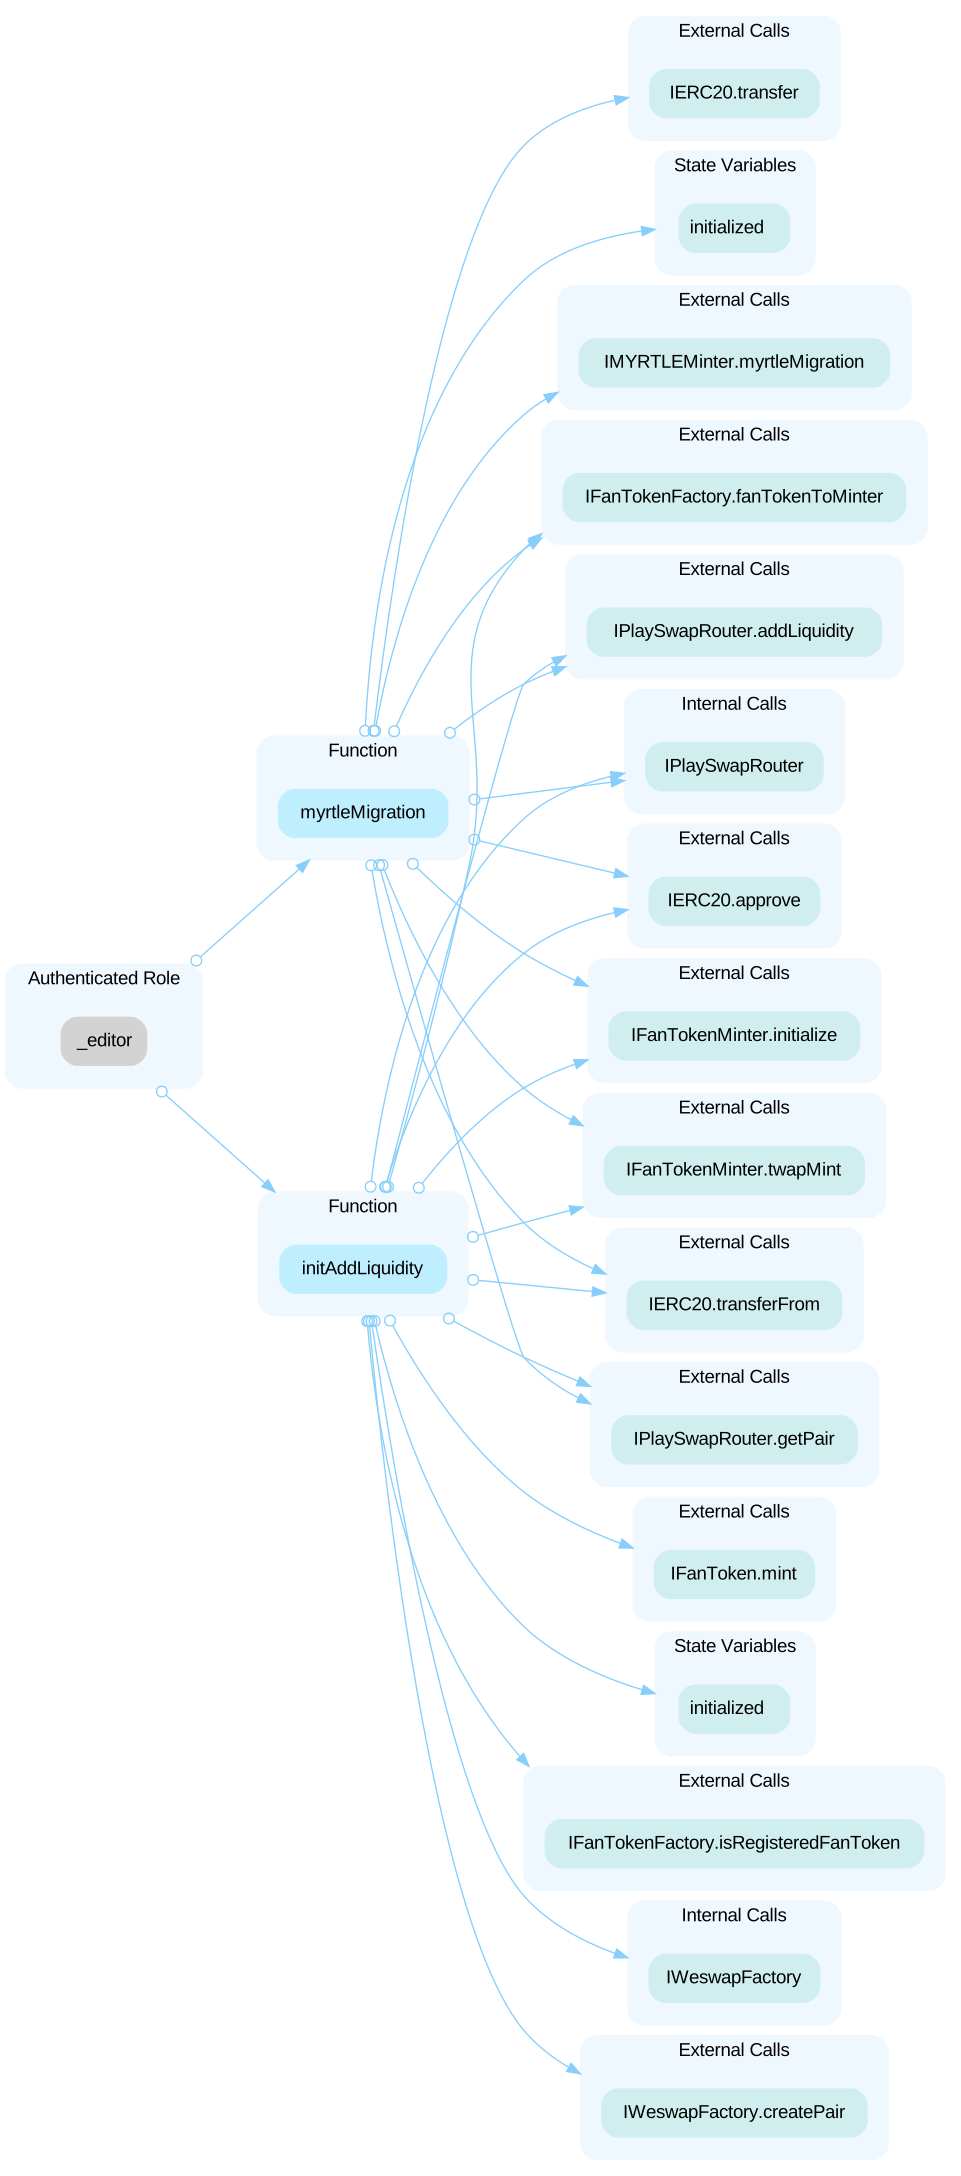 In the contract `FanTokenRouter` the role `batch` has authority over the functions shown in the diagram below. Any compromise to the `batch` account may allow the hacker to take advantage of this authority. 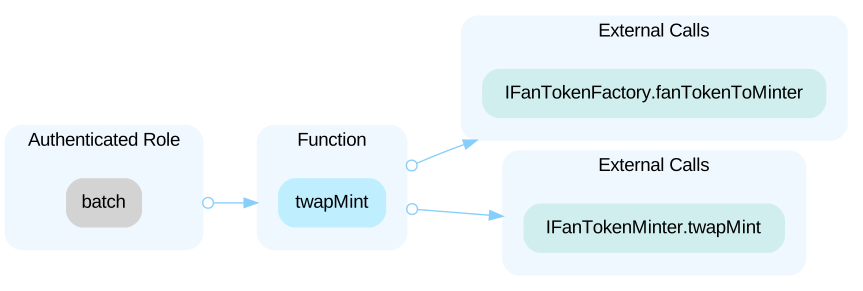 In the contract `FanTokenRouter` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority. 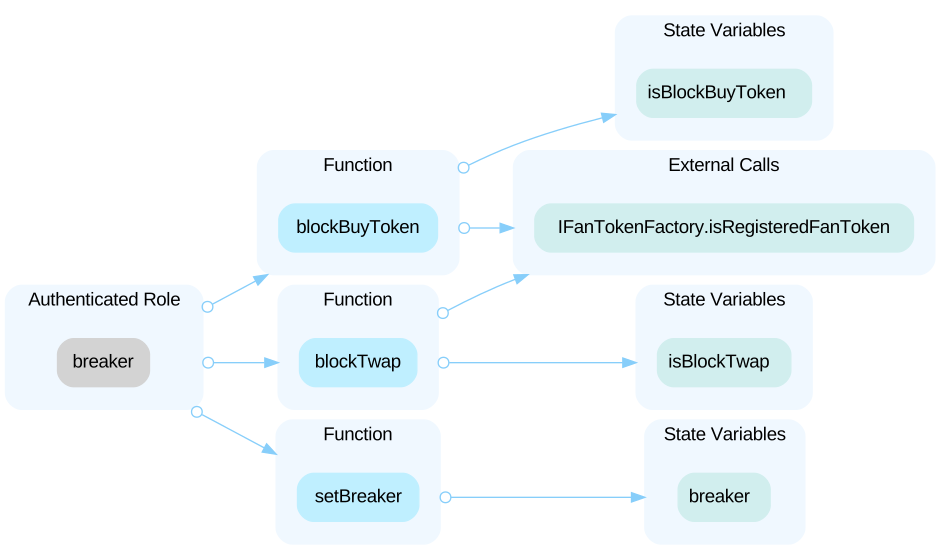 In the contract `FanTokenRouter` the role `parameterSetter` has authority over the functions shown in the diagram below. Any compromise to the `parameterSetter` account may allow the hacker to take advantage of this authority. 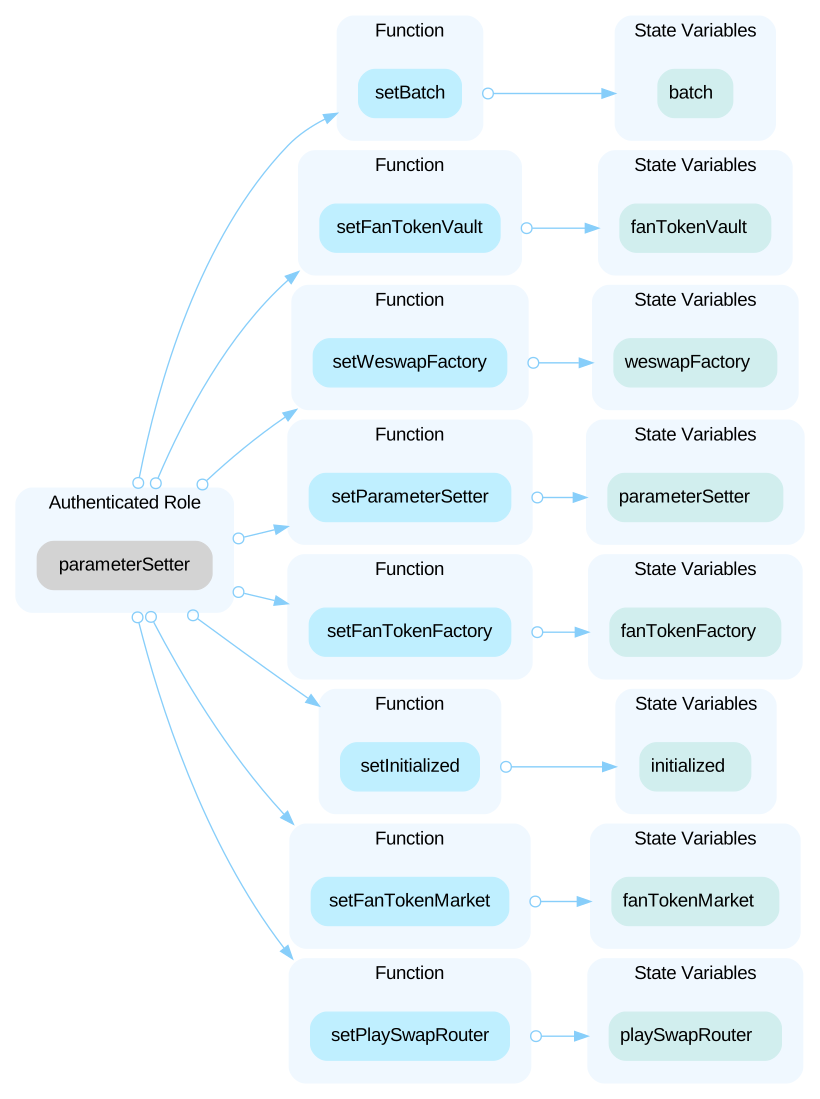 ----- In the contract `FanTokenVault` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and drain funds. 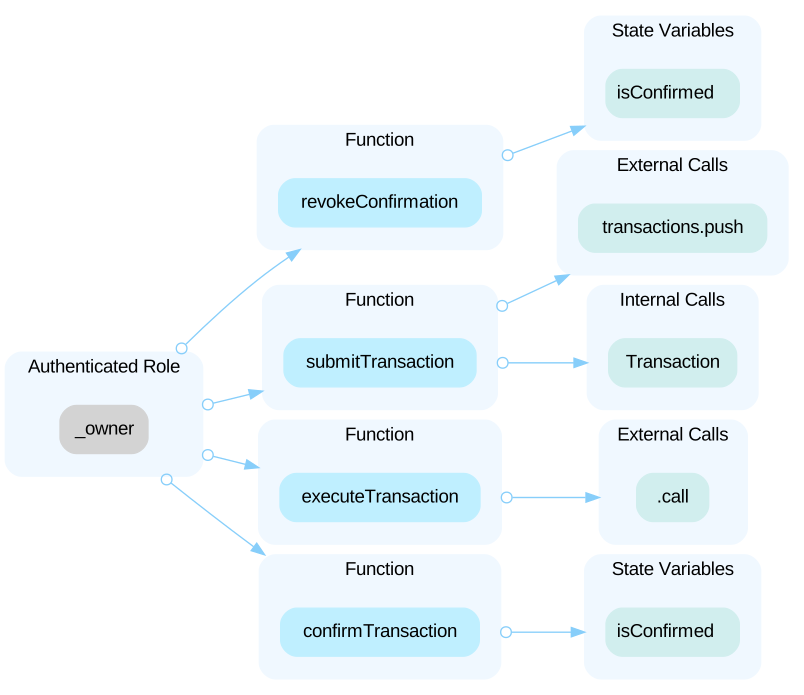 ----- In the contract `GameTokenTwapRouter` the role `_editor` has authority over the functions shown in the diagram below. Any compromise to the `_editor` account may allow the hacker to take advantage of this authority. 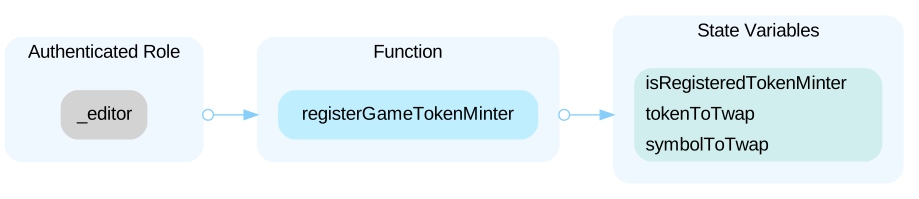 ----- In the contract `NightCrowTWAP` the role `_ow
LowLack of validation on token URIOpen
The NFT token URI is specified by the editor role but lacks duplication validation to prevent NFT tokens from sharing the same URI. NFT tokens are inherently unique, and their URIs should not be identical.
LowMint less fan tokens if `twapMint()` is not calleOpen
The minter of the fan token (`fanTokenToMinter[fanToken]`) can be modified using the `factory::registerFanToken()` or `factory::createFanTokenMinter()` functions. However, the `minter::twapMint()` function is not invoked for the new minter to initiate the "first twap record." If price of fan token increases from \$1 to \$1.1, and `twapMint()` is called for the first time, with `twapGrade = highestPriceGrade` (FanTokenMinter, L353), the `mintingAmount` calculated by `_computeMintable()` is zero. Therefore, no fan token will be minted, even though token price has increased.
LowMissing Update `initialized` State VariableOpen
Based on the implementation of the `myrtleMigration()` and `initAddLiquidity()` functions, it is evident that the state variable `initialized` is employed to track the initialization status of the FanToken by invoking the `initialize()` function within the `FanTokenMinter.sol` file. Nevertheless, in the `upgradeMinter()` function, there is an absence of code logic to update the state variable `initialized`, despite the invocation of the `initialize()` function at line 86. ```solidity=33 mapping(address => bool) public initialized; ``` ```solidity=78 //only for upgrading FanTokenMinter function upgradeMinter(uint highestPrice, address fanToken) external onlyEditor NotZeroAddress(fanToken) { address fanTokenMinter = IFanTokenFactory(fanTokenFactory).fanTokenToMinter(fanToken); require(fanTokenMinter != address(0), "FTR : MYRTLE is not registered in factory"); address swapPair = IPlaySwapRouter(playSwapRouter).getPair(fanToken, WEMIXDollar); require(swapPair != address(0), "FTR : swap pool is not created"); IFanTokenMinter(fanTokenMinter).initialize(parameterSetter, breaker, fanTokenVault, WEMIXDollar,fanTokenMarket, fanToken, swapPair); ISpecialTokenMinter(fanTokenMinter).specialMigration(highestPrice); IFanTokenMinter(fanTokenMinter).twapMint(); } ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (15)
- FanToken/contracts/FanTokenMarket.sol
- FanToken/contracts/tokens/FanNFT.sol
- FanToken/contracts/FanTokenMinter.sol
- FanToken/contracts/MYRTLE/MYRTLE.sol
- FanToken/contracts/FanTokenVault.sol
- FanToken/contracts/FanTokenFactory.sol
- FanToken/contracts/MYRTLE/MYRTLENFT.sol
- FanToken/contracts/FanNFTMinter.sol
- FanToken/contracts/tokens/FanToken.sol
- FanToken/contracts/GameTokenTwapRouter.sol
- FanToken/contracts/FanTokenRouter.sol
- FanToken/contracts/MYRTLE/MYRTLEMinter.sol
- FanToken/contracts/tokens/PapyrusNFT.sol
- FanToken/contracts/NightCrowTWAP.sol
- FanToken/contracts/MYRTLE/MYRTLENFTMinter.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us