maxdao
CertiK reviewed MaxDAO on 26 Sep 2022: 13 findings, 0 critical; 8 marked fixed, 4 acknowledged, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings13
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 2 | 2 |
| Low | 1 | 0 | 6 |
HighCentralization Risks in MaxDAO.solAcknowledged
In the contract `MaxDAO` the role `_owner` has authority over the functions shown in the diagram below. 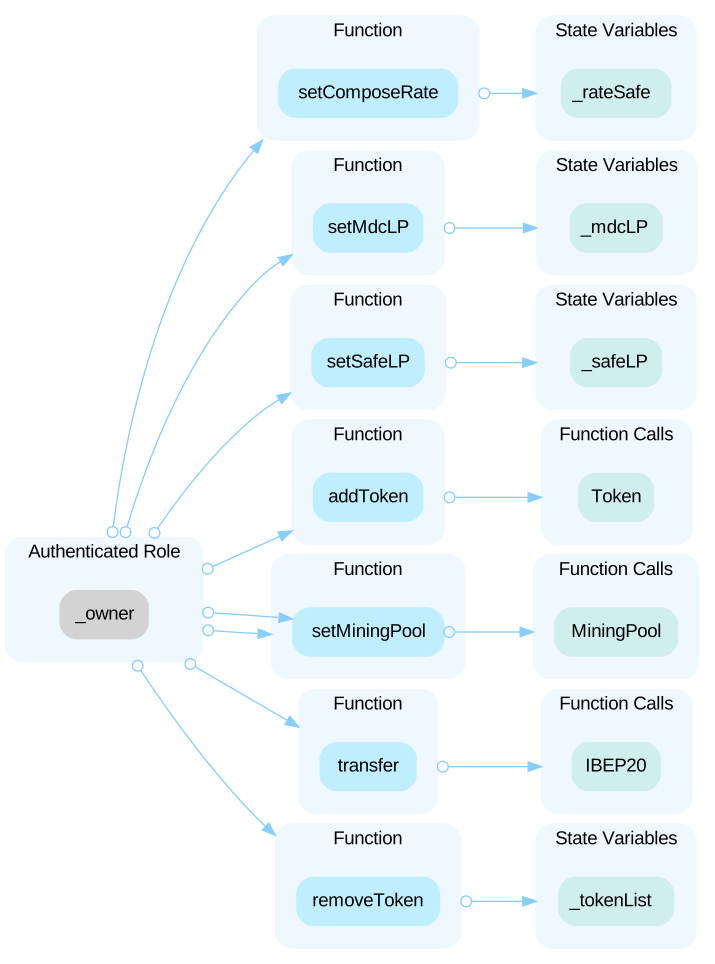 --- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 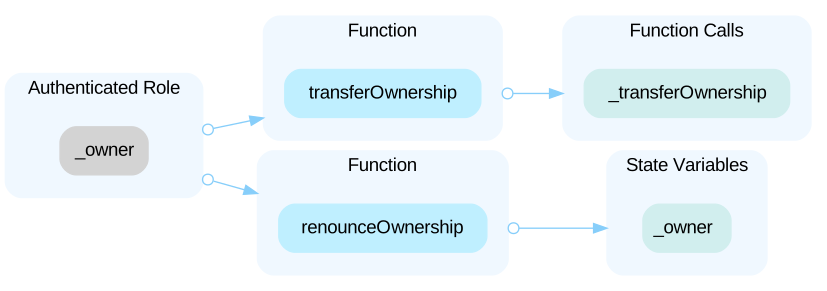 Any compromise to the privileged accounts may allow the hacker to take advantage of this authority, update the sensitive settings, and execute sensitive functions of the project.
HighCentralization Risks in MDC.solAcknowledged
In the contract `MDC` the role `_allowMint` has authority over the functions shown in the diagram below. 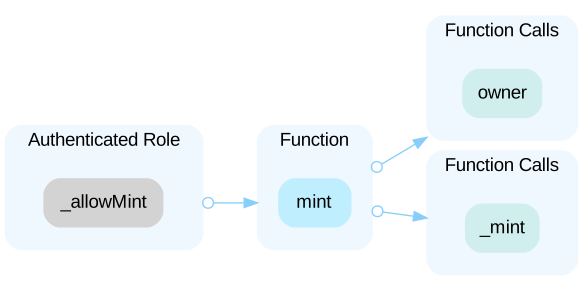 --- In the contract `MDC` the role `_owner` has authority over the functions shown in the diagram below. 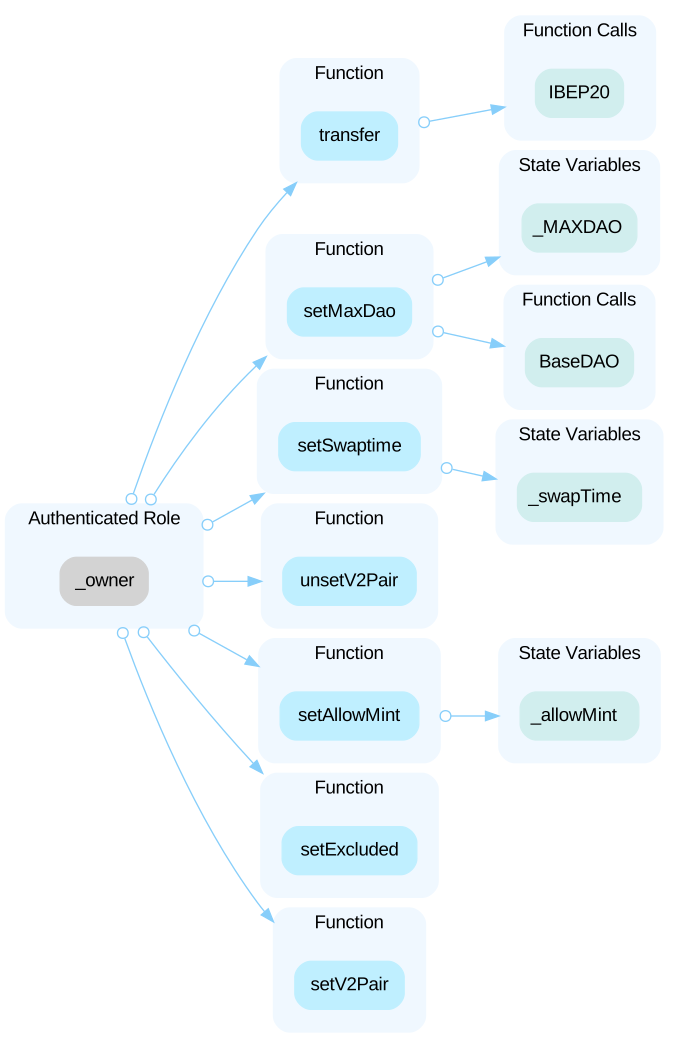 --- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 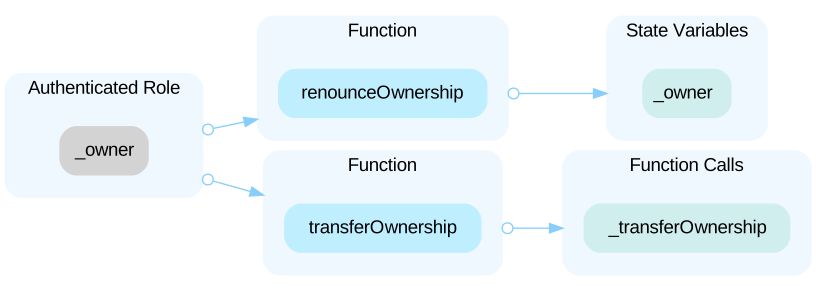 Any compromise to the privileged accounts may allow the hacker to take advantage of this authority, update the sensitive settings, and execute sensitive functions of the project.
MediumOpenZeppelin library code included in source codeAcknowledged
Here is the description text of a finding from that project that might be relevant. It is highly recommended NOT to include OpenZeppelin library code directly in the source code, but import the original library to minimize risk because even slight changes to the library code may lead to critical/major vulnerabilities/bugs. For Solidity version 0.6.x, the latest OpenZeppelin version 3.4.2 should be used.
MediumUnchecked Token DecimalAcknowledged
In the function `depositAlone()`, `currentValue` is calculated with the unit of the token, which is hardcoded as `1e18`. Considering `_token` may have decimal precision other than 18 digits, therefore, the actual unit decimal of the token in `_token` address would be inconsistent with the 1e18.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- MaxDAO.sol
- MDC.sol
Part of MaxDAO’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us