Wemix PoET Retainer 52
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix PoET Retainer 52) on 25 Aug 2023: 9 findings, 0 critical; 6 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings9
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 2 | 0 | 5 |
HighCentralization Risks in PoET.solOpen
In the contract `PoET` the role `_operator` has authority over the functions shown in the diagram below. Any compromise to the `_operator` account may allow the hacker to take advantage of this authority and setting high rewards for hacker affiliated addresses and subsequently drain WEMIX token from the contract. 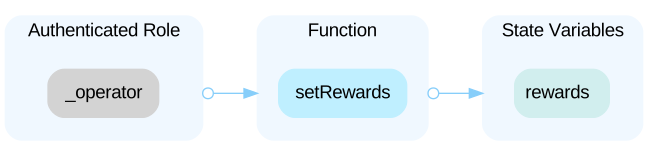 In the contract `PoET` the role `_operatormanager` has authority over the functions shown in the diagram below. Any compromise to the `_operatormanager` account may allow the hacker to take advantage of this authority and change operators. 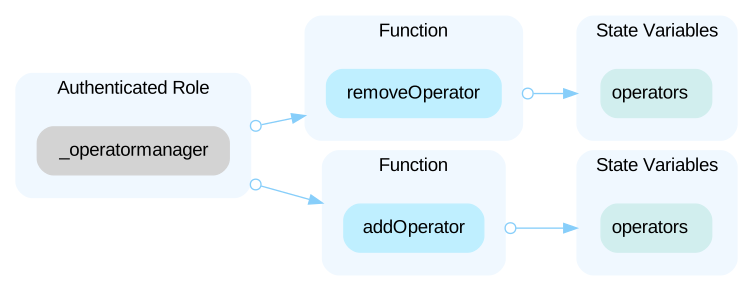 In the contract `PoET` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change `_operatormanager` 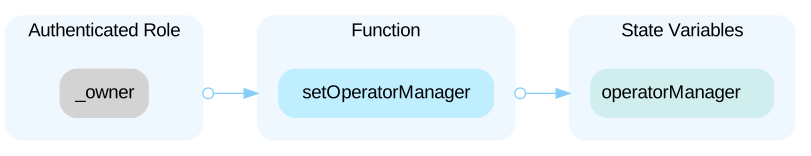
LowPotential Outdated Library UsageOpen
The `initialize()` function of the `PoET` contract contains `__Ownable_init()` with no function argument. In the latest OpenZepplin library, the `__Ownable_init()` function contains an `initialOwner` function argument, as seen here: https://github.com/OpenZeppelin/openzeppelin-contracts-upgradeable/blob/master/contracts/access/OwnableUpgradeable.sol This indicates that the OpenZeppelin library being used might not be the latest one. In certain situations, this might create real problems. For example, if the deployer of the `PoET` logic contract is the same as the Admin or Owner of the proxy contract, and if the proxy contract uses the Transparent Proxy pattern that only delegate calls to the `PoET` contract from non admin / non owner addresses, then the `onlyOwner` function in `PoET` contract might be unreachable, as the proxy contract would not reach the `fallback()` function if the caller is the admin / owner address.
LowThird-Party DependenciesOpen
The `PoET` contract is a logic contract that should be used in connection with a proxy contract. The scope of the audit does not include the proxy contract itself, and this audit treats it as a black box and assumes its functional correctness. However, if the proxy contract contains errors or vulnerabilities, it may lead to loss or stolen assets, such as via upgrading the contract to allow the hacker to withdraw all Wemix tokens.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- contracts/interfaces/IPoET.sol
- contracts/PoET.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us