Wemix DIOSG - Retainer 32
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix DIOSG - Retainer 32) on 9 Jun 2023: 11 findings, 0 critical; 5 marked fixed, 6 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings11
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 3 |
| Medium | 0 | 0 | 0 |
| Low | 4 | 0 | 2 |
HighCentralization Related RisksOpen
In the contract `AuthorizedMintAccess` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change whitelist status or sensitive state addresses. 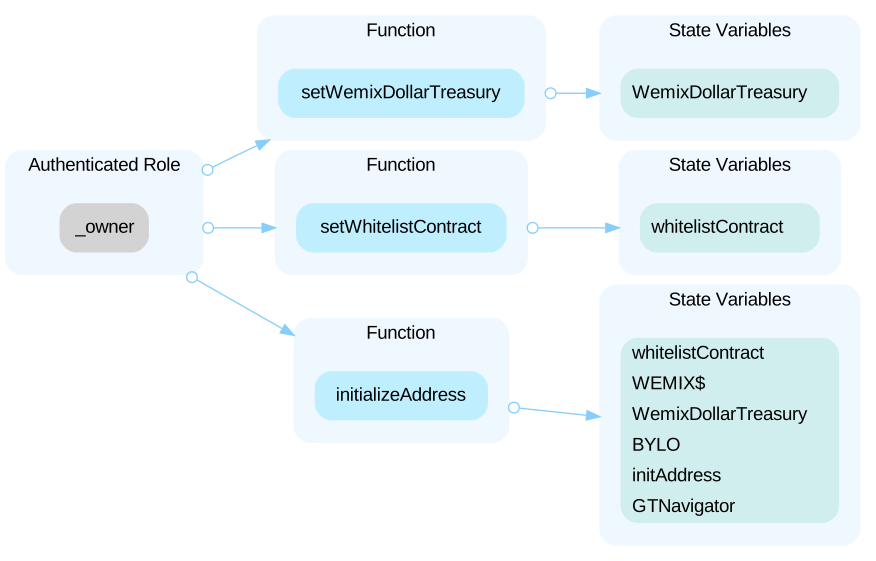 In the contract `AuthorizedMintAccess` the role `_whitelistaddresses` has authority over the functions shown in the diagram below. Any compromise to the `_whitelistaddresses` account may allow the hacker to take advantage of this authority and call for the exchange of WEMIX$ and BYLO tokens. 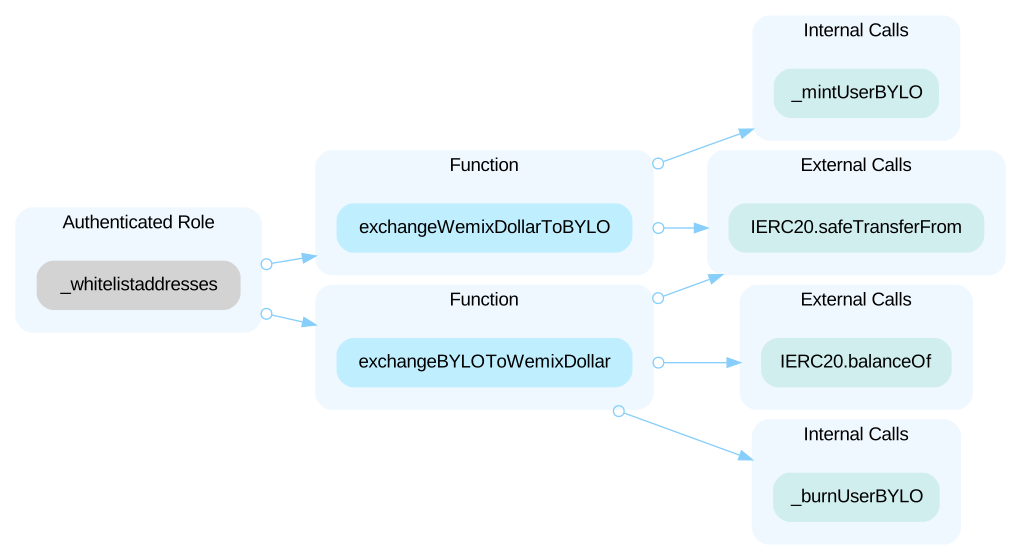 In the contract `AuthorizedMintAccess` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority and stop or resume contract functionality. 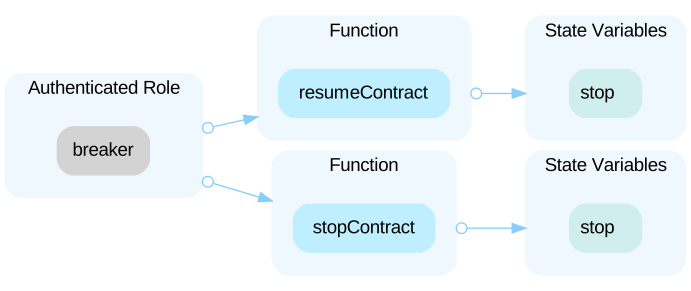 In the contract `AuthorizedMintAccess` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority and change the respective breaker or breakerSetter addresses. 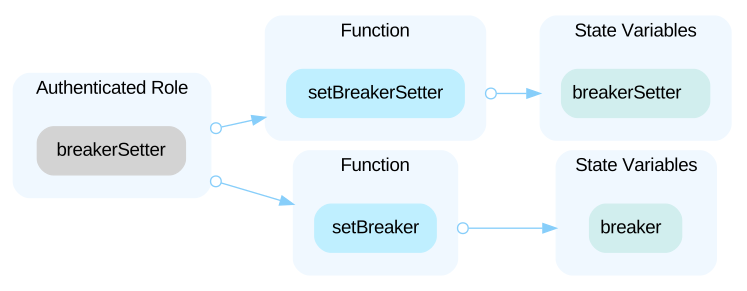 In the contract `WemixDollarTreasury` the role `_isOwner` has authority over the functions shown in the diagram below. Any compromise to the `_isOwner` account may allow the hacker to take advantage of this authority and create and process transactions through their lifecycle. 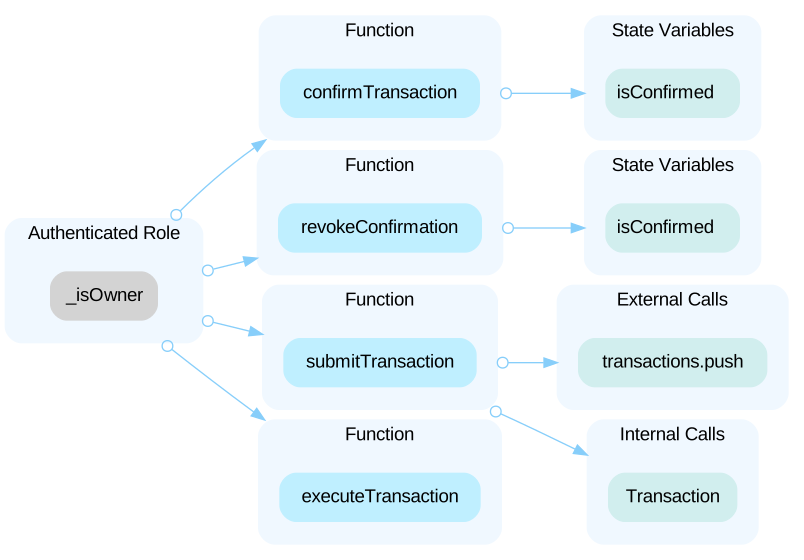 In the contract `WemixDollarTreasury` the role `_wallet` has authority over the functions shown in the diagram below. Any compromise to the `_wallet` account may allow the hacker to take advantage of this authority and add/remove/replace owners. 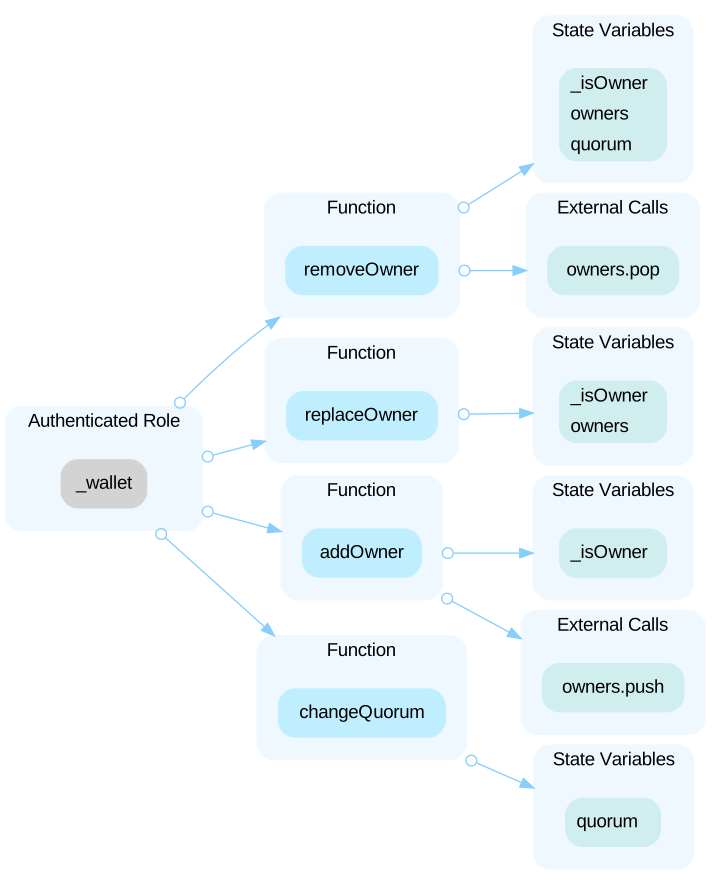 In the contract `DollarInAndOutStabilizerGame` the role `_isOwner` has authority over the functions shown in the diagram below. Any compromise to the `_isOwner` account may allow the hacker to take advantage of this authority and change sensitive contract state data including respective addresses, fees, and `stakingSwitch`. 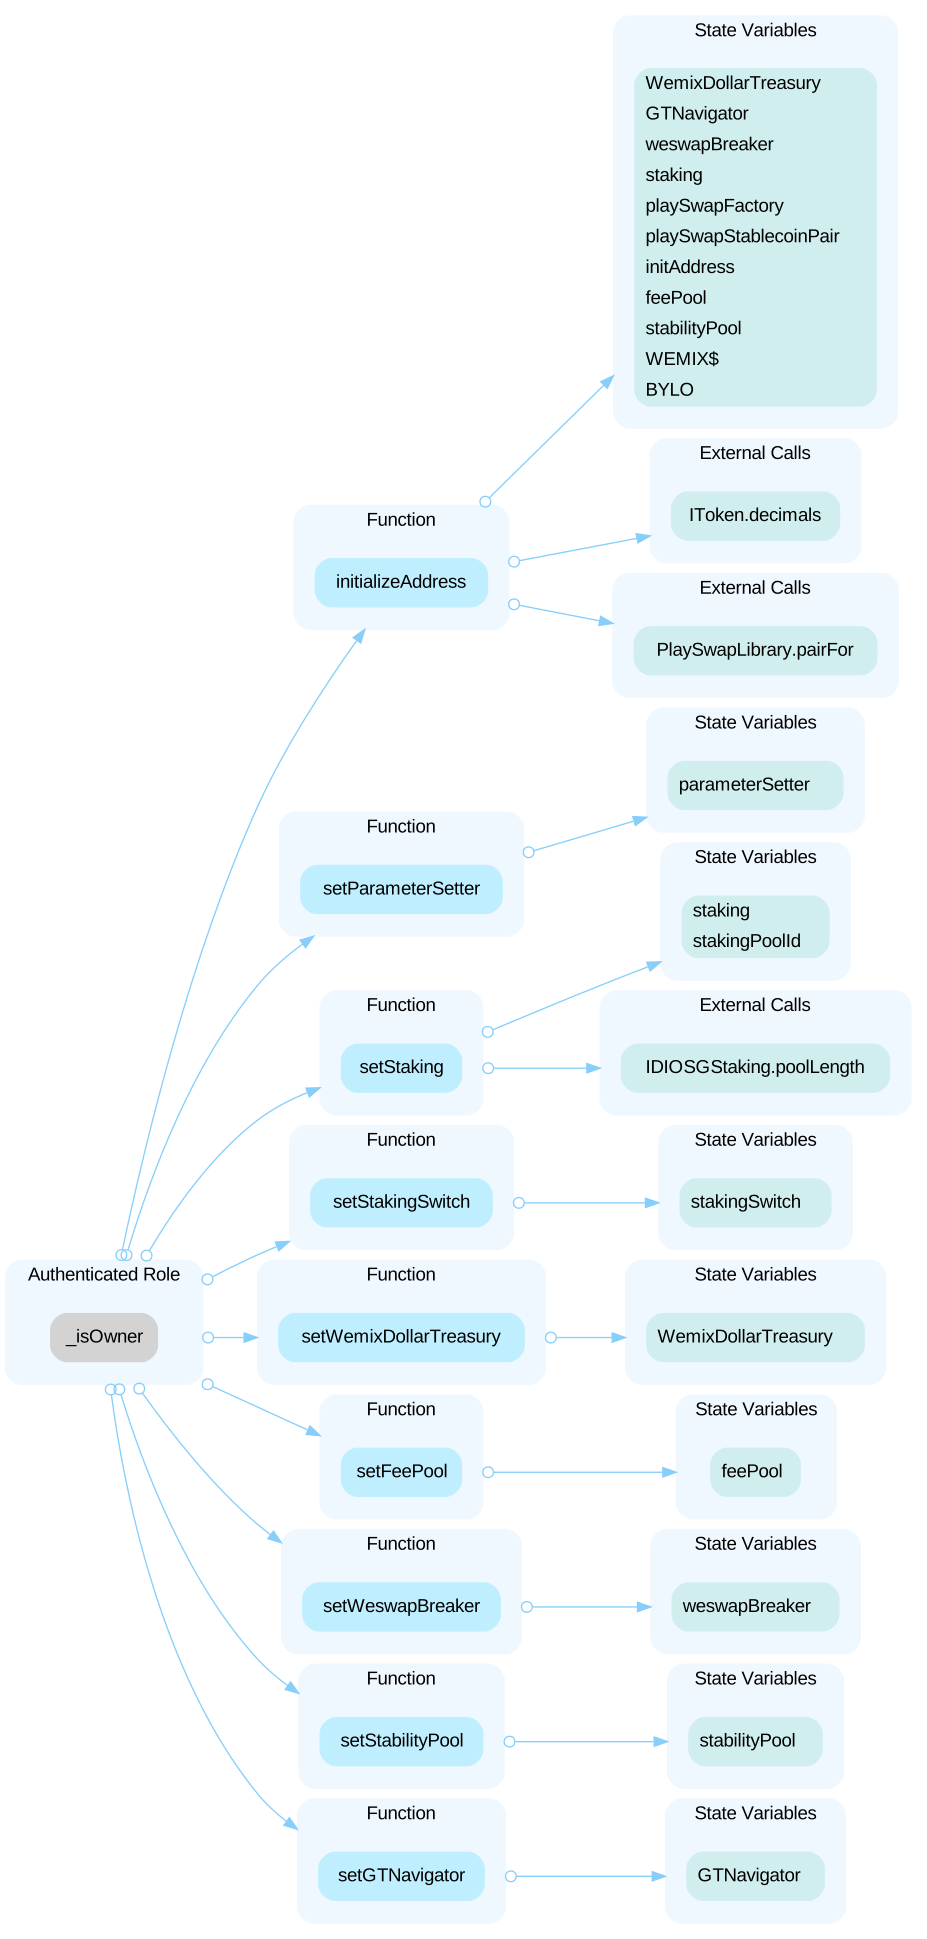 In the contract `DollarInAndOutStabilizerGame` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority and stop or resume contract functionality. 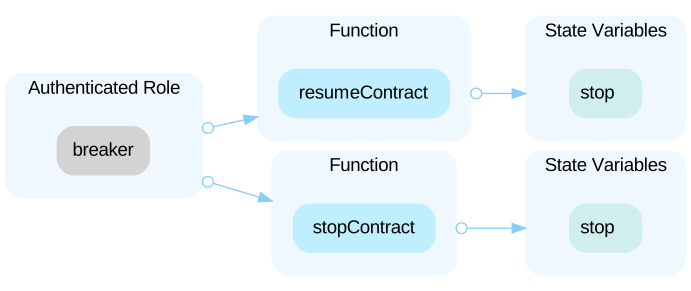 In the contract `DollarInAndOutStabilizerGame` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority and change the respective breaker or breakerSetter addresses. 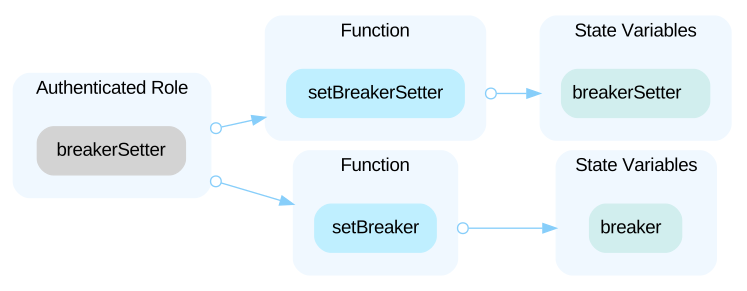 In the contract `DollarInAndOutStabilizerGame` the role `parameterSetter` has authority over the functions shown in the diagram below. Any compromise to the `parameterSetter` account may allow the hacker to take advantage of this authority and change sensitive contract state data. 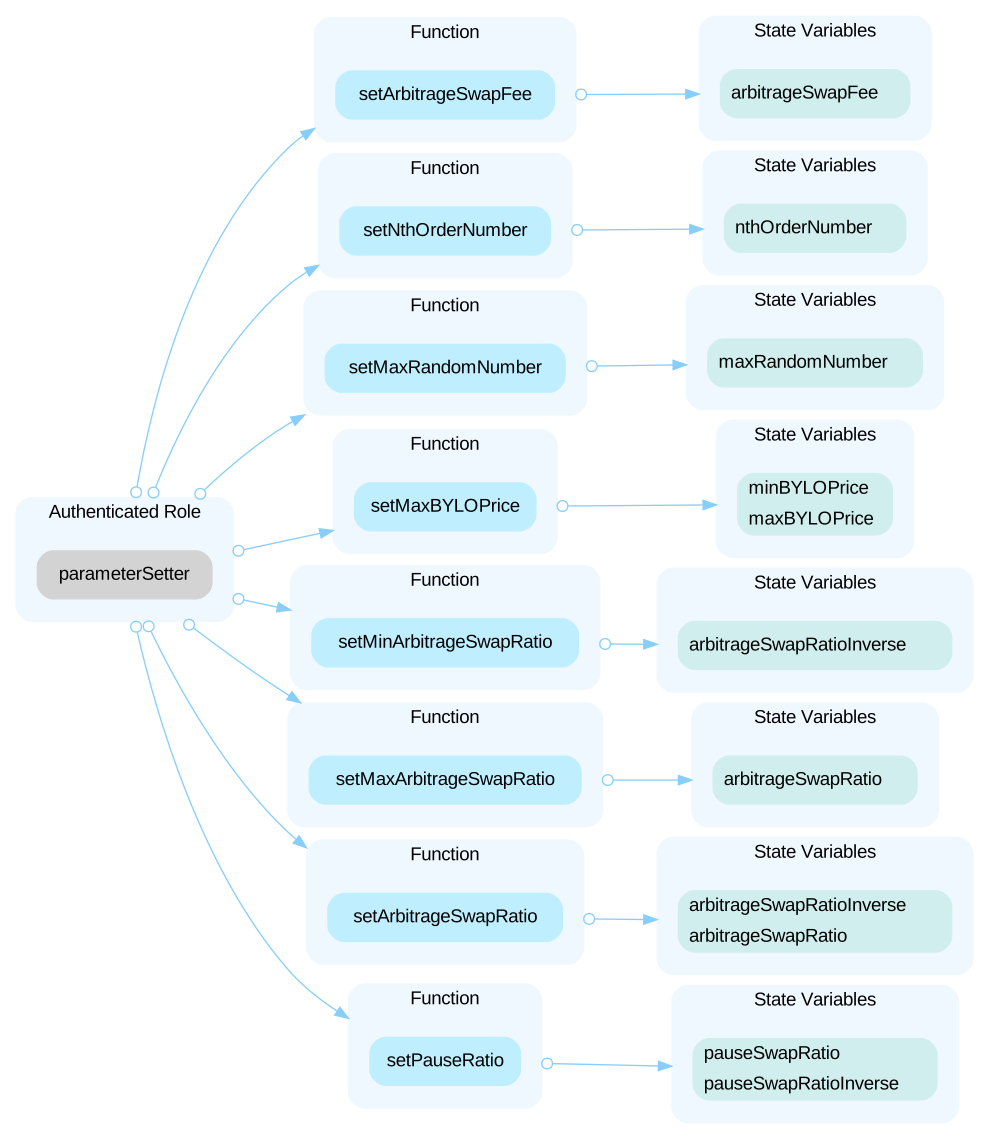 In the contract `DollarInAndOutStabilizerGame` the role `swapExecutor` has authority over the functions shown in the diagram below. Any compromise to the `swapExecutor` account may allow the hacker to take advantage of this authority and call for arbitrage swaps to be executed. ` defined in the comment it is not implemented in the code and could be false. See the scenario section for more information.
LowThird-Party DependenciesOpen
The audited code base contains external dependencies that are not in scope for this particular audit engagement, including but is not limited to: `GTNavigator`, `whitelistContract`, `WeswapBreaker`, `WeswapPair`, `BYLO` token, etc. The scope of the audit treats these entities as black boxes and assumes their functional correctness. However, in the real world, they can be compromised and this may lead to lost or stolen assets.
LowUsage of Magic NumbersOpen
In the functions `computeProfitMaximizingTradeRenewal` and `computeProfitMaximizingStablecoinPoolTrade` used for swap amountIn calculation, the magic number used in the calculation of `leftSide` and `rightSide`. We need confirm the mathematics of the formulas. Why the number `53200`, `53067`, and `636804` are used for the left side and `799`, `798`( `636804`'s square root ) for the right side.
LowWeak PRNGOpen
The functions `DollarInAndOutStabilizerGame.quadraticRandomPrice()` and `DollarInAndOutStabilizerGame._linearRandomPrice()` utilize modulus operation on the parameter `_randomNumber` to calculate `randomNumber`, a pseudo-random number. This value is then used for price calculation and may be influenced by a user who can change the `_randomNumber` parameter by sending and canceling transactions to calculate a more desirable price.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (9)
- PlaySwapLibrary.sol
- PlaySwapLiquidityMathLibrary.sol
- IAuthorizedMintAccess.sol
- IWeswapBreaker.sol
- Math.sol
- IDollarInAndOutStabilizerGame.sol
- IDIOSGStaking.sol
- IToken.sol
- IWemixDollarTreasury.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us