Xwin Finance
CertiK reviewed xWIN Finance on 24 Aug 2022: 25 findings, 0 critical; 14 marked fixed, 11 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings25
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 6 | 0 | 2 |
| Medium | 2 | 0 | 3 |
| Low | 3 | 0 | 9 |
HighCentralization Related Risks in ToppyMysteriousNFOpen
In the contract `ToppyMysteriousNFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 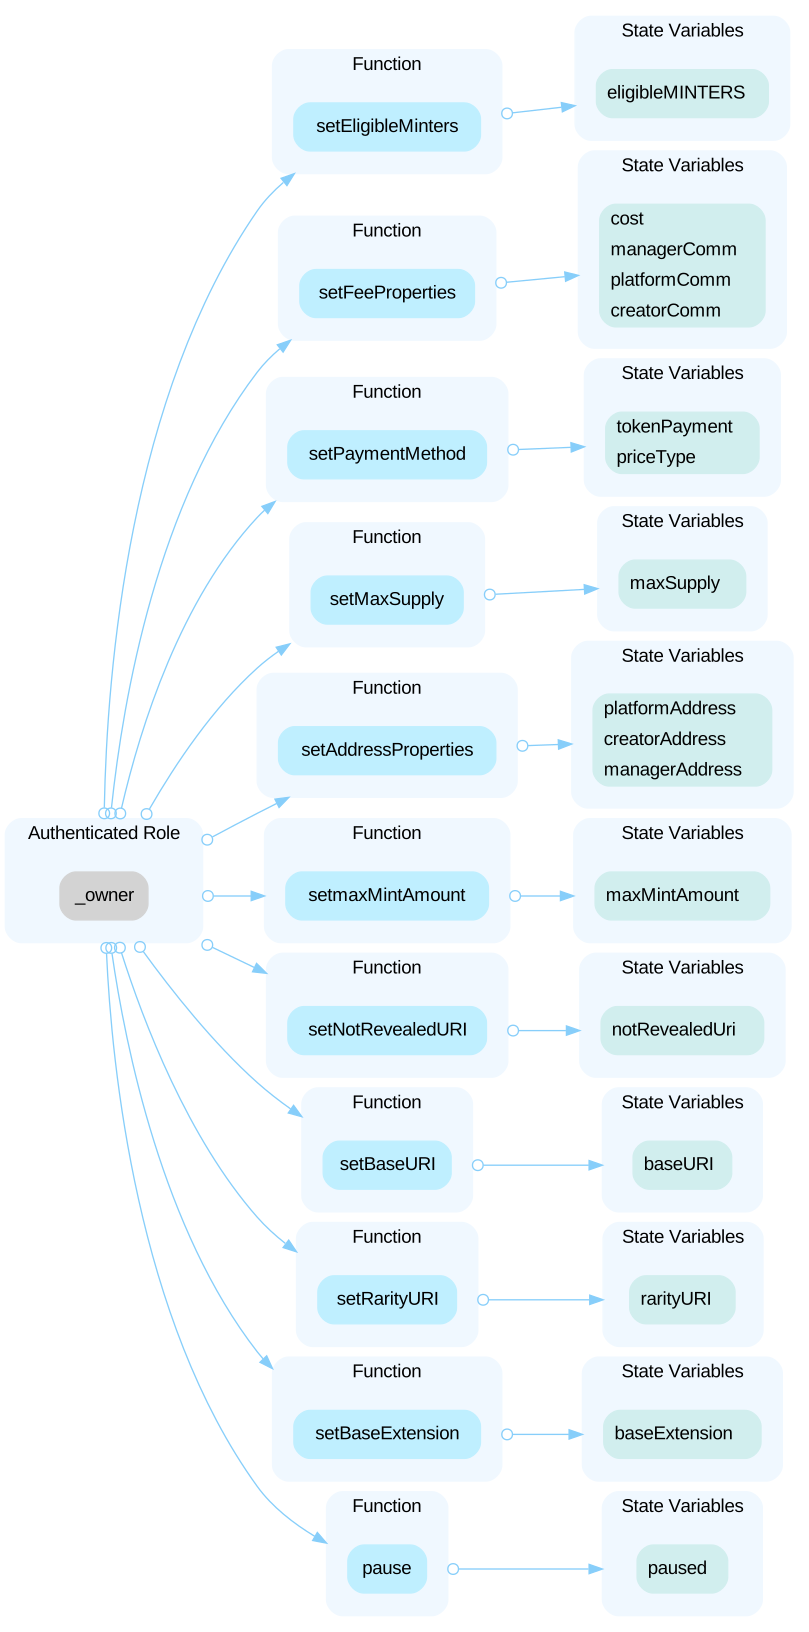
HighCentralization Risk in ToppyMarketplace.solOpen
In the contract `ToppyMarketPlace` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 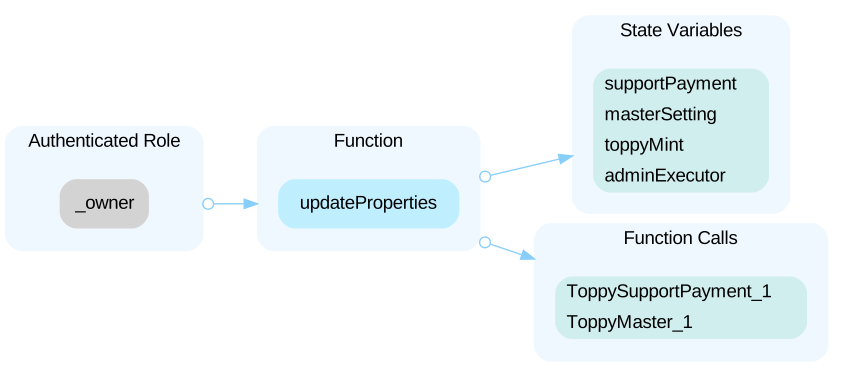 In the contract `ToppyMarketPlace` the role `adminExecutor` has authority over the functions shown in the diagram below. Any compromise to the `adminExecutor` account may allow the hacker to take advantage of this authority. 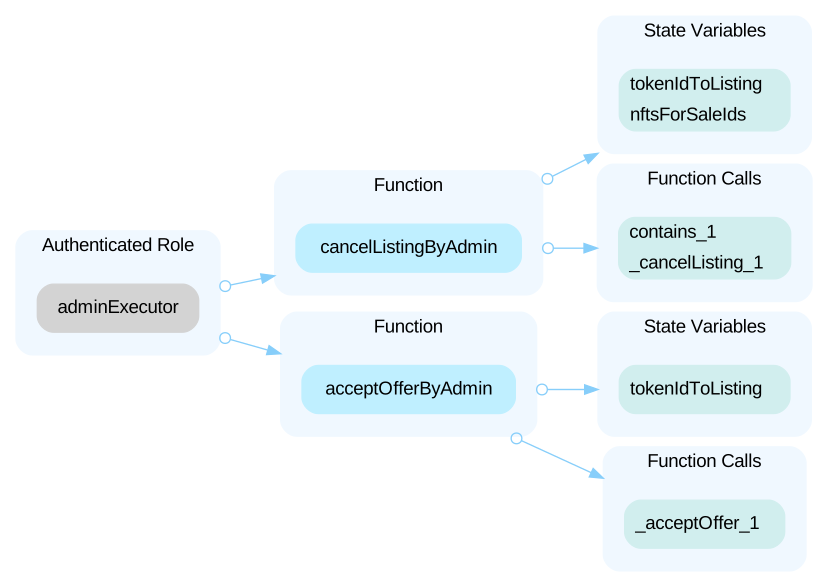
HighCentralization Risk in ToppyMasterSetting.solOpen
In the contract `ToppyMaster` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 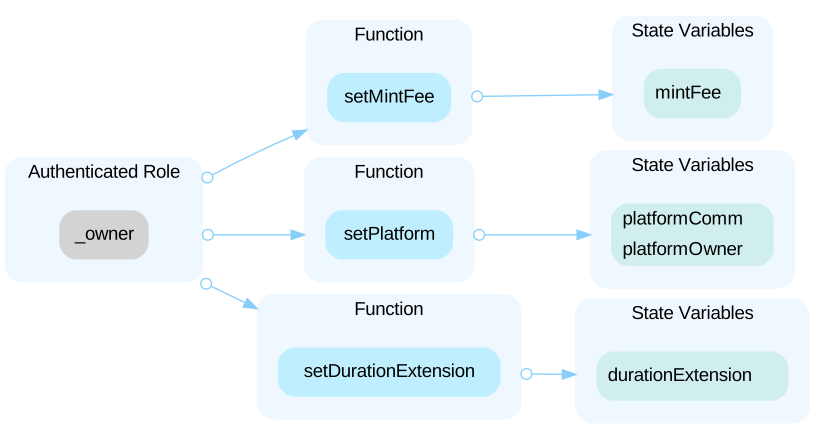
HighCentralization Risk in ToppyStaking.solOpen
In the contract `ToppyStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 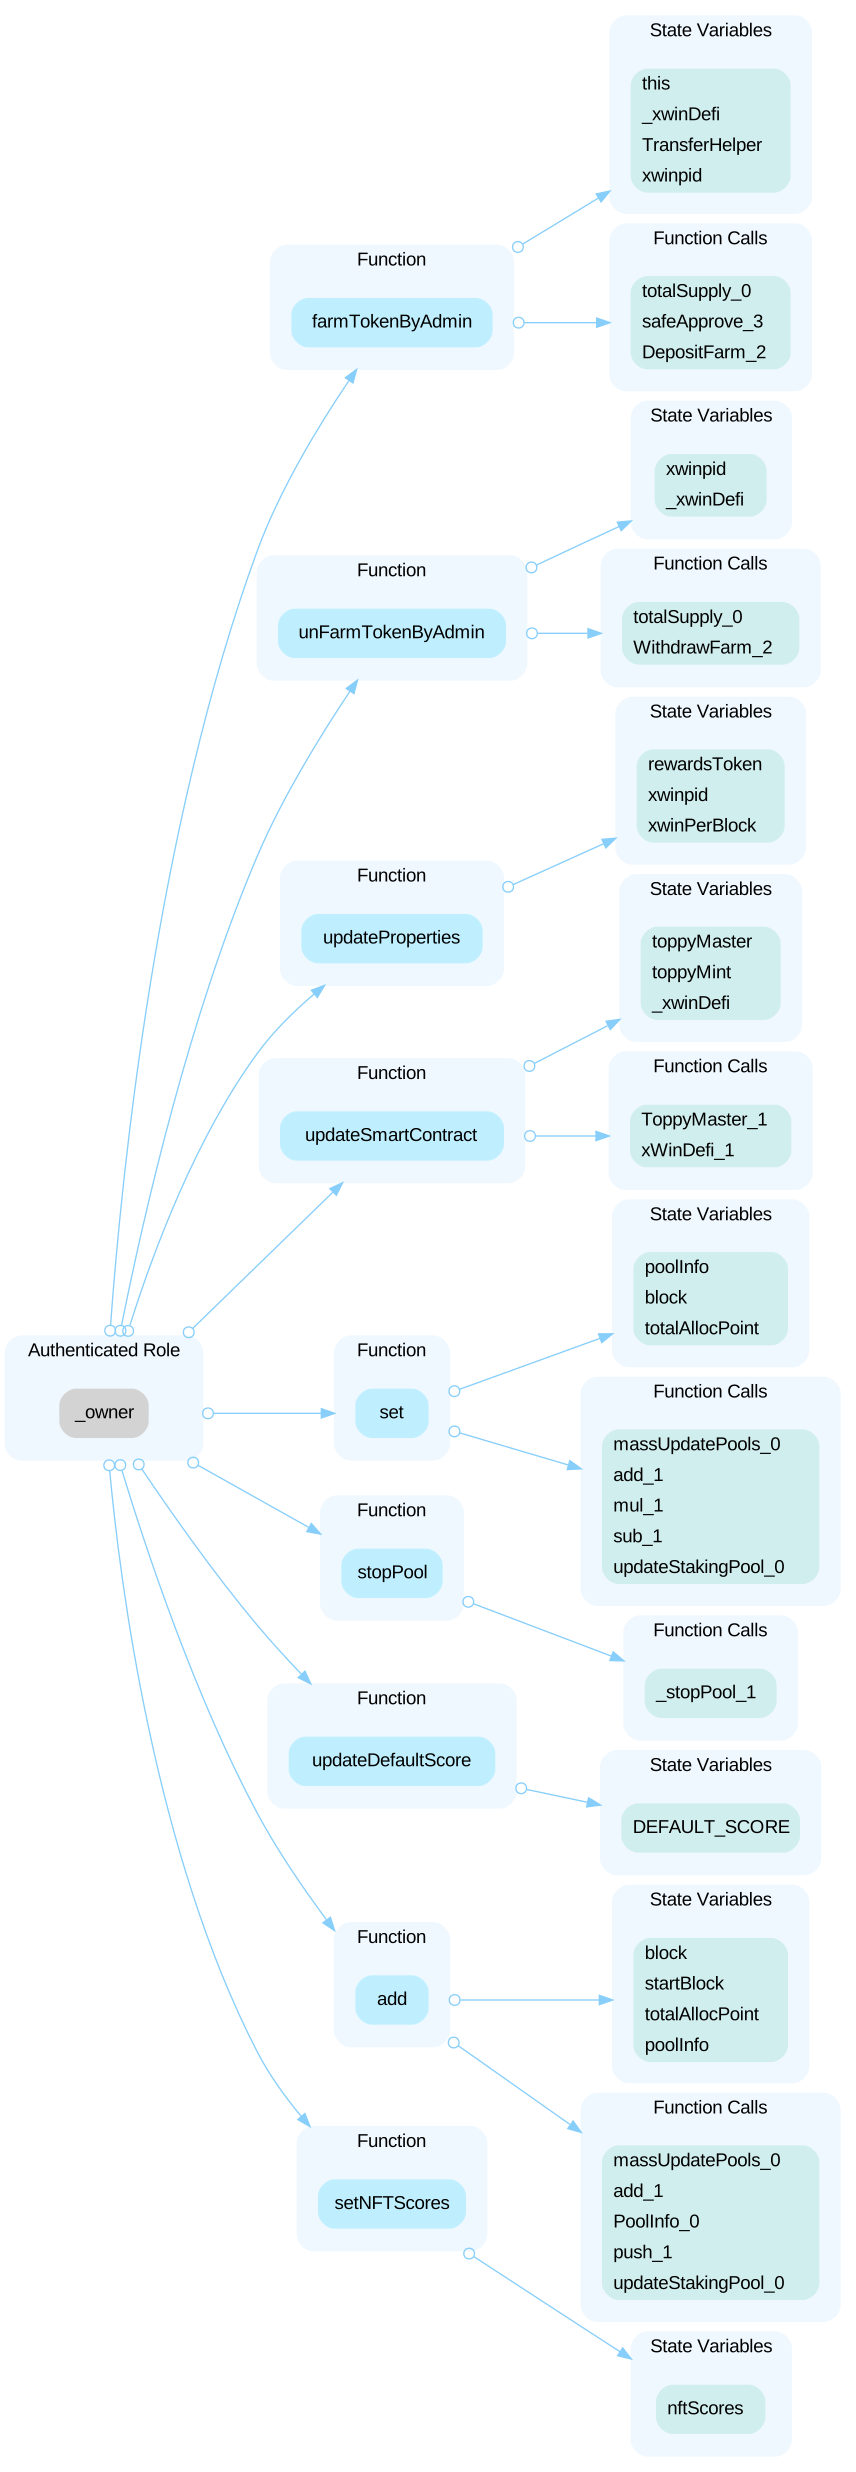
HighCentralization Risk in ToppyStandardNFT.solOpen
In the contract `ToppyStandardNFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 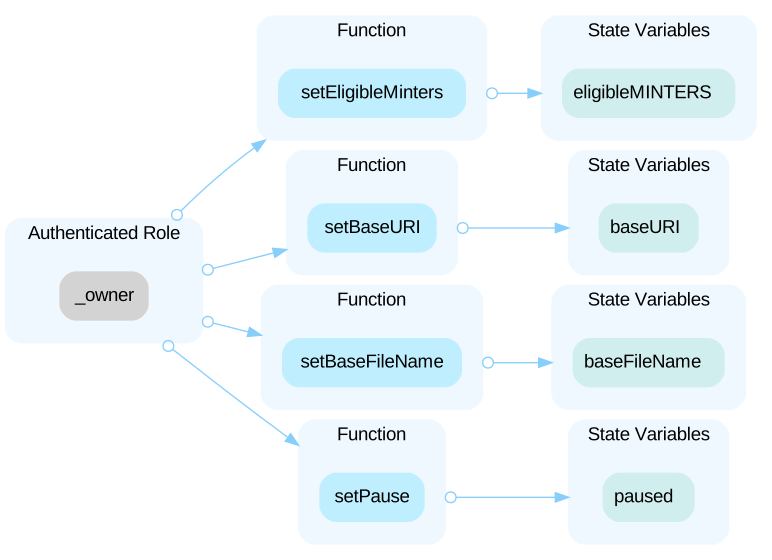
HighCentralization Risk in ToppySupportPayment.solOpen
In the contract `ToppySupportPayment` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 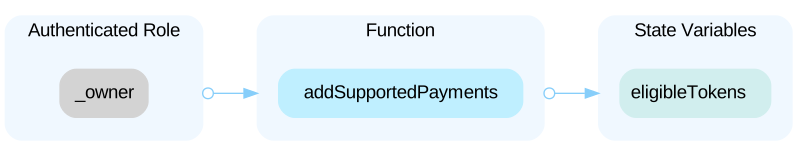
MediumCheck Effect Interaction Pattern ViolatedOpen
The order of external call and storage manipulation must follow the check-effect-interaction pattern.
MediumNo New Tokens MintedOpen
Only one token is minted in the contstructor, no new tokens minted in the contract. The function `farmTokenByAdmin` can only deposit one token to `_xwinDefi`. `totalSupply` is used in `farmTokenByAdmin` and `unFarmTokenByAdmin` functions is always `1*10**18`.
LowLack of Input ValidationOpen
The owner can call `setDurationExtension` to update `durationExtension`, the input parameter `_durationExtension` can be any value including zero. If `durationExtension` is zero, it may affect the process of `English Auction`. The fix commit added the upper limit, lower limit is also needed. ```=js require(_durationExtension <= 86400, "max duration extension 24hours"); ```
LowNo Need to Use Library `SafeMath`Open
Solidity v0.8.0 and later versions check underflow/overflow by default, and therefore the library `SafeMath` is not necessary. Source: [link](https://docs.soliditylang.org/en/v0.8.7/080-breaking-changes.html)
Show 1 more
LowWhy `onlyAdminExecutor` Can Call `cancelListingByOpen
Why admin executor can cancel user's `listing_`?
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (13)
- contracts/ERC721.sol
- contracts/ToppySupportPayment.sol
- contracts/ToppyMysteriousNFT.sol
- contracts/IToppyMint.sol
- contracts/ToppyStaking.sol
- contracts/ToppyMint.sol
- contracts/ToppyMarketplace.sol
- contracts/IBEP20.sol
- contracts/ToppyStandardNFT.sol
- contracts/tests/ToppyMarketPlace_test.sol
- contracts/TransferHelper.sol
- contracts/ToppyMasterSetting.sol
- contracts/BEP20.sol
Part of xWIN Finance’s security record
 xWIN Finance
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us