Wemix Retainer 119 DIOSV3 (2)
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 119 DIOSV3 (2)) on 8 Jul 2024: 5 findings, 0 critical; 2 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 2 |
HighCentralization Related RisksOpen
In the contract `UIOS` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the `BaseTick` price which is the target price for sync operations. 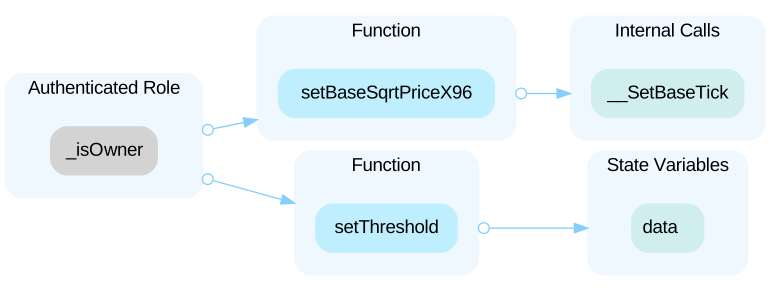 In the contract `UIOS` the role `_operator` has authority over the functions shown in the diagram below. Any compromise to the `_operator` account may allow the hacker to take advantage of this authority and trigger the `WEMIX$` price stabilizing functions `syncToBaseTick`. 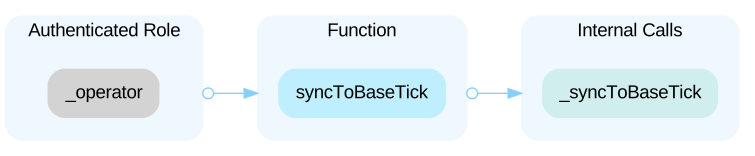 In the contract `OperatorManagement` the role `operatorManager` has authority over the functions shown in the diagram below. Any compromise to the `operatorManager` account may allow the hacker to take advantage of this authority and add/remove the operator role. 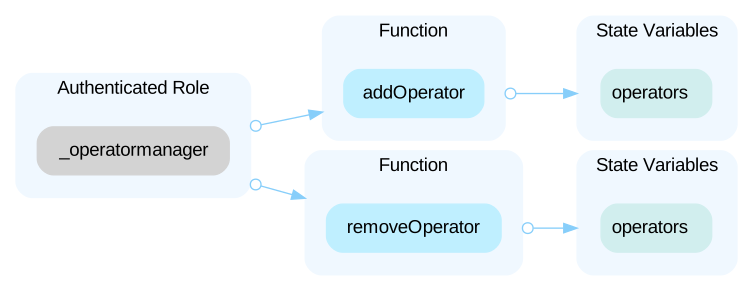 In the contract `UIOSAuthorizedMint` the role `_breaker` has authority over the functions shown in the diagram below. Any compromise to the `_breaker` account may allow the hacker to take advantage of this authority and pause/resume the contract. 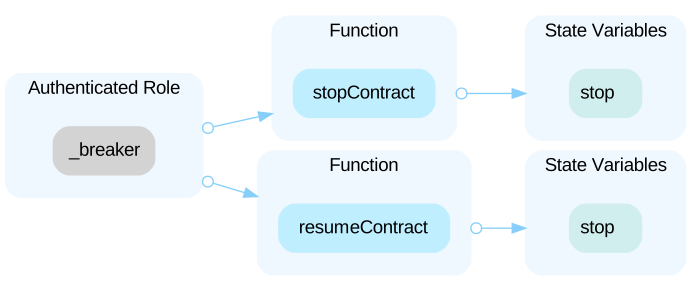 In the contract `UIOSAuthorizedMint` the role `_breakersetter` has authority over the functions shown in the diagram below. Any compromise to the `_breakersetter` account may allow the hacker to take advantage of this authority and set breaker role and breakersetter role. 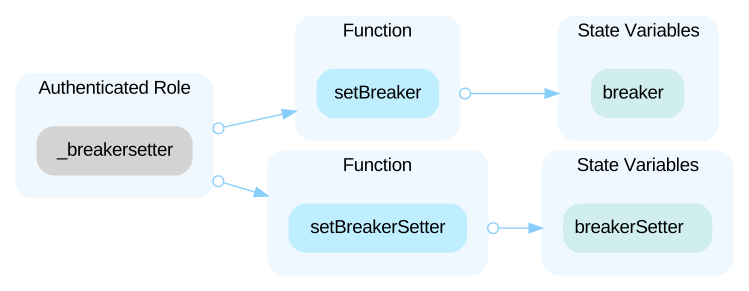 In the contract `UIOSAuthorizedMint` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set whitelisted accounts and modify the USDC treasury address. 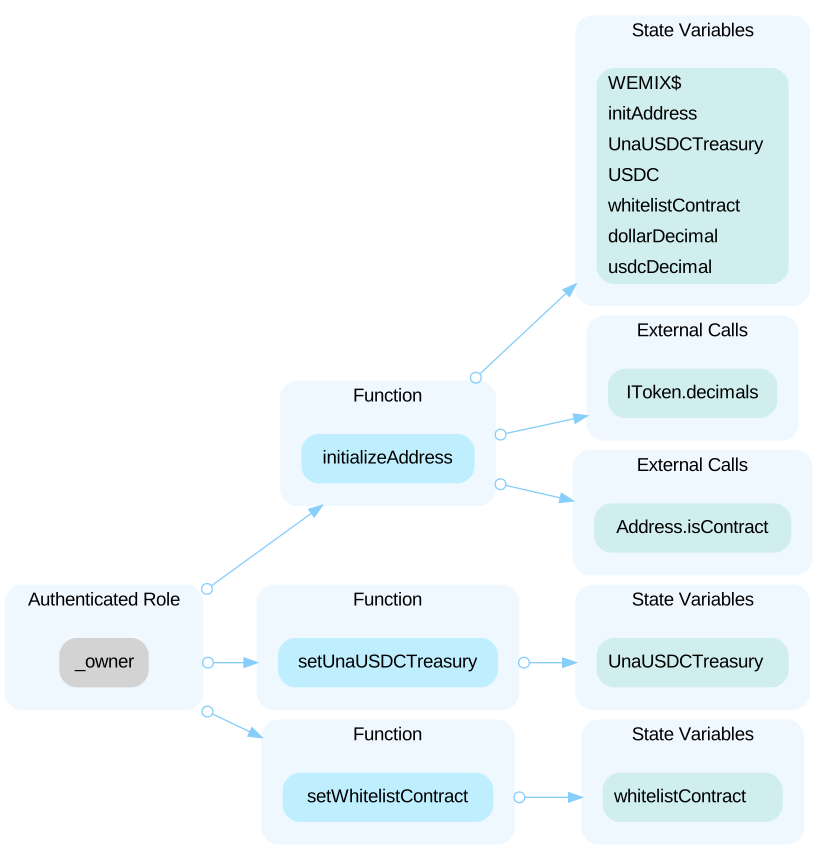 In the contract `UIOSDollarTreasury` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and submit/confirm malicious transaction proposals. 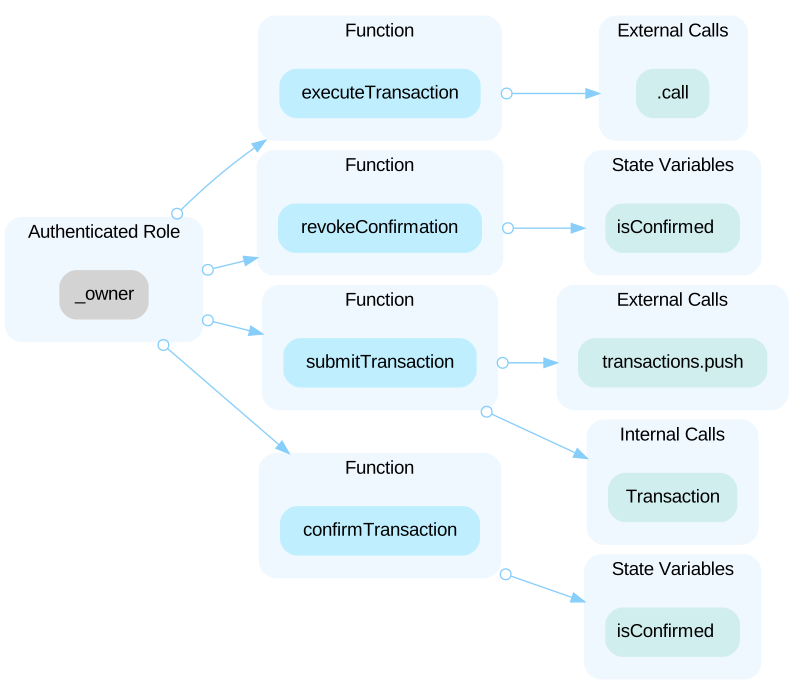
HighCentralized Control of Contract UpgradeOpen
`OperatorManagement` and `UIOS` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the proxy admin account, he can change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
LowRisks Associated with Unknown Implementations inOpen
When the `executeTransaction()` function is called, it executes code contained within `transaction.data`, which is not known or specified within the audit's scope. ```solidity=108 (bool success, ) = transaction.to.call{value: transaction.value}(transaction.data); ``` While the transaction requires confirmation by multiple signatories, there remains a vulnerability if one or more owners inadvertently approve a malicious transaction. Such transactions could potentially lead to the unauthorized transfer of assets or other harmful actions within the contract. This audit treats external implementations referred to in `transaction.data` as black boxes and assumes their functional correctness. Given the inherent risks of executing unknown code, it is crucial for the development team to monitor these transaction contents continuously.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (4)
- extentions/OperatorManagement.sol
- UIOS.sol
- UIOSDollarTreasury.sol
- UIOSAuthorizedMint.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us