Meta Ruffy - Audit 3
CertiK reviewed metaruffy.io (Meta Ruffy - Audit 3) on 28 Sep 2022: 10 findings, 0 critical; 1 marked fixed, 9 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 7 | 0 | 1 |
HighCentralization Risks in METARUFFY.solOpen
In the contract `METARUFFY` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of the following: - Set new receivers to get ether from swaps if passed the threshold. - Update the divider between the marketing and developer wallet. - Change the burn, developer, and marketing fee. - This would allow the malicious user to set the burn fee to zero and maximize token gain for themselves. - Change the threshold for swaps to maximize ether gained into their wallets. - Enable the antiSnipe bot for transactions. --- 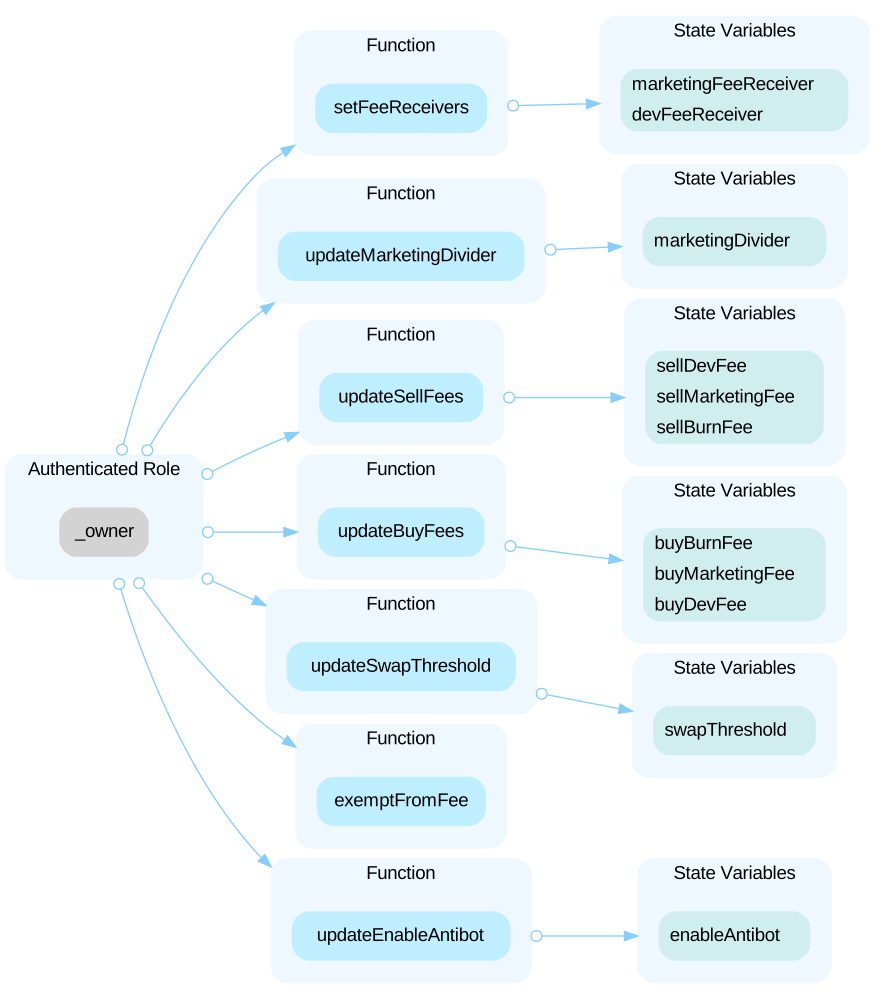 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this and transfer or renounce ownership. 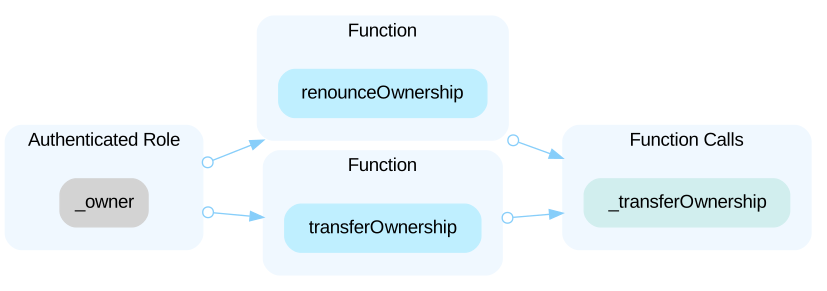
HighInitial Token DistributionOpen
When deploying `MetaRuffy`, all the tokens are sent to the contract deployer. This could be a centralization risk as the team can distribute tokens without obtaining the consensus of the community.
LowPotential Blending of EtherOpen
If a user sends ether to the smart contract, then it has to wait until a transfer function calls `swapAndSendEth()` to have the funds sent to the marketing and dev wallet.
LowState Variable Should Be Declared ConstantOpen
State variables that never change should be declared as `constant` to save gas. ```solidity=566 uint256 _totalSupply = 300 * 10 ** 9 * (10**_decimals); ``` - `_totalSupply` should be declared `constant`.
LowThird Party DependencyOpen
The contract is serving as the underlying entity to interact with one or more third party AMM and PinkAntiBot protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=580 IPinkAntiBot public pinkAntibot; ``` - The contract `METARUFFY` interacts with third party contract with `IPinkAntiBot` interface via `pinkAntibot`. The `pinkAntibot` directly influences how the `transfer()` function works and can lead to unintended consequences if an error occurs.
LowToo Many DigitsOpen
Literals with many digits are difficult to read and review. ```solidity=563 address constant public DEAD = 0x000000000000000000000000000000000000dEaD; ```
LowTypoOpen
The event and emit for "UpdateMarketingDevider" is spelled incorrectly.
LowUnclear Error MessageOpen
The following error message(s) could be interpreted as unclear: ```Solidity=727 require(_marketingFee.add(_devFee).add(_burnFee) <= 10, "METARUFFY: Max fee limit exceeds"); ``` --- ```Solidity=787 require(_marketingFeeReceiver != address(0), "METARUFFY: zero address passed"); require(_devFeeReceiver != address(0), "METARUFFY: zero address passed"); ``` --- ```Solidity=824 require(_newPercent >= 25, "Marketing divider is low."); ```
LowUnnecessary Use of SafeMathOpen
The `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0xa4cb3ef5f41a4d89d6fced22ea8a1c57957629aa | Chain: Ethereum | Source code: Verified source |
Part of metaruffy.io’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us