Affyn Land
CertiK reviewed Affyn (Affyn Land) on 7 Oct 2022: 17 findings, 0 critical; 11 marked fixed, 1 acknowledged, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings17
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 5 | 0 | 11 |
HighCentralization RisksAcknowledged
In the contract `AccessPass` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and perform the following operations: - grant an higher privileges access pass to address he owns or controls. - change the maximum number of access passes available for a certain access type. - close and open access pass sales or change sale's durations. - change the FYN price of access passes. - overwrite the timelock release time. 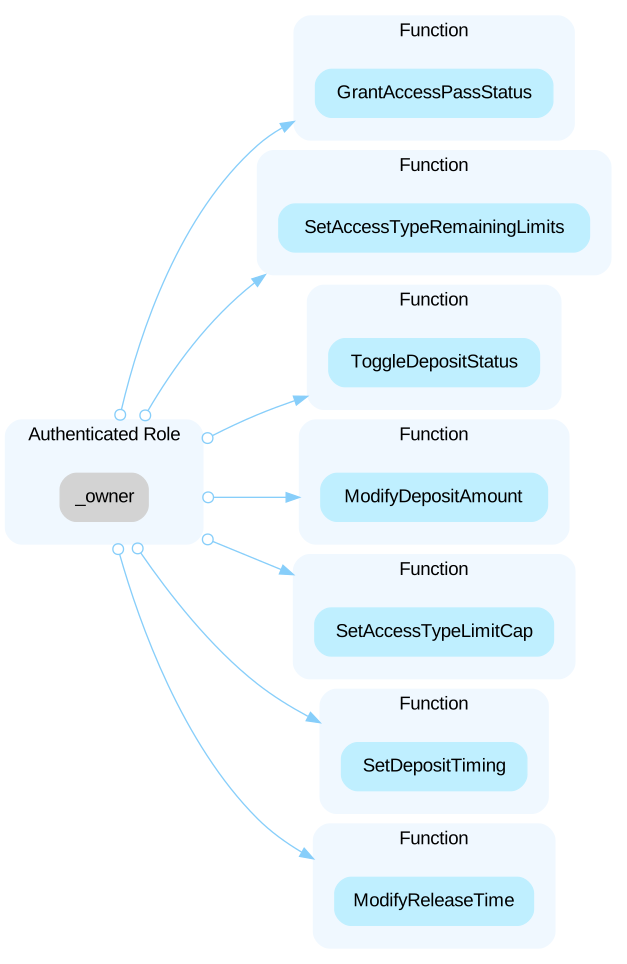 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership to a malicious contract he owns. 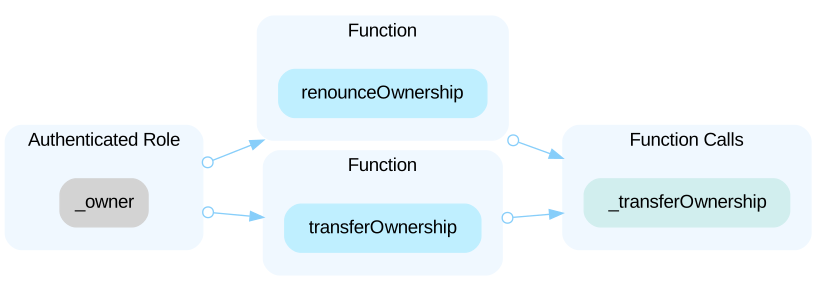 In the contract `TokenTimelock` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and change the release time of the contract. 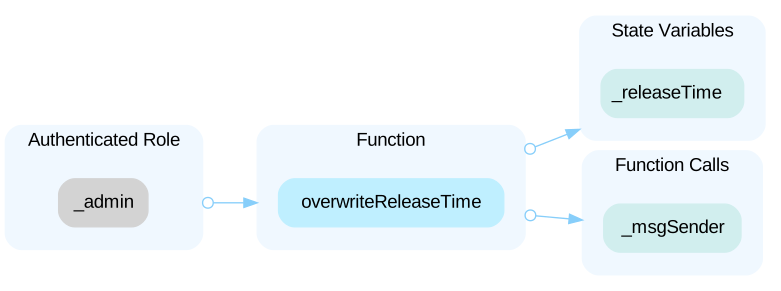 --- In the contract `LandSale` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and perform different operations, for example: change flag burning time and price, mint all the private lands he wants to address he owns or controls, create new city sales, open or close flag and city sales, change the `whitelistedMerkleRoot` etc... 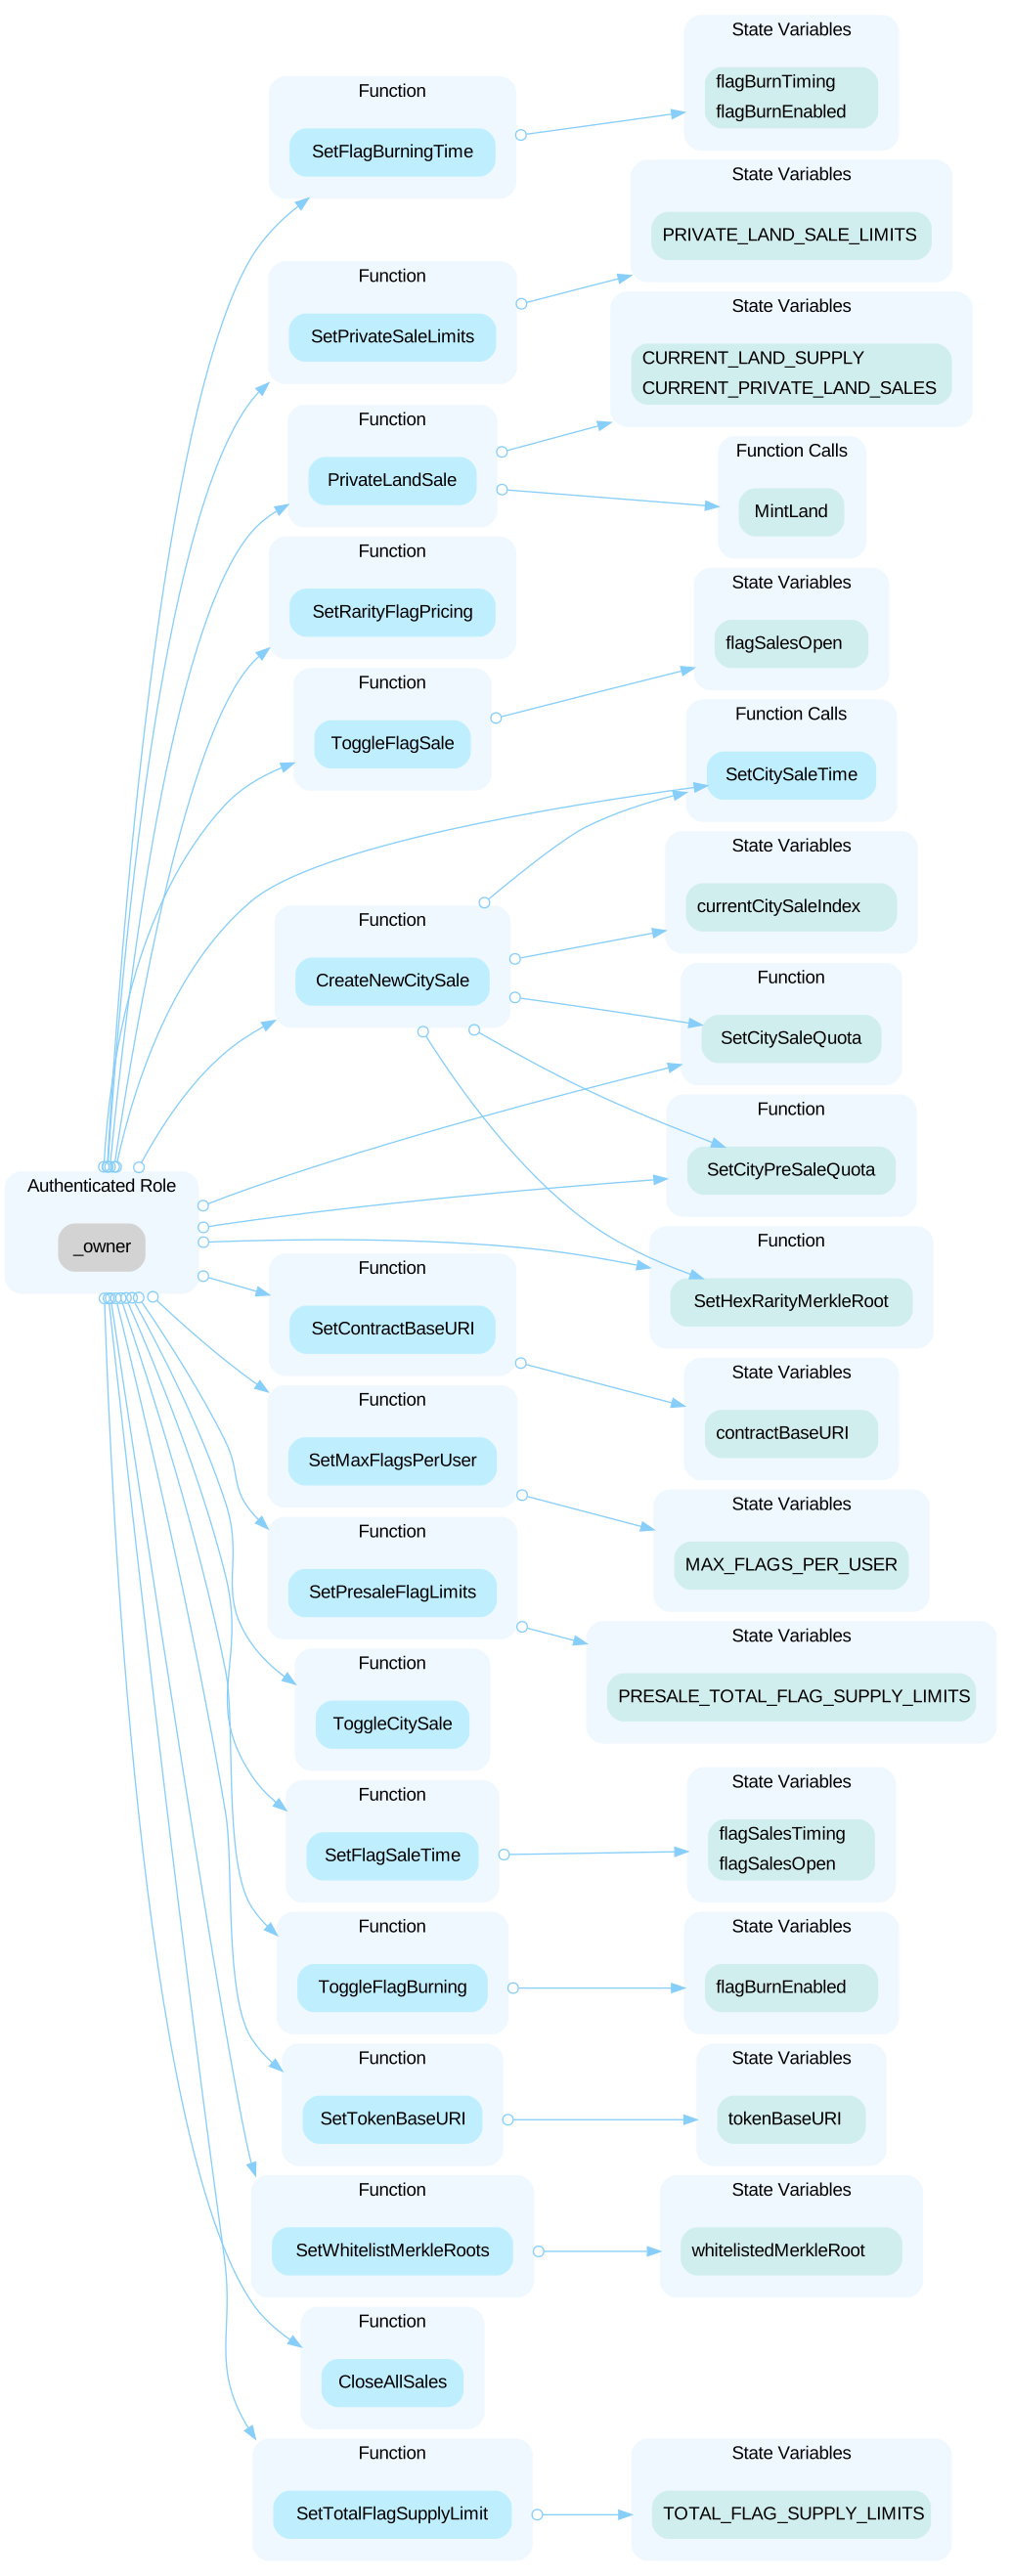 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership to a malicious contract he owns. 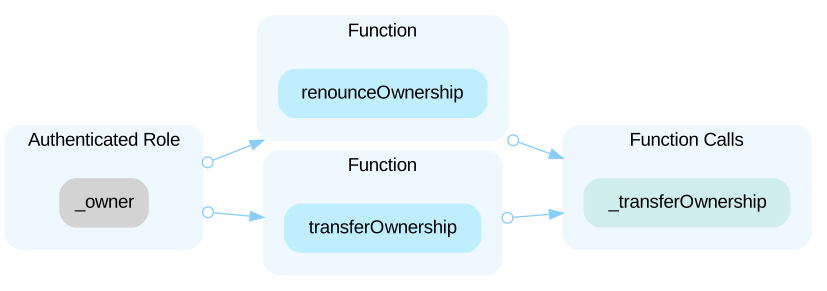
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- LandAndFlagContract.sol
- AccessPassContract.sol
Part of Affyn’s security record
 Affyn
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us