Wemix Retainer 142 - PNIX DEX V2
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 142 - PNIX DEX V2) on 15 Nov 2024: 2 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings2
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 0 |
HighCentralization Related RisksOpen
In the contract `Factory`, the role `GOVERNOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `GOVERNOR_ROLE` account may allow the hacker to take advantage of this authority and set the quote unit for a pair, unpause the specified trading pair, set the base unit, and pause the specified pair. 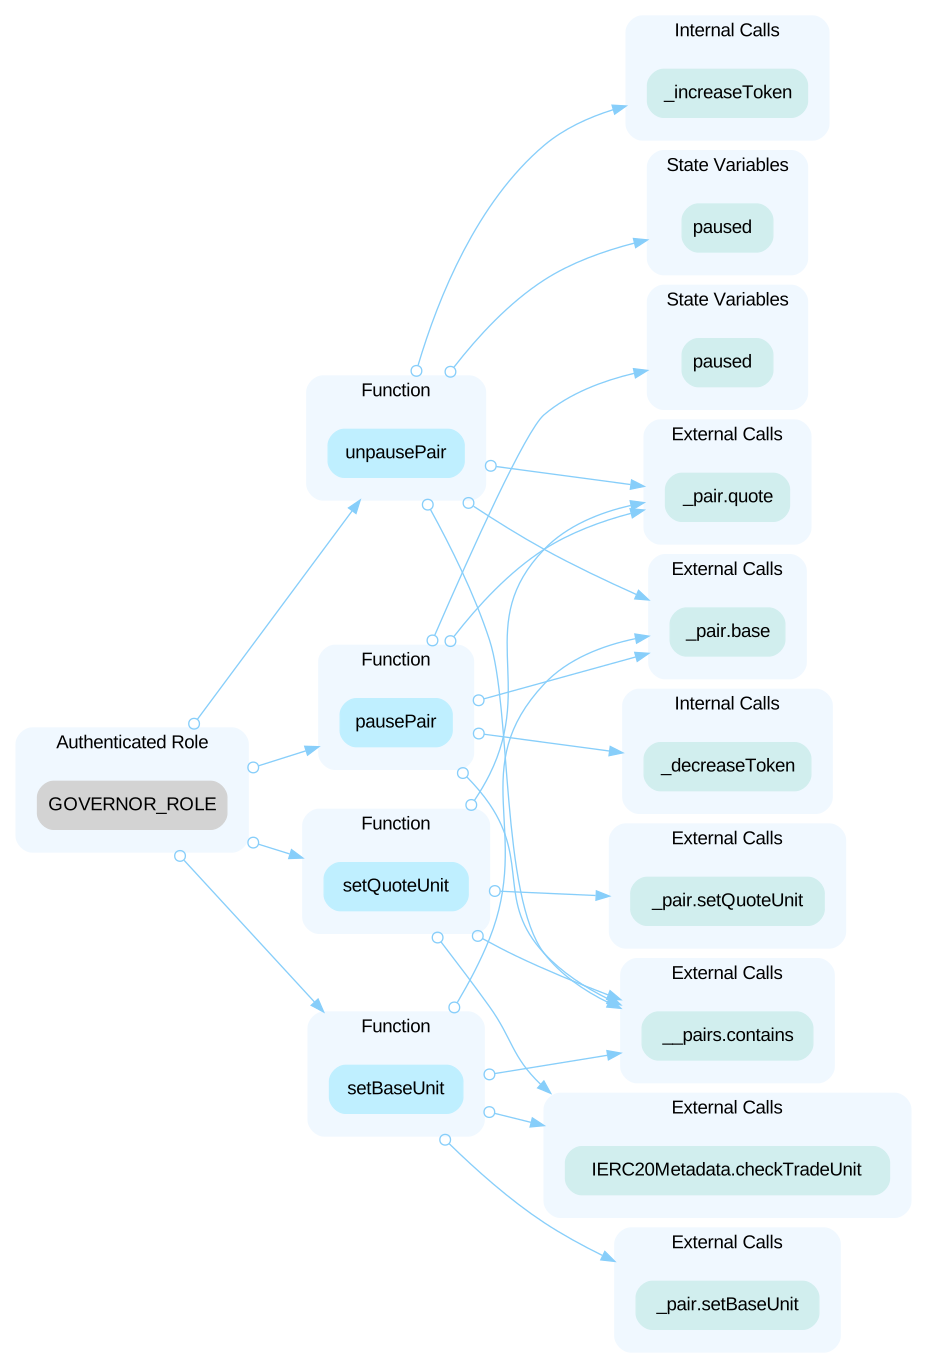 In the contract `Factory`, the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and create a new trading pair. 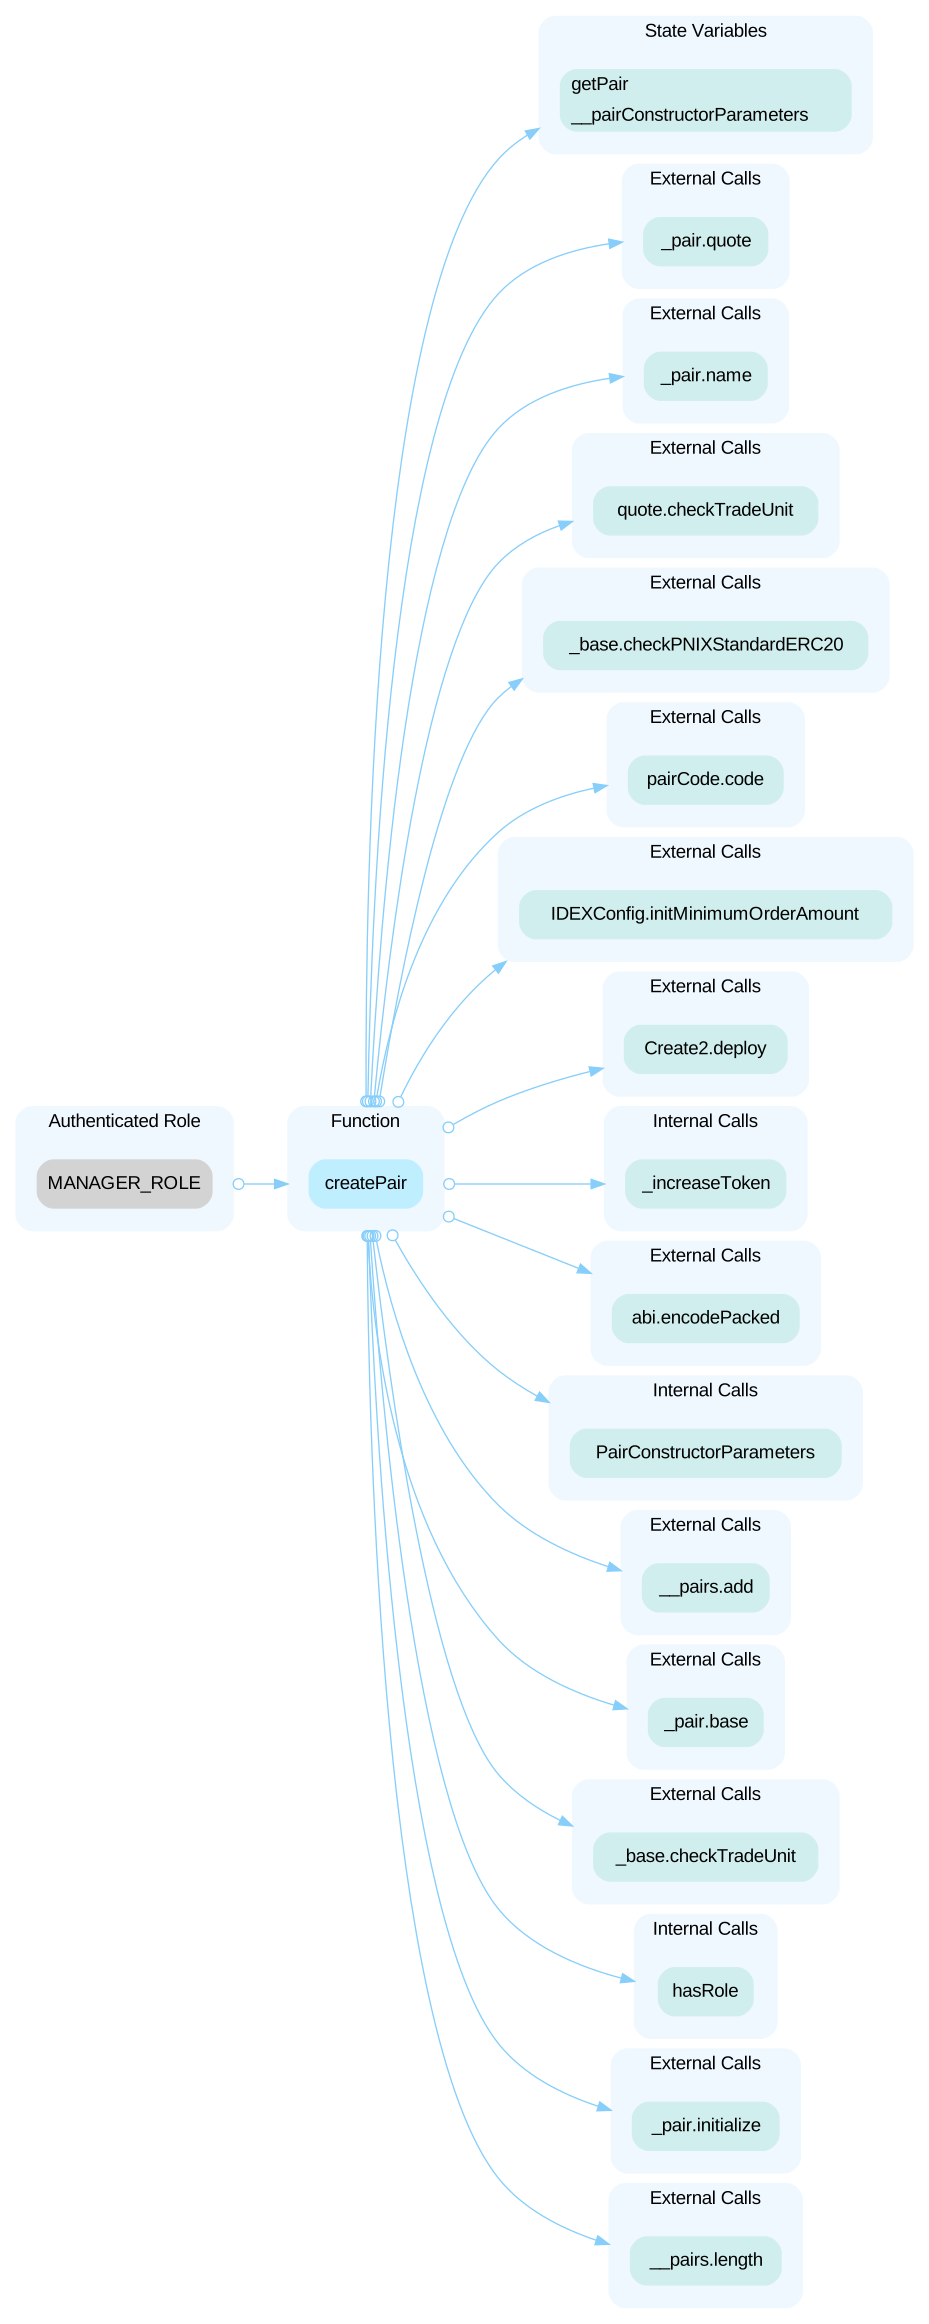 In the contract `Factory`, the role `MASTER_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set or remove router for a component, set a component address, and set the quote token. 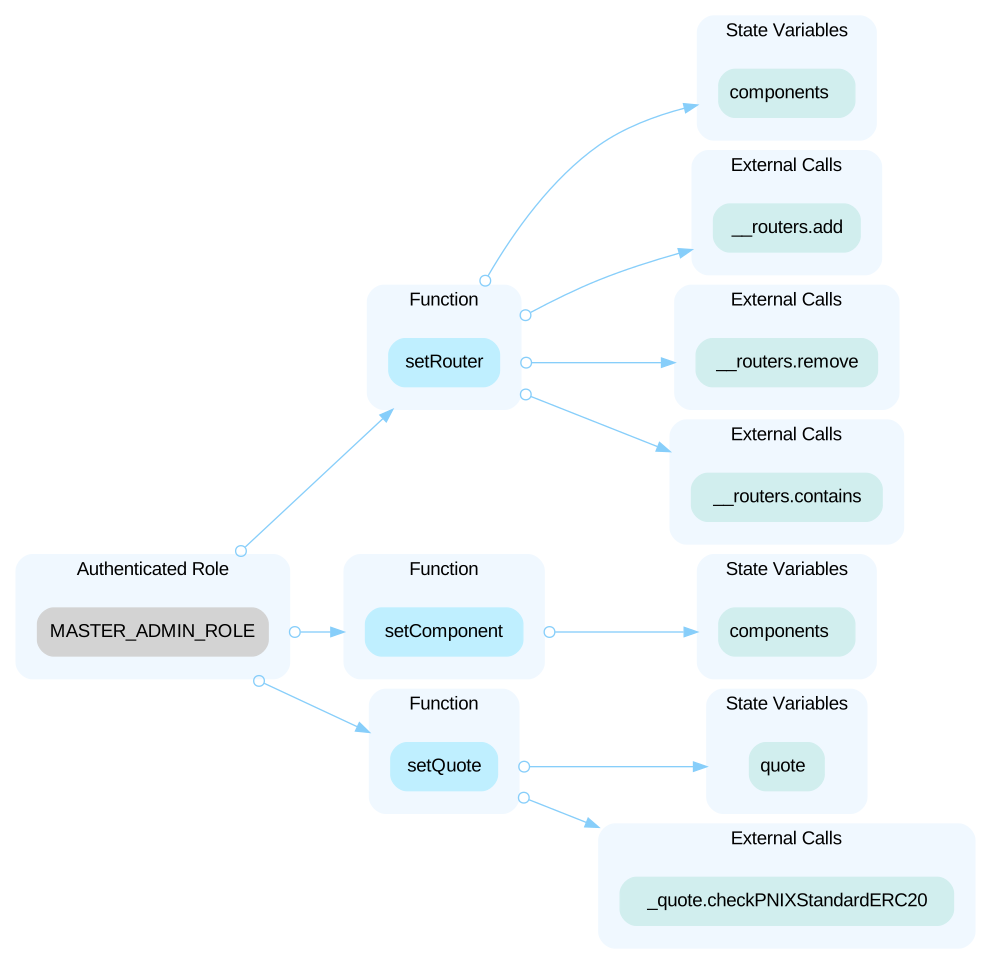 In the contract `Factory`, the role `PAIR_CREATOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAIR_CREATOR_ROLE` account may allow the hacker to take advantage of this authority and create a trading pair with specified parameters. 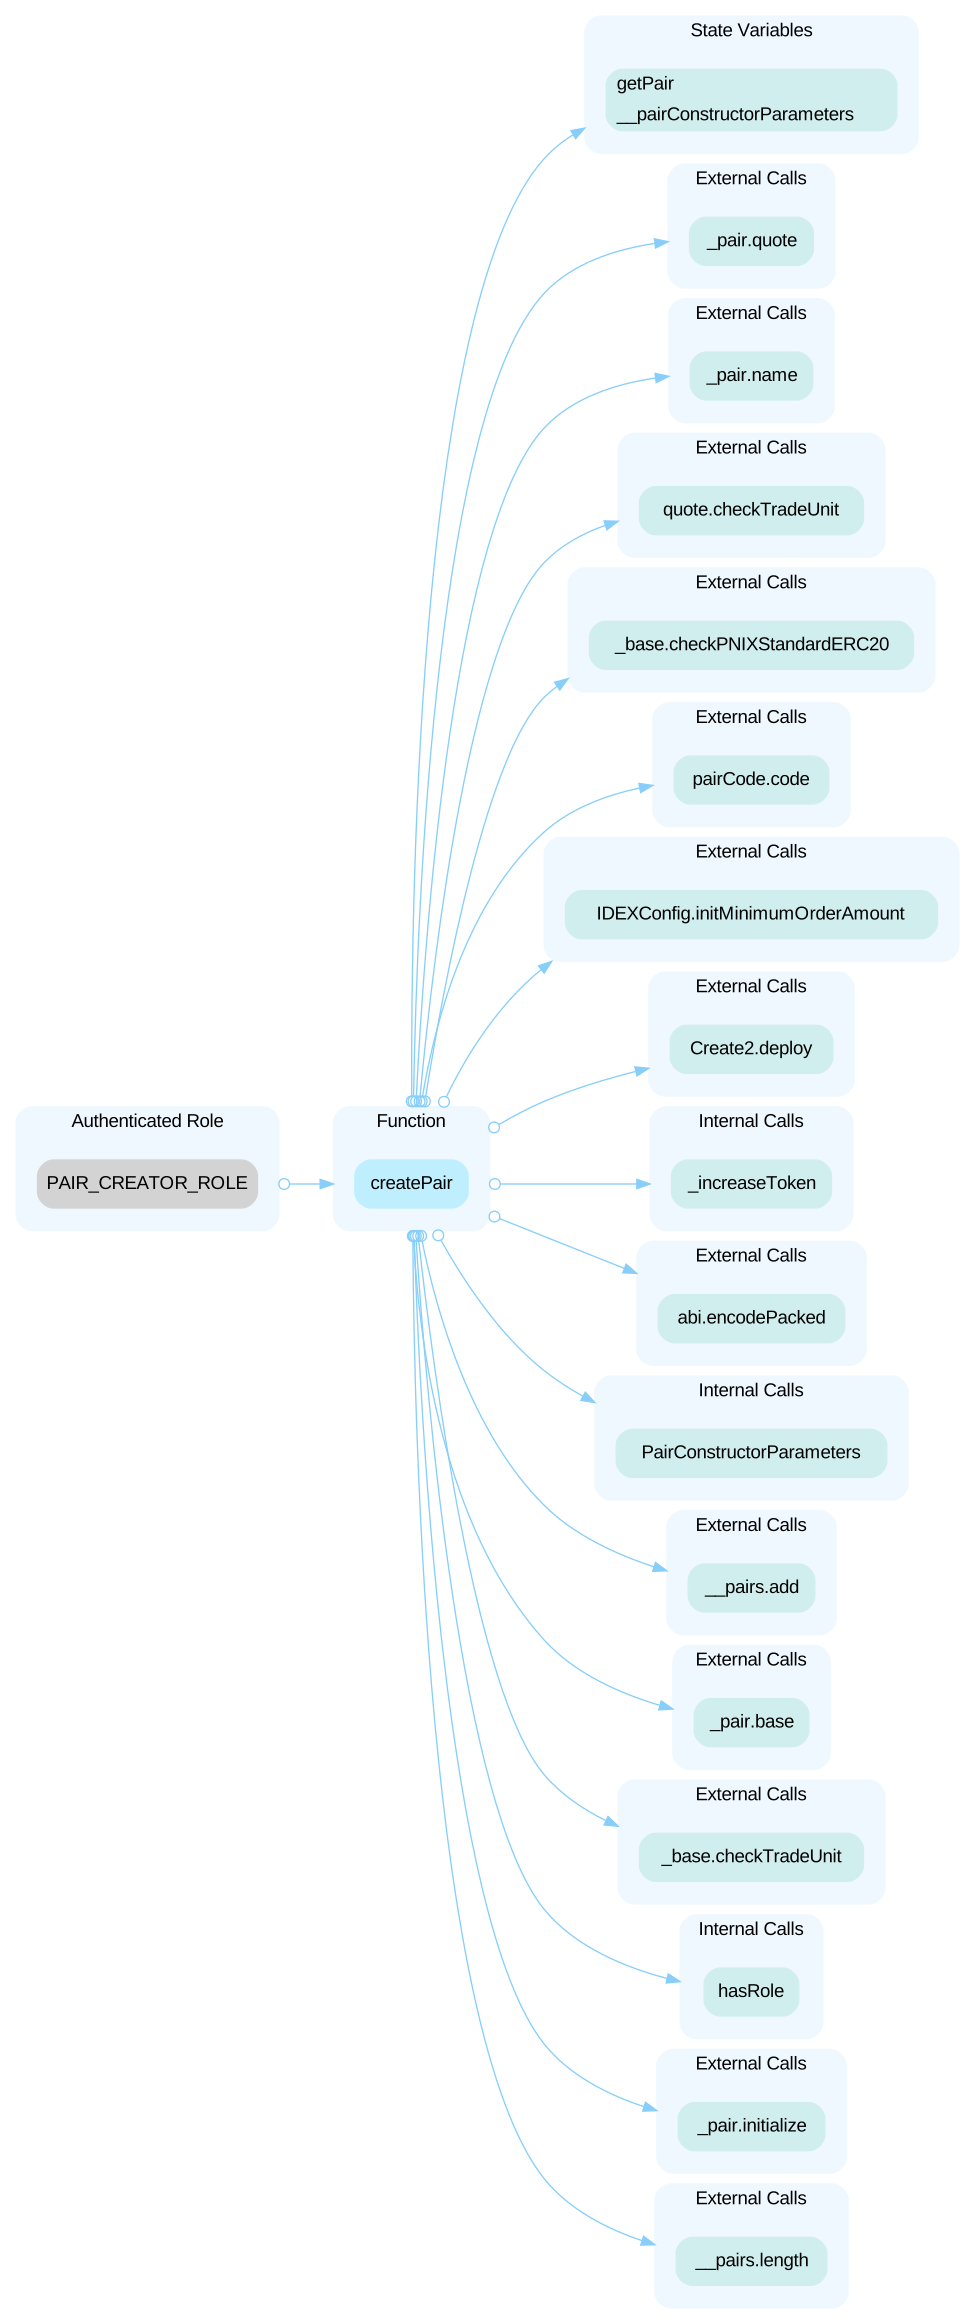 In the contract `Factory`, the role `_role` has authority over the functions shown in the diagram below. Any compromise to the `_role` account may allow the hacker to take advantage of this authority and set role administrator. 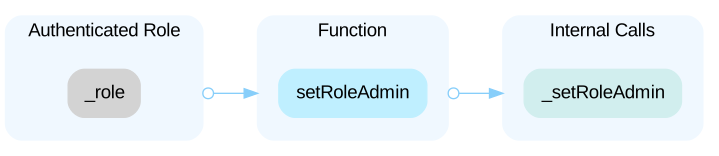 ----- In the contract `Router`, the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and skim excess tokens from a liquidity pool. 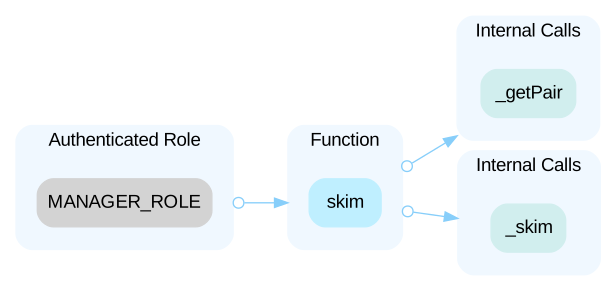 In the contract `Router`, the role `MASTER_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and authorize a contract upgrade. 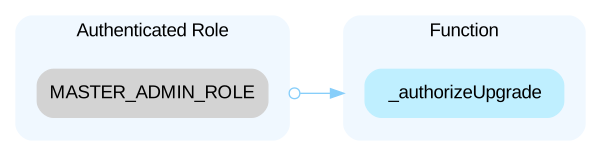
HighCentralized Control of Contract UpgradeOpen
In the contract `Router`, the role `MASTER_ADMIN_ROLE` has the authority to update the implementation contract behind these contracts. Any compromise to the `MASTER_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- contracts/Router.sol
- contracts/Pair.sol
- contracts/Factory.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us