AMIS Platform
CertiK reviewed Amis (AMIS Platform) on 2 Dec 2022: 6 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 4 | 0 | 0 |
HighCentralization Related RisksOpen
In the contract `AmisToken` the role `onlyOwner` has authority over the functions shown in the diagram below. Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this authority and pause/unpause the contract or pause/unpause an address from transferring tokens. The hacker can still transfer tokens while the contract is paused. 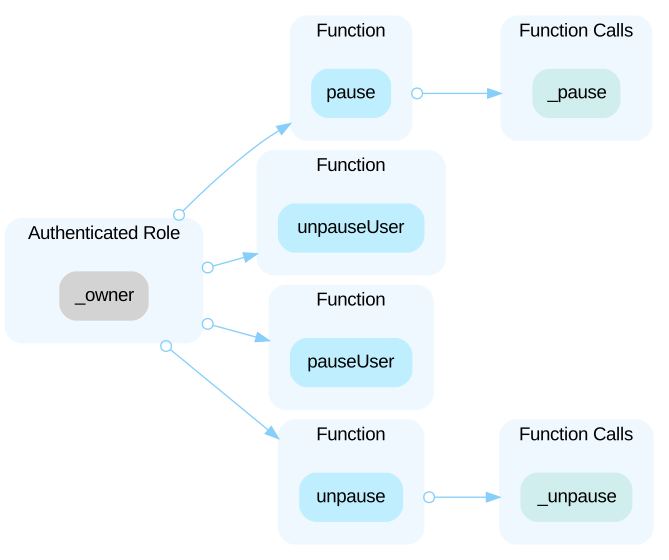 In the contract `Ownable` the role `onlyOwner` has authority over the functions shown in the diagram below. Any compromise to the `onlyOwner` account may allow the hacker to take advantage of this authority and renounce the ownership or transfer the ownership to a malicious address he owns or controls. 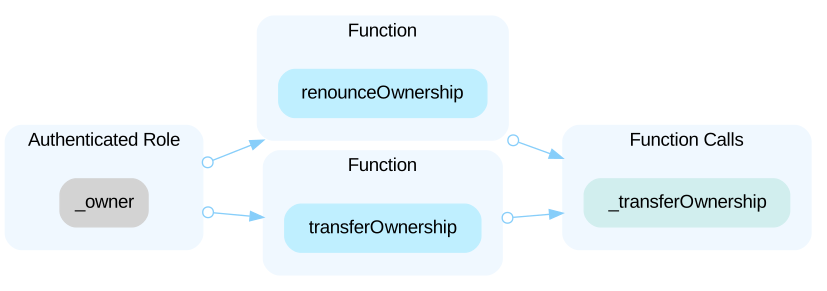
HighInitial Token DistributionOpen
All **AMIS** tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute **AMIS** tokens without the consensus of the community.
LowFunction Should Be Declared ExternalOpen
The functions which are never called internally within the contract should have external visibility for gas optimization.
LowMultiple Solidity VersionsOpen
In the codebase, there are multiple `pragma` declarations on the aforementioned lines. --- Furthermore the solidity version used is unlocked. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to an ambiguity when debugging as compiler specific bugs may occur in the codebase that would be difficult to identify over a span of multiple compiler versions rather than a specific one.
LowToo Many DigitsOpen
Literals with many digits are difficult to read and review. Long digits are also more error prone than using scientific notation. ```solidity=738 _mint(msg.sender, 1000000000 * 10 ** 18); ```
LowUnnecessary `_decimals` and `decimals()`Open
The private state variable `_decimals` is initialized to the value 18 in the constructor. There is no need to explicitly create it since the default value for decimals in the standard OZ ERC20 implementation is 18 already. --- Furthermore also overriding `decimals()` is unnecessary since the base `ERC20.decimals()` returns 18.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x3e5a06a60dcb2817d321be08bdbef4a52154ecbf | Chain: Ethereum | Source code: Verified source |
Part of Amis’s security record
 Amis
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us