Wemix Retainer 60 Reflect project
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 60 Reflect project) on 13 Oct 2023: 15 findings, 0 critical; 13 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings15
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 3 |
| Medium | 0 | 0 | 7 |
| Low | 1 | 0 | 3 |
HighCentralization Related RisksOpen
In the contract `REFLECT` the role `_minter` has authority over the functions shown in the diagram below. Any compromise to the `_minter` account may allow the hacker to take advantage of this authority and mint tokens at will. 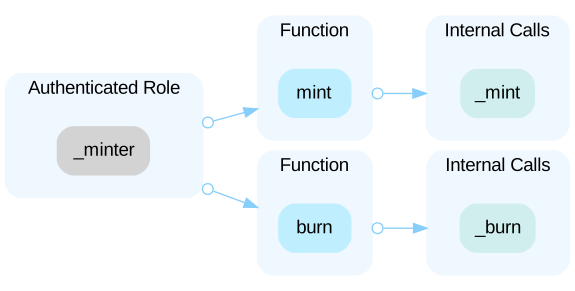 In the contract `REFLECT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and make the contract malfunction by changing blacklist. 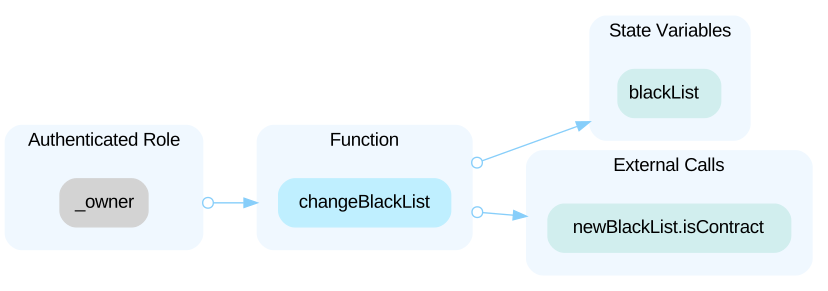 ----- In the contract `ReflectExchanger` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and make the contract malfunction and steal tokens from the contract. 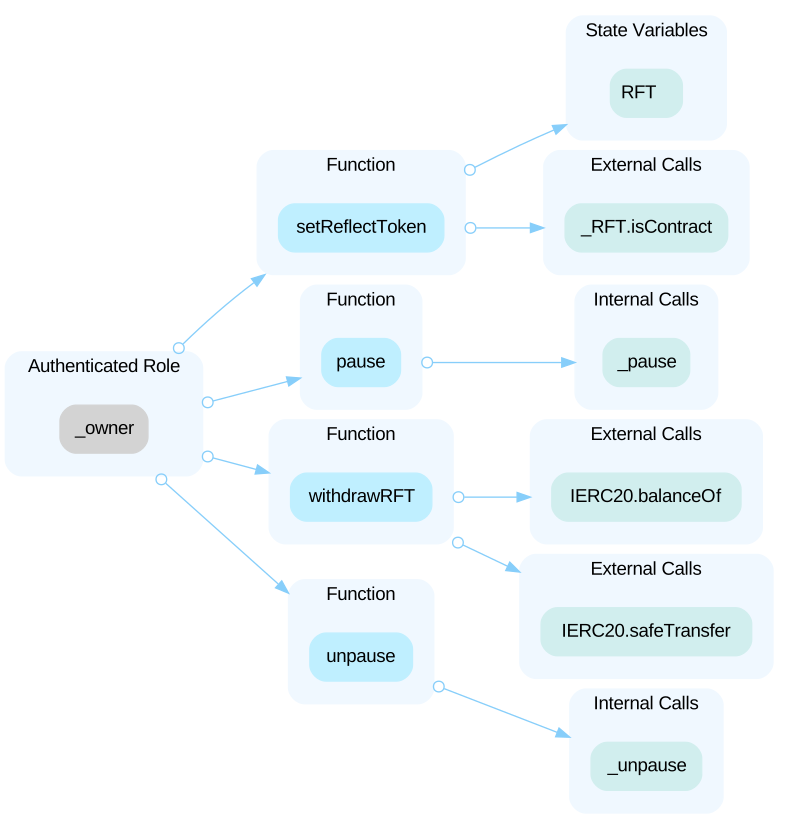 ----- In the contract `ReflectRouter` the role `_editor` has authority over the functions shown in the diagram below. Any compromise to the `_editor` account may allow the hacker to take advantage of this authority and pause/unpause many functions. 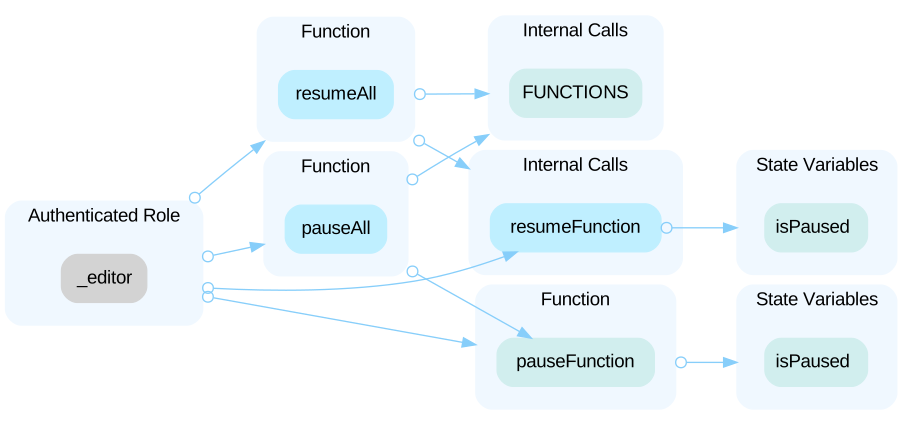 In the contract `ReflectRouter` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change vault contract to potentially steal tokens. 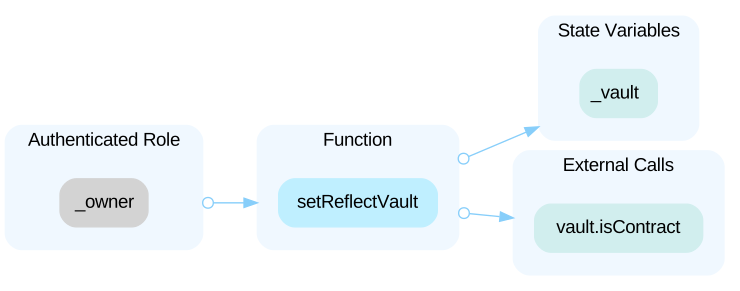 ----- In the contract `ReflectRouterV2`, the role `_owner` has authority over the following functions: - function pause() - function unpause() - function setOperator() - function setExchanger() Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and make the contract malfunction and change important privileged roles operator/exchanger. ----- In the contract ReflectVaultV3, the role `Editor` has authority over the following functions: - setFusedAmount() - setSwapRouter() - setMainnetReflectVault() - setBridge() - addTokens() - subTokens() - activateTokens() - withdrawTokens() - addToken() - subToken() - activateToken() - withdrawToken() Any compromise to the `Editor` account may allow a hacker to take advantage of this authority and make the contract malfunction, steal tokens from the contract. In the contract ReflectVaultV3, the role `Validator` has authority over the following functions: - fusion() - restoreFusion() - fission() Any compromise to the `Validator` account may allow a hacker to take advantage of this authority and make the contract malfunction, steal tokens from the contract. ----- In the contract `ReflectVault`, the role `Editor` has authority over the following functions: - pause() - unpause() - setReflectRouter() - setPlayReflectVault() - setSwapRouter() - setBridge() - setFusedAmount() - addTokens() - subTokens() - activateTokens() - withdrawRemovedAllToken() - addToken() - subToken() - activateToken() - withdrawRemovedToken() Any compromise to the `Editor` account may allow a hacker to take advantage of this authority and make the contract malfunction, steal tokens from the contract. In the contract `ReflectVault`, the role `owner` has authority over the following functions: - withdraw() Any compromise to the `owner` account may allow a hacker to take advantage of this authority and steal tokens from the contract.
LowLack of Safety Check in `setFusedAmount()` FunctiOpen
The `setFusedAmount()` function allows the Editor to set `fusedAmount` to any positive number. The `fusedAmount` variable is supposed to track the users' total fusion minus total fission amount, as the `finalFusion()` function increments this variable and the `finalFission()` function decrements this variable. If the `fusedAmount` is set to be too low, then any legitimate fission transaction would revert, as line 486 would revert if/when there's underflow.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (6)
- contracts/REFLECT.sol
- contracts/ReflectExchanger.sol
- contracts/ReflectVault.sol
- contracts/ReflectRouter.sol
- Reflect/ReflectRouterV2.sol
- Reflect/ReflectVaultV3.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us