Farm Token
CertiK reviewed CryptoFarmers (Farm Token) on 16 Sep 2024: 6 findings, 0 critical; 2 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 2 |
HighCentralization Risks in FARM_Token_v1.solOpen
In the contract `FARM` the role `_owner` has authority over the functions shown in the diagram below. 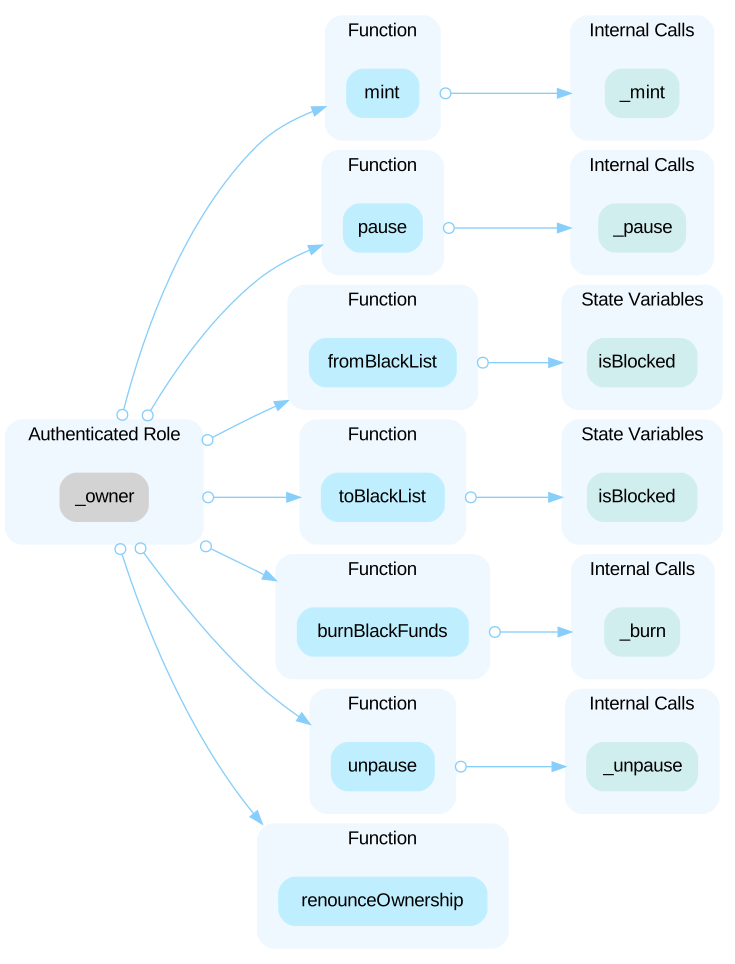 - `mint(address to, uint256 amount)`: Mints new tokens to the specified address. Only the contract owner can call this function. - `toBlackList(address forBlock)`: Adds an address to the blacklist, preventing it from making transfers. Only the contract owner can call this function. - `fromBlackList(address forUnblock)`: Removes an address from the blacklist, allowing it to make transfers. Only the contract owner can call this function. - `burnBlackFunds(address account, uint256 amount)`: Burns a specified amount of tokens from a blacklisted address. Only the contract owner can call this function. - `pause()`: Pauses all token transfers. Only the contract owner can call this function. - `unpause()`: Unpauses all token transfers. Only the contract owner can call this function. - `renounceOwnership()`: Allows the current owner to relinquish control of the contract. Only the contract owner can call this function. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project.
HighCentralized Balance ManipulationOpen
In the contract `FARM`, the role `owner` has the authority to update the token balance of an arbitrary account without sanity restriction. Any compromise to the `owner` account may allow a hacker to take advantage of this authority and manipulate users' balances by calling the `mint()` function and/or `burnBlackFunds()`
HighInitial Token DistributionOpen
All of the `FARM` tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
LowIneffective Implementation of `renounceOwnership`Open
The `renounceOwnership` function in its current form does nothing, effectively disabling the ability to renounce ownership. This can prevent the contract from entering a truly decentralized state, where no single entity has control over it. If the owner wishes to renounce ownership and decentralize control of the contract, the current implementation will not achieve this, leading to a potential centralization risk and lack of trust from users.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- FARM_Token_v1.sol
Part of CryptoFarmers’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us