Wemix Retainer 88 NILE MarketPlace (hybrid)
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 88 NILE MarketPlace (hybrid)) on 13 Feb 2024: 10 findings, 2 critical; 6 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 2 |
| High | 2 | 0 | 2 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 2 |
HighCentralization Related RisksOpen
In the contract `HybridAuctionOrder`, `OHybridAuctionOrder` and `CHybridAuctionOrder` the role `_editor` has authority over the functions shown in the diagram below. Any compromise to the `_editor` account may allow the hacker to take advantage of this authority and reset the price of an order. 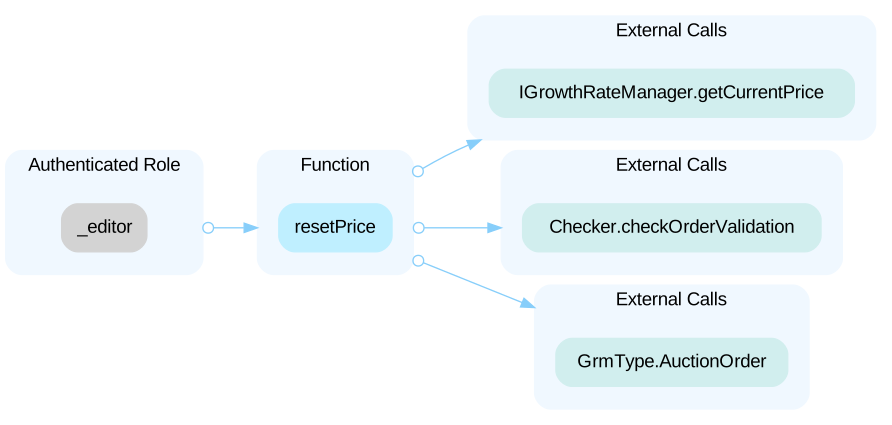 In the contract `ExecuteManager.sol` the role `ADMIN` has authority over the functions shown below. Any compromise to the `ADMIN` account may allow the hacker to take advantage of this authority and modify the configuration of the ExecuteManager. * setRoleManager * changeExecutability * changeExecutabilityBelongContract In the contract `GrowthRateManager.sol` the role `SETTER` has authority over the functions shown below. Any compromise to the `SETTER` account may allow the hacker to take advantage of this authority and modify the configuration of the GrowthRateManager and affect the auction process. * setCloseDelay * setGrowthRateVersion * setGrowthRate * setCollection * setMarketType In the contract `RoleManager.sol` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and modify privileged roles with in the system and damage the operation of the project. * setRoleAdmin * revokeRole
HighCentralized Control of Contract UpgradeOpen
The `RoleManager.sol`, `ExecuteManager.sol` and `GrowthRateManager.sol` contract inherits upgradeable contracts, indicating that it is part of an upgradeable system. Upgradeable contracts often pair with a proxy contract that is responsible for managing contract upgrades. The `privileged roles` of the proxy often have the authority to update the implementation contract. Any compromise of the privileged account could allow a hacker to exploit this authority, potentially altering the implementation contract pointed to by the proxy and thus executing malicious functionality within the implementation contract.
LowPotential function selector collisionOpen
The `ExecuteManager` contract is designed to manage un-executable function selectors by maintaining a map that marks certain functions as un-executable. It is worth noting that functions in different contracts could share the same function selector. Since these functions may belong to different contracts, marking a function selector as un-executable could inadvertently affect legitimate and intended functionalities in the protocol.
LowUnused owner roleOpen
The `RoleManager` contract is designed as a multiple role management contract. However, it inherits `Ownable2StepUpgradeable`, which is specifically designed to facilitate an owner role that can be granted exclusive access to specific functions within the contract. It was observed that the `RoleManager` contract does not make use of the owner role functionality provided by the `Ownable2StepUpgradeable`. The `ExecuteManager` contract shares the similar issue that the owner role is unused.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (7)
- contracts/etc/manager/RoleManager.sol
- contracts/NILE2.0/order/CHybridAuctionOrder.sol
- contracts/GrowthRate/GrowthRateManager.sol
- contracts/GrowthRate/GrowthRateV1.sol
- contracts/NILE1.0/order/HybridAuctionOrder.sol
- contracts/etc/manager/ExecuteManager.sol
- contracts/NILE1.0/order/OHybridAuctionOrder.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us