ClearCryptos
CertiK reviewed ClearCryptos on 10 Oct 2022: 7 findings, 0 critical; 4 marked fixed, 1 acknowledged, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings7
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 4 |
HighCentralization Related RisksAcknowledged
In the contract `ClearCryptos` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to manage administrative addresses and pause/resume trading. 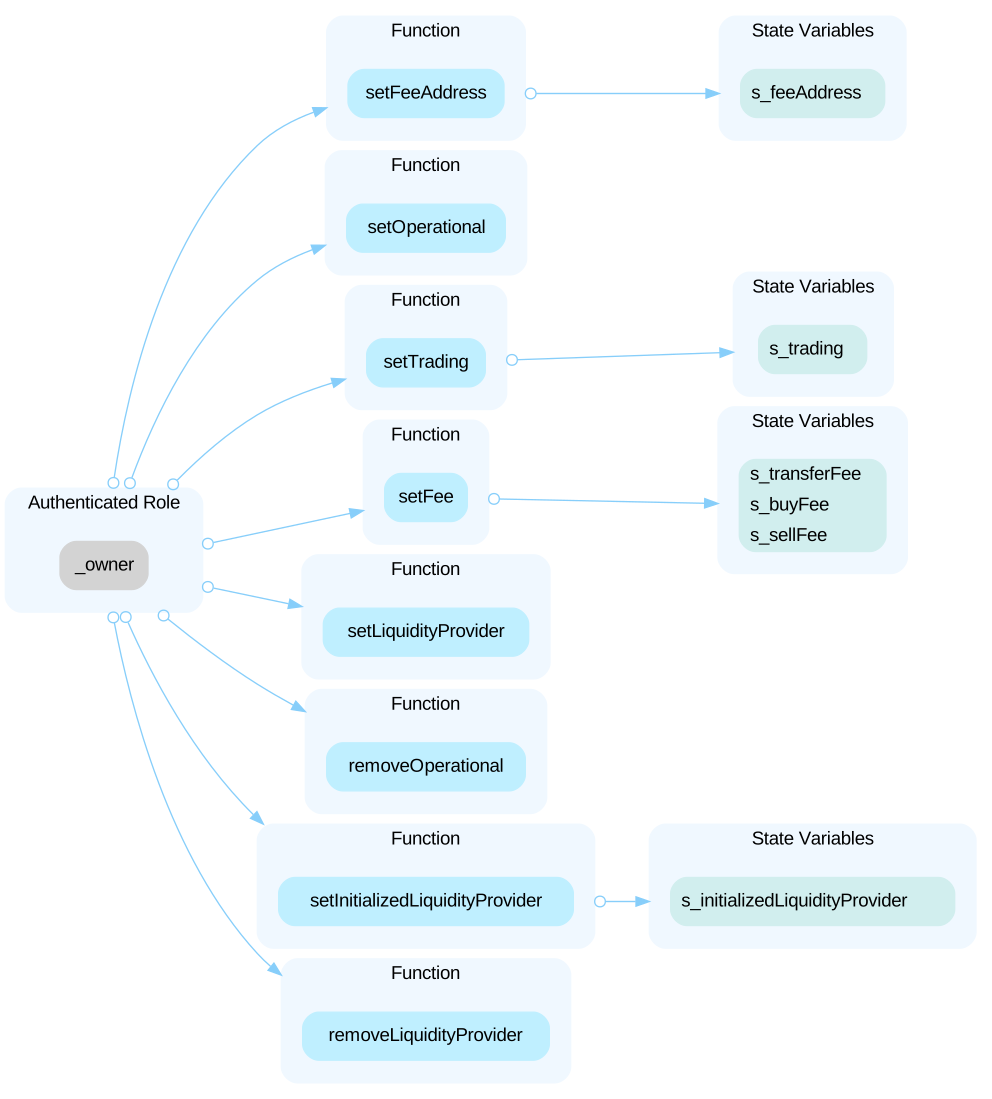 The `_owner` can also upgrade the contract without the community's consent. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract. With access to the functions `transferOwnership()` and `renounceOwnership()` the `_owner` has the authority to change the `_owner` at will and transfer special privileges to any address of choice. The above centralization issues related to upgrading and contract ownership will apply to all `Proxy.sol` and `ProxyAdmin.sol` contracts (within the Proxy module - `0x31492847f0fe646aaaf775a2bb80cc25c4655c81` and Admin module - `0x826d30961244554900ed9946721adcd5c9ae9eb2`) that are further implemented in future iterations as well. It is essential to highlight this risk and how it relates to each module of the platform to ensure that proper controls and monitors are set in place to mitigate against the risk of exploits.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of ClearCryptos’s security record
 ClearCryptos
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us