Wemix Retainer 83 Governance & Wonder Staking
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 83 Governance & Wonder Staking) on 19 Jan 2024: 21 findings, 0 critical; 15 marked fixed, 6 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings21
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 1 | 0 | 6 |
| Low | 3 | 0 | 9 |
HighCentralization Related RisksOpen
In the contract `GovImp` the role `_govmem` has authority over the functions shown in the diagram below. Any compromise to the `_govmem` account may allow the hacker to take advantage of this authority and add proposals, vote, and finalize the end vote. 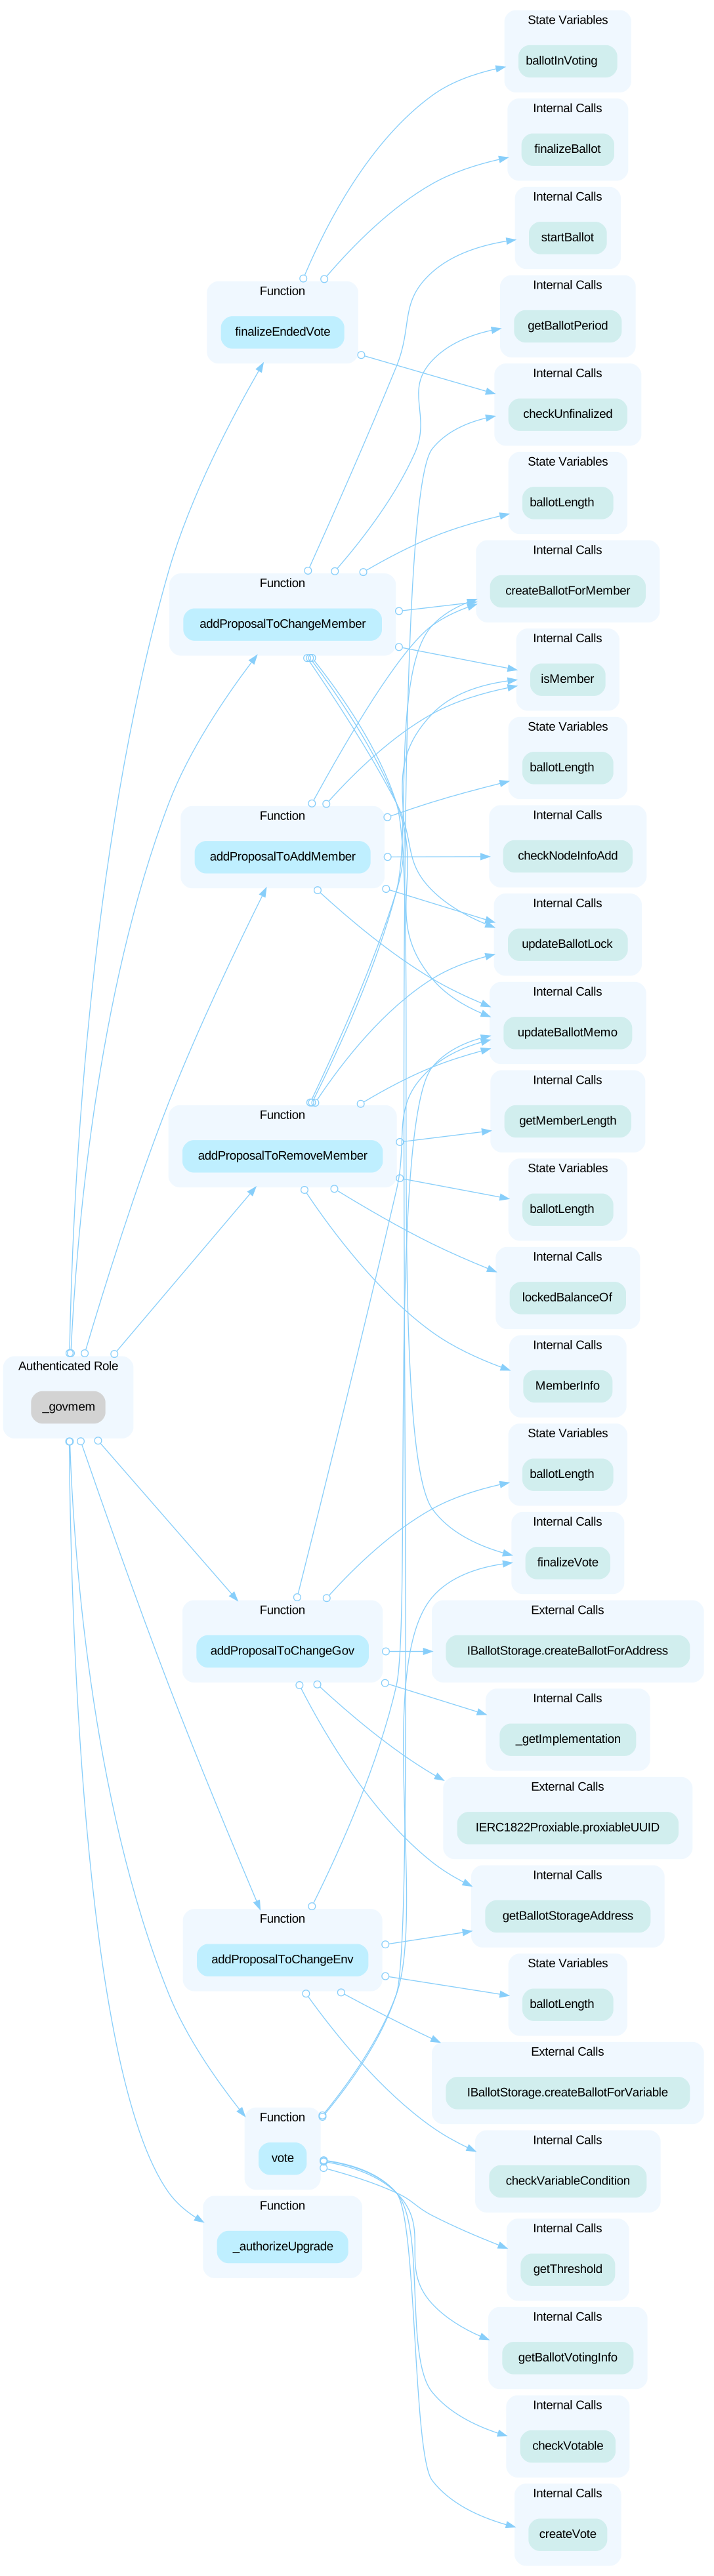 In the contract `GovImp` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and can re-init and set `posalTimePeriod`. 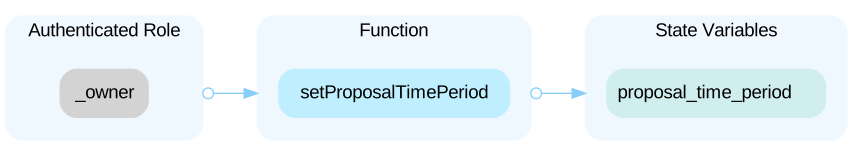 In the contract `StakingImp` the role `_govstaker` has authority over the functions shown in the diagram below. Any compromise to the `_govstaker` account may allow the hacker to take advantage of this authority and lock more amounts. 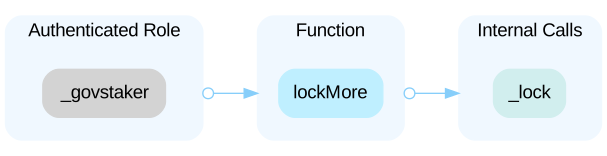 In the contract `StakingImp` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and revoke the staking contract, upgrade the staking contract, and set the NCP staking address. 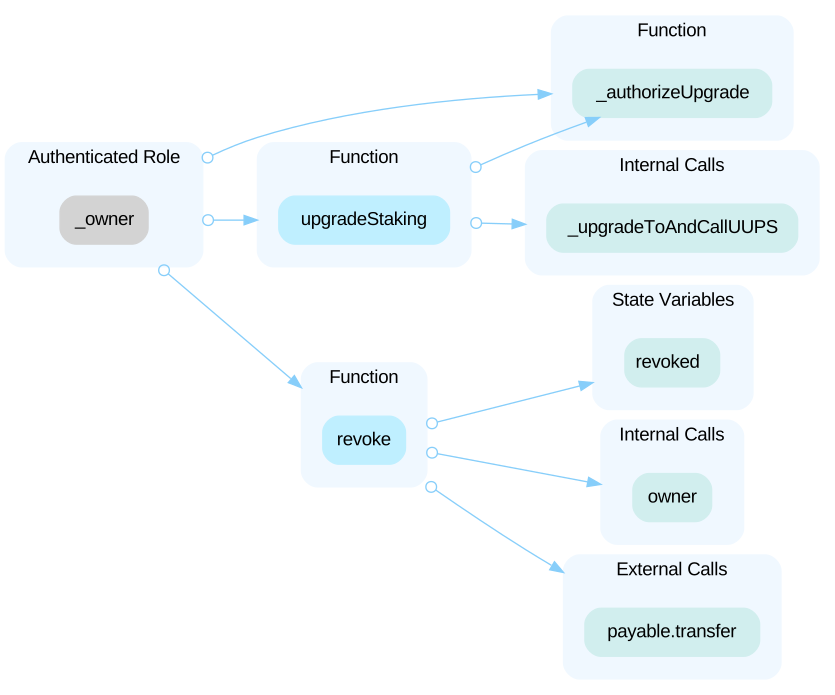 In the contract `NCPExitImp` the role `_administrator` has authority over the functions - withdrawForAdministrator() - getAvailableAmountForAdministrator() Any compromise to the `_administrator` account may allow the hacker to take advantage of this authority and withdraw tokens to any address and get the available amount. In the contract `NCPExitImp` the role `_administratorSetter` has authority over the functions - setAdministrator() - setAdministratorSetter() Any compromise to the `_administratorSetter` account may allow the hacker to take advantage of this authority and set the administrator and administrator setter address. Any compromise to the `_owner` of the contract `NCPExitImp` may allow the hacker to take advantage of this authority and upgrade the `NCPExitImp` contract. In the contract `NCPStaking` the role `_owner` has authority over the functions shown in the diagram below. 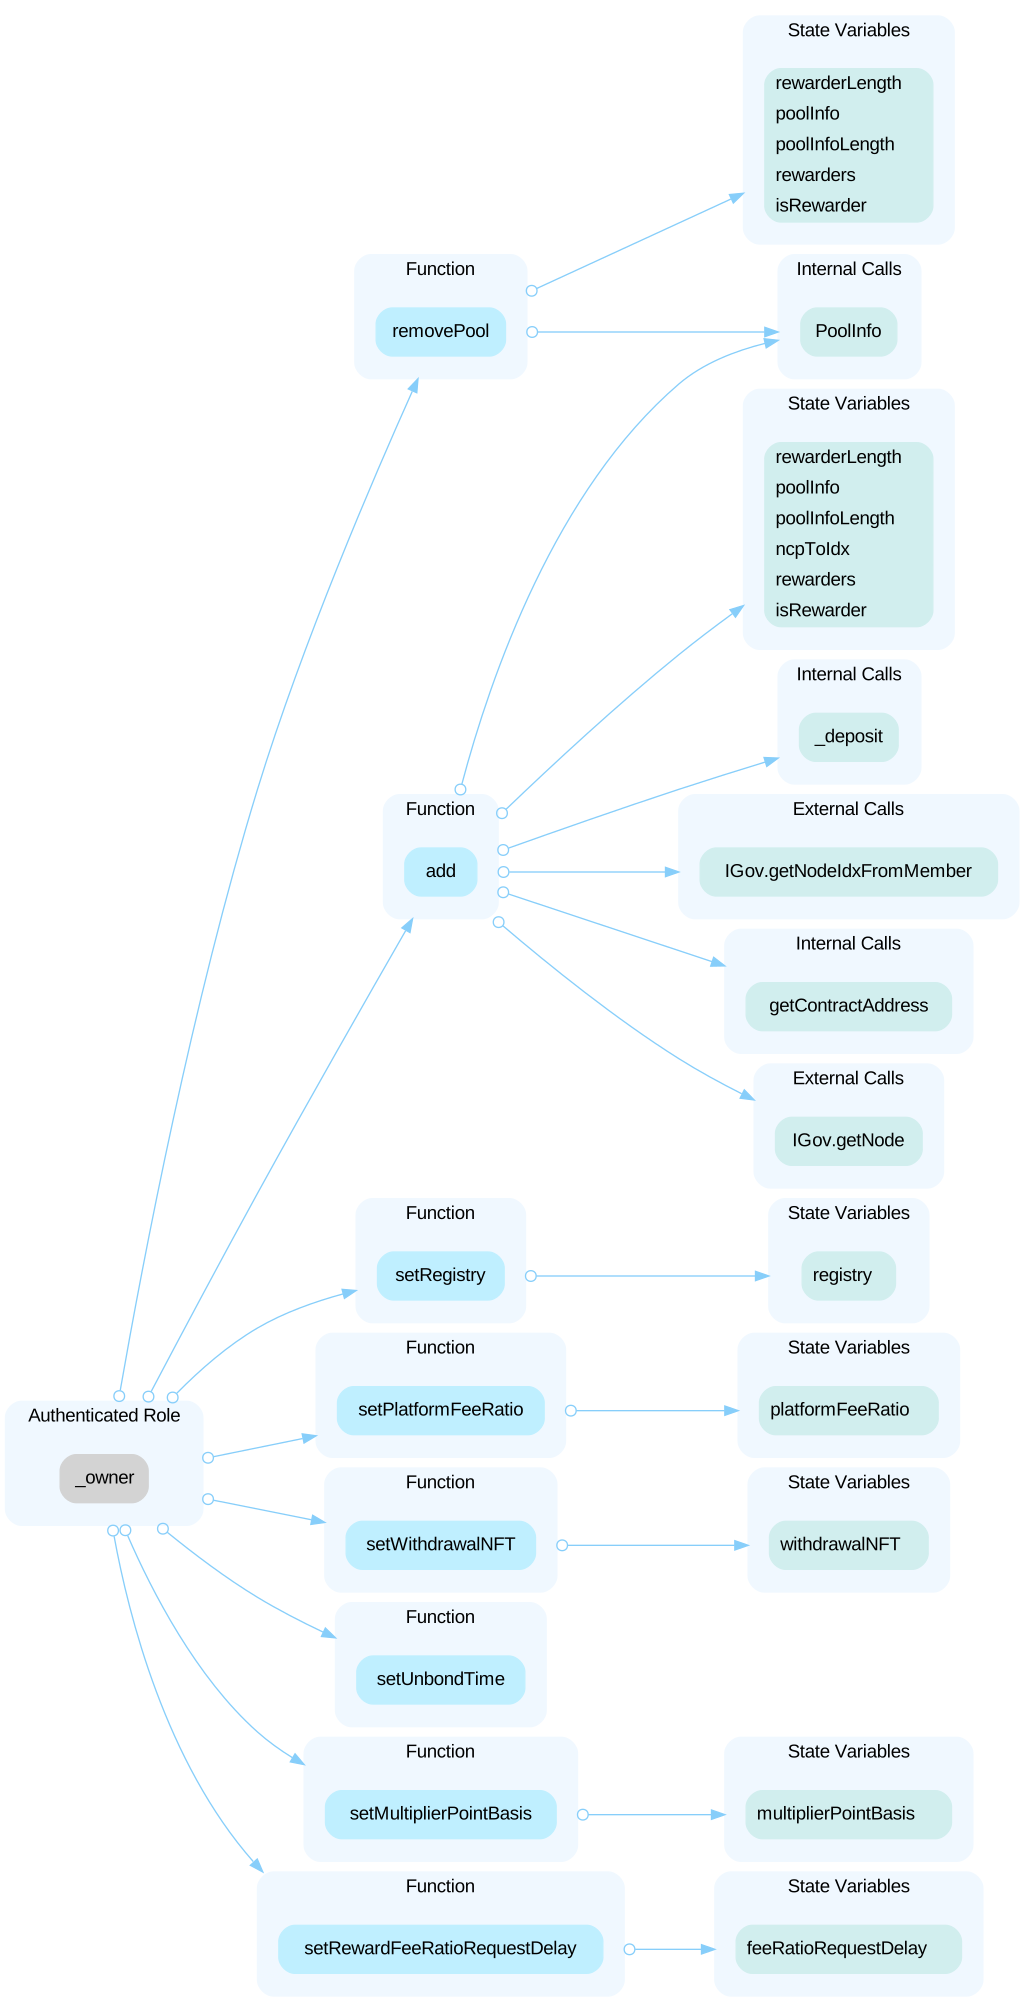 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and can call multiple functions such as `removePool`,`setPlatformFeeRatio`, `setWithdrawalNFT`, `addPool`, and so on. The hacker can set the platform fee ratio to 100% or remove an existing pool to reset all user rewards. If the hacker removes an active pool, users will not be able to withdraw their stakings. Besides, the `add` function allows the contract owner to perform the initial deposit without any cost.** Once the owner role gets compromised, the attacker can withdraw funds from `GovernanceStaking` by adding a new pool and then withdraw. In the contract `NCPStaking` the role `_rewarderowner` has authority over the functions shown in the diagram below. 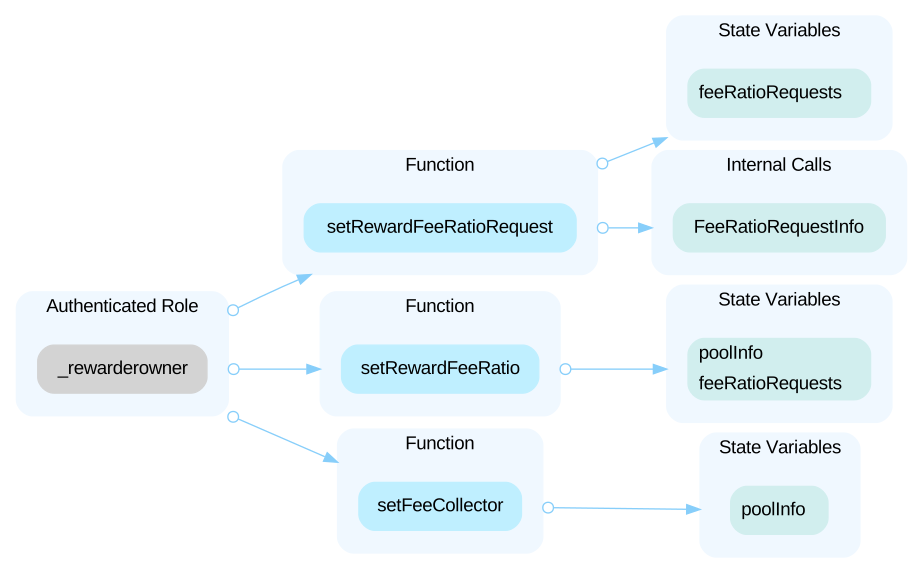 Any compromise to the `_rewarderowner` account may allow the hacker to take advantage of this authority and can change `rewardFeeRatio`. In the contract `Rewarder` the role `_owner` has authority over the functions shown in the diagram below. 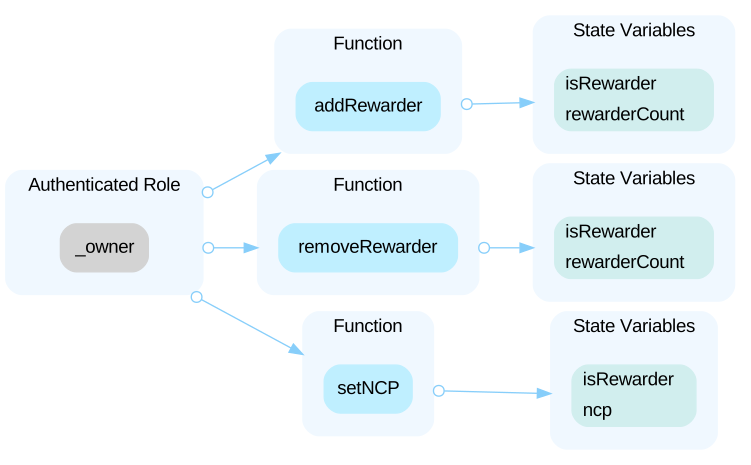 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add/remove rewarder addresses and NCP.
HighCentralized Control Of Contract UpgradeOpen
In the above contracts, the role `owner` has the authority to update the implementation contract behind the proxy contract. Any compromise to the `owner` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
MediumLack of Storage Gap in Upgradeable ContractOpen
There is no storage gap preserved in the logic contract `GovChecker`. Any logic contract that acts as a base contract inherited by other upgradeable contracts should have a reasonable size of storage gap preserved for potential new state variables introduced in future upgrades. Otherwise, there could be potential storage slot collision.
LowDivide Before MultiplyOpen
Performing integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=59 uint256 poolTotalRewardAPR = ((totalRewardAPR) * 1 ether) / govTotalLockedBalance; ``` ```solidity=74 uint256 apr = ((poolTotalRewardAPR * (10000 - platformFeeRatio)) * (10000 - pool.feeRatio)) / 10000 / 10000; ``` --- ```solidity=289 uint256 x = computePoolAPR(pid) / SECONDS_PER_YEAR * 10**18; ``` --- ```solidity=291 uint256 x2 = x * x / BASE_ETHER; ``` ```solidity=292 uint256 x3 = x2 * x / BASE_ETHER; ``` --- ```solidity=309 uint256 poolTotalRewardAPR = (getTotalRewardAPR() * ratio * 1 ether) / 10000 / stakedLP; ``` ```solidity=311 apr = (((poolTotalRewardAPR * (10000 - platformFeeRatio))) * (10000 - pool.feeRatio)) / 10000 / 10000; ``` --- ```solidity=332 uint256 poolTotalRewardAPR = (getTotalRewardAPR() * ratio * 1 ether) / 10000 / stakedLP; ``` ```solidity=337 apr = ((poolTotalRewardAPR * (10000 - platformFeeRatio)) * (10000 - feeRatio)) / 10000 / 10000; ```
LowUnused MappingOpen
The mapping `pidMap` is never used in the `NCPStaking.sol`. ```solidity=1558 mapping(uint256 /* pid */ => uint256 /* new pid */) public pidMap; ```
LowUnused State VariableOpen
Some state variables are not used in the codebase. This can lead to incomplete functionality or potential vulnerabilities if these variables are expected to be utilized. ```solidity=18 uint256 public accRewardPerShare; ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (10)
- contracts/storage/BallotStorage.sol
- contracts/StakingImp.sol
- contracts/gateway/NCPStakingGateway.sol
- contracts/NCPExit.sol
- contracts/NCPStaking.sol
- contracts/GovImp.sol
- contracts/Rewarder.sol
- contracts/withdrawalToken/WithdrawalNFT.sol
- contracts/NCPExitImp.sol
- contracts/storage/BallotStorageImp.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us