Wemix Retainer 69 WEMIX Swap V3
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 69 WEMIX Swap V3) on 7 Nov 2023: 12 findings, 1 critical; 9 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings12
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 3 |
| Low | 1 | 0 | 5 |
HighCentralization Related RisksOpen
In the contract `WeswapV3Factory` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority and pause/unpause any pool contracts. 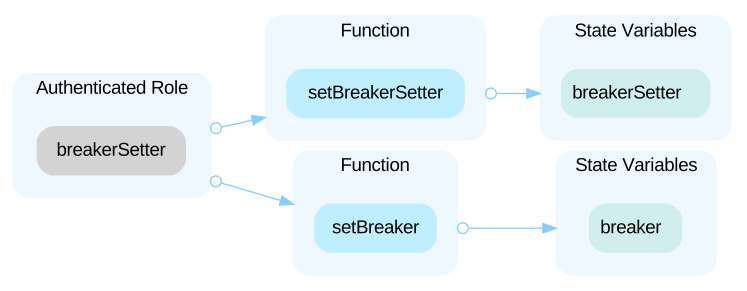 In the contract `WeswapV3Factory` the role `feeControllerSetter` has authority over the functions shown in the diagram below. Any compromise to the `feeControllerSetter` account may allow the hacker to take advantage of this authority and set protocol fees for any pool contracts. 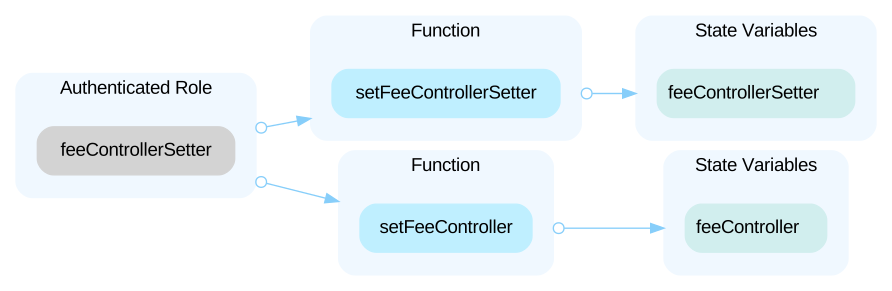 In the contract `WeswapV3Factory` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and - Add/remove arbitrary addresses to/from the whitelist.The whitelisted account can still use the pool contract when it is paused. - Set `tickSpacing` fee through the function `enableFeeAmount()`. - Change `DenylistContract` address through the function `setDenylistContract()` 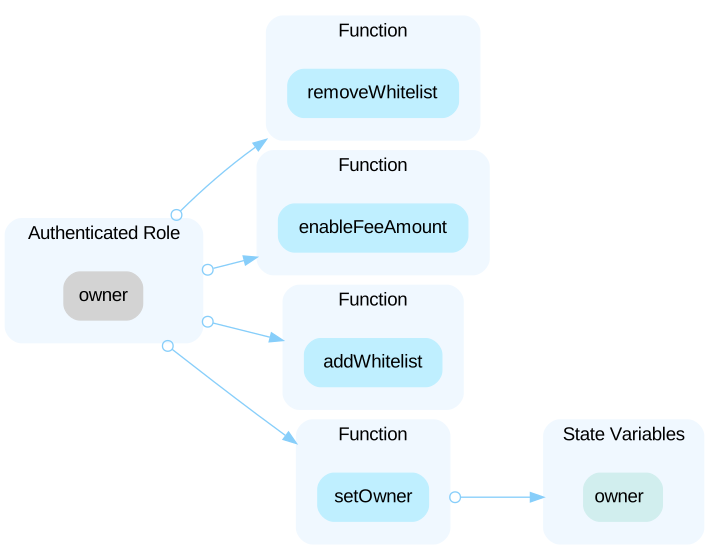 In the contract `NonfungiblePositionManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and initialize the pool. 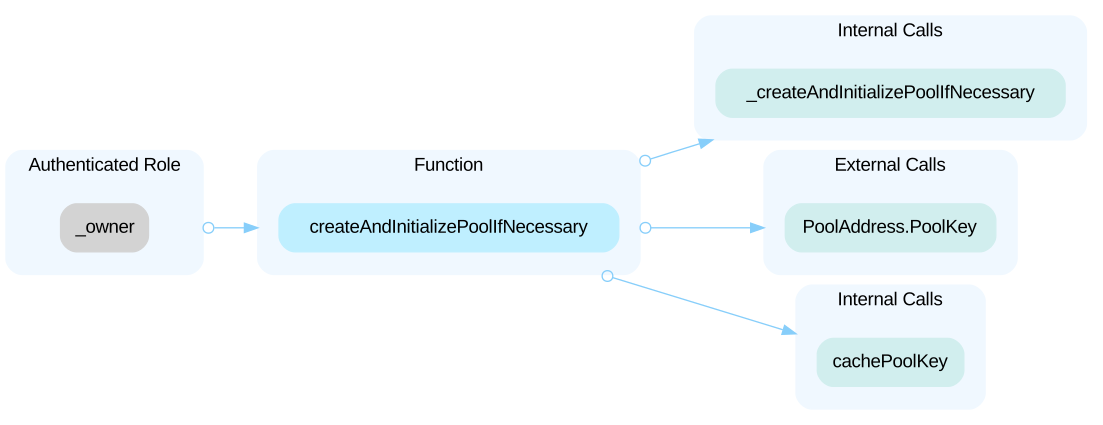
HighCentralized Control of Contract UpgradeOpen
`NonfungiblePositionHelper`/`Quoter`/`QuoterV2`/`WeswapV3Factory`/`NonfungiblePositionManager`/`SwapRouter` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the proxy admin account, he can change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Low`collectBlockNumber` not returned in function `poOpen
The `positions()` function is intended to expose details about a specific position. While the function successfully returns most of the details, it omits the `collectBlockNumber` field that is available in the Position struct. ```solidity=185 function positions( uint256 tokenId ) external view override returns ( uint96 nonce, address operator, address token0, address token1, uint24 fee, int24 tickLower, int24 tickUpper, uint128 liquidity, uint256 feeGrowthInside0LastX128, uint256 feeGrowthInside1LastX128, uint128 tokensOwed0, uint128 tokensOwed1 ) ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (57)
- contracts/libraries/PositionKey.sol
- contracts/libraries/UnsafeMath.sol
- contracts/base/PeripheryPayments.sol
- contracts/libraries/BitMath.sol
- contracts/base/PoolInitializer.sol
- contracts/libraries/TokenRatioSortOrder.sol
- contracts/lens/TickLens.sol
- contracts/libraries/TickBitmap.sol
- contracts/WeswapV3PoolDeployer.sol
- contracts/libraries/LowGasSafeMath.sol
- contracts/libraries/OracleLibrary.sol
- contracts/libraries/TickBitmapFixed.sol
- contracts/libraries/FixedPoint96.sol
- contracts/libraries/SqrtPriceMath.sol
- contracts/libraries/TickMath.sol
- contracts/utils/WWEMIX.sol
- contracts/libraries/PoolTicksCounter.sol
- contracts/WeswapV3Factory.sol
- contracts/SwapRouter.sol
- contracts/libraries/Tick.sol
- contracts/base/PeripheryPaymentsWithFee.sol
- contracts/libraries/PoolAddress.sol
- contracts/base/BlockTimestamp.sol
- contracts/libraries/LiquidityMath.sol
- contracts/libraries/FixedPoint128.sol
- contracts/base/SelfPermit.sol
- contracts/base/ERC721Permit.sol
- contracts/libraries/TransferHelper.sol
- contracts/libraries/FullMath.sol
- contracts/libraries/ChainId.sol
- contracts/libraries/SqrtPriceMathPartial.sol
- contracts/NoDelegateCall.sol
- contracts/NonfungiblePositionHelper.sol
- contracts/libraries/LiquidityAmounts.sol
- contracts/libraries/Position.sol
- contracts/WeswapV3Pool.sol
- contracts/libraries/HexStrings.sol
- contracts/libraries/PositionValue.sol
- contracts/libraries/CallbackValidation.sol
- contracts/base/LiquidityManagement.sol
- contracts/base/Multicall.sol
- contracts/lens/Quoter.sol
- contracts/libraries/Path.sol
- contracts/base/PeripheryValidation.sol
- contracts/NonfungibleTokenPositionDescriptor.sol
- contracts/libraries/SafeCast.sol
- contracts/libraries/SwapMath.sol
- contracts/lens/QuoterV2.sol
- contracts/lens/WeswapInterfaceMulticall.sol
- contracts/base/PeripheryImmutableState.sol
- contracts/libraries/NFTDescriptor.sol
- contracts/libraries/NFTSVG.sol
- contracts/libraries/BytesLib.sol
- contracts/NoDelegateCallUpgradeable.sol
- contracts/libraries/Oracle.sol
- contracts/NonfungiblePositionManager.sol
- contracts/utils/Utils.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us