Parex
CertiK reviewed Parex on 15 Oct 2024: 14 findings, 1 critical; 10 marked fixed, 4 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings14
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 0 | 1 | 4 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 3 | 3 |
HighCentralization Risks in PRX-BSCToken.solAcknowledged
In the contract `BSCToken`, the role `PRX` has authority over the functions shown in the diagram below. Any compromise to the `PRX` account may allow the hacker to take advantage of this authority. - `pause()`: pause the contract - `unpause()`: unpause the contract - `blacklist()`: add a account to blacklist - `unblacklist()`: remove a account from blacklist - `unlockTokens()`: unlock the tokens - `setBridgeFee()`: set the `bridgeFee` - `setMaxAmount()`: set the `maxAmount` - `sendBridgeOwnerReward()`: withdraw the token 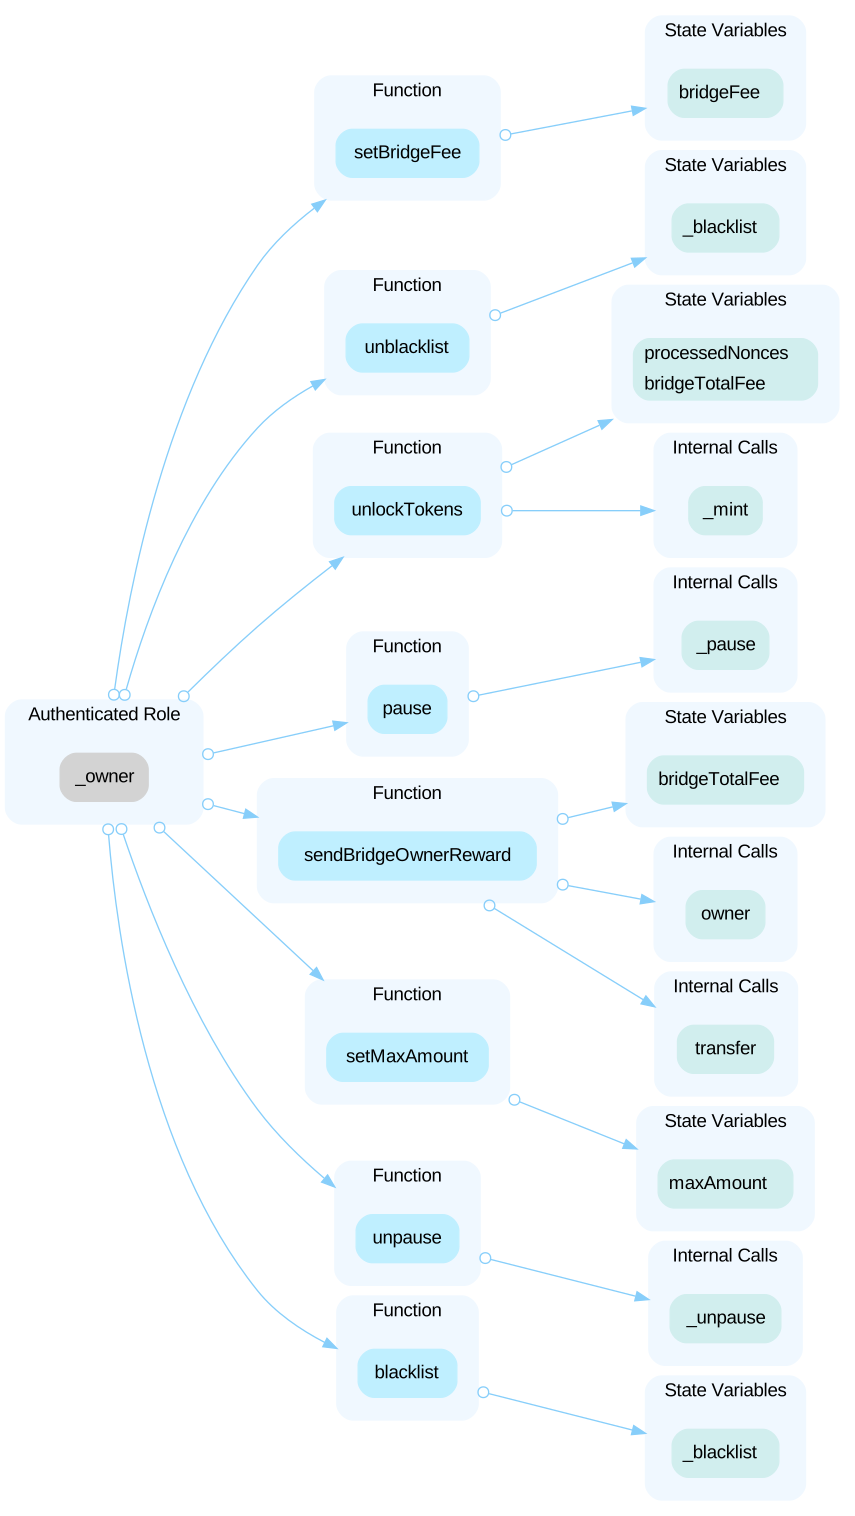
LowFixed Fee Deduction in `unlockTokens` FunctionAcknowledged
The `unlockTokens()` function, called by the contract owner to unlock tokens for users, deducts a fixed `bridgeFee` instead of a fee proportional to the amount of tokens being unlocked. This introduces a potential inconsistency in the amount of tokens unlocked for users, especially in cases where larger token amounts are involved. ```solidity=145 if (amount > 0) { require(amount > bridgeFee, "Amount must be greater than bridge fee"); amountToMint -= bridgeFee; // Deduct the bridge fee bridgeTotalFee += bridgeFee; // Accumulate the total fees collected } ```
LowPull-Over-Push Pattern In `transferOwnership()` FAcknowledged
The change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
LowWithout Re-Approving in `_burnFrom` FunctionAcknowledged
The `_burnFrom` function allows users to burn tokens without updating their allowance. Specifically, on line 798, the function checks the user's approved allowance but does not to reduce the allowance after execution. This allows users to repeatedly call the function without re-approving the contract. ```solidity=797 function _burnFrom(address account, uint256 amount) internal virtual { uint256 currentAllowance = allowance(account, address(this)); require(currentAllowance >= amount, "ERC20: burn amount exceeds allowance"); _burn(account, amount); } ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- PRX-BSCToken.sol
Part of Parex’s security record
 Parex
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us