Liquid Protocol ($LP) - Audit
CertiK reviewed Liquid Protocol (Liquid Protocol ($LP) - Audit) on 11 Oct 2023: 15 findings, 0 critical; 6 marked fixed, 9 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings15
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 2 |
| Medium | 0 | 0 | 2 |
| Low | 8 | 0 | 2 |
HighCentralization Risks in liquidprotocol.solFixed
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership to any address and renounce ownership. 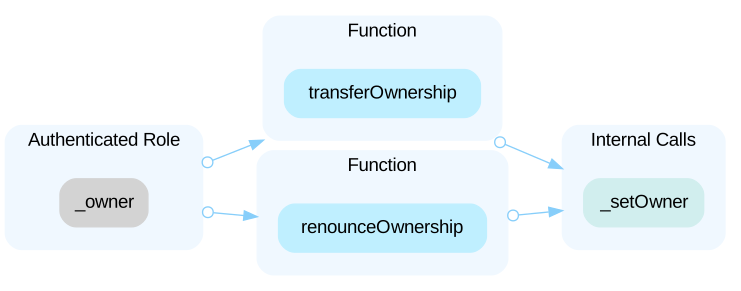 In the contract `liquidprotocol` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set `tradingEnabled`, `swapEnabled`, and `genesis_block`, exclude the account from the reward, include the account in reward, exclude the account from fee, include the account in fee, set taxes, airdrop tokens to any address, bulk exclude accounts from the fee, set `marketingWallet`, `donationWallet`, `coolDownTime`, `coolDownEnabled`, `swapTokensAtAmount`, `swapEnabled`, `_isBlacklisted`, `allowedTransfer`, `maxBuyLimit`, `maxSellLimit`, `router`, `pair`, transfer ETH to the owner and transfer any tokens to any address. 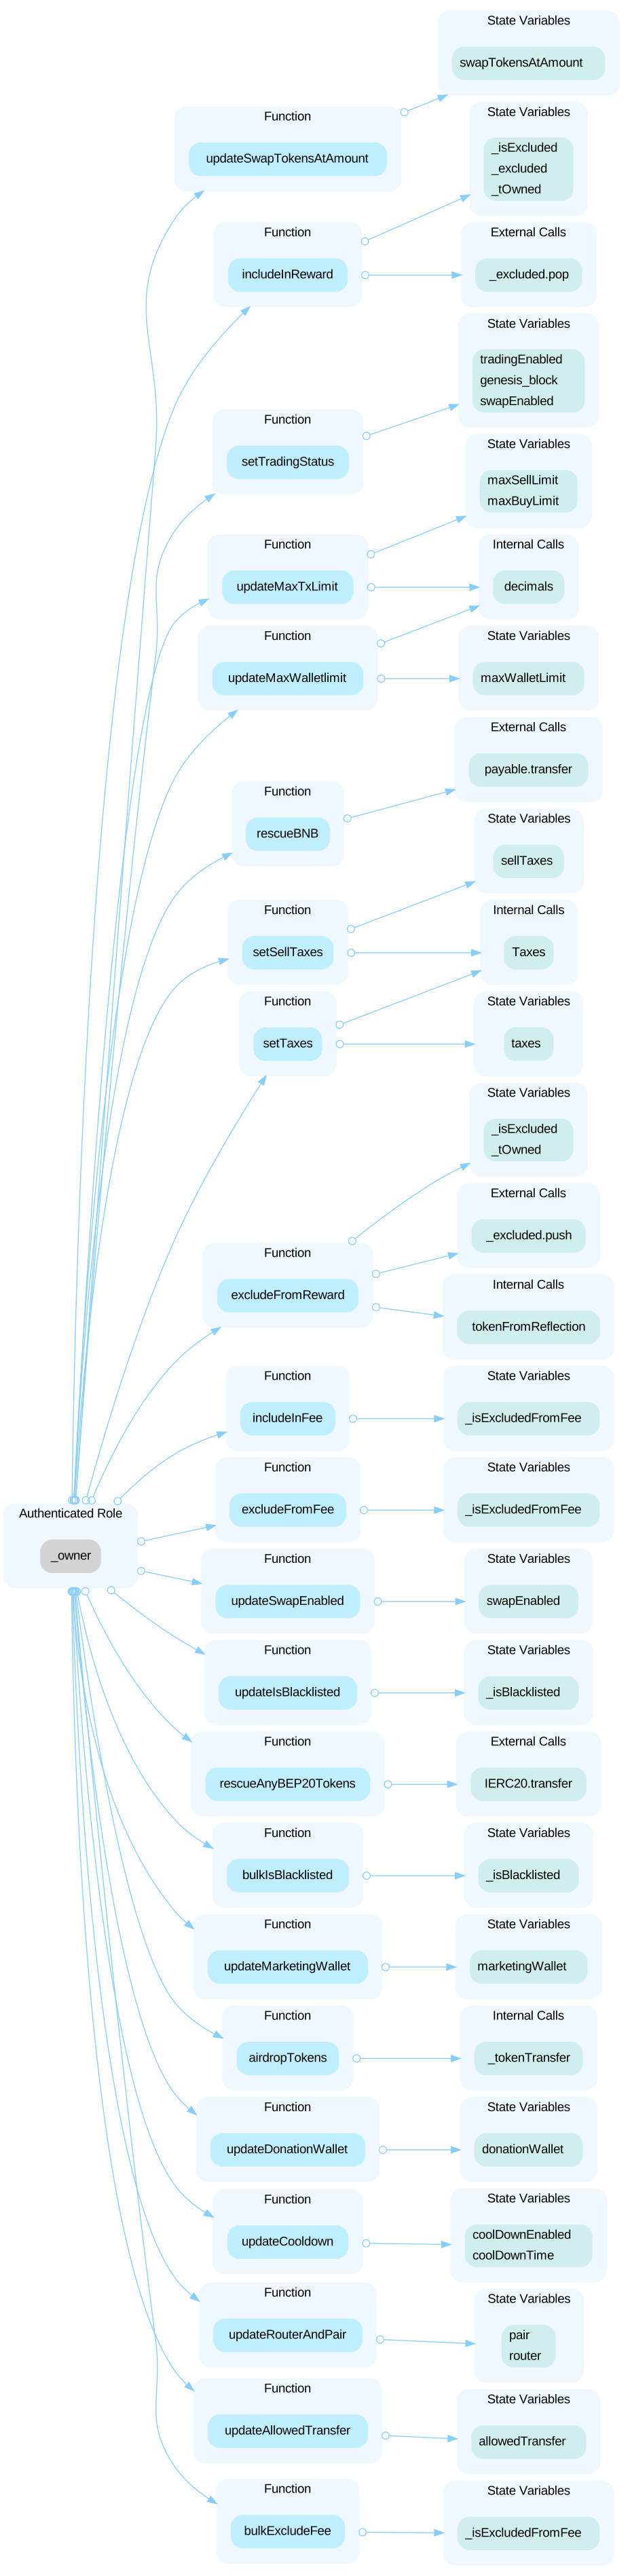
HighCentralized Risk In `addLiquidity`Fixed
```solidity=824 // add the liquidity router.addLiquidityETH{value: bnbAmount}( address(this), tokenAmount, 0, // slippage is unavoidable 0, // slippage is unavoidable owner(), block.timestamp ); ``` The `addLiquidity()` function calls the `router.addLiquidityETH` function with the `to` address specified as `owner()` for acquiring the generated LP tokens from the `LP-ETH` pool. As a result, over time the `_owner` address will accumulate a significant portion of LP tokens. If the `_owner` is an EOA (Externally Owned Account), mishandling of its private key can have devastating consequences to the project as a whole.
MediumNo Upper Limits for FeesFixed
There is no upper limit restricting parameters `_rfi`,`_marketing`,`_liquidity`, and `_donation` of `setSellTaxes()`/`setTaxes()`. This lack of limitation potentially allows for fees on transactions of up to 100%.
MediumVariable `_rOwned[account]` Not Updated in FunctiFixed
Variable `_rOwned[account]` is not updated in the function `includeInReward()`, which will make the accounts included siphon off the tokens out of the balances of all token holders. The Rate was higher at the moment of the `excludeFromReward(account)` call, so the `_rOwned[account] / _tOwned[account]` ratio is bigger than expected for accounts included in the reward. ```solidity =331 function includeInReward(address account) external onlyOwner() { require(_isExcluded[account], "Account is not excluded"); for (uint256 i = 0; i < _excluded.length; i++) { if (_excluded[i] == account) { _excluded[i] = _excluded[_excluded.length - 1]; _tOwned[account] = 0; _isExcluded[account] = false; _excluded.pop(); break; } } } ```
LowMissing Zero Address ValidationFixed
Addresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior or vulnerabilities. For example, transferring tokens to a zero address can result in a permanent loss of those tokens. ```solidity=628 marketingWallet = newWallet; ``` - `newWallet` is not zero-checked before being used. --- ```solidity=632 donationWallet = newWallet; ``` - `newWallet` is not zero-checked before being used. --- ```solidity=675 pair = newPair; ``` - `newPair` is not zero-checked before being used.
LowPair Should Be Excluded From RewardsFixed
In the `constructor`, the pair is excluded from rewards. However, the new pair is not excluded from rewards in the function `updateRouterAndPair()`.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x3e8203e0b1d56984abc66f183a8d0b1a09a7e607 | Chain: Ethereum | Source code: Verified source |
Part of Liquid Protocol’s security record
 Liquid Protocol
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us