SquidGrow - V3 Contract
Part of CertiK’s series
CertiK reviewed SquidGrow (SquidGrow - V3 Contract) on 3 Sep 2024: 6 findings, 0 critical; 2 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 2 | 0 | 1 |
HighCentralization Related RisksOpen
In the contract `SquidGrow` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown as below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and do the following things: - `enableTrading()`, maliciously enable trade and set trade start time. - `pause()`, maliciously pause token transfer. - `addToWhitelist()`, add any invalid account into white list. - `removeFromWhitelist()`, remove valid account from white list. - `grantRole()`, grant key role to malicious account and add into white list. - `revokeRole()`, maliciously revoke key role of valid account and remove from white list. - `renounceRole`, maliciously renounce `DEFAULT_ADMIN_ROLE` role. - `emergencyWithdrawOtherToken()`, maliciously withdraw any ERC20 tokens. - `emergencyWithdrawEth()`, maliciously withdraw ETH. 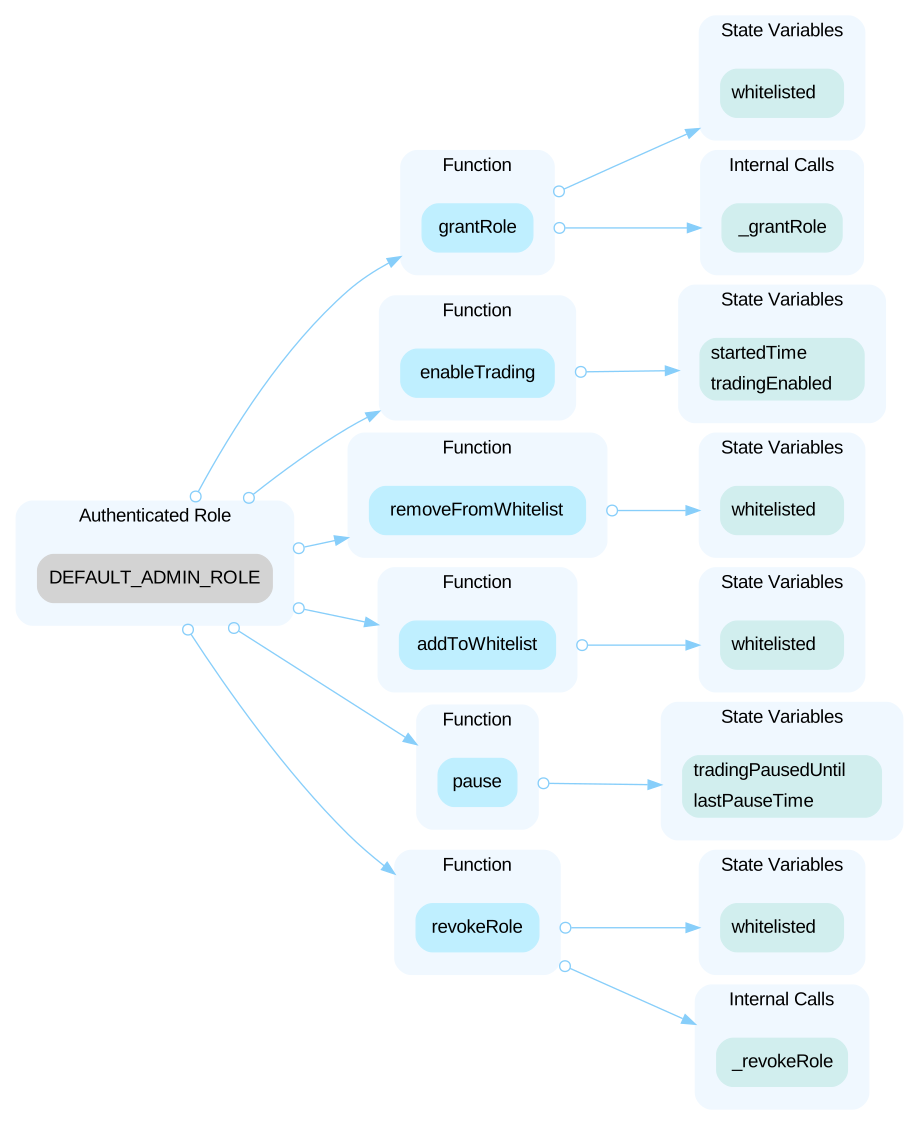
HighInitial Token DistributionOpen
All of the `SQGROW` tokens, `1_000_000_000 * 10e9`, are minted to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
LowDesign Logic of Trade Pause DurationOpen
The `pause()` is designed to pause the `SquidGrow` token transfer only for one hour. So that if there is a liquidity injection using the SAM contract trading can be paused to avoid sandwich attacks. However, the trade can only be paused once within a 24-hour period, with a maximum pause duration of 1 hour. This leaves 23 hours during which trading remains active. During these 23 hours, if liquidity is injected using the SAM contract, there is still a risk of a sandwich attack. ```solidity=78 /** * @notice Pauses all token transfers for exactly one hour. * @dev Can only be called by an account with the DEFAULT_ADMIN_ROLE. This function can only be called once every 24 hours. */ function pause() external onlyRole(DEFAULT_ADMIN_ROLE) { if (block.timestamp < lastPauseTime + 24 hours) revert PauseAlreadyTriggered(); lastPauseTime = block.timestamp; tradingPausedUntil = block.timestamp + 1 hours; } ```
LowInconsistent Comment and CodeOpen
The comment for the `renounceRole()` function states that it allows users to renounce their granted roles. However, according to the code logic of the `renounceRole()` function, only accounts with the `DEFAULT_ADMIN_ROLE` can access the function to renounce this `DEFAULT_ADMIN_ROLE` role. ```solidity=172 /** * @dev Allows someone to renounce their `role` from `account`. Also removes the account from the whitelist. * Requirements: the caller must have ``role``'s admin role. * May emit a {RoleRevoked} event. */ function renounceRole() public virtual override onlyRole(DEFAULT_ADMIN_ROLE) { whitelisted[msg.sender] = false; _revokeRole(DEFAULT_ADMIN_ROLE, msg.sender); } ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/SquidgrowV3.sol
Part of SquidGrow’s security record
 SquidGrow
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us