WeMix - Liquid Staking audit
CertiK reviewed WEMIX (WeMix - Liquid Staking audit) on 5 Dec 2022: 7 findings, 1 critical; 4 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Statuses are the security firm’s own, from this report. Trustblock does not review code.
Findings7
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 1 | 0 | 2 |
HighCentralization Risks in StWEMIX.solNot fixed
In the contract `StWEMIX` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - claim rewards, transfer fees to the treasury address, transfer other rewards to the staking pool, unlock withdrawal, and set phase two to `true` - set the fees for phase two 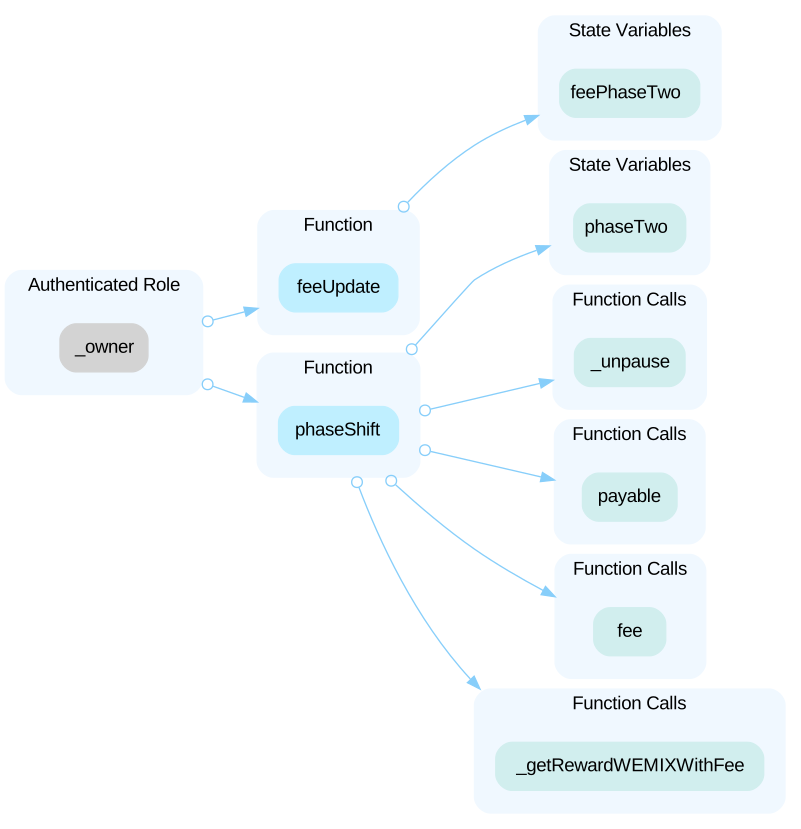
HighCentralized Control of Contract UpgradeNot fixed
`StWEMIX` is an upgradeable contract, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
LowThird Party DependencyNot fixed
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=26 IStaking public staking; // immutable ``` - The contract `StWEMIX` interacts with third party contract with `IStaking` interface via `staking`.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- contracts/interfaces/IStWEMIX.sol
- contracts/interfaces/IStaking.sol
- contracts/StWEMIX.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us