Wemix Swap - Retainer 4
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Swap - Retainer 4) on 17 Jan 2023: 18 findings, 0 critical; 7 marked fixed, 11 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings18
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 9 | 0 | 6 |
HighCentralization Related RisksOpen
In the contract `AuthorizedMintAccess` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change whitelist status or sensitive state addresses. 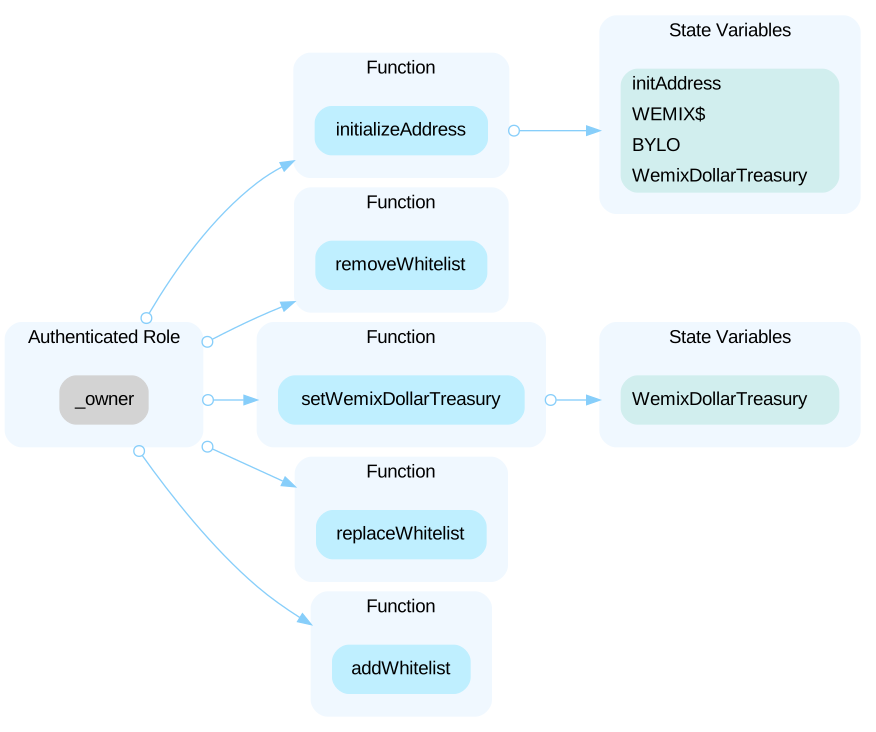 In the contract `AuthorizedMintAccess` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority and stop or resume contract functionality. 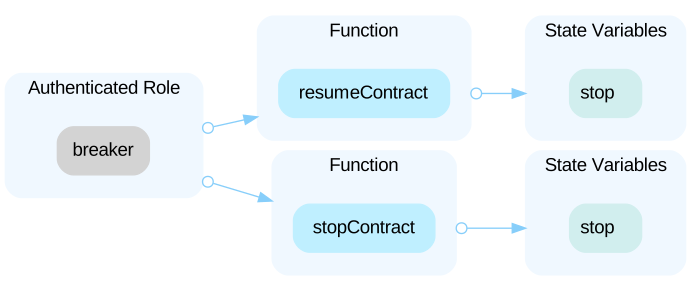 In the contract `AuthorizedMintAccess` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority and change the respective `breaker` or `breakerSetter` addresses. 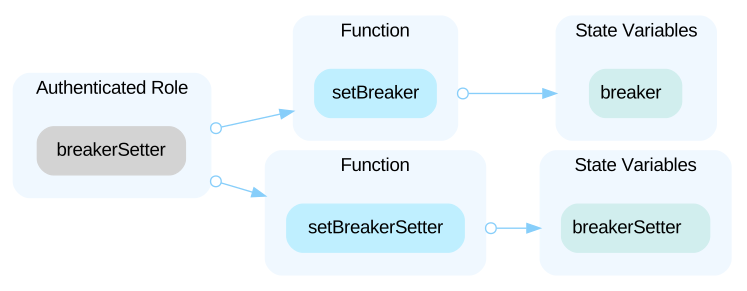 In the contract `AuthorizedMintAccess` the role `isWhitelistAddresses` has authority over the functions shown in the diagram below. Any compromise to the `isWhitelistAddresses` account may allow the hacker to take advantage of this authority and call for the exchange of WEMIX$ and BYLO tokens. 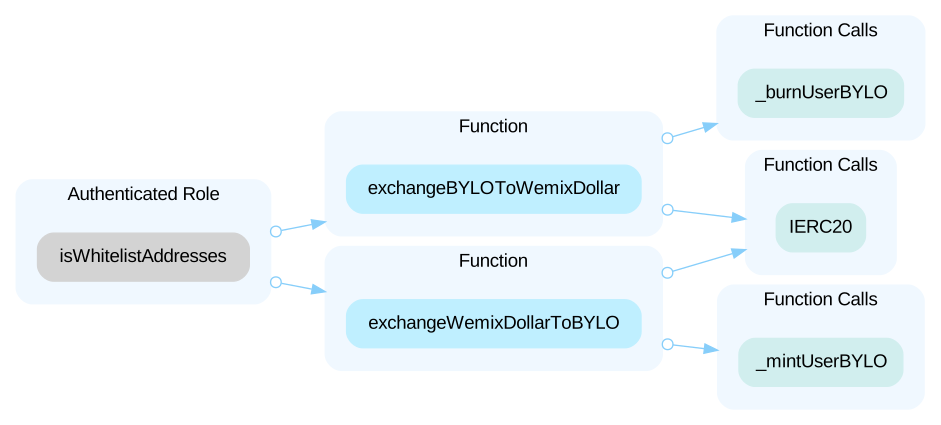 In the contract `DollarInAndOutStabilizerGame` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change sensitive contract state data including respective addresses, fees and `stakingSwitch`. 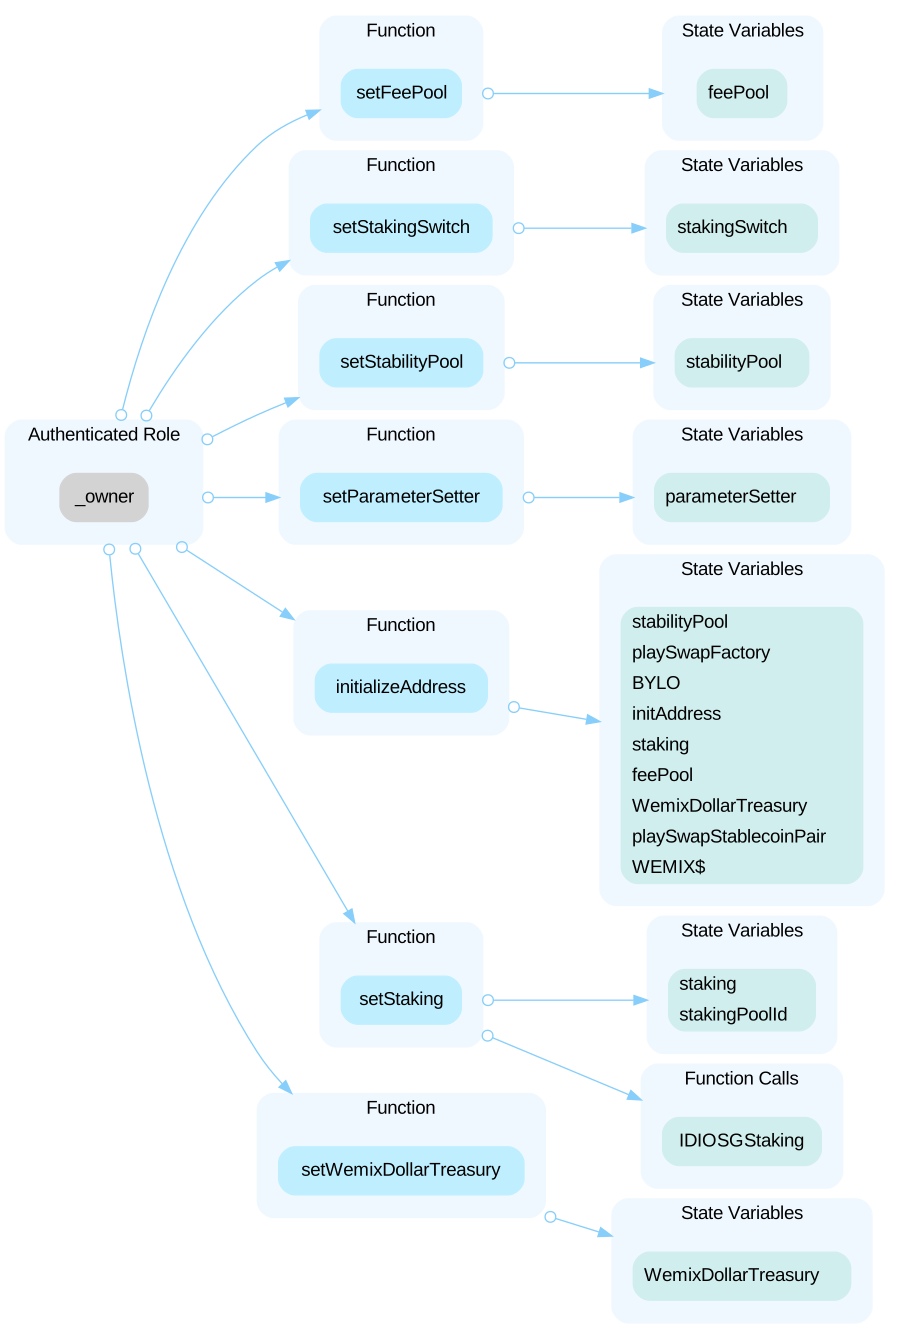 In the contract `DollarInAndOutStabilizerGame` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority and stop or resume contract functionality. 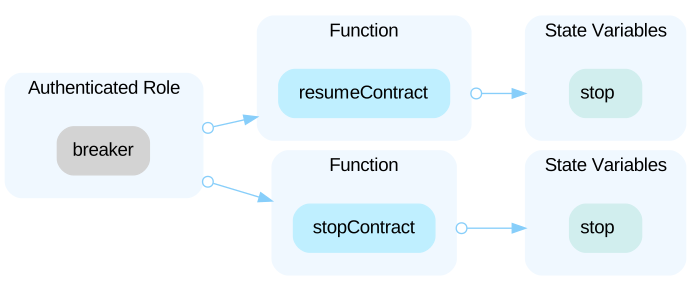 In the contract `DollarInAndOutStabilizerGame` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority and change the respective `breaker` or `breakerSetter` addresses. 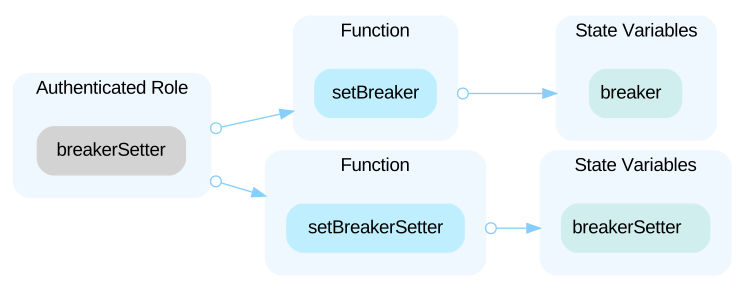 In the contract `DollarInAndOutStabilizerGame` the role `parameterSetter` has authority over the functions shown in the diagram below. Any compromise to the `parameterSetter` account may allow the hacker to take advantage of this authority and change sensitive contract state data. 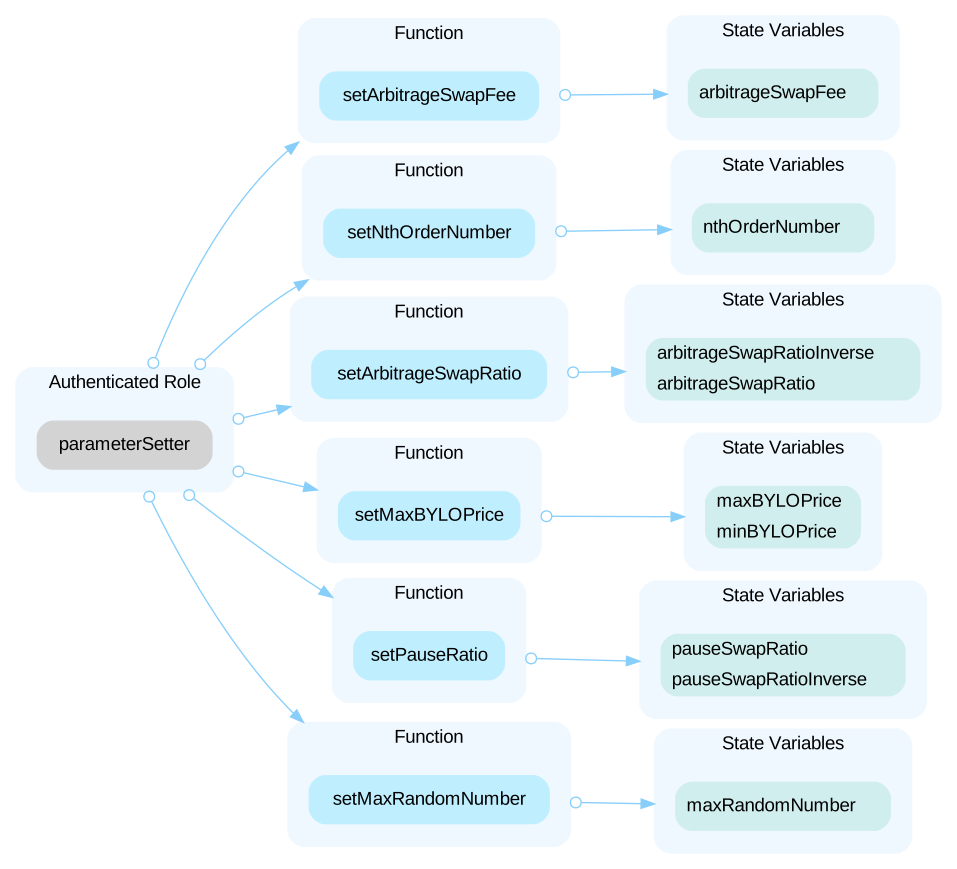 In the contract `DollarInAndOutStabilizerGame` the role `swapExecutor` has authority over the functions shown in the diagram below. Any compromise to the `swapExecutor` account may allow the hacker to take advantage of this authority and call for arbitrage swaps to be executed. 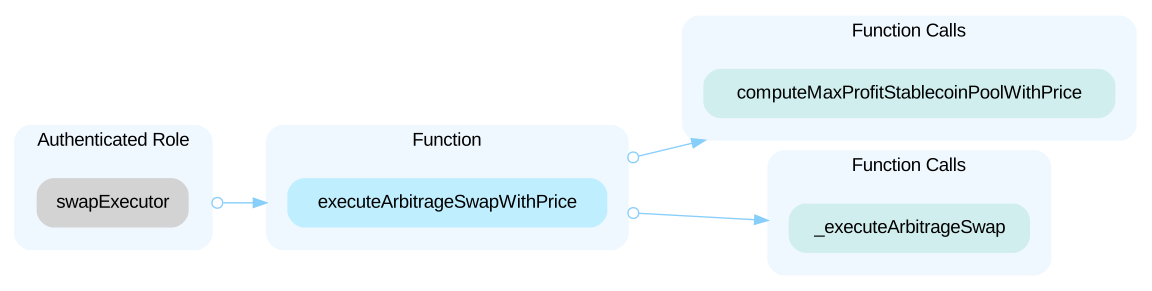 In the contract `DollarInAndOutStabilizerGame` the role `swapExecutorSetter` has authority over the functions shown in the diagram below. Any compromise to the `swapExecutorSetter` account may allow the hacker to take advantage of this authority and change the respective addresses `swapExecutor` and `swapExecutorSetter`. 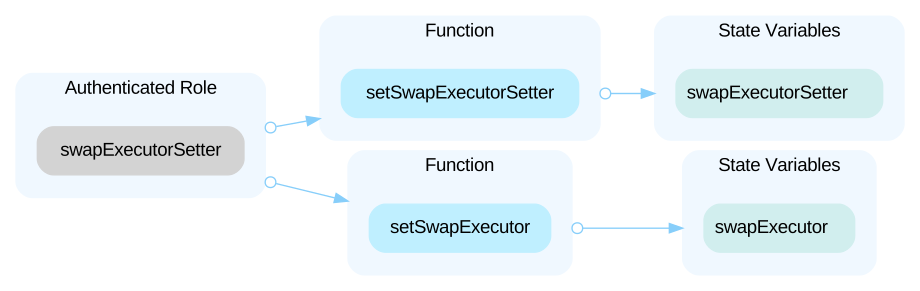 In the contract `DollarInAndOutStabilizerGame` the role `_owner` or `bearer` has authority over the following function: - `setMaxArbitrageSwapRatio()` - `setMinArbitrageSwapRatio()` Any compromise to the `parameterSetter` account may allow the hacker to take advantage of this autho
HighNo Upper Limits for FeesOpen
There are no upper limits restricting the value of `arbitrageSwapFee`, potentially enabling up to 100% of fees on transactions.
Low`quorum` should not be updatedOpen
In the function `removeOwner`, it update the `quorum` to `owners.length` if the `quorum` is greater than the owner numbers, this may cause the `notExecuted` transaction to be executed.
LowLack of Input ValidationOpen
The `ParameterSetter` can call `setMaxRandomNumber` to update `maxRandomNumber` with any nonzero value, like 1. I think the minimal value is not valid.
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowMissing ERC20 FieldOpen
The `PlaySwapERC20` fields `name` and `symbol` are unassigned and have no related setter method. Users looking for this metadata would be unable to find descriptive information for the related token.
LowOutdated Solidity VersionOpen
All the contracts in the project use Solidity version 0.6.x, which is a version introduced more than two years ago. Outdated versions might contain security issues and miss the new features and security enhancements included in the recent solidity version.
LowPotential Sandwich AttacksOpen
A sandwich attack may happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (executing before the target) a transaction to purchase one of the assets and make profits by backrunning (executing after the target) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `_swap()`
LowUnused ContractOpen
```solidity=8 library Math { ``` - The library `Math` is declared but never used. --- ```solidity=4 library UQ112x112 { ``` - The library `UQ112x112` is declared but never used. --- ```solidity=4 library TransferHelper { ``` - The library `TransferHelper` is declared but never used.
LowVariables That Could Be Declared as ImmutableOpen
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Show 1 more
LowWeak PRNGOpen
The functions `DollarInAndOutStabilizerGame.quadraticRandomPrice()` and `DollarInAndOutStabilizerGame._linearRandomPrice()` utilize modulus operation on the parameter `_randomNumber` to calculate `randomNumber`, a pseudo-random number. This value is then used for price calculation and may be influenced by a user who can change the `_randomNumber` parameter by sending and canceling transactions to calculate a more desirable price.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (23)
- AuthorizedMintAccess.sol
- PlaySwapRouter.sol
- interfaces/IERC20.sol
- libraries/PlaySwapLiquidityMathLibrary.sol
- interfaces/IPlaySwapFactory.sol
- WemixDollarTreasury.sol
- interfaces/IPlaySwapZapOut.sol
- interfaces/IPlaySwapERC20.sol
- PlaySwapPair.sol
- interfaces/IDollarInAndOutStabilizerGame.sol
- interfaces/IPlaySwapRouter.sol
- PlaySwapFactory.sol
- DollarInAndOutStabilizerGame.sol
- libraries/Math.sol
- interfaces/IToken.sol
- interfaces/IAuthorizedMintAccess.sol
- libraries/TransferHelper.sol
- libraries/PlaySwapLibrary.sol
- interfaces/IWemixDollarTreasury.sol
- PlaySwapERC20.sol
- interfaces/IPlaySwapPair.sol
- interfaces/IPlaySwapZapIn.sol
- libraries/UQ112x112.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us